TL;DR
Start a WebMCP implementation now for read-only, high-volume workflows, but hold payments, account changes and other write actions until the spec settles. WebMCP lets a web page hand AI agents named tools with JSON Schema inputs, so agents stop guessing their way through your interface. It is a Community Group draft running as an origin trial in Chrome (from version 149) and Edge, not a shipped standard. Existing HTML forms become tools with a few attributes, while app logic needs a short JavaScript registration. Keep server-side MCP for back-end integration, because WebMCP tools exist only while a user has your page open. Measure task completion and cancel rates on the pilot before you expose anything that changes data.
Key Takeaways
- WebMCP is a browser API, so a page registers tools (name, description, JSON Schema, execute function) on
document.modelContextfor agents to call. - The spec is still a draft Community Group Report, so treat every WebMCP implementation as a progressive enhancement.
- Declarative tools reuse existing HTML forms, while imperative tools wrap JavaScript functions; many sites need both.
- Pick first workflows by volume, reversibility and data sensitivity, because order status and ticket intake carry far less risk than payments.
- Write actions need confirmation, server-side validation, a named owner and an audit log before launch.
- Server-side MCP and WebMCP solve different problems, so most enterprise agent programs will run both.
The Returns Form an Agent Has to Guess At
Picture a customer who asks the AI assistant in her browser to return a damaged kettle. The assistant then opens your returns page and starts reading the screen. It has to work out which box holds the order number, which dropdown sets the reason and which of three buttons actually submits.
Every one of those guesses can go wrong. A redesigned page or a slow script can send the agent to the wrong field. When that happens, the customer gives up and calls support anyway.
Now picture the same page with a declared tool called request_return. This tool says what it does, lists the two inputs it needs and describes valid values. So the agent calls it with an order number and a reason, the form fills itself in front of the customer, and she clicks Submit. Nothing was guessed. That shift, from screen-reading to a published contract, is what a WebMCP implementation buys you.
What Is WebMCP, and What It Is Not
WebMCP is a way for a website to tell AI agents exactly what it can do. Instead of leaving an agent to infer purpose from buttons and fields, the page registers named tools that the agent can discover and call.
Chrome’s documentation calls it a proposed web standard for exposing structured tools to agents. Under the hood, the page uses a browser API on document.modelContext, as defined in the WebMCP draft specification. Because tools run inside the visible page with the user’s own session, the customer can watch what happens.
WebMCP is not a back-end protocol or a crawler feed. Agents learn about tools only when they visit the page. Chrome built the API for a person working in a browser with an assistant beside them.
What WebMCP Means for SEO and AI Search
Marketing teams often ask whether tools help a site rank or get cited in AI answers. There is no published evidence that WebMCP affects search rankings or AI search citations. The discovery model explains why: tools exist only while a page is open, so no search index can read them.
Search and AI visibility still bring the visitor, so keep pages crawlable and clearly written as before. WebMCP works one step later, once an assistant has landed and needs to finish a task. Judge it on task completion and agent-session share, which the measurement section below covers, rather than on traffic.
The Tool Contract
Every WebMCP tool is a small contract between your page and the agent. When the contract is precise, the agent behaves predictably; when it is vague, you are back to guessing. In practice, each tool has five parts.
- Name: a short, stable identifier such as
get_order_status. - Description: when to use the tool and what comes back, for example “Look up one of the signed-in customer’s orders. Returns status, carrier and delivery date.”
- Input schema: a JSON Schema object that lists parameters, types, allowed values and required fields, such as an
orderNumberstring of exactly eight digits. - Execute function: the page code that returns a result, such as fetching the order and opening the order panel.
- Annotations (optional): hints, all false by default:
readOnlyHint(the call changes nothing),untrustedContentHint(the output may carry third-party text) andconsequentialHint(the call does something hard to undo), plus adebuggingflag. Security and Governance below covers how to use them.
Two Things Called WebMCP
Search results often mix two different projects under one name, especially in older tutorials. The earlier one is the open-source MCP-B project (originally MiguelsPizza/WebMCP, with packages under @mcp-b), which polyfilled navigator.modelContext before the browser specification took shape. This guide covers the specification developed in the W3C Web Machine Learning Community Group, which Chrome and Edge implement.
That difference matters when you copy code from older tutorials. Many of them show navigator.modelContext, while the current spec defines the API on document.modelContext. The practical rule is to feature-detect document.modelContext and treat navigator-based samples as outdated.
Where WebMCP Stands in November 2026
WebMCP status changes month to month; the table reflects the primary sources as of November 13, 2026.
| Item | Status |
|---|---|
| Specification | Draft Community Group Report; not a W3C Standard and not on the Standards Track |
| Chrome local testing | Flag at chrome://flags/#enable-webmcp-testing |
| Chrome origin trial | Sign-up open from Chrome 149, announced June 9, 2026 |
| Edge origin trial | Open, with an expiration date of March 30, 2027 |
| Frameworks | Experimental support in React, Angular and Vue |
| Debugging | Chrome DevTools shows how the browser parses each JSON Schema |
| Tool removal | As of Chrome 153, a tool can be unregistered without breaking in-flight executions |
Sign-up details are in Google’s WebMCP origin trial announcement and on Microsoft’s Edge WebMCP origin trial page. The agentic browsers that call these tools are evolving at a similar pace, so plan for change on both sides.
WebMCP vs MCP Servers vs Browser Automation
Enterprises can connect an agent to a web application in three ways, and each layer fits a different job. Your choice depends on where the agent runs, whose credentials it uses and whether a person is watching.
Server-side MCP connects AI applications to tools and data through servers you host, so no browser is needed. Browser automation drives the interface the way a person would, with clicks and keystrokes. WebMCP sits between them, since the page itself publishes tools and the agent calls them inside the user’s live session.
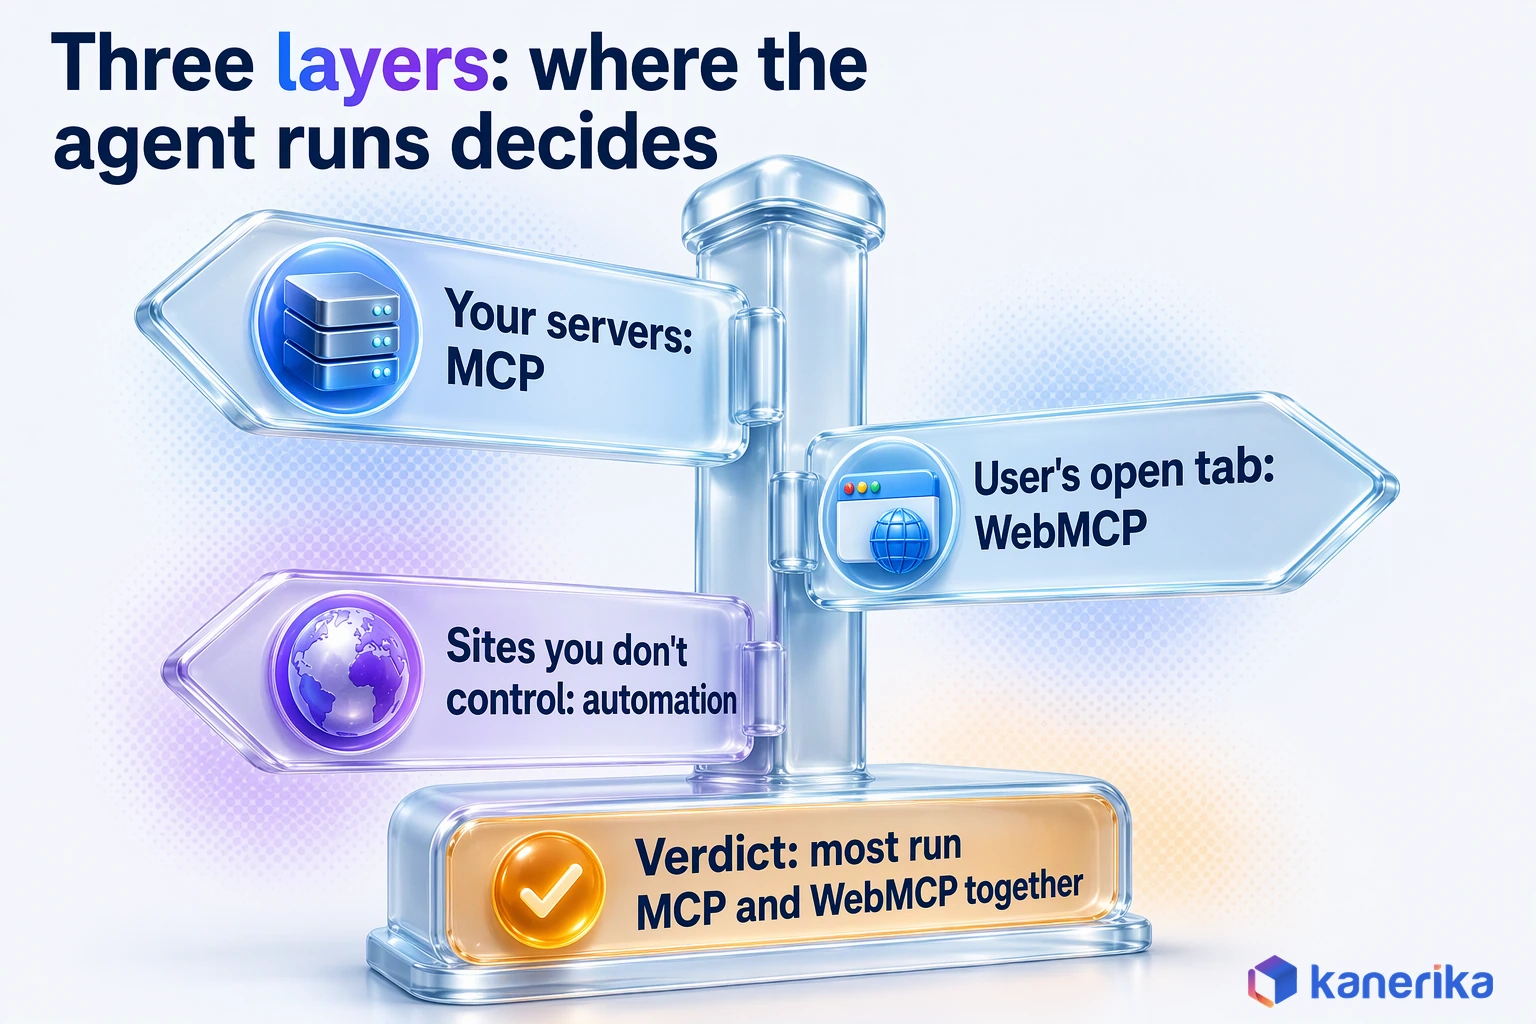
Take the support portal from the opening. Order-status data syncs into the CRM through a server-side MCP server, with no browser involved. The customer’s return happens through a WebMCP tool on the returns page, while she watches the form fill. A carrier’s tracking site that you do not own still needs browser automation, because nobody there has published tools for your agent.
| Layer | Where it runs | Auth model | Best for | Weak spot |
|---|---|---|---|---|
| Server-side MCP | Your servers | Service credentials or OAuth per client | Back-end data and actions, no browser needed | Separate auth and hosting for every server |
| WebMCP | The user’s browser tab | The user’s existing session | In-page tasks with a person present | Works only while the page is open |
| Browser automation | A scripted or agentic browser | Stored or user credentials | Sites you do not control | Breaks when the layout changes |
For MCP fundamentals, read our guide to the Model Context Protocol, now governed by the Linux Foundation’s Agentic AI Foundation. See MCP vs A2A for how agents talk to each other. Retrieval-heavy designs such as agentic RAG usually call server-side tools, while WebMCP covers the actions a user takes on your pages. In practice, most enterprise agent programs end up running server-side MCP and WebMCP side by side.
How a WebMCP Tool Call Works, Step by Step
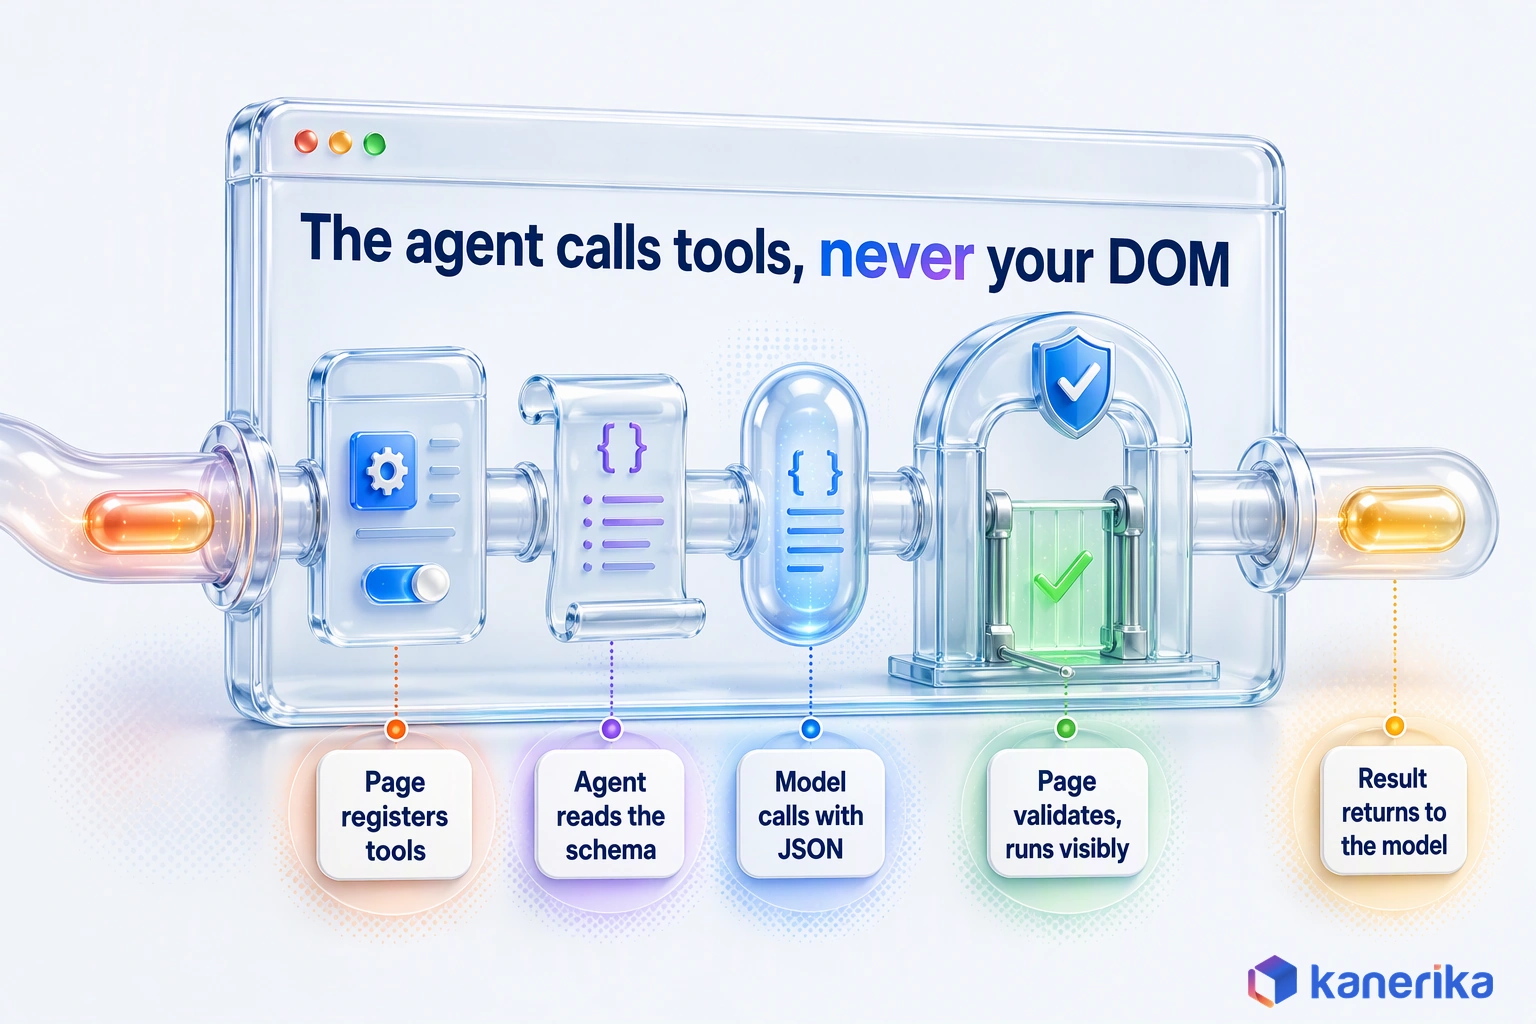
A tool call follows the same short loop every time, so it is easy to reason about and test. The agent never touches your DOM directly; instead, it talks to the browser, and the browser talks to your page.
- Register: On load, the page registers its tools with
registerTool()or through annotated forms. - Discover: When the agent arrives, it asks the browser which tools the page offers and reads each name, description and schema.
- Call: The model then picks a tool and sends arguments as JSON that should match the schema.
- Validate and run: Your page checks the arguments and runs the execute function in the visible tab, updating the interface as it goes.
- Return: The result goes back to the model as text or structured data, so the agent can decide its next step.
Forms add one detail. When an agent triggers a declarative form, the submit event carries agentInvoked set to true, so your code can tell agent sessions from human ones.
The agent in this loop is often one of the conversational AI assistants your customers already use. Each tool must therefore make sense to a general model. WebMCP gives that assistant hands, while planning, memory and policy live elsewhere in your AI agent architecture and the agent frameworks built on it. Keeping those concerns apart lets a front-end team ship tools without rebuilding the agent.
Imperative or Declarative: Choosing the Integration Pattern
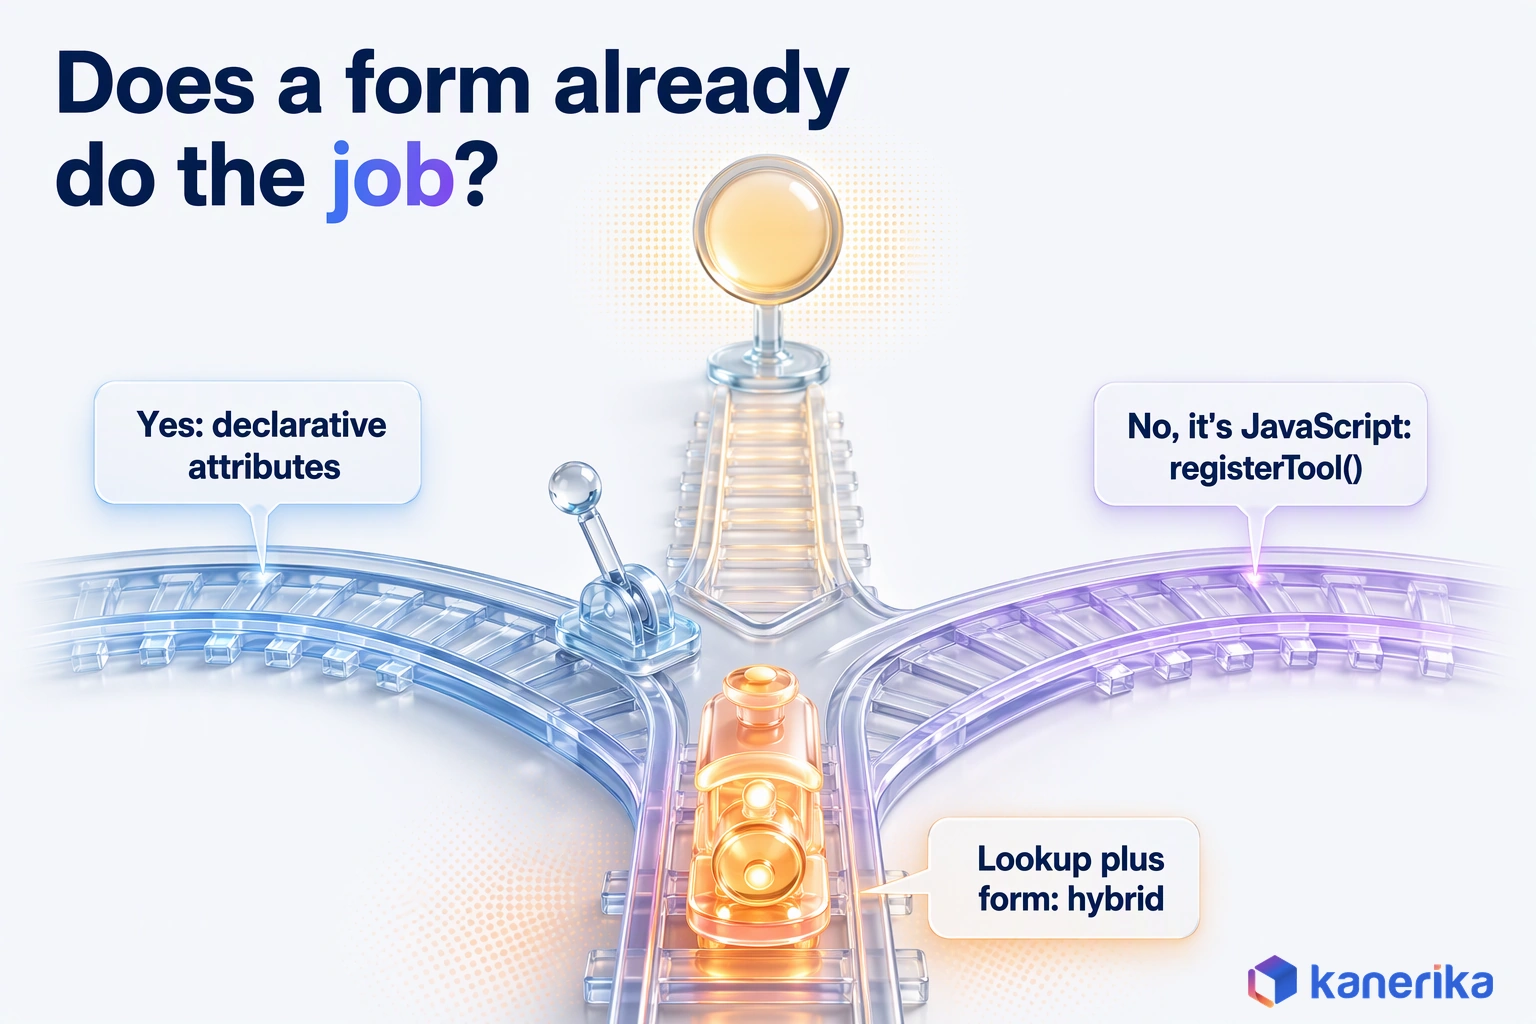
WebMCP gives you two ways to expose a tool, and the right one depends on what already exists on the page. If a form already does the job, annotate the form; if the job lives in JavaScript, register a function.
With the declarative API, you add toolname and tooldescription attributes to an existing HTML form. The browser then builds the JSON Schema from the fields, labels and an optional toolparamdescription on each input. The imperative API instead calls registerTool() with a schema and an execute function you write. That suits searches, filters and multi-step app logic especially well.
| Pattern | Effort | Best for | Watch out for |
|---|---|---|---|
| Declarative | Low: attributes on markup you already ship | Contact, support, quote and return forms | Labels that make sense to people but not to a model |
| Imperative | Medium: schema plus an execute function | Search, filters, order lookups, app state changes | Interface not updating after the tool runs |
| Hybrid | Medium | Flows that start with a lookup and end in a form | Two tools that overlap in purpose |
Single-page apps deserve extra care. Chrome’s documentation warns that highly complex interfaces may need refactoring to handle application state, so budget for that work before you promise a date.
Worked Example: An Order-Status and Return-Request Tool
A support portal, where AI agents for customer support already handle routine requests, is a good place to see both patterns working together. Here the first tool reads data and changes nothing, while the second fills a form that the customer still submits. Both samples are illustrative, so they are trimmed for clarity, and both follow the Chrome API documentation.
// Illustrative: a read-only order-status tool (imperative API)
const controller = new AbortController();

await document.modelContext.registerTool({
  name: "get_order_status",
  description: "Look up one of the signed-in customer's orders by order number. Returns status, carrier and expected delivery date.",
  inputSchema: {
    type: "object",
    properties: {
      orderNumber: { type: "string", pattern: "^[0-9]{8}$", description: "Eight-digit order number from the confirmation email" }
    },
    required: ["orderNumber"]
  },
  annotations: { readOnlyHint: true },
  execute: async ({ orderNumber }, { signal }) => {
    const res = await fetch(`/api/orders/${orderNumber}`, { signal });
    if (!res.ok) return "No order found for that number.";
    const order = await res.json();
    showOrderPanel(order); // keep the visible page in sync
    return `Order ${orderNumber}: ${order.status}, ${order.carrier}, due ${order.eta}`;
  }
}, { signal: controller.signal });
Its description tells the model what comes back, which cuts wasted calls. The schema pattern rejects anything that is not an eight-digit number before your API sees it. With readOnlyHint set, the agent knows the call has no side effects, and the signal lets a user cancel a slow lookup. Calling controller.abort() later removes the tool, for example when the customer signs out.
Talk to Kanerika
Planning a WebMCP Pilot?
Kanerika can help you pick the first workflows, design the tool contracts and set the controls, so your pilot ships small, safe and measurable.
Schedule a Demo →<!-- Illustrative: a return request the customer confirms (declarative API) -->
<form id="return-form" action="/returns" method="post"
toolname="request_return"
tooldescription="Start a return for one item in a delivered order. The customer reviews and submits.">
<label for="order">Order number</label>
<input id="order" name="orderNumber" required>
<select name="reason" required toolparamdescription="Why the customer is returning the item">
<option value="damaged">Arrived damaged</option>
<option value="wrong_item">Wrong item</option>
<option value="not_needed">No longer needed</option>
</select>
<button type="submit">Review and submit return</button>
</form>
<script>
const form = document.getElementById("return-form");
form.addEventListener("submit", (e) => {
e.preventDefault();
const done = submitReturn(new FormData(form)); // your existing handler, returns a Promise
if (e.agentInvoked) e.respondWith(done); // the agent receives the result
});
</script>This form has no toolautosubmit attribute, and that is deliberate. The agent fills the fields, then the browser brings the form into focus, and the customer clicks the button herself. Once she does, respondWith() hands the outcome back to the agent, so it can quote the return number instead of guessing whether it worked.
Decision Framework: Which Workflows to Expose First
The first two or three tools decide whether a pilot earns a second phase, so pick them with a score rather than a hunch. A short scoring pass keeps the first release small, safe and easy to measure.
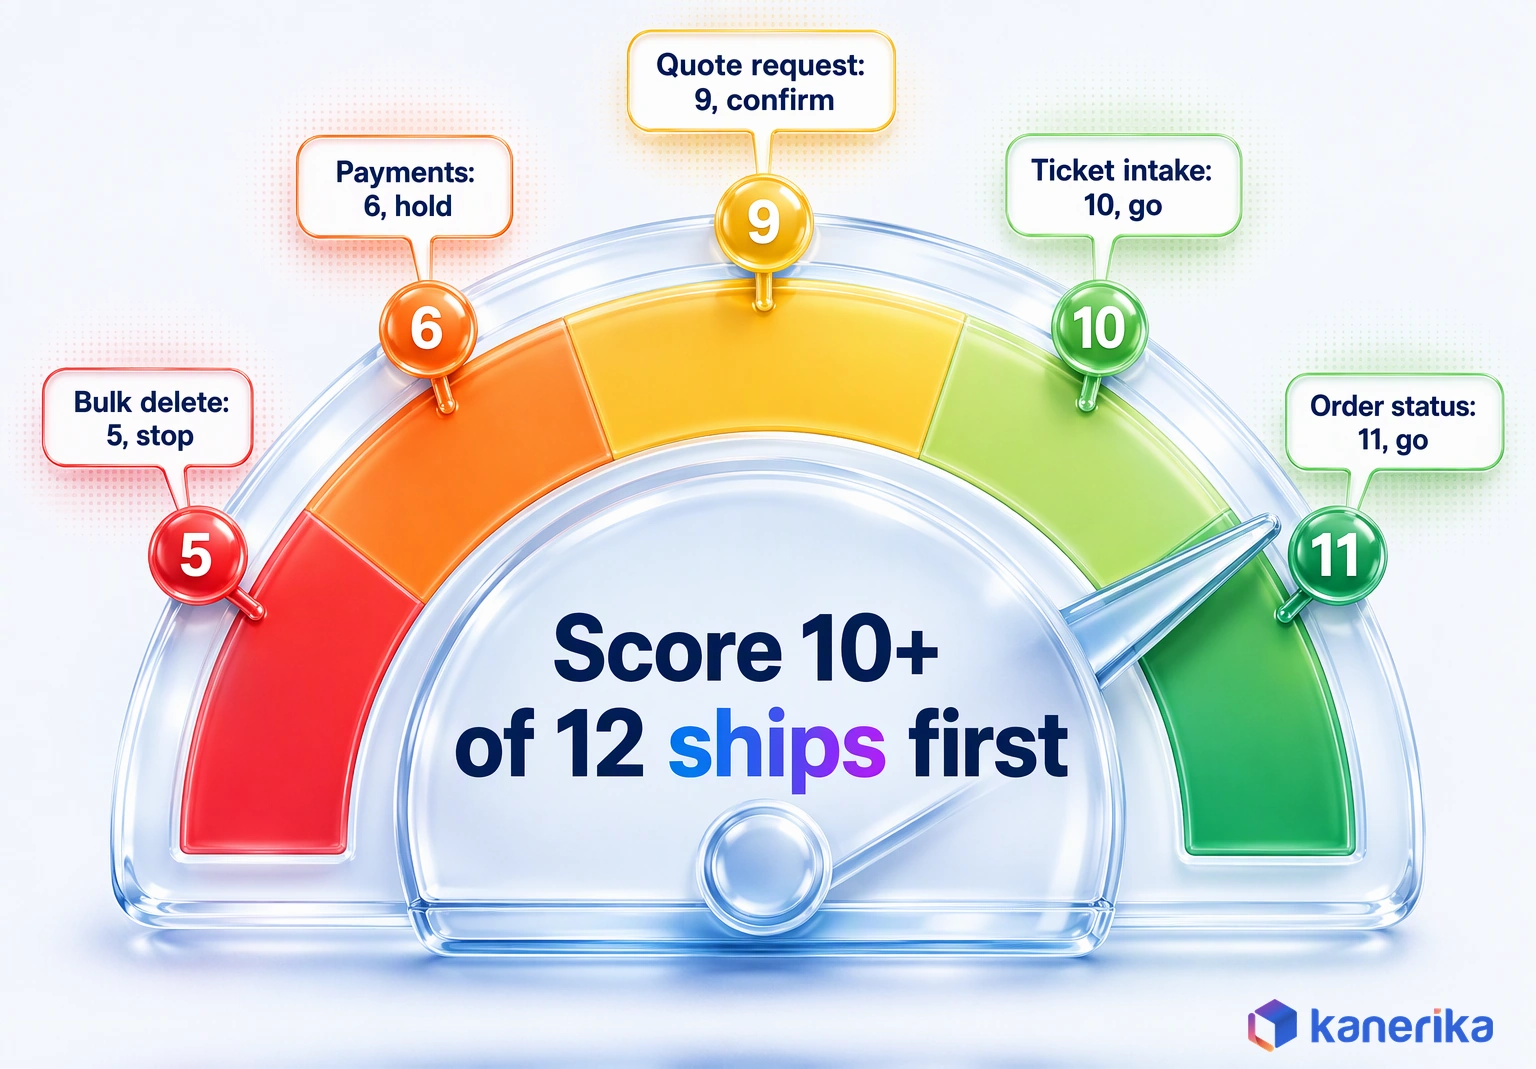
Score each candidate from 1 to 3 on four factors. These are request volume, reversibility (3 means read-only), data sensitivity (3 means low) and whether front-end logic already exists. Every factor is scored so that higher means safer or cheaper to ship, which is why a high total is a go. A total of 10 or more is a go, while 8 or 9 is a go with user confirmation. Anything at 7 or below waits, and irreversible bulk actions stop regardless of score.
| Workflow | Scores (volume, reversibility, sensitivity, logic) | Total | Call |
|---|---|---|---|
| Order status lookup | 3, 3, 2, 3 | 11 | Go |
| Support ticket intake | 3, 2, 2, 3 | 10 | Go |
| Quote request | 2, 2, 2, 3 | 9 | Go with confirmation |
| Payment or account change | 2, 1, 1, 2 | 6 | Hold |
| Admin bulk delete | 1, 1, 1, 2 | 5 | Stop |
These scores are illustrative, so swap in your own traffic and risk data. The pattern still holds for most portals. Lookups and intake forms clear the bar easily, whereas anything that moves money or identity waits for stronger controls. That includes the agentic commerce flows where an agent pays on a user’s behalf. UI complexity acts as a tiebreaker, since a tangled single-page flow can double the build effort for the same score.
WebMCP Implementation Steps: From Pilot to Production
A WebMCP rollout works best as a sequence of small releases, because each one can be rolled back. Each step below produces something you can review before the next one starts.
- Inventory workflows: List the tasks customers or staff repeat on your web app, with monthly volume and completion rates. Then score them with the framework above and keep two or three.
- Design the tool contract: Write the name, description and JSON Schema for each tool before any code. Review them with product and security owners, just as you would an API change.
- Implement: Start declarative wherever a form exists, and use the imperative API for lookups and app logic. TypeScript projects can also add the
webmcp-typesnpm package. - Test: Turn on the Chrome testing flag, check each schema in DevTools and execute tools directly. After that, run task-level AI agent evaluations on realistic requests with an agent, such as Chrome’s example WebMCP extension or an open-source local agent (see how the OpenClaw architecture routes tool calls).
- Release to a trial cohort: Register for the Chrome or Edge origin trial and ship to a limited audience. Keep the human path untouched, so customers without an agent see no change.
- Measure and expand: Compare agent sessions with human sessions on the same flows. Add a tool only when the first ones meet their targets.
Teams that skip step two usually pay for it later, in step four. Vague descriptions produce wrong calls, and a wrong call is far harder to debug than a schema review is to run.
Checklist
Agentic AI Readiness Checklist
Use Kanerika’s agentic AI readiness checklist to confirm data access, permissions, oversight and success metrics before you expose tools to agents.
Get the Checklist →Security and Governance for WebMCP Tools
A WebMCP tool is a new entry point into your application, so it deserves the same scrutiny as a public API. Here the caller is a language model acting for a user, which adds risks your existing controls may not cover.
Prompt Injection and Untrusted Output
The OWASP LLM01:2025 entry on prompt injection describes indirect attacks that arrive through external content such as websites. A tool that returns product reviews, forum posts or support tickets can carry hidden instructions straight into the model. Mark those tools with untrustedContentHint: true so the agent and browser treat the payload with extra care. Also keep the returned text as short as the task allows, and red-team each such tool with planted instructions before launch.
Consequential Actions and User Confirmation
Some tools change things that cannot be undone, such as placing an order or deleting a record. Set consequentialHint: true on those, so agents and browsers can require a confirmation prompt. On declarative forms, leave toolautosubmit off, because then the customer stays the one who presses Submit. Which actions count as consequential is a policy call, so record it in your agentic AI governance rules rather than in each developer’s head.
Permissions Policy, HTTPS and Iframes
Both APIs are gated by a tools permissions policy that defaults to self. Tools therefore register in top-level and same-origin frames but stay disabled in cross-origin iframes, unless the parent page adds allow="tools". The API also runs only in secure contexts, so every page that registers tools must load over HTTPS.
Logging, Ownership and Audit
Log every agent-invoked call with the tool name, arguments, result and user session, so incidents can be traced. One record per call is enough, and it can be as plain as the illustrative entry below.
// Illustrative: one log record per agent-invoked call
{
  "tool": "request_return",
  "schemaVersion": "1.2",
  "agentInvoked": true,
  "session": "s-7f3a91",
  "args": { "orderNumber": "40418822", "reason": "damaged" },
  "result": "submitted_by_user",
  "owner": "returns-team"
}
Records like this feed the same AI agent observability stack you use for other agents. Name one owner per tool, and treat a schema change like an API change, with review and a changelog. For the wider control set, our guides to agentic AI risks and the LLM gateway pattern cover policy enforcement across many agents.
| Risk | Control |
|---|---|
| Injected instructions in returned content | untrustedContentHint, short outputs, output sanitizing and AI guardrails |
| Agent takes an unintended action | consequentialHint, no toolautosubmit, confirmation dialog |
| Malformed or hostile arguments | Strict schemas plus server-side validation on every call |
| Third-party frame registers tools | Default tools policy; grant allow="tools" only to vetted frames |
| No trail after an incident | Per-call logs, a named owner, versioned schemas |
None of these controls is exotic. They are the same habits a mature API program already follows, applied to a caller that reads instructions as well as data.
Effort and Cost: Sizing a WebMCP Pilot
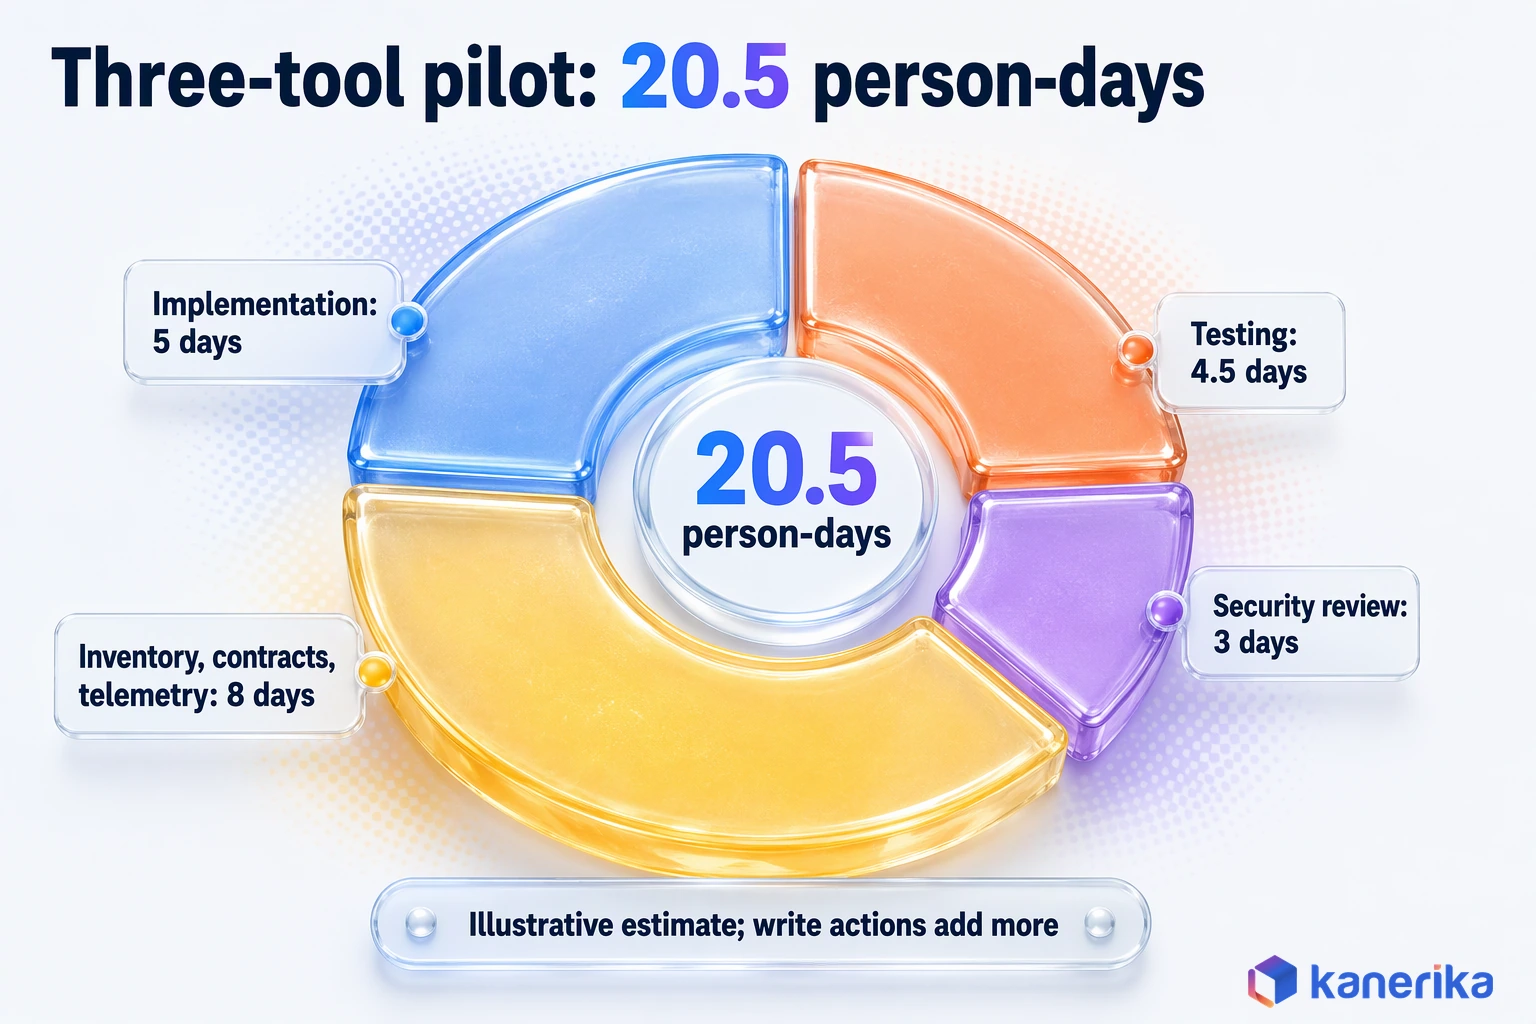
Budget conversations go faster when the estimate is built from deliverables rather than a headline number. The figures below are an illustrative model for one support portal, not a quote or a benchmark, so replace each assumption with your own.
Assume a pilot of three tools: two imperative read-only lookups and one declarative return form. The team also has one front-end engineer, a part-time product owner and a security reviewer. All three flows have working front-end logic already, so no refactoring is needed.
| Deliverable | Assumption | Person-days |
|---|---|---|
| Workflow inventory and scoring | One short workshop plus analysis | 3 |
| Tool contracts and schemas | 3 tools at 1 day each | 3 |
| Implementation | 2 imperative tools at 2 days, 1 declarative form at 1 day | 5 |
| Testing and agent evaluations | 3 tools at 1.5 days each | 4.5 |
| Security review | Threat model, policy and logging check | 3 |
| Telemetry and dashboard | Events plus one KPI view | 2 |
| Total | 20.5 |
At about 20 person-days, that pilot fits roughly two sprints for a small team, provided that scope holds. Three things push the number up quickly. A single-page app that needs state refactoring adds engineering time, and each write action adds confirmation design, server checks and more review. Regulated data also brings privacy and compliance sign-off, which often sets the real calendar.
Once the pilot grows into a product, Kanerika’s AI application development team typically handles the front-end build alongside agent design.
Measuring a WebMCP Rollout
A pilot is only useful if it answers a clear question: do agents finish real tasks on your site more reliably than before? So pick a small set of metrics, capture a baseline in the first week, and compare agent sessions with human sessions on the same flows.
| KPI | What it tells you | Signal to capture |
|---|---|---|
| Tool-call success rate | Whether calls return a valid result | Execute results and errors per tool |
| Task completion rate | Whether the user’s goal was met, agent versus human | Funnel completion by session type |
| Error and cancel rate | Where tools confuse the agent or the user | toolcancel events, validation failures |
| Agent-session share | How much traffic arrives through agents | agentInvoked on form submits, toolactivated events |
| Deflection or conversion | Business value on exposed flows | Support contacts avoided, quotes or orders completed |
Read the metrics as a set rather than one at a time. High call success with low task completion usually signals a description problem, because the agent picked the right tool for the wrong job. A rising cancel rate on one tool is also a design signal worth acting on before you add more.
AI Assessment
How Ready Is Your Organization for AI Agents?
Take Kanerika’s AI maturity assessment to see whether your data, processes and governance are ready before agents start acting on your web apps.
Start Your AI Assessment →Common WebMCP Implementation Mistakes
Early pilots tend to fail in predictable ways, and almost all of them trace back to scope or contract design. Each mistake below also has a simple fix.
- Too many tools at once: Agents choose worse when a page offers dozens of overlapping tools, so start with two or three.
- Vague descriptions: “Handles orders” tells the model nothing, so say what the tool does, what it needs and what it returns.
- Write actions first: Leading with payments or account changes raises risk before you have data, so ship read-only tools first.
- No server-side validation: The schema guides the model but does not protect you, so validate every argument on the server as well.
- A stale interface: If a tool changes state but the page does not refresh, users lose trust, so update the visible UI inside the execute function.
- Treating a trial as production: Origin trials end and APIs change, so keep the human path complete and track the spec.
How Kanerika Delivers WebMCP and Agent Integration
Kanerika approaches a WebMCP implementation the same way it delivers other agent work. It starts narrow, proves value on real traffic and only then widens the scope with governance in place. The method, delivered through its agentic AI services, runs in four stages so that risk grows only with evidence.
- Assess and pick workflows: Map candidate tasks, score them with the decision framework, and then agree on success metrics.
- Read-only pilot: Build two or three lookup and intake tools, test them with agents and then release to a trial cohort.
- Harden and add approved actions: Add confirmation, logging, server checks and an owner for each new write tool before it goes live.
- Expand and operate: Grow tools on measured completion, coordinate with back-end agents through AI agent orchestration, and review schemas as the spec moves.
Kanerika has not yet published a WebMCP case study, so the closest precedent is a support agent project. Kanerika built an LLM-driven ticket response system for a B2B SaaS company, and the results are in the card below.
It fits because support flows are the first WebMCP use case Chrome lists. That project rested on a clean knowledge base, prepared historical tickets and a rollout measured step by step. A WebMCP support pilot needs the same three things: accurate data behind each tool, real past requests to test against and a metric gate before each new tool goes live.
Case Study
80% Ticket Auto-Resolution with LLM-Driven AI
A B2B SaaS company serving SMB clients in 40+ countries used an LLM-driven ticket response system from Kanerika to auto-respond to 80% of tickets and cut resolution time by 50%.
Read the Case Study →Should You Implement WebMCP Now?
Yes for a pilot, and not yet for production write actions. The specification is still a draft, browser support is a trial, and the agents that call tools keep changing. That combination rewards small, reversible experiments and punishes big commitments.
Before you launch, check six things.
- Two or three workflows scored and approved, all read-only or confirm-to-submit.
- Tool names, descriptions and schemas reviewed like an API change.
- Server-side validation on every argument, since schemas only guide the model.
- Hints set where they apply, such as
readOnlyHint,untrustedContentHintorconsequentialHint. - Per-call logging and a named owner for each tool.
- A baseline for task completion and cancel rates.
So, should your enterprise start a WebMCP implementation in 2026? Yes, as a read-only pilot on two or three high-volume workflows, with write actions held until the spec and your own metrics say they are ready.
Frequently Asked Questions
What is WebMCP and how does it differ from traditional API integration approaches?
WebMCP is a browser API that lets a web page register tools with a name, description and JSON Schema for AI agents to call. A traditional API integration needs a separate back-end endpoint and credentials for each agent. WebMCP reuses the page, the user’s signed-in session and the front-end logic you already run.
Which browsers currently support WebMCP implementation?
As of November 2026, Chrome offers WebMCP through an origin trial that opened with Chrome 149, plus a local testing flag for developers. Microsoft Edge runs its own origin trial with an expiration date of March 30, 2027. No browser ships WebMCP on by default yet, so build it as a progressive enhancement over your normal pages.
Can WebMCP tools run inside a cross-origin iframe?
Yes, but only with permission from the embedding page. The tools permissions policy defaults to self, which allows registration in top-level and same-origin frames and disables it in cross-origin iframes. The parent page must add an allow attribute set to tools on the iframe element, and you should grant that only to frames you have vetted.
Should enterprises adopt WebMCP now or wait?
Enterprises should pilot now and wait on bigger commitments. Run a read-only pilot on one or two high-volume workflows through the Chrome or Edge origin trial, and keep the human path unchanged. Hold production write actions such as payments or account changes until the specification stabilizes and your own completion metrics justify them.
What are the primary security considerations for enterprise WebMCP deployment?
Validate every tool argument on the server, mark state-changing tools as consequential and keep user confirmation for purchases or submissions. Flag tools that return reviews or other user content as untrusted to limit prompt injection. Keep the tools permissions policy at its default, serve pages over HTTPS and log every agent-invoked call for audit.
What industries benefit most from WebMCP implementation?
Industries with high-volume, form-heavy web workflows see the clearest fit. Examples include retail order lookups and returns, travel booking, insurance quote and claims intake, banking service requests and B2B support portals. The deciding factor is the workflow, so score each task on volume, reversibility and data sensitivity before you pick an industry use case.
How does Kanerika approach a WebMCP implementation?
Kanerika starts with a workflow assessment that scores candidate tasks and agrees on success metrics. It then builds a read-only pilot of two or three tools and releases it to a trial cohort. Approved write actions follow with confirmation, logging and named owners, and the tool set grows only as measured task completion improves.
Is WebMCP the same as MCP?
WebMCP borrows ideas from the Model Context Protocol, yet the two run in different places. MCP connects AI applications to servers that expose tools and data from your back end. WebMCP is a browser API, so a web page exposes tools to an agent working in the user’s tab, using the page and the existing session.
Do I need to rebuild my website to implement WebMCP?
Usually you do not need a rebuild. The declarative API adds toolname and tooldescription attributes to HTML forms you already ship, and the imperative API wraps JavaScript functions you already have. Complex single-page apps may need some refactoring so the interface reflects state changes that agents make, which is worth scoping before you commit dates.
How do I test a WebMCP implementation?
Turn on the enable-webmcp-testing flag on Chrome’s flags page and relaunch the browser. Inspect each registered tool and its parsed JSON Schema in Chrome DevTools, then execute tools directly to confirm results. Finish with task-level evaluations, running an agent such as Chrome’s example WebMCP extension against realistic customer requests and recording completion and cancel rates.
How long does a WebMCP pilot take?
Timing depends on how many tools you build and whether the front-end logic already exists. An illustrative pilot of three tools on an existing support portal comes to about 20 person-days, or roughly two sprints for a small team. Write actions, single-page app refactoring and regulated data each add design, review and sign-off time.
Does WebMCP help SEO or AI search visibility?
There is no published evidence that WebMCP affects search rankings or AI search citations. Chrome’s documentation says agents discover tools only when they visit a page, so WebMCP is not a crawler feed. Treat it as a way to help agents finish tasks on your site, and measure completion rather than traffic.