call/text us now

+1 (855) 6-KANERI

AI Compliance and Risk Detection Agent

Catch regulatory risk as it happens, not at the quarterly review.

3x

Faster expert vetting

60%

Less manual compliance work

24/7

Continuous monitoring

Hire the AI Compliance and Risk Detection Agent for 30 Days
SOC 2

Type II certified delivery

ISO 27001

Certified security practices

250+

Technology certifications

Catch regulatory risk as it happens, not at the quarterly review.

Regulations change faster than any compliance calendar, and the cost of finding a problem late keeps rising. Kanerika builds and runs an AI compliance and risk detection agent on your own cloud that monitors transactions, content and policy changes in real time, flags what matters and keeps a human in charge of every decision. As an AI agent for compliance, it leaves your team reviewing findings instead of hunting for them.

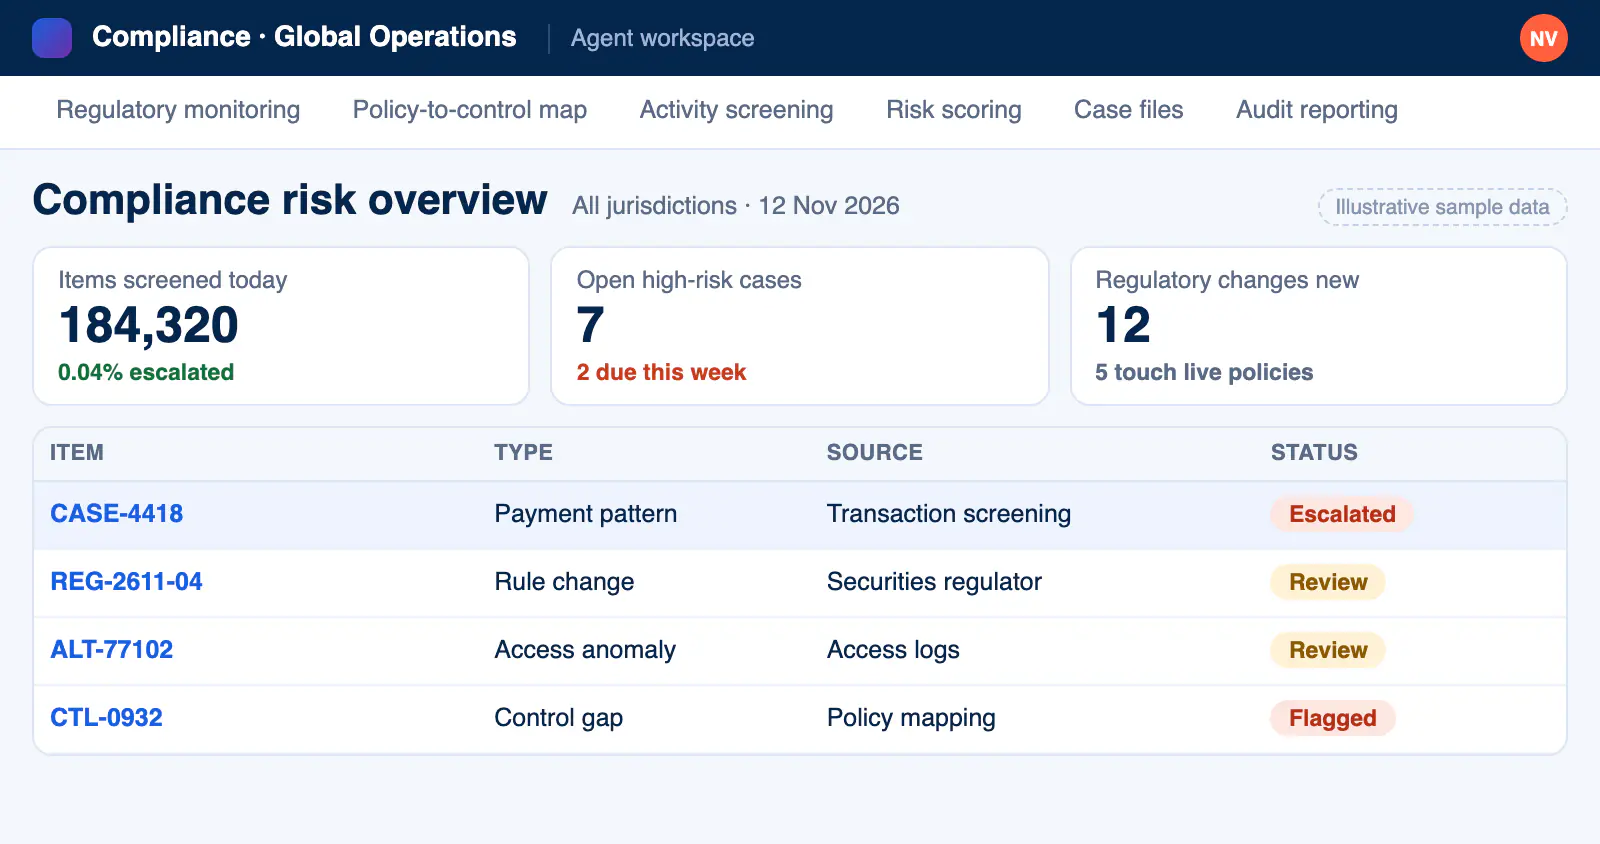
AI compliance agent interface showing continuous compliance monitoring of regulatory change

How the AI Compliance and Risk Detection Agent Works

deployed code icon

Deployed on Your Stack

Kanerika deploys the agent on your Azure, AWS, GCP or on-premises environment. Nothing moves to a third-party platform, and your security team keeps full visibility.

verified user icon

Governed and Secure by Design

Kanerika holds SOC 2 Type II, ISO 27001 and ISO 9001 credentials and is GDPR compliant. The agent inherits your access controls, classification tags and retention policies.

forum icon

Answers Where Compliance Teams Work

Alerts, case summaries and regulatory updates arrive in Teams, Slack or email. Nobody logs into yet another dashboard to find out what changed.

lock icon

Your Data Stays in Your Tenant

Transaction records, communications and policy documents never leave your environment. They are never used to train external models.

assignment turned in icon

Human Review Before Anything Is Filed

The agent drafts findings, risk scores and case files. A compliance officer approves, edits or rejects each one before it enters the record.

find in page icon

Every Flag Traced to Its Source

Each alert links back to the rule, regulation clause or data point that triggered it, so reviewers can verify the reasoning in seconds.

Compliance Monitoring: What the Agent Flags and Documents

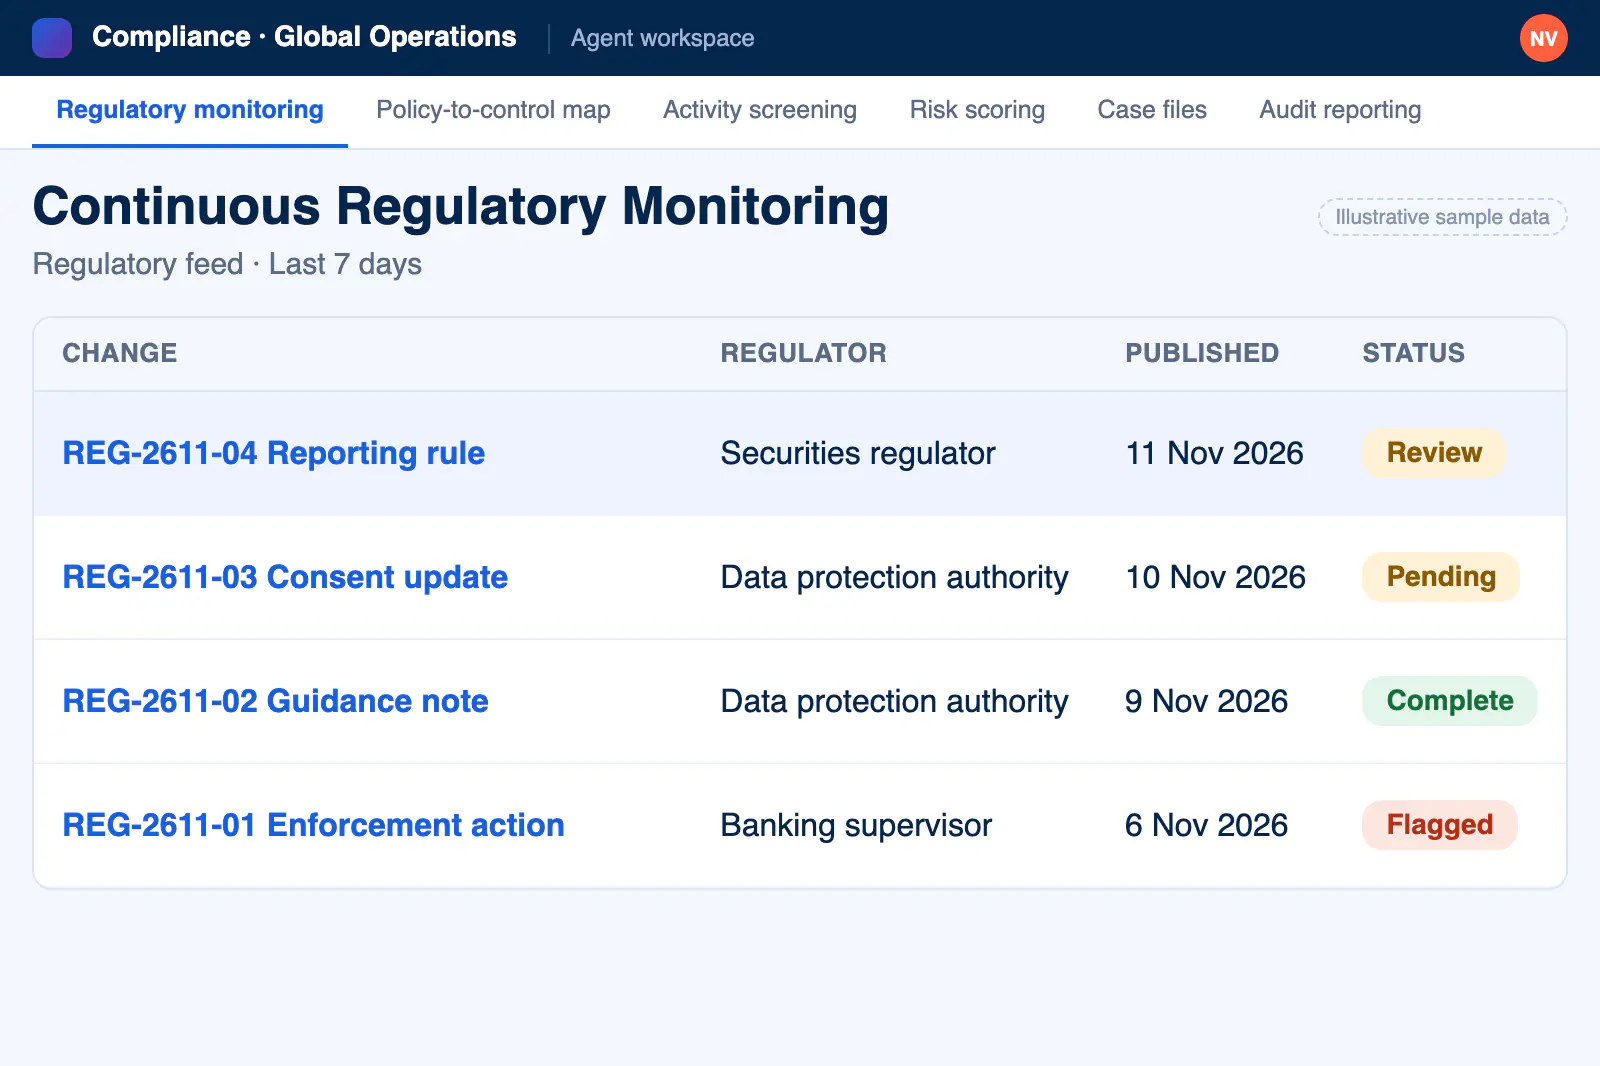
Continuous Regulatory Monitoring

The agent tracks regulator publications, rule changes and enforcement actions relevant to your business, then maps each change to the policies and controls it touches.

Compliance AI Agent screen for continuous regulatory monitoring

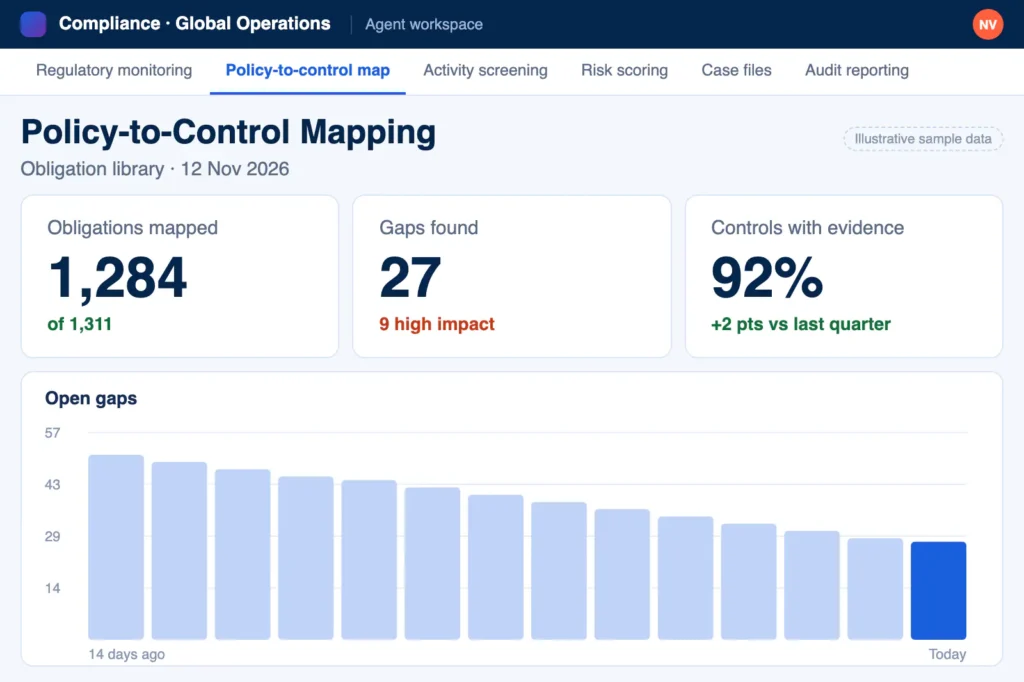
Policy-to-Control Mapping

It reads your policy library and connects every obligation to a specific control, owner and evidence source, exposing gaps before an auditor does.

Compliance AI Agent screen for policy-to-control mapping

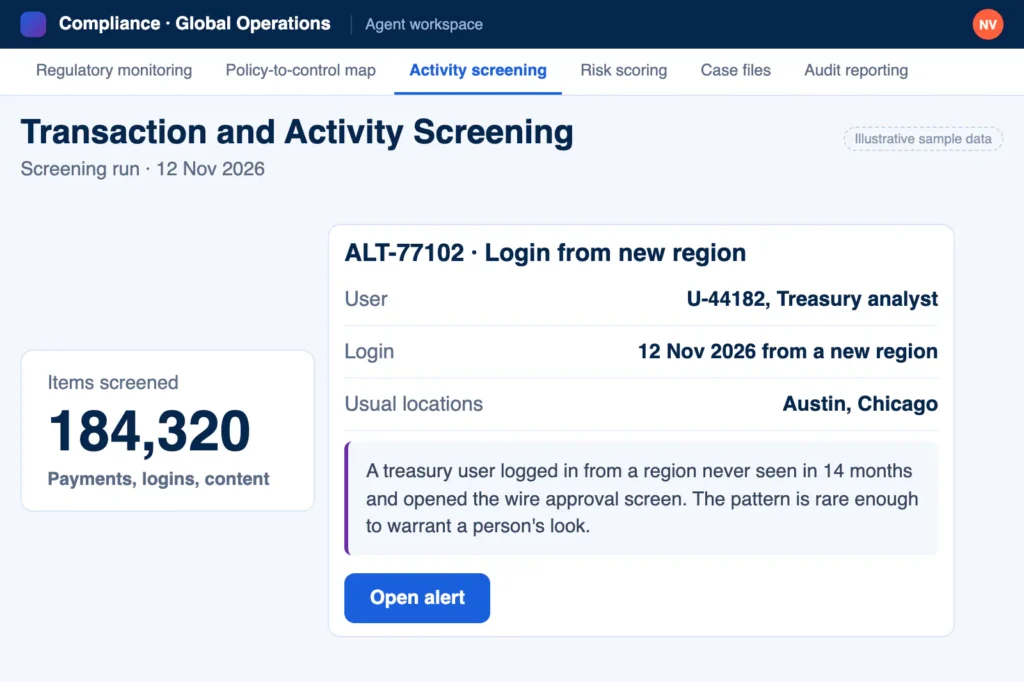
Transaction and Activity Screening

High-volume screening across transactions, access logs and submitted content surfaces the small share of activity that genuinely needs expert review.

Compliance AI Agent screen for transaction and activity screening

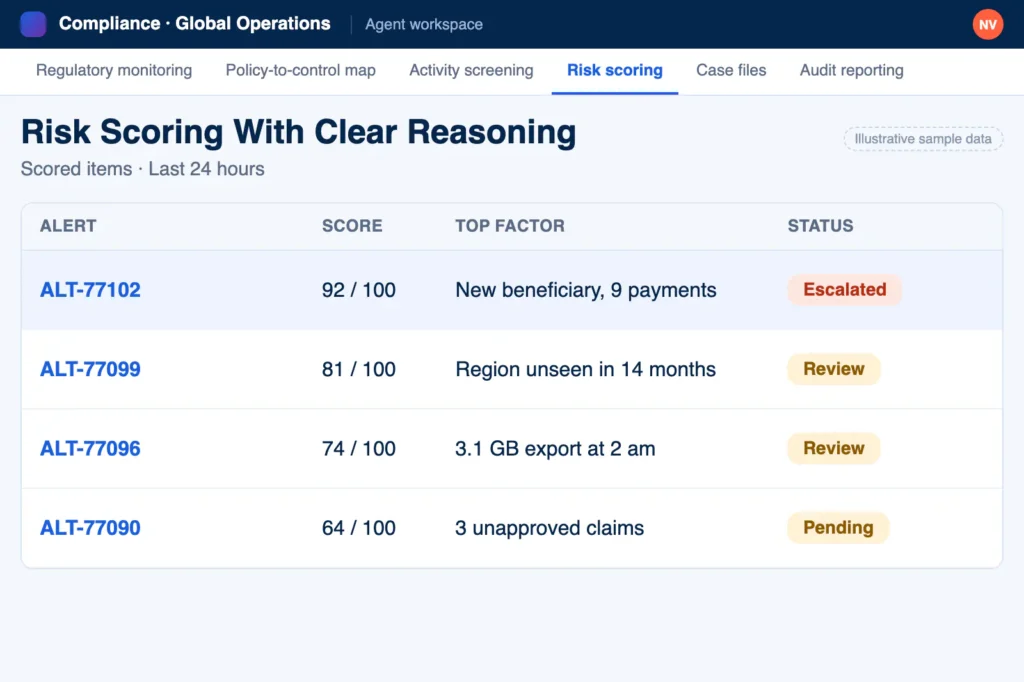
Risk Scoring With Clear Reasoning

Each flagged item carries a risk score and a plain-language explanation of why it scored that way, not an opaque number.

Compliance AI Agent screen for risk scoring with clear reasoning

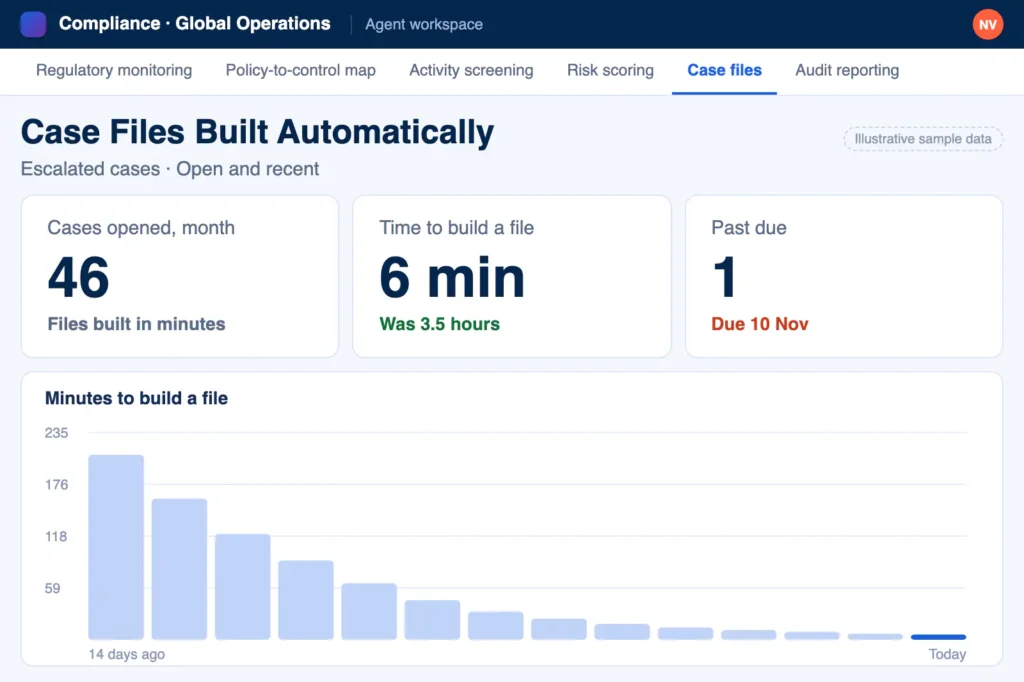
Case Files Built Automatically

When an item is escalated, the agent assembles the supporting documents, timeline and relevant policy citations into a ready case file.

Compliance AI Agent screen for case files built automatically

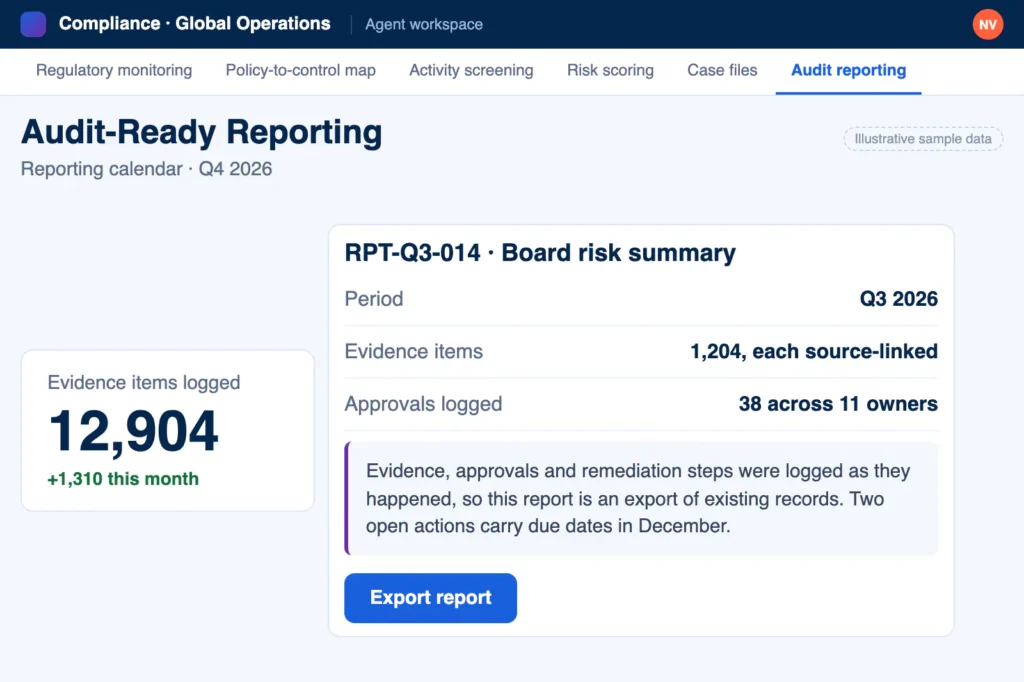
Audit-Ready Reporting

Evidence, approvals and remediation steps are logged as they happen, so audit preparation becomes an export rather than a scramble.

Compliance AI Agent screen for audit-ready reporting

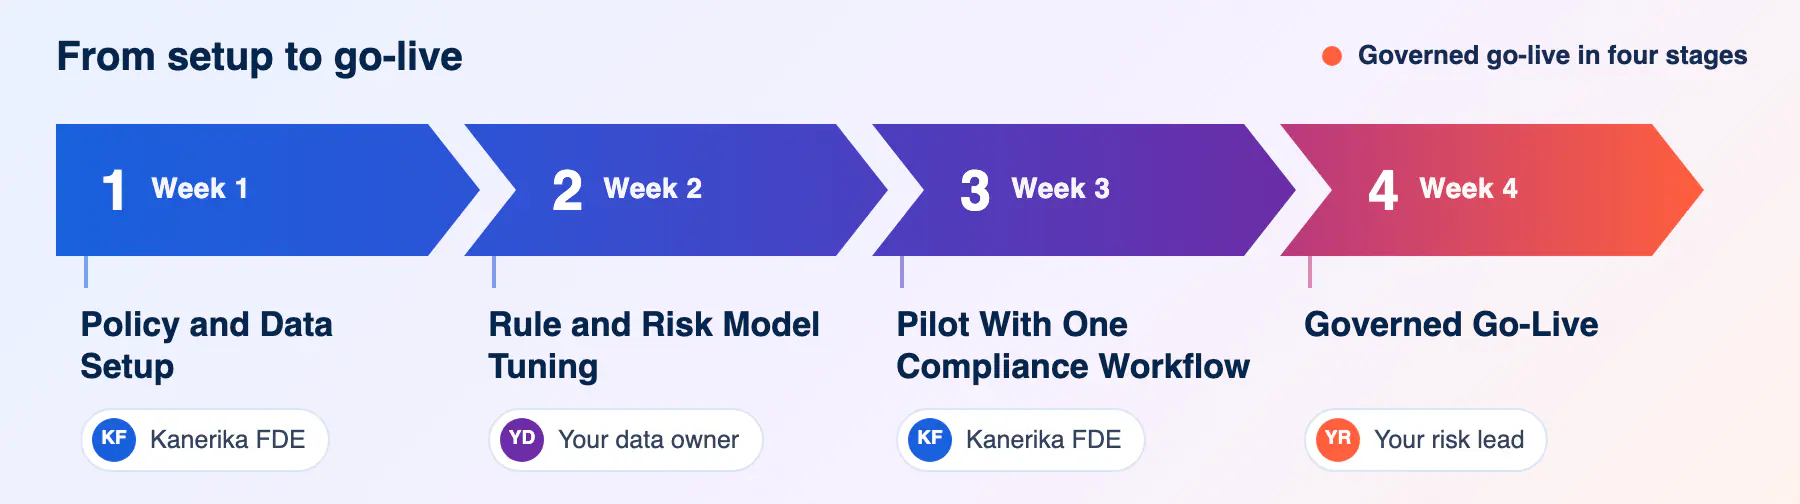
Deploy Your Compliance AI Agent in Weeks

Compliance AI Agent rollout plan from setup to governed go-live
data_table.svg

Policy and Data Setup

Kanerika connects the agent to your policy library, regulatory feeds and monitored systems, and configures access controls with your security team.

help_center.svg

Rule and Risk Model Tuning

Detection rules and risk thresholds are tuned to your risk appetite, jurisdictions and products, with your compliance leads reviewing every rule.

batch_prediction.svg

Pilot With One Compliance Workflow

A single workflow, such as content vetting or transaction screening, goes live first. The team measures precision and adjusts thresholds on real cases.

export_notes.svg

Governed Go-Live

The agent rolls out across workflows with role-based access, escalation paths and full audit logging in place from day one.

Where Compliance Teams Put the Agent to Work

update icon

Regulatory Change Management

New rules are summarized, mapped to affected policies and routed to the right owner with a deadline, replacing manual horizon scanning.

rate review icon

Expert Content Vetting

The agent screens expert content and submissions against policy before publication, so reviewers spend their time only on items that need judgment.

supervised user circle icon

Third-Party and Vendor Risk

Vendor documents, certifications and sanctions lists are checked at onboarding and re-checked on a schedule, with changes flagged automatically.

forum icon

Communications Review

Outbound communications are screened against disclosure and conduct rules, with risky drafts flagged before they go out rather than after.

verified user icon

Policy Attestation Follow-Up

The agent chases outstanding attestations and training completions, then reports exceptions to compliance leadership without manual tracking.

report icon

Incident Triage and Escalation

Reported incidents are classified, scored and routed with the supporting evidence attached, so serious matters reach the right desk fast.

Built for Regulated Industries

account balance icon

Banking and Financial Services

Screening, reporting obligations and conduct monitoring at transaction scale. See Kanerika's work in banking and financial services .

shield with heart icon

Insurance

Policyholder communications, claims conduct and state-by-state regulatory variance, covered on the insurance industry page .

local hospital icon

Healthcare

Patient data handling and documentation rules monitored continuously. More on healthcare .

medication icon

Pharma

Promotional review, submission vetting and quality documentation for pharma compliance teams.

factory icon

Manufacturing

Safety, environmental and trade compliance evidence collected where manufacturing operations run.

local shipping icon

Logistics and Supply Chain

Customs, carrier and partner compliance checks across the logistics and supply chain network.

Why Teams Choose Kanerika for Compliance Automation Software

Compliance Results from Real Kanerika Deployments

Detecting Rental Transaction Risk Early with AI-Powered Risk Intelligence

Impact:

  • ~500 Risk findings surfaced 
  • ~1.2M Financial exposure identified
  • 6 Risk categories used to classify findings

60% Less Manual Compliance Work with AI

Impact:

  • 40% Faster Regulatory Response
  • 60% Less Manual Compliance Work
  • 5X Better Audit Traceability

3x Faster Expert Vetting with an AI Compliance Agent

Impact:

  • 3X Faster expert vetting
  • 70% Decrease in backlog cases
  • 40% Reduction in event delays

FAQs

It is an AI system that monitors transactions, content, policies and regulatory changes, flags items that breach rules or thresholds, and assembles the evidence a reviewer needs. Kanerika builds and runs these agents on the client’s own infrastructure, so monitoring runs continuously while compliance officers keep final authority over every finding and escalation.

No. The agent removes the repetitive work of scanning, sorting and documenting, and your team keeps every decision. Findings arrive scored and explained, a compliance officer approves or rejects each one, and escalations follow the paths you define. In Kanerika deployments the team reviews more activity than before, with less effort per case.

The agent runs inside your own Azure, AWS, GCP or on-premises environment, deployed and operated by Kanerika’s team. Your data never leaves your tenant and is never used to train external models. Access follows your existing role-based controls, and Kanerika holds SOC 2 Type II, ISO 27001, ISO 27701 and ISO 9001 credentials.
The monitoring scope is configured to your business, so it covers the regulations, internal policies and jurisdictions you operate under. During setup, Kanerika maps your policy library and regulatory feeds to specific controls and owners. New rules and amendments are then tracked continuously and routed to the people responsible for responding to them.

Kanerika deploys the agent in weeks, not quarters. Setup connects your policy library, feeds and monitored systems, tuning adjusts rules to your risk appetite, and a pilot workflow goes live with one team. Full go-live follows once precision is proven on real cases, with governed access and audit logging active from the first day.

Every rule and threshold is tuned against your historical cases during setup, and the pilot phase measures precision before wider rollout. Each flag carries its reasoning, so reviewers can correct the agent quickly, and those corrections feed back into tuning. Over time the share of alerts worth an expert’s attention keeps rising.

Klara reviews contracts against a playbook, flags clause risks and suggests redlines, so its territory is the document on the negotiating table. The compliance and risk detection agent watches ongoing operations, transactions, content and regulatory change across the business. Many clients run both, since contract review and operational monitoring answer different questions.

Two published case studies anchor this page. A real-time compliance agent made expert vetting three times faster by catching issues before publication, and an AI regulatory management platform cut manual compliance work by 60%. Both are linked above with full detail on scope, architecture and the measured outcomes for each client.

Start with traceability: every flag should link back to the rule, regulation clause or data point that triggered it. Then check that findings arrive scored and explained, that a compliance officer approves each one before it enters the record, and that thresholds are tuned on your own historical cases. Kanerika’s AI compliance agent also runs inside your own cloud, so transaction records and policy documents never leave your tenant.

No. Governance, risk and compliance software holds your policies, controls and risk records. The agent does the continuous work around them: it tracks regulatory change, maps each change to the policies and controls it touches, screens transactions and content, and assembles evidence into case files for review. Kanerika connects it to your policy library and monitored systems during setup, and every approval and remediation step is logged for audit.

Let’s Transform Your Business

get started today

Your Free Resource is Just a Click Away!