TL;DR
A data governance maturity model rates governance from Level 1 to Level 5, and you move up by fixing the weakest dimension first. Score six dimensions, such as ownership, data quality and lineage, only on evidence you could show an auditor. Set a target level for each data domain instead of one number for the whole company.
Regulated domains such as customer, financial or patient data usually need Level 4, while most other domains do well at Level 3. Level 5 pays off only where automation saves real effort, such as high-volume sensitive data. Then climb one level at a time, with named owners, measured controls and a reassessment at the end of each 90-day cycle.
Key Takeaways
- A data governance maturity model is a five-level scale that scores how consistently governance happens, based on evidence rather than intent.
- Score six dimensions separately, such as ownership, policies, data quality, lineage, access and governance operations.
- Your real level is set by your weakest dimension, because one missing control breaks the evidence chain for the rest.
- Target a level per data domain, so regulated domains aim for Level 4 while most others stop at Level 3.
- Use a published framework such as DCAM or DAMA-DMBOK as a reference, but keep your rubric simple enough that two assessors agree.
- Move one level at a time in 90-day cycles, and prove each step with KPIs such as owner coverage and lineage coverage.
Watch on YouTube
State of Enterprise AI 2026: Data Foundations, Maturity Stages & ROI
Kanerika’s look at the State of Enterprise AI 2026 report: why data foundations decide AI results, how maturity stages differ, and where ROI appears.
The Auditor’s Question About One Customer Field
Picture a quarterly audit review at a mid-sized lender. The auditor points at the email field in the customer table and asks three questions.
Who owns this field? Who approved the people who can read it? Where does it flow after it leaves the CRM?
The governance lead knows the answers, roughly. Still, the owner is listed in a spreadsheet from two reorganizations ago, while the access list lives in a ticket queue. The lineage exists only in one engineer’s head, so none of the answers comes with proof.
Now swap the auditor for an AI agent that wants to use the same field to draft customer emails. It asks the same questions through metadata instead of a meeting, and it gets the same blank stare.
That gap between knowing and proving is what a data governance maturity model measures. This guide covers the five levels and the six dimensions worth scoring. It then shows how to run an assessment with a rubric, and how to move up one level at a time.
What Is a Data Governance Maturity Model?
A data governance maturity model is a staged scale that scores how consistently your organization governs its data, based on evidence you can produce. It turns a vague question such as “how good is our governance?” into a level you can defend and a next step you can plan.
Most models use five levels, from ad hoc work at the bottom to automated, self-improving practice at the top. Each level describes behavior, for example whether owners are named, whether policies are standard and whether controls are measured. You then score each part of your program against those descriptions, so the scores show where to invest next.
The model is a measuring tool rather than a program in itself. It sits alongside your governance framework, policies and tools, and it tells you how well they work together. If you are still drawing the line between two related disciplines, see how data governance differs from information governance before you scope an assessment.
Maturity vs Effectiveness: A Program Is Not a Level
Two words get mixed up in almost every maturity conversation. Maturity describes how repeatable and well-run a practice is, while effectiveness describes whether that practice produces the outcome you wanted.
Take access reviews, a core part of data access governance, as an example. Running a quarterly access review on every sensitive table, on schedule and with signed evidence, is a sign of maturity. A steady fall in unauthorized-access findings at audit, by contrast, is a sign of effectiveness.
You need both, because a perfectly run review that never removes anyone shows maturity without effectiveness. So when you score maturity, pair each dimension with one outcome metric. Treat a high score with flat outcomes as a warning sign.
Why Governance Maturity Matters More in 2026
Governance maturity used to be a concern for audit season only. In 2026 it matters every day, because AI systems, cloud platforms and regulators all read the same governance evidence and act on it.
Three forces push it up the agenda. First, AI agents decide what data they may use based on metadata such as owner, classification and lineage. Second, cloud data platforms enforce access through policies, so a missing classification becomes an open door. Third, boards want governance tied to business results rather than to the number of policies written.
AI Agents Read Your Governance Metadata
An AI agent cannot walk over to a data steward and ask whether a column is safe to use. Instead, it relies on the labels, owners and lineage your program has already recorded. When those are missing or wrong, the agent either refuses useful data or uses data it should never touch. That is why AI governance starts with data governance.
Regulation points the same way. Article 10 of the EU AI Act covers high-risk AI systems that are trained with data. Their training, validation and testing data must follow “data governance and management practices appropriate for the intended purpose” (EU AI Act, Article 10). So a team that cannot show who owns a dataset, or where it came from, will struggle to prove that practice exists. The same metadata also drives the access rules of an AI security framework, which decide what an agent may retrieve.
Data readiness is the other half of the story. In a Gartner survey published in February 2025, 63% of organizations lacked, or were unsure they had, the right data management practices for AI. If you are planning AI work, pair this assessment with an AI maturity model so the data side and the model side move together.
AI Assessment
How AI-Ready Is Your Data Governance?
Take Kanerika’s AI Maturity Assessment to see where your data, governance and teams stand before AI agents start reading your metadata.
Start Your AI Assessment →
Governance That Cannot Show Outcomes Fails
In February 2024, Gartner predicted that “by 2027, 80% of data and analytics (D&A) governance initiatives will fail due to a lack of a real or manufactured crisis.”
Saul Judah, a Gartner VP Analyst, added that a program “that does not enable prioritized business outcomes fails.” That is a useful test for any maturity score. A move from Level 2 to Level 3 should therefore connect to a result the business already wants. Examples include faster audit evidence, fewer reporting errors or approval for an AI use case.
So the maturity model earns its keep when every level you climb has a named business reason. Without one, the program turns into paperwork, and paperwork is the first thing cut in a budget review.
The Five Levels of Data Governance Maturity
Five levels describe how governance behaves as it grows up, from heroic individual effort to a measured, automated system. Labels vary between models, so treat the names below as common shorthand rather than a fixed standard.
What matters most at each level is its evidence tell, that is, the proof that separates it from the level below. If you cannot prove a level, you have not reached it, however good the intentions behind it.
| Level | What it looks like | The evidence tell | Next move |
|---|
| 1. Initial | Governance happens only when someone notices a problem | No named owners, so fixes live in email threads | Name owners for critical data |
| 2. Developing (Repeatable) | Some teams follow practices while others do not | An owner register exists, and a few policies are written | Standardize policies and stewardship |
| 3. Defined | One standard way of governing across domains | Council, RACI, glossary and policies applied in every domain | Measure controls |
| 4. Managed (Measured) | Controls carry targets and are reported | Evidence such as quality scorecards and lineage coverage | Automate and improve |
| 5. Optimized | Controls run automatically and improve from feedback | Policy-as-code, automated classification and monitored drift | Sustain, then extend to new domains |
What Each Level Looks Like in Practice
At Level 1, Initial, data problems get fixed by whoever is closest to them. Because there is no owner register, the same issue gets solved three times by three teams.
Owners and written policies appear in a few domains at Level 2, Developing, usually after an audit finding or a migration. Practice depends on the people involved, so it breaks when they move on.
The turning point is Level 3, Defined.
Governance follows one documented standard across domains. A council sets policy while stewards apply it, and a shared glossary means “active customer” has one meaning in finance and marketing.
With Level 4, Managed, controls carry targets, and someone reports against them. For example, you can say what share of critical data elements has quality rules and how many access reviews closed on time.
Few organizations need Level 5, Optimized, everywhere, which is why target setting matters. Controls run automatically, and the program learns from its own metrics. Classification happens as data lands, while policy changes deploy like code.
Six Dimensions to Score in a Data Governance Maturity Model
A single maturity score hides more than it shows, so assessments break governance into dimensions and score each one on its own. Six dimensions cover what auditors, regulators and AI systems actually check.
Each dimension answers one core question. Ownership asks who is accountable, while lineage asks whether anyone can trace a number back to its source. Scoring them separately shows you, for example, that access control is strong even though data quality is still ad hoc. Our guides to data stewardship and data lineage go deeper on two of them.
Some models split these six differently, and the pillars of data governance cover the same ground, so pick the split your stakeholders already recognize.
| Dimension | Core question | Evidence to collect |
|---|
| Ownership and stewardship | Who is accountable for this data? | Owner register, steward assignments and sign-offs |
| Policies and standards | Which rules apply, and are they followed? | Approved policies and an exception log |
| Data quality | Is the data fit for its use? | Quality rules, scorecards and issue tickets |
| Metadata and lineage | Can we trace a number to its source? | Catalog entries and lineage graphs |
| Access, privacy and classification | Who can see sensitive data, and why? | Classification labels and access review records |
| Governance operations | Does the program run as a routine? | Council minutes, issue workflow and roadmap |
Why Evidence Beats Opinion in Scoring
Every evidence column above lists an artifact rather than an opinion. That choice keeps the scoring honest, because what a team believes and what it can prove often differ.
Take the business glossary as an example. A team can believe its glossary is in use, yet the evidence is whether reports actually reference the glossary terms. So pull the 20 most-used reports and count how many define their main metrics with glossary terms.
If, say, only 4 of the 20 do, the glossary is published but not adopted, and the dimension scores 2 rather than 3. The same test works on every row: ask for the artifact that shows the practice in use.
Datasheet
Elevate Data Governance, Compliance and Security of Your Organization
A datasheet on how Kanerika approaches data governance, compliance and data security across ownership, classification and access controls.
Get the Datasheet →
How to Run a Data Governance Maturity Assessment
An assessment is a structured way to find your current level, compare it with where you need to be and decide what to fix first. The steps below work for one domain or a whole enterprise, although starting with one domain gives faster, more believable results.
Plan for interviews and evidence collection rather than a survey alone. A survey tells you what people think, while evidence tells you what actually happens. You need both, but only evidence sets the score.
- Scope it to a business goal. Pick the domains that matter for an outcome, such as audit readiness for customer data.
- Pick the model. Use a published framework, an internal model or a blend, then fix the level definitions before anyone scores.
- Build the questionnaire. Write three to five questions per dimension, so each one ties to a piece of evidence.
- Collect evidence. Gather artifacts such as owner registers, quality reports, lineage views and access review records.
- Score each dimension. Use the 0 to 5 rubric below, and record the evidence behind every score.
- Compare against the target. Set a target level per domain, then list the gaps.
- Prioritize, assign owners and reassess. Fix the two weakest dimensions first, then reassess at the end of each 90-day cycle.
The whole assessment is only as good as step four. When the evidence is thin, the honest score is low, even when the conversation in the room felt confident.
Checklist
Data Governance Checklist
Work through ownership, policies, quality, classification and access controls step by step, so every maturity score rests on evidence.
Get the Checklist →
A 0 to 5 Scoring Rubric With Sample Questions
A rubric keeps two assessors from giving the same team different scores. The version below maps scores 1 to 5 onto the five levels, and it adds 0 for practices that do not exist at all.
| Score | Meaning | Sample question |
|---|
| 0. Absent | No practice exists | Is there any list of who owns customer data? |
| 1. Ad hoc | Done by individuals when problems surface | When a report is wrong, who fixes it? |
| 2. Repeatable | Documented in some domains but not all | Which domains have written quality rules? |
| 3. Defined | One standard applied across domains | Does every domain use the same glossary and RACI? |
| 4. Measured | Tracked against targets and reported | What share of access reviews closed on time? |
| 5. Automated and improving | Runs automatically, then adapts from metrics | Is new sensitive data classified once it lands? |
One rule matters more than the wording of any question. Score only what the evidence proves. If a policy exists but nobody can show it in use, that dimension scores 2 at best, not 3.
To roll scores up, average the six dimension scores for a domain. Then report the lowest score next to the average, because the minimum shows the level you can actually defend.
Worked Example: Scoring a Customer Data Domain
Here is how the rubric plays out on one domain. The scores below are illustrative, made up for this example rather than drawn from any client.
| Dimension | Score | Evidence found |
|---|
| Ownership and stewardship | 2 | Owners named for the CRM tables but not for downstream copies |
| Policies and standards | 2 | Retention policy written, though no exception log |
| Data quality | 1 | Duplicates fixed by hand when sales complains |
| Metadata and lineage | 1 | No lineage from the CRM to the revenue dashboard |
| Access, privacy and classification | 3 | PII columns labeled, and a quarterly access review runs |
| Governance operations | 2 | Issues tracked in a shared inbox without target times |
The average is 11 divided by 6, or about 1.8. The lowest scores are 1, in data quality and in lineage. So the defensible level for this domain is Level 1, even though access control already sits at Level 3.
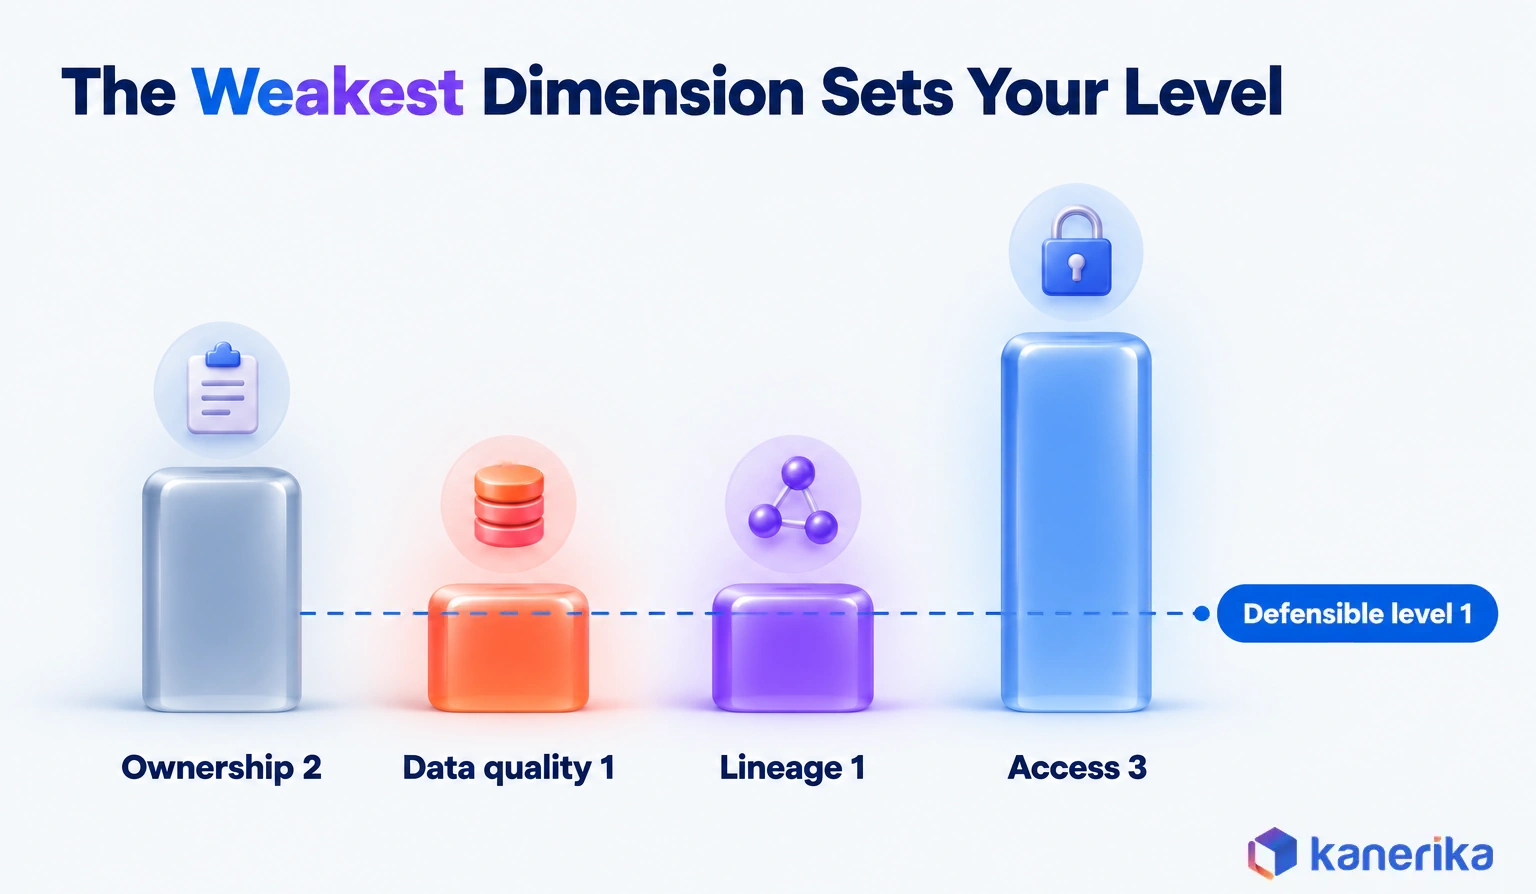
That weakest-link reading changes the plan, so the next quarter goes to the two weakest dimensions. First, the team writes quality rules for the ten customer fields behind revenue reporting. After that, it maps lineage from the CRM to the revenue dashboard.
Both fixes are small and visible, and finance already knows the cost of bad data quality in revenue reports. If the target for this domain is Level 3, the next 90 days aim to lift quality and lineage to 2 first, then to 3.
Three Ways Assessments Go Wrong
Assessments fail in predictable ways, and each one produces a score that looks better than reality. Once you know the three common errors, you can design them out before the first interview.
The first is self-rating inflation. Teams that score themselves tend to round up, especially when the result goes to leadership. So use a neutral assessor, or at least require evidence for any score above 2.
The second is scoring documents instead of behavior. A well-written policy that nobody follows is a Level 2 artifact at best. Ask for proof of use, such as a closed exception or a completed review, rather than the policy PDF.
The third is one company-wide number. A single score of 2.8 can hide both a Level 4 finance domain and a Level 1 customer domain, so score per domain. For problems outside scoring, such as funding or culture, see our guide to common data governance challenges.
Which Maturity Framework Should You Use?
A framework gives your levels and dimensions an outside reference. That helps when auditors or a board ask why your scale looks the way it does. So choose based on your industry, cloud footprint and the rigor your stakeholders expect.
Financial firms often lean on the EDM Council’s frameworks, because they were built with banks and are scored against auditable evidence. Other teams prefer to adapt DAMA’s body of knowledge into a lighter internal model. Either way, keep the level definitions stable once scoring starts, or your trend line means nothing.
Talk to Kanerika
Not Sure Which Level You Are At?
Kanerika can score one of your data domains against evidence, set a target level with its owner and map the first 90 days of fixes.
Schedule a Demo →
How the Main Frameworks Compare
The table below compares the frameworks teams most often borrow from, along with how to get access to each one.
| Framework | What it is | Best for | Access |
|---|
| DCAM v3 (EDM Council) | 8 core components and 34 capabilities, scored against auditable evidence | Banks and regulated firms that want an external benchmark | EDM Council member firms only |
| CDMC (EDM Council) | 14 key controls and automations for sensitive data in the cloud | Cloud-heavy estates with PII, client data or MNPI | Free license for internal use |
| DAMA-DMBOK | A body of knowledge whose knowledge areas many internal models borrow | Teams that build their own model on a shared vocabulary | Book and DAMA resources |
| IBM Data Governance Council model | One of the earliest five-level, multi-discipline benchmarks | Historical reference for level design | Legacy material |
| Gartner maturity research | Analyst guidance for data and analytics leaders | Gartner clients who want peer comparison | Gartner clients only |
| Internal model | Your own levels and dimensions, usually adapted from the above | Most mid-market and first-time programs | Free, but it needs discipline |
Choosing among them comes down to cost, audience and cloud exposure. DCAM goes deepest, with 101 sub-capabilities, yet its members-only access suits a bank that needs an external benchmark more than a mid-market team. That team gets most of the value by borrowing DAMA’s vocabulary, which new hires often already know. It can then add the CDMC controls if sensitive data sits in the cloud, because CDMC is free for internal use.
DAMA revised the DMBOK 2nd Edition in 2024 and started a 3.0 project in 2025, so that vocabulary is still maintained. Whatever the blend, keep the rubric simple enough that two assessors agree.
Which Maturity Level Should You Target?
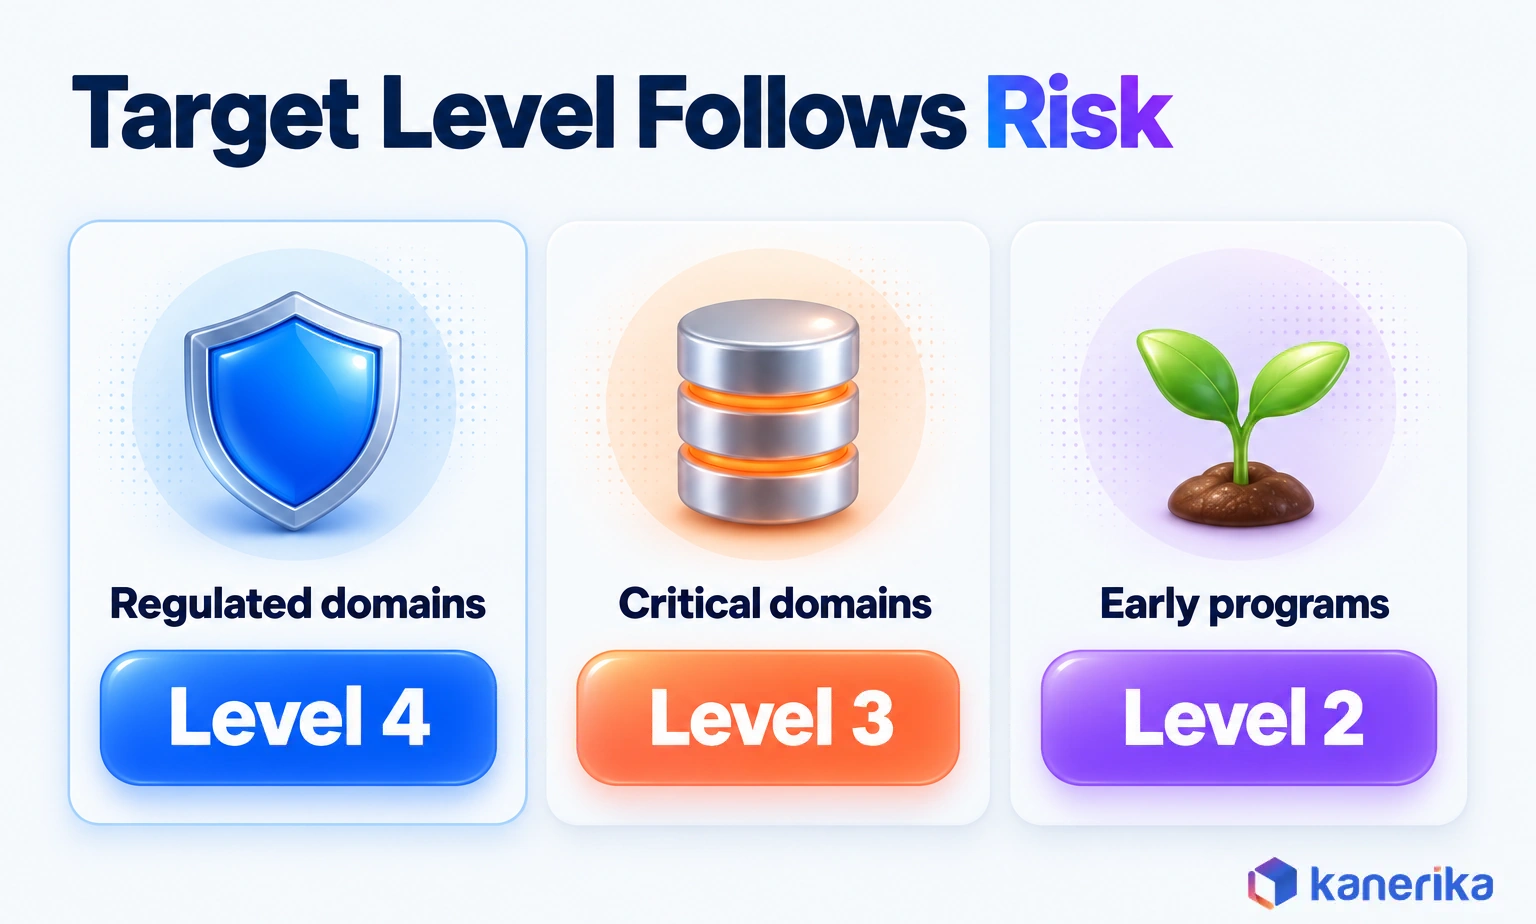
The right target is the level your risk and your goals require, set per domain, and it is rarely Level 5. Chasing the top level everywhere spends money on automation that some domains will never need.
Think about it the way a bank thinks about data security. The vault gets more controls than the stationery cupboard, so customer, financial and patient data deserve measured controls. A marketing events list, meanwhile, can live happily at Level 3.
| Organization or domain type | Realistic target | Why |
|---|
| Regulated domains in banking, insurance or healthcare | Level 4 | Regulators expect measured controls and evidence on demand |
| Data feeding high-risk AI systems | Level 4 | Training data must follow documented governance practices |
| Mid-market firms growing analytics and AI | Level 3 on critical domains | One standard way of working removes most reporting disputes |
| Early programs or a first governance hire | Level 2 on one or two domains | Named owners and first policies come before anything else |
| High-volume sensitive data with frequent change | Level 5, selectively | Automated classification saves more effort than it costs |
Set the target with each domain’s business owner, not only the governance team. When the owner agrees that customer data needs Level 4, the work to get there has a sponsor. That domain ownership echoes the data mesh principles of treating data as a product owned by its domain.
Then write the target down next to the current score for every domain. That pair becomes the backbone of your roadmap and the first slide of every progress report.
How to Move Up One Level at a Time
Moving up works best as a series of small, provable steps, one level per domain at a time. Skipping a level rarely sticks, because each level builds the evidence the next one measures.
Each transition below names the main shift, the work involved and the proof that you have arrived. Use them as a checklist for the domain you are lifting next.
Level 1 to 2: Name Owners for Critical Data
The first move is accountability. List the critical data elements in your target domain, such as customer ID, email and credit limit, then name one business owner for each.
Next, write the first two or three policies that owners will enforce, usually for quality, retention and access. Keep them short, because a one-page policy that people read beats a forty-page standard that nobody opens. Our list of data governance best practices helps you pick which controls come first.
You have reached Level 2 once an owner register exists, owners have signed it and the first policies are approved. If you need a structure to hang these pieces on, our guide to building a data governance framework walks through it.
Level 2 to 3: Standardize Policies and Stewardship
Level 3 is where governance stops depending on who happens to be in the room. You form a council and agree on a RACI for each domain. Then you publish a shared business glossary in one of the metadata management tools your teams already search.
The hard part is consistency. Finance and sales must use the same definition of “active customer,” while stewards in every domain follow the same issue workflow. Our guide to the enterprise data governance operating model covers how councils, roles and RACI work at scale.
You have reached Level 3 when every domain in scope follows the same policies. Reports should reference the glossary, and stewards should log issues in one place.
Level 3 to 4: Measure Controls
At Level 4, every control gets a number and a target. You track the share of critical data elements with quality rules, lineage coverage for top reports and access reviews completed on schedule.
This is usually the point where spreadsheets stop scaling, so a data catalog tool becomes necessary. Microsoft Purview, for example, shows governance health controls at the governance-domain level in its Unified Catalog, according to Microsoft documentation updated November 18, 2025. Those controls include classification and labeling coverage, data product ownership, data quality score coverage and OKR alignment, though custom controls are not supported (Microsoft Learn).
Kanerika Service
Data Governance Services
Kanerika assesses maturity per domain, sets target levels with business owners and implements the priority controls, from ownership to lineage.
Explore Data Governance Services
Setting those controls up is mostly configuration. A user with the data health owner role opens a control and sets an overall target score. Thresholds then map scores to Healthy, Fair, Not healthy or Critical. The same Controls page schedules refreshes in days, weeks or months. Microsoft bills these controls on pay-as-you-go Data Governance Processing Unit (DGPU) meters, so put them in the Level 4 budget.
Purview is one option among several, and our comparison of data governance tools covers how to choose. You have reached Level 4 when control metrics are reported on a fixed rhythm and missed targets trigger action.
Level 4 to 5: Automate and Improve
Level 5 turns measured controls into automated ones. Sensitive data gets classified as it lands, while access policies deploy as code and quality rules run inside data pipelines. Automation needs consistent labels, so settle your data classification best practices first.
Monitoring closes the loop. Data observability watches freshness, volume and schema drift, so problems surface before a business user finds them.
You have reached Level 5 when most controls in a domain run without manual steps and the program adjusts its own rules from its metrics. Reserve this effort, then, for domains where volume or risk justifies it.
What Each Step Costs and Who Leads It
The cost of moving between levels is mostly people’s time rather than software. So compare the steps by effort and by who leads them. The table below is a qualitative comparison, not a price list, because licensing and staffing differ between estates.
| Move | Who leads | Main cost driver | Relative effort |
|---|
| Level 1 to 2 | Business owners, with one governance lead | Owner time to review critical data and sign the register | Low |
| Level 2 to 3 | A governance council and domain stewards | Cross-team agreement on the glossary, RACI and issue workflow | Medium |
| Level 3 to 4 | Stewards working with data engineers | Catalog licensing, quality rules and lineage scanning | Medium to high |
| Level 4 to 5 | Data engineers and platform owners | Automation, policy-as-code and monitoring | High, so apply it selectively |
Time is easier to estimate than money. Kanerika’s published delivery estimates put initial data discovery and classification at 4 to 6 weeks. Glossary and catalog setup takes 6 to 10 weeks, while policy and access control deployment takes 8 to 12 weeks.
Full program maturity takes 12 to 18 months in that estimate, which fits a one-level-at-a-time pace.
KPIs That Prove Maturity Improved
A maturity level is a claim, and KPIs are the evidence behind it. Pick a small set that maps to your six dimensions. Then measure it the same way every quarter, and show the trend next to the score.
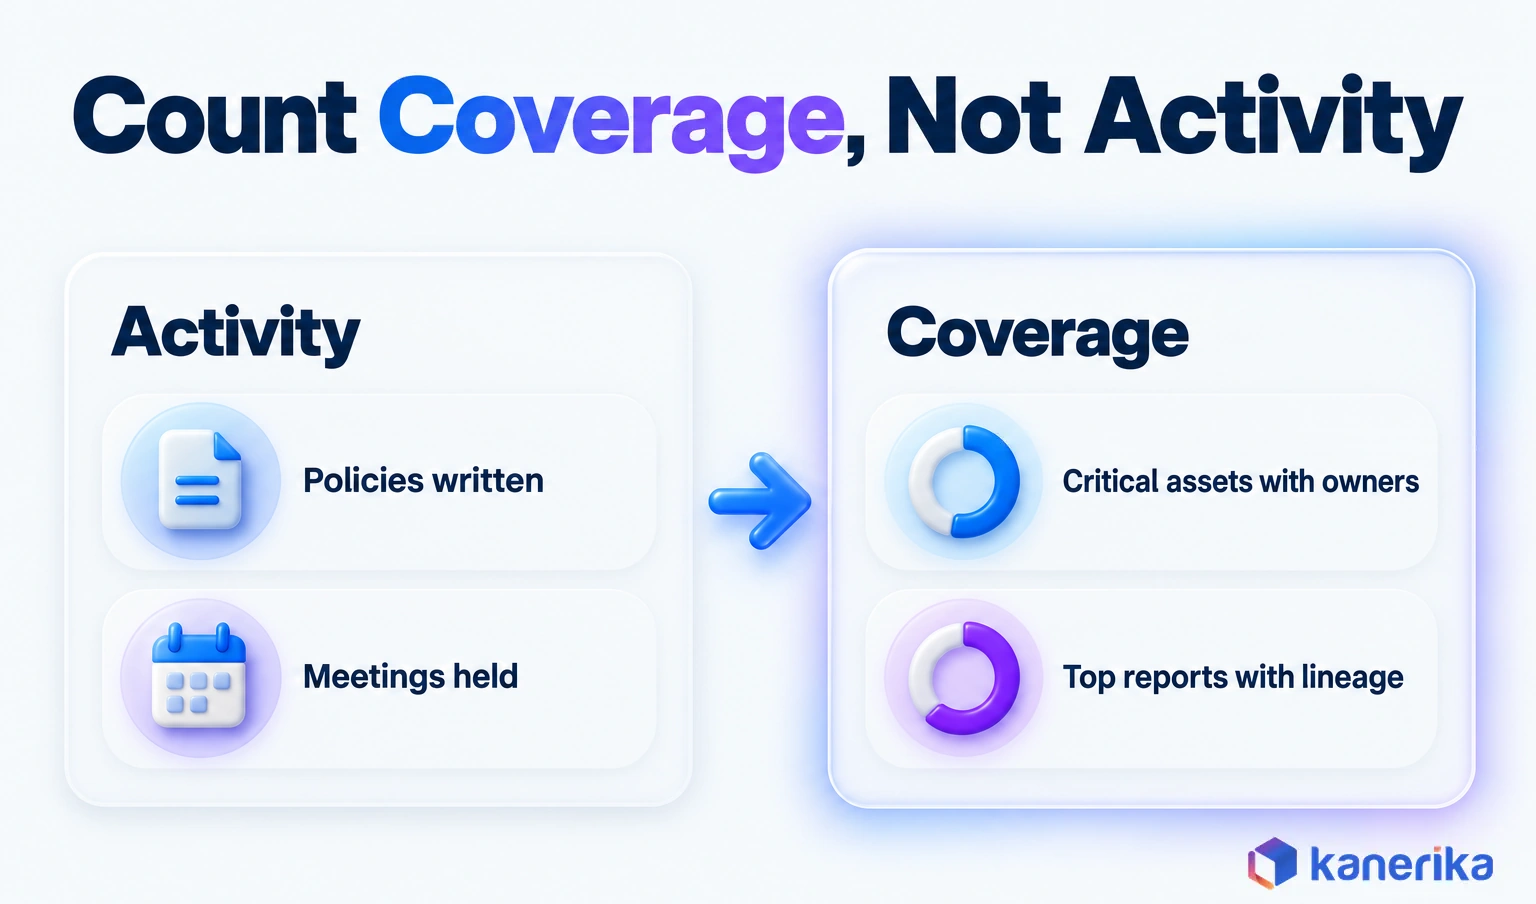
Count coverage, meaning how much of your critical data each control reaches. “Policies written” and “meetings held” measure effort, while “share of critical assets with a named owner” measures whether the effort changed anything.
| KPI | Dimension | How to measure |
|---|
| % of critical assets with a named owner | Ownership and stewardship | Owned critical assets divided by all critical assets in scope |
| % of critical data elements with active quality rules | Data quality | Elements with at least one running rule, divided by all critical elements |
| Lineage coverage of top reports | Metadata and lineage | Top reports with source-to-report lineage, divided by all top reports |
| % of access reviews completed on time | Access, privacy and classification | Reviews closed by the due date, divided by reviews due |
| Median days to resolve a data issue | Governance operations | Median of close date minus open date, once issues close |
| % of policy exceptions closed on time | Policies and standards | Exceptions closed within the agreed window, divided by all exceptions |
Pair each KPI with the level it supports. Owner coverage near 100% supports Level 2 ownership, while a falling median resolution time supports Level 4 operations.
Keep the definitions frozen for at least a year. If the denominator changes every quarter, the trend line tells you nothing.
A 90-Day Plan to Move Up One Level
Ninety days is long enough to show real progress in one domain and short enough to keep attention. The plan below lifts one domain by one level, so the two weakest dimensions become the focus.
Think of it as a sprint with a measured finish line. You baseline, you fix, and then you reassess with the same rubric so the change is visible.
| Phase | Actions | Evidence at the end |
|---|
| Days 1 to 30: assess and baseline | Score the domain on all six dimensions, agree on the target with its owner, then pick the two weakest dimensions | Scored rubric, target level and signed scope |
| Days 31 to 60: fix the two weakest | Name owners, write rules and map lineage for the critical elements behind one key report | Owner register, live quality rules and a lineage view |
| Days 61 to 90: measure, reassess, extend | Report the KPIs and rescore the domain, then choose the next domain or dimension | KPI trend, new scores and a next-cycle plan |
Keep the first cycle narrow on purpose. One domain moved from Level 1 to Level 2 with clear evidence persuades more sponsors than five domains moved halfway.
At day 90, publish the before and after scores with the KPI trend. That report then becomes the case for funding the next cycle.
How Kanerika Helps Enterprises Move Up the Maturity Curve
Kanerika starts every governance engagement with an assessment, because the right fix depends on which dimension is weakest. That assessment is the Initiate phase of IMPACT, our six-phase method of Initiate, Map, Plan, Activate, Check and Track. We score maturity per domain and agree on target levels with business owners. Then we put the priority controls in place.
Watch on YouTube
Transform Your Data Strategy with Microsoft Purview: Governance, Security & Growth
A Kanerika session on Microsoft Purview for data governance and security, the platform many teams use to measure classification, ownership and quality controls at Level 4.
Those controls usually include Microsoft Purview classification, access policies and automated lineage. We then measure progress through control scores and reassess, so each step up comes with evidence. If your estate runs on Microsoft, our guide to Microsoft Purview for data governance shows how those controls fit together.
One example is a global bank with about 9,000 branches and 22,000 ATMs. Its data was spread across SAP, Dynamics 365, CRM, Oracle and Netezza core banking systems and file systems.
Kanerika used the Purview Data Map to discover and classify that data. The team applied Purview policies for PII, PCI and PHI, then built automated lineage through the lakehouse layers. It then centralized governance metrics, so the bank could track progress across those systems in one place.
In maturity terms, that work lifted three dimensions at once: classification, access and lineage, the core of a Level 3 to Level 4 move. The bank reported 0% data breaches and 100% adherence to compliance regulations, while data classification accuracy improved by 72%.
Our data governance services add what an internal team finds hard to supply on its own. An independent assessor scores your domains without the self-rating inflation described above. For catalog and glossary work we use KANGovern, our accelerator built on Purview and Databricks Unity Catalog. Teams already on Purview start with a gap analysis of their current configuration. Our Microsoft Purview engineers then implement the controls that move each domain up a level.
Case Study
Zero Breaches, 100% Compliance for a Bank with Purview
Kanerika used Microsoft Purview to discover, classify and govern a global bank’s data across SAP, Oracle and Netezza, improving classification accuracy by 72%.
Read the Case Study →
The Bottom Line on Data Governance Maturity
A data governance maturity model is only useful when it changes what you do next. Score six dimensions on evidence, read your level from the weakest one, and set targets per domain rather than for the whole company.
So how do you move up? Fix the two weakest dimensions in one domain within 90 days, prove the change with KPIs, then repeat one level at a time.
Frequently Asked Questions
What is a data governance maturity model?
A data governance maturity model is a staged scale, usually with five levels, that scores how consistently an organization governs its data. Each level describes observable behavior, such as named owners, standard policies or measured controls. Teams score their program against those descriptions using evidence, then use the gaps to plan which improvements to make next.
What are the five levels of data governance maturity?
The common five levels are Initial, Developing or Repeatable, Defined, Managed or Measured, and Optimized. Level 1 relies on individual effort, Level 2 adds owners and first policies, and Level 3 applies one standard across domains. Level 4 tracks controls against targets, and Level 5 automates them. Labels vary between models, so the descriptions matter more.
What KPIs measure data governance maturity?
Useful KPIs measure coverage of controls rather than activity. Examples include the share of critical assets with a named owner, critical data elements with active quality rules, top reports with end-to-end lineage and access reviews completed on time. Median days to resolve a data issue and policy exceptions closed on time round out the set.
How long does it take to move up a maturity level?
It depends on scope, the starting point and how many domains you include. A focused effort on one domain can show measurable progress within a 90-day cycle, especially at the lower levels. Enterprise-wide moves take longer because every domain must meet the same standard. Plan one level and one domain at a time.
Why do governance programs stall at early maturity levels?
Programs often stall when governance is not tied to a business outcome, so sponsors lose interest after the first policies are written. Other causes include owners without time allocated, scoring documents instead of behavior and one company-wide score that hides weak domains. Our guide to common data governance challenges covers fixes for each of these problems.
How often should maturity be reassessed?
Reassess each domain you are actively improving at the end of every 90-day cycle, using the same rubric and evidence rules. Domains that are not in an improvement cycle can be reviewed once or twice a year. Keep the level definitions and KPI formulas fixed between assessments, or the trend line loses its meaning.
Can Microsoft Purview improve data governance maturity?
Purview can raise scores in dimensions it automates, such as classification, access policies, lineage and catalog coverage. Its Unified Catalog also reports health controls at the governance-domain level, which supports Level 4 measurement. A tool cannot name owners or agree policies for you, so ownership and stewardship still depend on people and process decisions.
What are the pillars of data governance?
Frameworks name them differently, but the pillars usually cover ownership and accountability, data quality, metadata and lineage, security and privacy, and compliance. Some models group them into three or four pillars instead. A maturity assessment scores the same ground as dimensions, so map your pillars to the six dimensions before you start scoring each domain.
What are the biggest challenges in data governance?
Common challenges include unclear ownership, weak executive sponsorship, siloed data across platforms, poor data quality and policies that nobody follows. AI adds new pressure, because models and agents use whatever data they can reach. A maturity assessment helps by showing which of these problems sits in your weakest dimension, so effort goes there first.
What is the Gartner data governance maturity model?
Gartner publishes maturity research for data and analytics leaders, but its detailed models are available to Gartner clients only. Public summaries describe a staged path from low awareness to effective, business-aligned governance. If you lack client access, build an internal five-level model on the same idea and score each dimension against evidence you can produce.
How do you assess data governance maturity?
Start by scoping the assessment to one business goal and a few critical domains. Pick a model, write three to five evidence-based questions per dimension and collect artifacts such as owner registers, quality reports and access reviews. Score each dimension from 0 to 5, compare the result with a target level and assign owners to close the gaps.
What dimensions does a data governance maturity assessment measure?
Most assessments score six dimensions. They are ownership and stewardship, policies and standards, data quality, metadata and lineage, access with privacy and classification, and governance operations. Some models group them into four or five areas instead. Scoring each dimension separately shows where the program is strong and where it is still ad hoc or missing entirely.
How do you calculate a data governance maturity score?
Score each dimension from 0 to 5 using a rubric, then average the six scores for each domain. Always report the lowest dimension score beside the average, because the weakest dimension sets the level you can defend to an auditor. Score domains separately so that one strong domain does not hide a weak one elsewhere.
What is the difference between DAMA-DMBOK and DCAM?
DAMA-DMBOK is a body of knowledge that defines data management knowledge areas and shared vocabulary, and many teams build internal maturity models from it. DCAM, from the EDM Council, is a capability assessment model with 8 core components and 34 capabilities, scored against auditable evidence. DCAM is available only to EDM Council member firms.
Which maturity level should an organization target?
Set the target per data domain based on risk and business goals. Regulated domains in banking, insurance or healthcare usually need Level 4, while most other critical domains do well at Level 3. Early programs should aim for Level 2 on one or two domains first. Level 5 is worth funding only where automation saves real effort.
How do you move from Level 2 to Level 3?
Level 3 means one standard way of governing across domains. Form a governance council, agree on a RACI for each domain and publish a shared business glossary. Then make every in-scope domain follow the same policies and issue workflow. You have arrived when reports reference glossary terms and stewards log every issue in one place.
How can an organization improve its data governance maturity?
Assess each domain against evidence, set a target level and fix the two weakest dimensions first. Name owners for critical data, standardize policies and stewardship, then measure controls with clear targets. Work in 90-day cycles, report KPIs such as owner and lineage coverage, and reassess with the same rubric so progress stays visible to sponsors.














