TL;DR
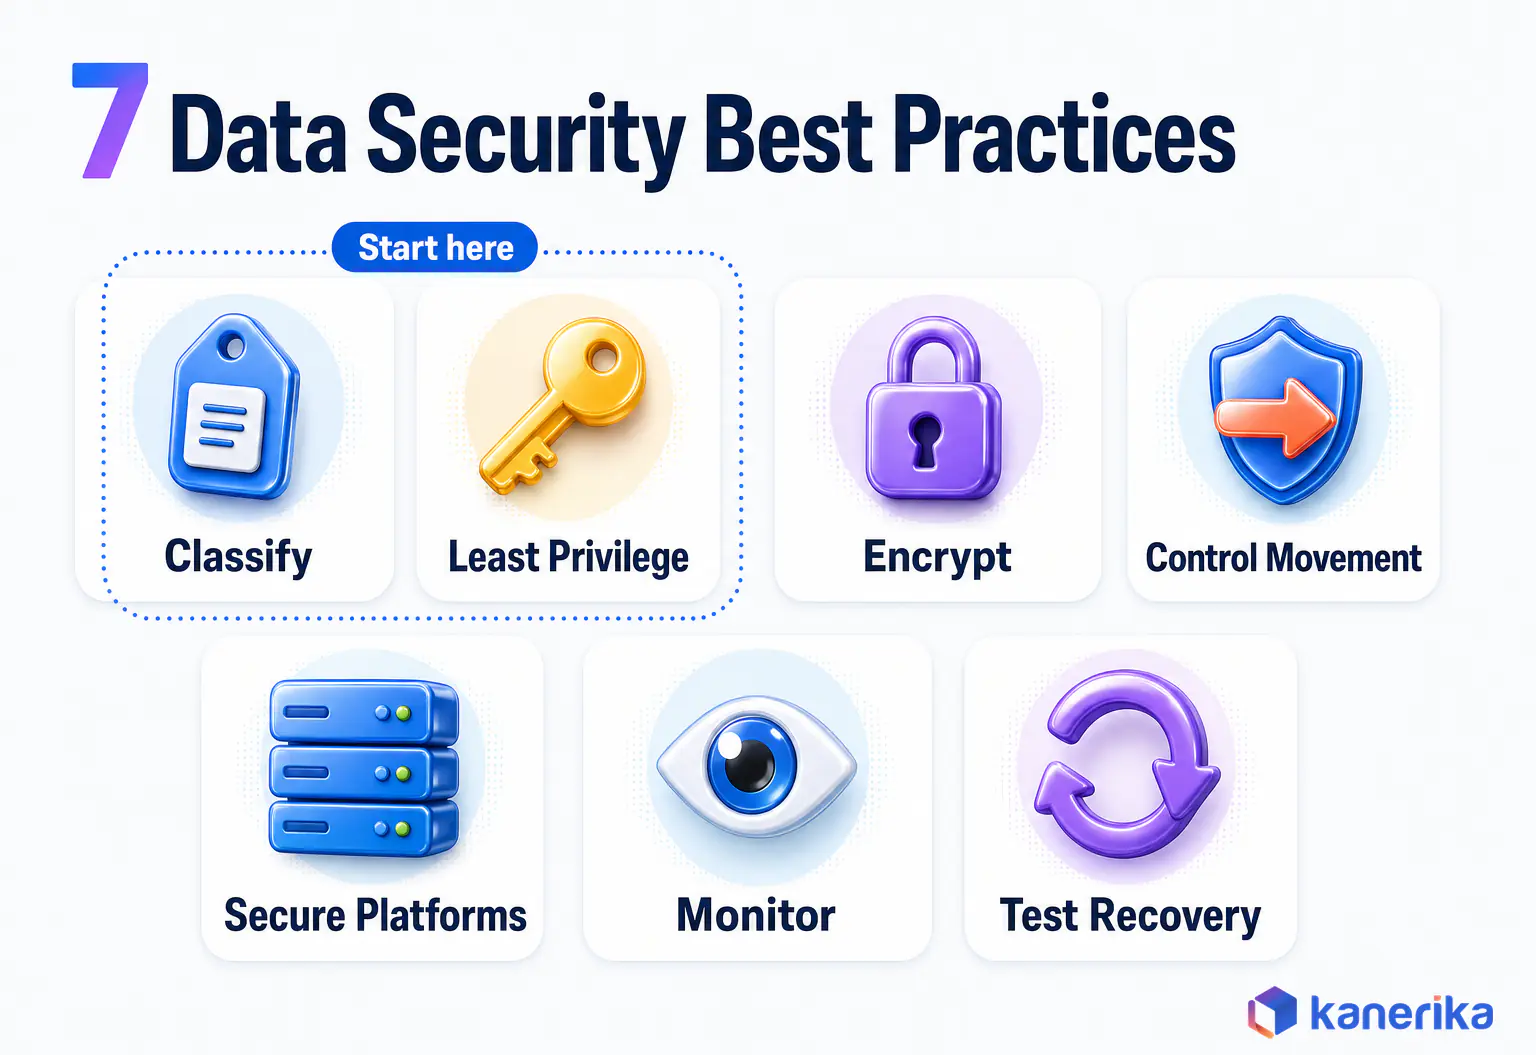
Of the 7 data security best practices every enterprise needs in 2026, start with two: classify sensitive data and enforce least privilege. The other five are encryption, data movement and AI controls, secure platforms, continuous monitoring and tested recovery. Classification comes first because every other control depends on knowing which data is sensitive and where its copies live.
Least privilege comes second because approved accounts, including AI assistants, can now reach far more data than their jobs need. With the average breach now costing USD 4.99 million (IBM, 2026), each practice needs an owner and evidence. Prove the program works by restoring backups on a schedule and reporting a short set of KPIs to leadership.
Key Takeaways
- The seven practices are classify, restrict access, encrypt, control movement and AI access, secure platforms, monitor, and test recovery.
- Classification and least privilege come first, since encryption, DLP and monitoring all depend on knowing what is sensitive and who can reach it.
- Machine identities such as service accounts, API keys and AI copilots now need the same owners, reviews and expiry dates as people.
- AI assistants should only retrieve what the signed-in user could already open, which makes sensitivity labels a precondition for any copilot rollout.
- Backups count only when a restore drill proves them, so set RTO and RPO per system and keep one immutable or offline copy.
- Seven leadership KPIs, from labelled data coverage to restore-test pass rate, show whether the program is working rather than merely documented.
When an Approved Account Becomes the Breach
Picture a reporting service account created three years ago for a finance dashboard. Nobody remembers who owns it, but it still holds read access to the full customer table.
Then the company switches on an AI copilot for its analysts. Because the copilot connects through a broad data connection, it can now summarise anything that account can see. One afternoon, a sales manager asks it for “top accounts by revenue” and gets back names, card fragments and home addresses.
Nobody hacked anything. Every login was valid, every query was authorised, and the firewall logs are clean. Even so, sensitive data reached someone who should never have seen it.
That is how enterprise exposure can happen with no attacker involved. The data was never labelled as sensitive, and the account that reached it had far more access than its job needed. So this guide puts classification and least privilege first, then covers the five practices that protect, watch and recover everything else.
What Do Data Security Best Practices Mean for an Enterprise in 2026?
Data security best practices are the repeatable controls that keep sensitive information confidential, accurate and available, wherever it sits or moves. If you need the foundations first, our guide on what data security covers explains the threat types and how security differs from privacy. This post goes one level down, into the operating program an enterprise actually runs.
A program like this protects data in more states than most teams expect. Production databases are only the start, because copies spread into exports, test environments, spreadsheets, backups and now AI context windows. After all, an attacker or a careless insider only needs the weakest copy.
- At rest: stored data, such as databases, file shares, data lakes, laptops and backup media.
- In motion: traffic between apps, users, clouds, partners and APIs, especially across public networks.
- In use: records loaded into reports, notebooks, prompts and AI responses while people work with them.
- Copies: extracts, sandboxes, email attachments and shared links that outlive their purpose.
The stakes are measurable. The IBM Cost of a Data Breach Report 2026 puts the global average breach at USD 4.99 million. That is a record high and 12% above the prior report, so boards now ask for evidence rather than intentions.
What Changed in 2026
The biggest shift is that software now reads enterprise data on a person’s behalf, often without anyone watching. In practice, AI assistants and agents search mailboxes, documents and databases through user and machine identities. As a result, any over-permissioned account becomes a fast, polite and very thorough leak.
Attackers also adopted the same tools. IBM reports a 56% increase in AI-driven attacks, led by deepfake impersonation and AI-enabled malware. Meanwhile, regulators tightened the rules on how quickly companies must disclose an incident and prove their controls.
Put together, these changes reward companies that know where their sensitive data is and can show who touched it. At the same time, they punish companies that can only describe a policy.
Watch on YouTube
AI Security for Enterprises: Kanerika’s CISO on Prompt Injection, ISO 27001 & SOC 2
Kanerika’s CISO explains how AI changes the attack surface, from prompt injection to the ISO 27001 and SOC 2 controls that keep enterprise data inside the right boundaries.
The 7 Data Security Best Practices at a Glance
Each practice below closes one specific risk, so each one needs a named owner. The last column matters most, because an auditor or a board will ask for proof rather than a description. Use the table as a one-page map before you read the detail for each practice.
| # |
Practice |
Risk it closes |
Typical owner |
Evidence an auditor accepts |
| 1 |
Discover, classify and minimize data |
Unknown sensitive copies |
CDO with data owners |
Data inventory, label coverage report, retention schedule |
| 2 |
Least-privilege access |
Over-permissioned people and service accounts |
CISO with IAM team |
Access review sign-offs, MFA coverage, secrets inventory |
| 3 |
Encryption and key control |
Readable stolen data |
Platform security |
Encryption settings, key rotation logs, masking rules |
| 4 |
Control data movement and AI access |
Leaks through email, links and copilots |
Security with data governance |
DLP policy reports, AI connector scopes |
| 5 |
Secure platforms and third parties |
Misconfiguration and vendor exposure |
Cloud and procurement teams |
Configuration baselines, patch SLAs, vendor reviews |
| 6 |
Monitor and validate controls |
Slow detection |
Security operations |
Alert runbooks, control test results |
| 7 |
Test response and recovery |
Ransomware and long outages |
IT operations with the CISO |
Restore test records, tabletop reports |
1. Discover, Classify and Minimize Sensitive Data
You cannot protect what you have not found. Discovery means scanning databases, file shares, SaaS apps and cloud storage for regulated data, then recording where each type lives. Most first scans surprise people, because customer data turns up in test copies and old exports nobody listed.
Classification then gives that data a label, such as Public, Internal, Confidential or Restricted. Labels are also what later controls read. A DLP rule, an encryption policy or an AI connector can only act on data it recognises. So a missing label quietly switches those controls off.
Minimization is the cheapest control of all, since data you delete on schedule cannot leak. For that reason, retention rules belong in this practice rather than in a separate legal project.
- Run automated discovery across structured and unstructured stores, starting with the systems that hold customer, payment and health data.
- Agree on four or five sensitivity labels, then apply them automatically where patterns are clear, such as card numbers and national IDs.
- Assign a business owner to every Restricted dataset so that access requests have someone to approve them.
- Set retention schedules and secure deletion for copies, extracts and logs, then track deletion as a measured task.
Classification works best inside a wider data governance model with owners, glossaries and policies. Our guide to data governance best practices covers that operating model, while these data governance principles explain how ownership and accountability fit together.
Kanerika Service
Data Governance Services
Kanerika helps enterprises discover and classify sensitive data, assign owners and set the retention and access policies that every later security control depends on.
Explore Data Governance Services
2. Enforce Least-Privilege Access for People and Machine Identities
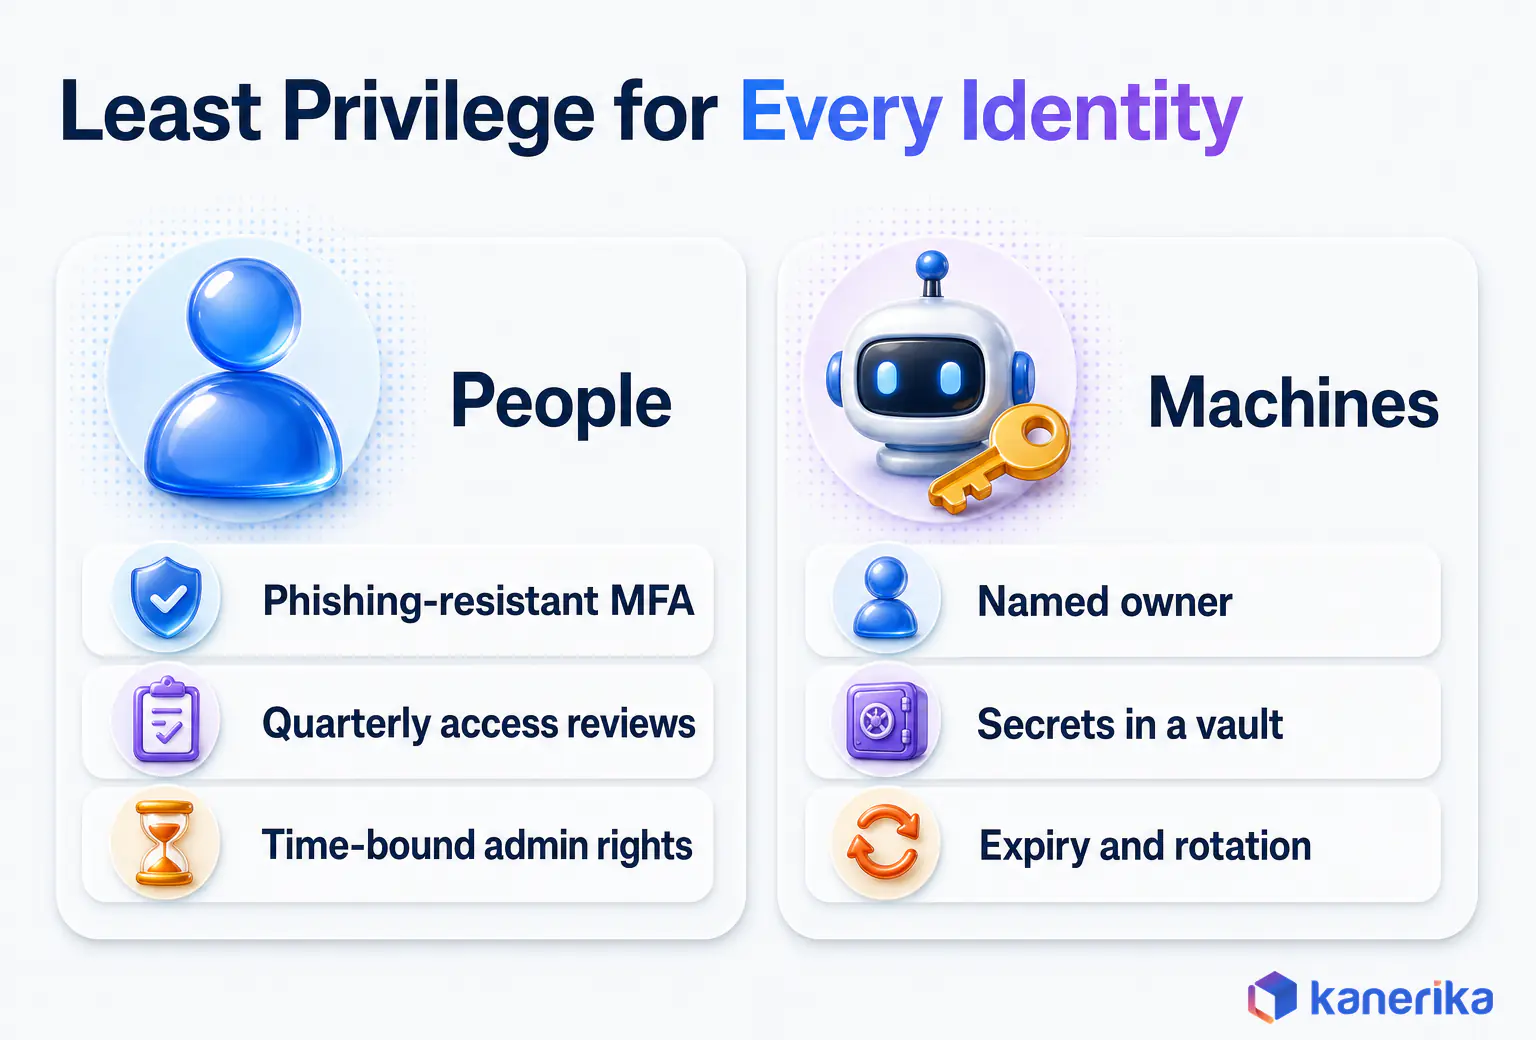
Least privilege means every identity gets the minimum access its job needs, for no longer than it needs it. That sounds simple when you think about employees. In practice, the harder problem is machine identities, because service accounts, API keys, pipelines and AI agents often outnumber the people in an environment.
Start with role-based access control (RBAC) for common jobs, then add attribute-based rules (ABAC) where context matters, such as region or data label. Also require phishing-resistant MFA for every privileged account. Replace standing admin rights with time-bound elevation, so nobody holds powerful access by default.
Machine identities need the same discipline, even though nobody logs in as them by hand. Each service account and API key should have a named owner, a documented purpose and an expiry date. Store secrets in a vault instead of code or config files, and rotate them on a schedule. The security of agentic AI depends on this too, because an agent acts with whatever credentials it is given.
- Review access quarterly for sensitive systems, and remove anything unused for 90 days.
- Enforce MFA on all admin, remote and cloud console access, as well as on email.
- Keep an inventory of service accounts, keys and tokens with owners and expiry dates.
- Log every privilege elevation, then review the log monthly.
Zero trust is the principle behind all of this. NIST SP 800-207, published in August 2020, defines it as granting access before each session based on identity, device and context. In other words, nothing is trusted just because it sits inside the network. Our guide to zero trust data security covers the architecture. Similarly, the companion piece on data access governance explains how to run access reviews at scale.
Training People to Spot the Attack
People still need training, though it works best when short and specific. For example, teach staff to spot a deepfake voice request, to verify payment changes by a second channel and to report mistakes fast. A culture where people report a misdirected email within minutes beats one where they hide it.
3. Encrypt Data at Rest and in Transit, and Control the Keys
Encryption turns stolen data into unreadable data. However, it does not stop an attacker who signs in with valid credentials, which is why it comes after access control in this list. Even so, it is the control that turns a lost laptop or a leaked backup into a non-event.
Use AES-256 for data at rest across databases, storage accounts, laptops and backups. Use TLS 1.3 for data in transit, and retire older protocol versions on internal services as well as public sites. Most cloud platforms encrypt by default, so the real work sits in key management.
Keep keys in a managed key management service (KMS) or a hardware security module (HSM). Rotate them on a schedule, and separate duties so the people who manage keys cannot also read the data. For development and test copies, mask or tokenize sensitive fields so that engineers work with realistic data that is useless to a thief. These data masking tools show the options.
Protecting Data That Crosses Networks
Encryption covers the data itself, while network controls limit where that data can travel. Three measures do most of the work.
- Segmentation: split networks so that a compromised laptop cannot reach database servers or backup systems directly.
- Private endpoints: connect apps to cloud databases and storage over private links rather than the public internet.
- Virtual private networks (VPNs): extend a private network across a public one. As noted by Mysterium VPN, VPNs can protect browsing activity by encrypting data and routing traffic through a private network. That matters when employees reach company systems over shared or public Wi-Fi. Expert comparisons on Cybernews, such as NordVPN and ExpressVPN, can help teams compare encryption strength and connection security before choosing a provider.
Understanding the different VPN types helps security teams pick the right approach for administrative access, branch-office links and remote sessions. On top of those encrypted paths, intrusion detection and prevention systems (IDS and IPS) watch traffic for suspicious patterns and block known attacks. Segmentation limits how far a compromised device can reach, and IDS or IPS alerts make sure it is noticed as well.
4. Control Data Movement, Sharing and AI Access
Many leaks look nothing like a break-in. They are files emailed to the wrong person, folders shared with “anyone with the link” or a copilot answering a question it should have refused. This practice controls where data can go once someone is allowed to see it.
Data loss prevention (DLP) is the core tool for this practice. It inspects content in email, endpoints, SaaS apps and sharing links, then warns, blocks or logs based on the sensitivity label. Microsoft Purview DLP is one example, detecting financial data, card numbers, health records and Social Security numbers across Microsoft services. Start DLP in audit mode, tune the false positives, and then switch to blocking within a set number of weeks.
| Channel |
Control that works |
| Email |
DLP on outbound mail, with policy tips for Confidential and blocks for Restricted |
| Endpoints |
Limits on USB copy, printing and uploads to personal cloud storage |
| SaaS and cloud storage |
Label-aware sharing rules and alerts on mass downloads |
| Sharing links |
Expiry dates by default and no anonymous links for labelled files |
| AI copilots and RAG pipelines |
Retrieval scoped to what the signed-in user can already open |
Watch on YouTube
How KANGuard Secures Your Data | Prevent Leaks & Unauthorized Access with DLP Policies
A short walkthrough of how DLP policies stop sensitive files and records from leaving through the wrong channel, the same control this practice puts on email, endpoints and sharing links.
Scoping What AI Assistants Can Read
AI access needs its own rule: an assistant should never retrieve anything the user could not open directly. That is, copilots and retrieval-augmented generation (RAG) pipelines must respect the source permissions and labels, rather than reading through one broad connector. Purview data security posture management for AI applies data security and compliance protections to Copilots and other generative AI apps.
For a deeper look, see our guides on securing data used by AI and on generative AI security controls. Both cover prompt injection as well as model-level risks. For the policy layer around the models themselves, an AI security framework sets the rules that sit beyond the scope of this list.
5. Secure Data Platforms, Pipelines and Third-Party Integrations
Cloud providers secure the infrastructure, but customers secure their own configuration, identities and data. This shared responsibility model is where many breaches start, for instance as a storage bucket left public or a database exposed to the internet.
Configuration baselines fix most of it when teams enforce them. Define secure defaults for each platform, scan against them continuously and treat drift as a ticket with an owner. Patch on a fixed timeline, with faster deadlines for internet-facing systems and actively exploited flaws.
Data applications deserve the same care as customer-facing software, because they hold the same customer data. Build security into development, with code review, dependency scanning and secrets checks in every pipeline. Then extend the review outward, because every SaaS tool and integration partner that touches your data widens the attack surface.
On-Demand Webinar
Data Security Risks in AI: How Microsoft Purview Protects You
An on-demand session on how sensitive data leaks through AI tools and how Microsoft Purview labels, DLP and posture management keep copilots inside the right boundaries.
Watch the Webinar →
- Publish a configuration baseline for each cloud and data platform, and scan against it daily.
- Set patching deadlines by severity, and then report on any exceptions.
- Add dependency, secrets and infrastructure-as-code scanning to every data pipeline.
- Review vendors and integrations before access is granted, and again each year.
- Remove integrations once they no longer have an owner or a business use.
Our SaaS security best practices cover vendor apps in more depth. For Microsoft cloud estates, these Azure security best practices map the same ideas to specific services.
6. Monitor Data Access and Validate Controls Continuously
Controls drift over time. Permissions creep back, new copies appear and a well-meant exception becomes permanent, so monitoring is how you notice before an attacker does.
Send access, authentication and admin logs to one central platform, and keep them long enough to investigate an incident months later. Then add user and entity behaviour analytics (UEBA) to flag unusual patterns, such as a service account suddenly reading a full table at 2 a.m. Data security posture management (DSPM) adds a data-centric view, finding exposed copies and over-shared sensitive files across clouds.
- Alert on mass downloads, unusual query volumes and first-time access to Restricted data.
- Scan regularly for sensitive data in places where it should not be, such as test systems.
- Test controls on a schedule, for example by checking that a DLP rule really blocks a sample file.
- Track every alert until closure, with an owner and a target time.
Native platform tools are often enough to start, because they see their own platform in detail. A central tool earns its cost once data spreads across several clouds and SaaS apps, since it gives one view and one alert queue. Our guide to data security posture management compares the approaches, and data lineage helps trace where a sensitive field travels. The Kanerika section below also shows how one transport operator sped up breach detection with this kind of monitoring.
Datasheet
Elevate Data Governance, Compliance and Security of Your Organization
A datasheet on how Kanerika combines governance, compliance and security controls so sensitive data stays classified, protected and auditable across platforms.
View the Datasheet →
7. Test Incident Response, Backups and Data Restoration
Every program eventually faces an incident, so the last practice is about recovering quickly and proving you can. Until a backup has been restored in a test, nobody knows whether it works.
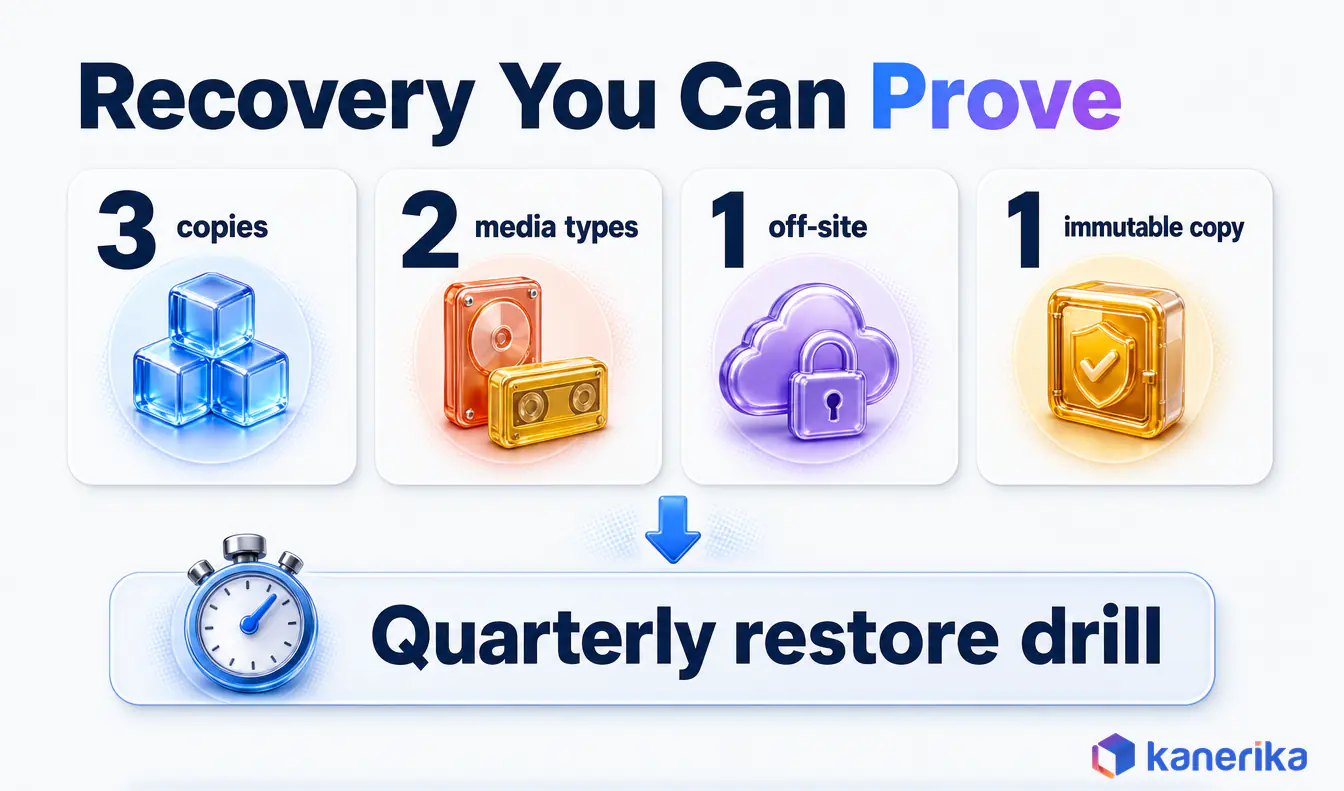
First, follow the 3-2-1 rule: three copies of important data, on two different media, with one copy off-site. Make at least one copy immutable or offline, because ransomware operators often go after backups. Then set a recovery time objective (RTO) and recovery point objective (RPO) for each critical system, and test against them.
Incident response also needs the same rehearsal. NIST SP 800-61 Rev. 3, published in April 2025, aligns incident response with the six functions of the NIST Cybersecurity Framework 2.0. The table shows what to have ready under each one.
| CSF 2.0 function |
What to have ready |
| Govern |
Named incident lead, decision rights, disclosure process and legal contacts |
| Identify |
Inventory of critical systems and sensitive data, with owners |
| Protect |
Access, encryption and backup controls from practices 1 to 5 |
| Detect |
Alerting and triage runbooks from practice 6 |
| Respond |
Containment playbooks, communication templates and a regulator timeline |
| Recover |
Tested restores, RTO and RPO targets and a lessons-learned review |
Run a tabletop exercise at least twice a year with executives in the room, and include the disclosure decision. In addition, restore a sample of critical systems every quarter and record the time it took. Our guide to Azure disaster recovery shows how to design the recovery side on Microsoft cloud.
Which Data Security Practices Should You Prioritize First?
Order matters, because few companies can run all seven practices at full depth on day one. The right starting point depends on what is happening in the business when you begin. A copilot rollout and a ransomware scare call for different first moves, even though both end up at the same seven practices.
The table maps common situations to the two practices that reduce the most risk first. In almost every row, classification or least privilege appears, because they make the other five effective.
| Scenario |
Start with |
Why |
| Regulated data in SaaS apps |
1 Classify, 4 Control movement |
Labels let DLP and sharing rules act on regulated fields |
| AI copilot rollout |
1 Classify, 2 Least privilege |
The copilot inherits every over-broad permission |
| Cloud migration |
3 Encrypt, 5 Secure platforms |
New platforms need keys and baselines before data lands |
| Merger or acquisition |
2 Least privilege, 6 Monitor |
Two identity estates meet and old accounts linger |
| Ransomware exposure |
7 Test recovery, 2 Least privilege |
Immutable backups and fewer admin rights limit the damage |
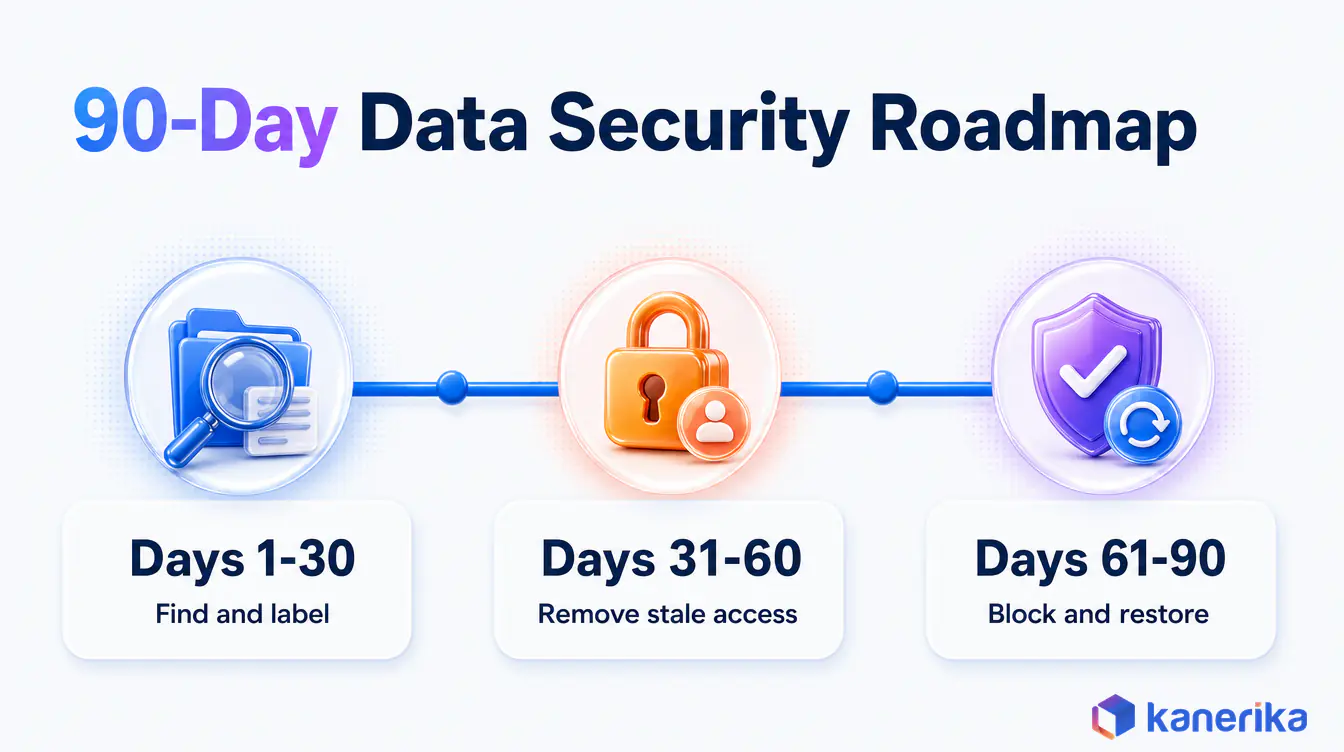
For most enterprises without a pressing trigger, a 90-day plan works well, especially when it starts with setting well-defined goals for each phase. It builds evidence early, so leadership sees progress within the first month.
- First 30 days: run discovery on the top ten systems, agree labels, enforce MFA on all admin accounts and list every service account.
- Days 31 to 60: remove stale access, move secrets into a vault, confirm encryption and key ownership, and start DLP in audit mode.
- Final 30 days: switch priority DLP rules to blocking, scope AI connectors, centralise logs and complete the first restore drill.
Worked Example: Securing Customer Data on a Cloud Analytics Platform
Consider a mid-sized retailer moving customer and loyalty data into a cloud analytics platform. Marketing also wants a copilot on top of it within a quarter. Here is how the seven practices play out in order.
- Classify: first, the team scans the source systems and labels email addresses, phone numbers and payment tokens as Restricted.
- Restrict: analysts get access to a masked view by default, while only the loyalty team can request the full table, with approval.
- Encrypt: the platform uses customer-managed keys, and the key administrators sit outside the analytics team.
- Control movement: DLP blocks exports of Restricted columns to personal email, and the copilot reads only the masked view.
- Secure the platform: a configuration baseline blocks public endpoints, and every pipeline is scanned for exposed secrets.
- Monitor: alerts fire when any account reads more than an agreed number of unmasked rows in an hour.
- Recover: the team restores last week’s snapshot into an isolated environment and records the time it took.
Nothing here needs a new security team. Instead, it needs owners for each step and an order of work that puts labels and permissions in place before the copilot goes live.
Which Frameworks and Regulations Shape Data Security in 2026?
Frameworks tell you what good looks like, while regulations tell you what you must prove. Most enterprises map one set of controls to several of them rather than running a separate program for each. The table lists the ones that most often shape a data security program, as checked on 21 October 2026.
| Framework or regulation |
Who it applies to |
What it asks of data security |
Status |
| NIST CSF 2.0 |
Any organization, voluntary |
Six functions from Govern to Recover |
Current version |
| ISO/IEC 27001:2022 |
Any organization seeking certification |
A managed, audited information security system |
Current edition |
| PCI DSS v4.0.1 |
Anyone storing or processing card data |
Protection of cardholder data, access control, logging |
Current version |
| GDPR |
Personal data of people in the EU |
Article 5 principles and security of processing |
In force; fines up to EUR 20M or 4% of turnover |
| CCPA regulations |
Certain CCPA-covered businesses |
Cybersecurity audits and risk assessments |
Effective 1 January 2026 |
| SEC Form 8-K Item 1.05 |
US-listed public companies |
Disclosure of material cyber incidents |
Four business days after the materiality decision |
| DORA |
EU financial entities |
ICT risk management, testing and incident reporting |
Applied since 17 January 2025 |
| NIS2 |
EU essential and important entities |
Cybersecurity risk management and incident reporting |
In force |
| HIPAA Security Rule |
HIPAA covered entities and their business associates |
Administrative, physical and technical safeguards for ePHI |
In force |
One control set can satisfy most of these at once, so long as the evidence is kept. For a closer look at the privacy side of US and EU rules, read our comparison of GDPR and CCPA compliance.
Talk to Kanerika
Not Sure Which Practice to Start With?
Bring your current data estate, your compliance obligations and any planned AI rollout. Kanerika will map your gaps against the seven practices and suggest the first two to fix.
Book a Working Session →
Common Data Security Mistakes and How to Avoid Them
Most failures come from gaps between the practices rather than from missing tools. Each mistake below is common, quiet and fixable once someone owns it.
| Mistake |
What it causes |
Fix |
| Untracked data copies |
Sensitive data in test systems and old exports |
Discovery scans plus retention and deletion rules |
| Standing admin access |
One stolen login reaches everything |
Time-bound elevation with approval and logging |
| Unowned service accounts |
Broad access that nobody reviews |
Owner, purpose and expiry for every machine identity |
| Untested restores |
Backups that fail during a ransomware attack |
Quarterly restore drills against RTO and RPO |
| DLP left in audit mode forever |
Leaks get logged but never stopped |
A dated plan to move tuned rules into blocking |
| AI tools connected before labels exist |
Copilots surface data users should not see |
Label and scope sources before switching AI on |
The last row is the newest of the six. Our guide on AI privacy explains why connecting AI to unlabelled data turns a permission problem into a disclosure problem. Well-designed AI guardrails then limit what a model may return, even when a source is mislabelled.
How Do You Know Your Data Security Practices Are Working?
A program is working when its numbers move in the right direction. For that reason, leadership needs a short list of measures that show coverage, hygiene and readiness. Seven KPIs across those three areas give a clear monthly picture.
- Labelled sensitive data: the share of known sensitive data stores with labels applied.
- Privileged accounts without MFA: the target is zero, since one gap is enough.
- Stale access removed: the number of unused permissions removed in each review cycle.
- Mean time to detect and contain: measured from the first alert until containment.
- Restore-test pass rate: the share of restore drills that met their RTO and RPO.
- Open critical misconfigurations: the count and age of high-severity configuration findings.
- Third parties with a current review: the share of vendors with data access reviewed in the past year.
Trends matter more than single readings. If label coverage rises while stale access falls, the program is gaining ground. If restore tests keep missing their RTO, though, recovery needs attention before anything else.
How Kanerika Helps Enterprises Put These Practices in Place
Kanerika helps enterprises turn these seven practices into a working program with owners, evidence and measurable results. We start from the data, because classification and access are where most programs stall.
Our work follows four stages. First, an assessment finds sensitive data, maps who can reach it and scores the gaps against the seven practices. Next, the design stage sets labels, access models and DLP policies. Then we implement them, often with Microsoft Purview for classification, DLP and data security posture management for AI. Finally, we monitor and tune the controls with the client’s own security team.
This work sits within our data governance services and our Microsoft Purview practice. For access protection, our kanGuard module from the kanSuite family helps prevent unauthorised access and data leaks through DLP policies. Our guide to data governance with Microsoft Purview explains how the governance side fits with these controls.
The approach shows up in delivery work. SeaLink, Australia’s largest integrated land, marine, tourism and public transport operator, struggled with disparate systems and slow reporting. Kanerika implemented a secure multi-tenant Incorta platform that consolidated its data and improved security. The result was a 47% decrease in breach identification time and a 32% improvement in compliance adherence.
Kanerika itself holds ISO 27001, ISO 27701 and SOC 2 Type II certifications, so we apply the same controls we recommend.
Case Study
47% Faster Breach Detection with Incorta Analytics
Kanerika consolidated SeaLink’s disparate systems into a single view of operations, cutting breach identification time by 47% and improving compliance adherence by 32%.
Read the Case Study →
Which Data Security Best Practices Should You Start With?
Every enterprise needs all seven practices, but the order decides how fast risk falls. Classify sensitive data and enforce least privilege first, because they make every later control effective. Once those two are in place, encryption and DLP have labels to act on, monitoring has a baseline to compare against, and restore drills prove the rest. The data security best practices to start with in 2026 are classification and least privilege, followed by encryption and DLP, and then tested recovery.
Frequently Asked Questions
What are data security best practices?
Data security best practices are repeatable controls that keep sensitive information confidential, accurate and available. For enterprises in 2026 they come down to seven: classify and minimize data, enforce least privilege, encrypt and control keys, govern data movement and AI access, secure platforms and vendors, monitor continuously, and test incident response and recovery.
What are the basics of data security?
The basics are knowing what sensitive data you hold, limiting who can reach it, and making it unreadable if stolen. That means an inventory with labels, role-based access with MFA, encryption at rest and in transit, and regular backups. Logging and a tested incident plan complete the foundation for any organization, whatever its size.
How can enterprises protect sensitive data in the cloud?
Start by finding and labelling sensitive data in every cloud account. Then apply least-privilege access, encrypt with keys you control, block public endpoints through configuration baselines and use private connections. Under the shared responsibility model the provider secures the infrastructure, but your team owns identities, configuration and data, so monitoring for drift is essential.
What is the difference between data security and data privacy?
Data security protects information from unauthorised access, change or loss through controls such as encryption, access management and backups. Data privacy governs how personal data is collected, used, shared and retained, and what rights individuals have. Security is how you protect data, while privacy is what you are allowed to do with it. You need both.
What is the best way to secure data at rest and in transit?
For data at rest, use AES-256 encryption across databases, storage, laptops and backups, with keys held in a managed KMS or HSM and rotated on schedule. For data in transit, use TLS 1.3 on every internal and external service. Separate key administration from data access so one compromised account cannot expose everything.
How does zero trust improve enterprise data security?
Zero trust removes the assumption that anything inside the network is safe. Each session is checked against identity, device health and context before access is granted, as described in NIST SP 800-207. For data security, that limits how far a stolen login or compromised device can reach, and it makes least-privilege access enforceable at scale.
How often should companies review data access permissions?
Review access to sensitive systems at least quarterly, and review privileged and admin access monthly. Remove permissions that have not been used in about 90 days, and revoke access immediately when someone changes role or leaves. Service accounts and API keys need the same review, with a named owner confirming each one is still needed.
What are the biggest data security risks in cloud migration?
The biggest risks are misconfigured storage or databases left publicly reachable, sensitive data copied into new environments without labels, and over-broad access granted to speed up the move. Unencrypted transfer paths and forgotten staging copies add more exposure. Set encryption, configuration baselines and access rules before data lands, not after the migration finishes.
How do you protect sensitive data used by AI agents and copilots?
Label sensitive data before connecting any AI tool, then scope retrieval so the assistant only reads what the signed-in user could already open. Give each agent its own identity with least-privilege access and an owner. Apply DLP to prompts and responses, log AI interactions and review connector permissions as often as you review human access.
What is the difference between DLP and DSPM?
Data loss prevention (DLP) watches data as it moves, through email, endpoints, SaaS apps and sharing links, and warns, blocks or logs risky actions. Data security posture management (DSPM) looks at data where it sits, finding sensitive copies, exposed stores and excessive permissions across clouds. DSPM tells you where the risk is, and DLP stops it leaving.
How do companies measure data security effectiveness?
Track a short set of KPIs every month: share of sensitive data labelled, privileged accounts without MFA, stale access removed per review, mean time to detect and contain, restore-test pass rate, open critical misconfigurations and vendors with a current risk review. Rising coverage and falling exposure over time show the program is working in practice.
How much does enterprise data security implementation cost?
Cost depends on the number of data sources, clouds and SaaS apps in scope, how much sensitive data lacks labels, existing licences such as Microsoft E5 or Purview, and whether you need new tooling or mainly configuration. Internal staff time for access reviews and DLP tuning is often the largest ongoing cost, rather than software.
What are 5 ways to secure data?
Five practical ways are to classify sensitive data, restrict access to the minimum each role needs, encrypt data at rest and in transit, use data loss prevention on email, endpoints and sharing links, and keep immutable backups that you restore on a schedule. Together they cover finding, limiting, protecting, controlling and recovering data.
What are the most common data security mistakes?
Common mistakes include untracked data copies in test systems, standing admin access, service accounts with no owner, backups that were never restored, DLP left in audit mode indefinitely and AI tools connected before data is labelled. Each one is quiet until an incident exposes it, and each one is fixable once someone owns the gap.
Who is responsible for data security in an enterprise?
Accountability usually sits with the CISO, but responsibility is shared. Data owners in the business decide who may access their data and how it is classified. IT and platform teams run encryption, configuration and backups. Every employee handles data safely day to day, and the board oversees risk and incident disclosure decisions.
What are the 4 A's of data security?
The 4 A’s are authentication, authorization, accounting and auditing. Authentication proves who a user or system is, and authorization decides what that identity may access. Accounting records what was done, and auditing reviews those records to confirm controls work. Together they form the identity and evidence backbone of least-privilege access and compliance reporting.
How much does a data breach cost in 2026?
IBM’s Cost of a Data Breach Report 2026 puts the global average cost of a breach at USD 4.99 million, a record high and 12% above the prior report. Costs include detection, containment, notification, lost business and regulatory response. Faster detection and tested recovery are among the most direct ways to reduce that figure.
Which regulations require data security controls for US companies?
Listed companies must disclose material cyber incidents under SEC Form 8-K Item 1.05. Certain businesses covered by the CCPA face cybersecurity audit and risk assessment rules effective 1 January 2026. HIPAA covered entities and business associates must meet Security Rule safeguards, and anyone handling card data must meet PCI DSS v4.0.1. Sector and state rules add further duties.
What are the 7 principles of data security?
A practical set of seven is: know your data, give least privilege, encrypt everything sensitive, control where data moves, secure the platforms that hold it, monitor access continuously, and rehearse recovery. These map directly to the seven practices in this guide and to the Govern, Identify, Protect, Detect, Respond and Recover functions of NIST CSF 2.0.
What are the 7 principles of data protection?
GDPR Article 5 sets seven principles for personal data: lawfulness, fairness and transparency; purpose limitation; data minimisation; accuracy; storage limitation; integrity and confidentiality; and accountability. The security principle is integrity and confidentiality, while accountability requires you to prove compliance. Many teams use the list as a design checklist for any personal data system.
What are the 5 pillars of data security?
A common way to frame the five pillars is confidentiality, integrity, availability, authentication and non-repudiation. The first three form the CIA triad. Authentication confirms who is acting, and non-repudiation means actions are logged so nobody can later deny them. Enterprise controls such as MFA, encryption, backups and audit logs each support one or more pillars.
What are the types of data security?
The main types are access control, encryption, data masking and tokenization, data loss prevention, backup and recovery, and secure deletion. Some guides group them as three types: physical, technical and administrative controls. Others use four, adding data erasure or resilience. Enterprises usually need every type working together, since each one closes a different gap.
What are the four elements of data security?
Four elements often cited are confidentiality, integrity, availability and accountability. The first three protect data from exposure, unwanted change and loss of access. Accountability adds logging and ownership, so every access and change can be traced to a person or system. Together they define what a data security program must deliver and prove to auditors.
What are the 5 C's in security?
The 5 C’s are usually listed as change, compliance, cost, continuity and coverage. They are a planning lens for choosing security controls and providers. Change asks whether a control adapts as the business grows, while coverage asks whether it reaches every system, cloud and user. Different sources word the list slightly differently.
What is the 3-2-1 rule for data protection?
The 3-2-1 rule means keeping three copies of important data, on two different types of media, with one copy stored off-site. Many teams now extend it by making one copy immutable or offline, because ransomware often targets backups. The rule only protects you if restores are tested regularly against agreed recovery time objectives.




