TL;DR
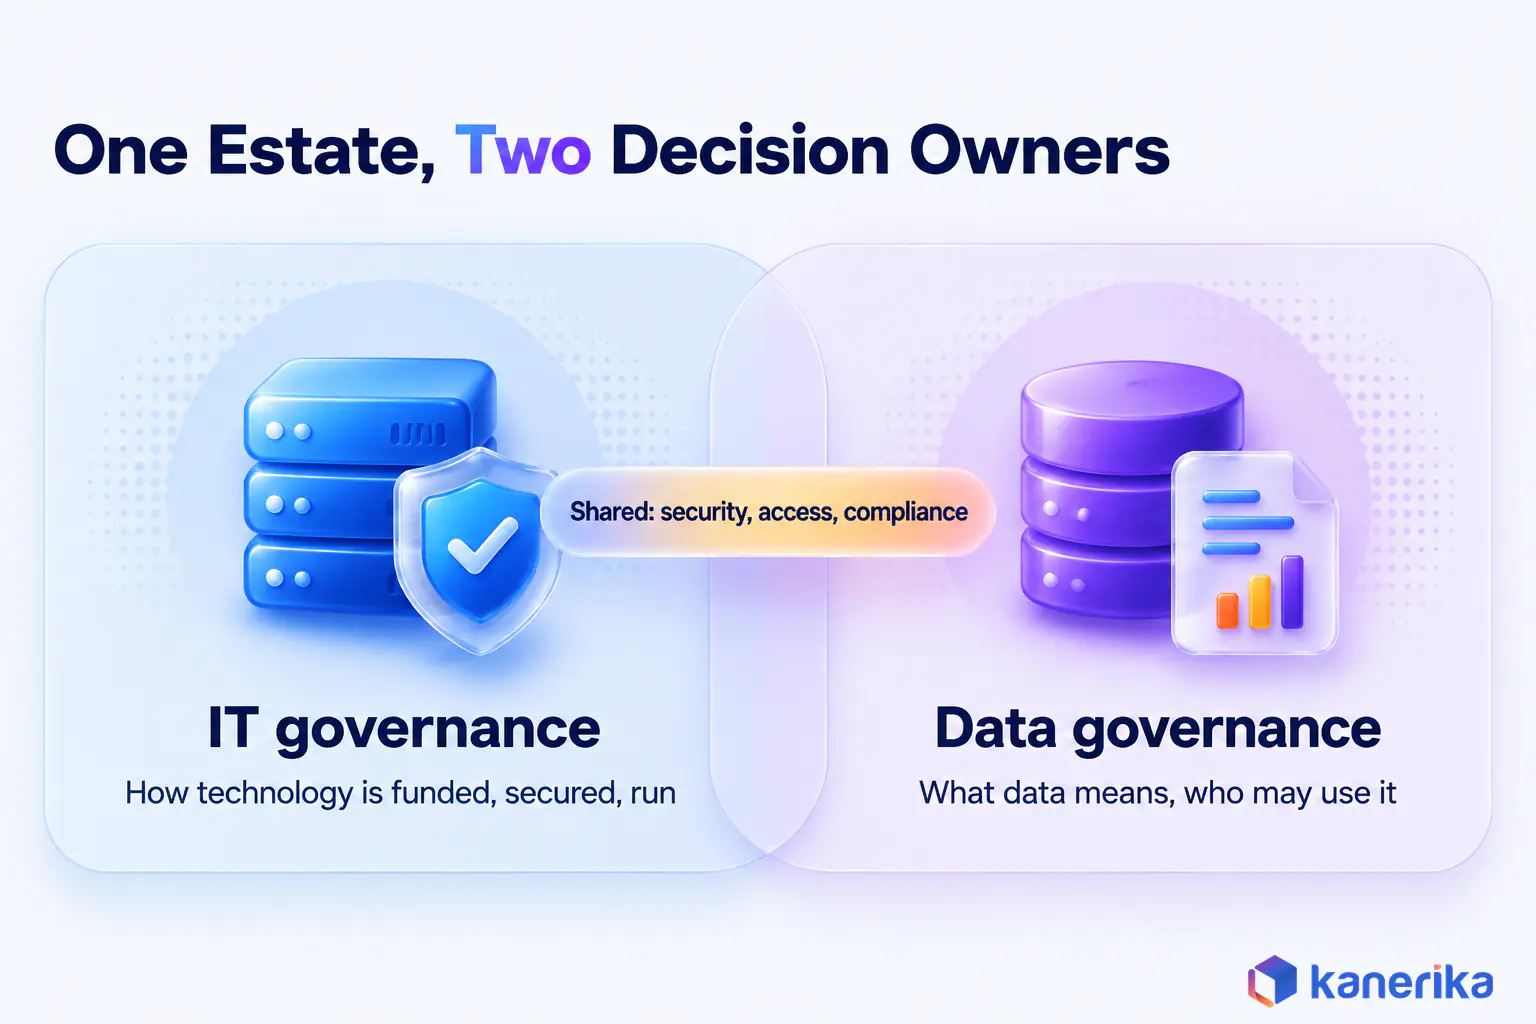
IT governance vs data governance comes down to who holds which decision rights over the same technology and data estate. IT governance, led by the CIO and an IT steering committee, sets how technology is funded, secured and run. Data governance, led by a chief data officer and a data council, sets what data means, who owns it and how it may be used. The two share security, access control and compliance, which is where most of the friction appears. Run both under one oversight forum with separate decision rights, rather than nesting one inside the other. If outages or shadow IT hurt most, fix IT governance first, and if teams argue over numbers or AI pilots stall on data, fix data governance first.
Key Takeaways
- IT governance decides how technology is funded, secured and run, and the CIO is accountable for it.
- Data governance decides what data means, who owns it and who may use it, and a CDO or data council is accountable for it.
- The two meet on security, access and compliance, so each shared decision needs one named owner.
- COBIT and ISO/IEC 38500 guide the IT side, while DAMA-DMBOK and DCAM guide the data side.
- Regulations such as SOX, HIPAA and GDPR place duties on both functions at once.
- Symptoms tell you which side to fix first, and a 90-day sequence can align both under one council.
The Fabric Rollout Where Nobody Could Define a Customer
Picture a US retailer moving its reporting onto Microsoft Fabric. The CIO’s steering committee approves the capacity, the security model and the budget in two meetings. So on paper, the project is fully governed.
Then the first sales dashboard goes live. Marketing counts an active customer as anyone who bought in the last 12 months, finance uses 6 months, and the loyalty team counts app logins. Three numbers reach the board, so each team ends up defending its own.
Still, nobody in the room has the authority to pick one definition.
The steering committee governs the platform rather than the meaning of the data on it. That gap sits at the heart of IT governance vs data governance, and it explains why a well-run platform can still produce numbers nobody trusts. The same split shows up in Microsoft Fabric governance, where workspace security and data ownership are two separate questions with two separate owners.
IT Governance vs Data Governance: The Differences at a Glance
The quickest way to tell the two apart is to ask which question each one answers. IT governance asks whether the company is spending on the right technology and running it safely. Data governance instead asks whether the company’s data is defined, trusted and used within the rules.
Ten Dimensions Side by Side
Both are governance in the same sense. They set decision rights, policies and accountability, and then check that people follow them. The difference lies only in what they govern, as the table below shows across ten dimensions.
| Dimension | IT governance | Data governance |
|---|
| Purpose | Align technology spending and operations with business goals and manage technology risk | Make data accurate, consistently defined, protected and used within policy |
| Core question | Are we investing in and running the right technology? | Can we trust this data, and who may use it for what? |
| Scope | Infrastructure, applications, vendors, projects, cyber risk | Definitions, quality, classification, lineage, access policy, retention |
| Accountable owner | Board and CIO | CDO or CDAO, with business data owners |
| Decision body | IT steering committee or architecture board | Data governance council |
| Frameworks | COBIT, ISO/IEC 38500 | DAMA-DMBOK, DCAM |
| Typical policies | Change management, access management, vendor selection, disaster recovery | Data definitions, quality thresholds, classification, retention, data sharing |
| Tools | IT service management, identity and access management, security monitoring | Data catalog, lineage, data quality and classification tools |
| Typical KPIs | Uptime, project ROI, patch latency, audit findings | Data quality score, owner coverage, access-review completion, lineage coverage |
| Failure symptom | Outages, budget overruns, shadow IT | Conflicting reports, failed data audits, stalled AI pilots |
Read the table by rows rather than columns. Every row shows two owners answering two different questions about the same estate, and both are needed for a working system.
Case Study
Zero Breaches, 100% Compliance for a Bank with Purview
A global bank had a mature IT estate across SAP, Dynamics 365, Oracle and Netezza but no unified data governance. Microsoft Purview classified its sensitive data and automated lineage, with zero breaches and 72% better classification accuracy.
Read the Case Study →
What Is IT Governance?
IT governance is the system a company uses to decide how technology is funded, built, secured and run, and who answers for those choices. It sits above day-to-day IT management. Managers run the service desk and the data center, while governance sets the rules they work within.
A simple test separates the two. For instance, choosing which cloud provider to standardize on is a governance decision. Restarting a failed server at 2 a.m., on the other hand, is management.
Decisions IT Governance Owns
IT governance owns the decisions that commit money, shape architecture or change the company’s exposure to technology risk. These choices are expensive to reverse, so they go through a formal body rather than one manager’s judgment.
- Investment: which projects get funded and in what order.
- Architecture: the standard platforms, integration patterns and cloud choices.
- Vendors: selection, contracts and exit plans for suppliers.
- Availability: uptime targets, backup and disaster recovery.
- Change: how changes to production systems are approved and rolled back.
- Cyber risk: identity, network security and incident response standards.
Notice, though, what is missing from that list. Nothing in it says what a customer, a product or revenue means, because those are questions about data rather than technology.
Who Runs IT Governance
The board holds final accountability, since technology risk is business risk. In practice the board delegates to the CIO, who chairs or sponsors an IT steering committee of business and technology leaders.
The CISO also owns security policy within that structure, often with a direct line to the board’s risk or audit committee. An architecture review board may sit underneath, checking that projects follow the agreed standards before they go live. The pattern is a clear chain from board to committee to the teams that carry out the work.
What Is Data Governance?
Data governance is how a company decides what its data means, who owns it, how good it must be and who may use it. It treats data as a business asset with named owners, in the same way that finance treats cash or HR treats employee records.
Ownership is the part that surprises people. In a working program, the head of sales owns the customer definition and the CFO owns revenue. The IT team runs the systems that hold the data, but it does not decide what the data should say.
Decisions Data Governance Owns
Data governance owns the decisions about meaning, trust and permitted use. These are business decisions, which is why they need business owners rather than system administrators.
- Definitions: the agreed meaning of terms such as active customer or net revenue.
- Quality thresholds: how complete, accurate and timely each critical data element must be.
- Classification: which data counts as public, internal, confidential or regulated.
- Access policy: who may see or use each class of data, and for what purpose.
- Lineage: where each important figure comes from and what changed it.
- Retention: how long data is kept and when it must be deleted.
Quality thresholds deserve a closer look, because teams often mix up quality with integrity. Our guide to data integrity vs data quality explains how the two differ and which one to fix first when a report breaks.
Checklist
Data Governance Checklist
A practical checklist for setting up data ownership, definitions, quality standards and access policies, so the data side of governance has named owners from day one.
Get the Checklist →
Who Runs Data Governance
A chief data officer, or chief data and analytics officer, usually leads the program and chairs a data governance council. The council then approves definitions and policies, and it settles disputes between business units.
Below the council sit three working roles. Data owners are senior business leaders accountable for a data domain, such as customer or product. Stewards then do the daily work of maintaining definitions, checking quality and answering questions.
Finally, data custodians, usually in IT, run the storage, security and backups that keep the data available. Because custodians sit in IT, theirs is the first role where the two governance systems visibly meet.
Is Data Governance Part of IT Governance?
This is the most common question about the two, and the honest answer is that it depends on how you draw the org chart. There are two models in use, and both can work when run well.
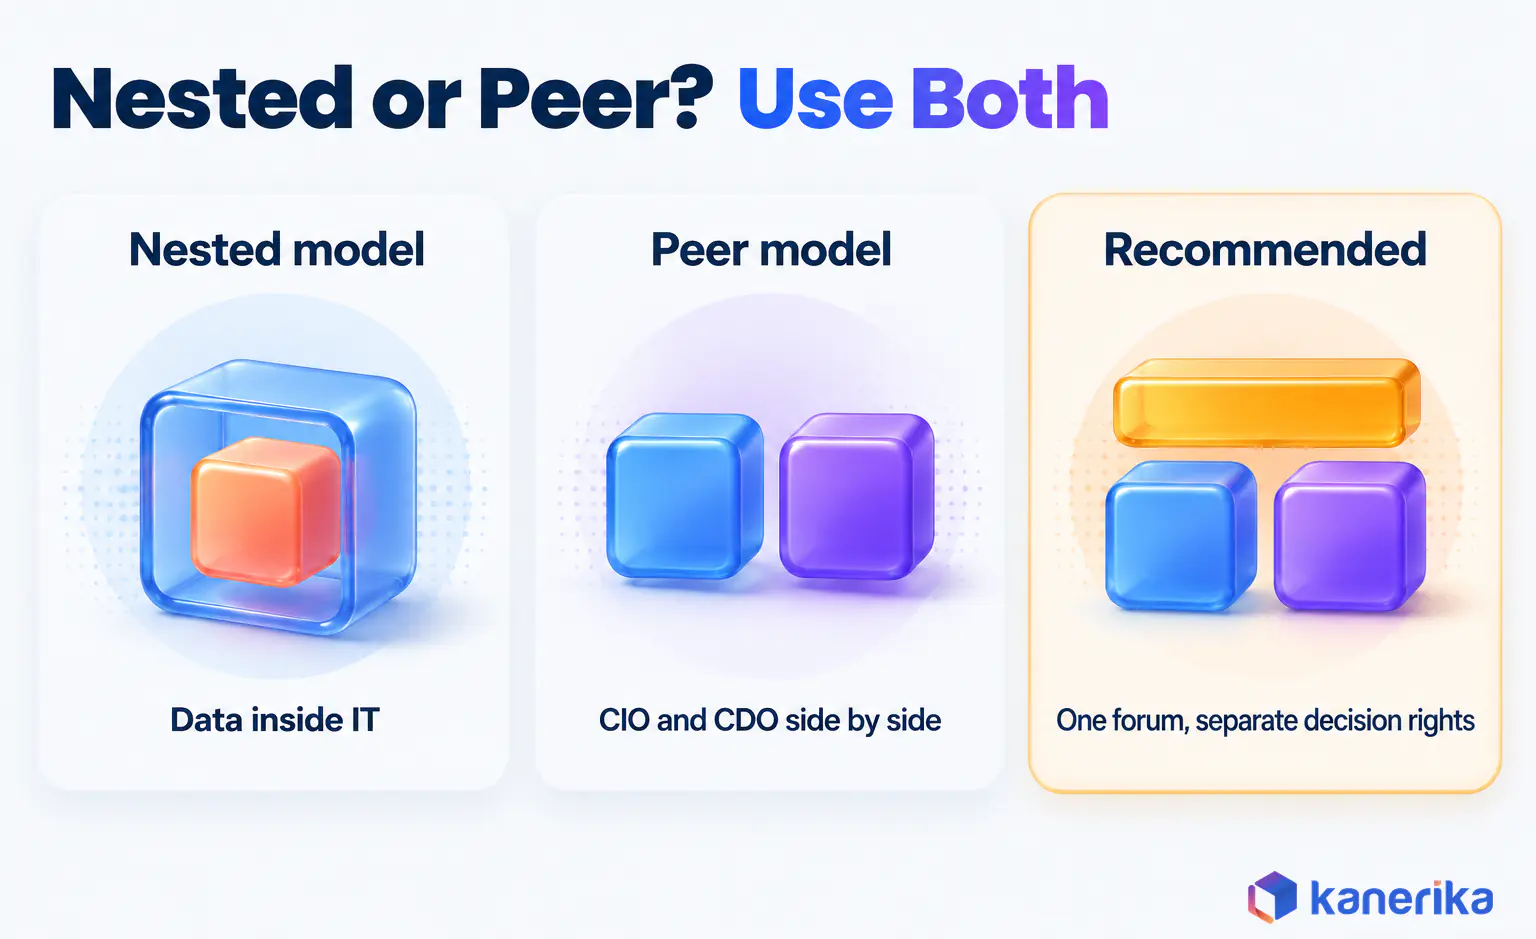
In the nested model, data governance sits inside IT governance as one of its programs. The CIO owns both, so the data council reports to the IT steering committee. This model is common when the data team grew out of IT, and it keeps one chain of command.
The weakness, though, shows up quickly. When data governance reports into IT, business leaders tend to treat definitions and quality as an IT problem. The retailer in our opening story would still have three definitions of an active customer, now with a ticket number attached.
In the peer model, the CDO and CIO sit side by side, and each owns a separate set of decision rights. Data governance then reports to the business, often through the COO, the CFO or the CEO. This makes business ownership real, but it can create two councils that disagree with no one to break the tie.
Our recommendation is a hybrid. Put both functions under one executive oversight forum for shared priorities and escalation, and keep separate decision rights underneath it. IT then decides how things run, the data side decides what the data means, and nobody has to guess which body owns a decision.
Where Technical Governance Fits
You will also see the term technical governance, which some platform vendors use for the IT side of this split. It covers the controls built into systems, such as access roles, encryption and monitoring. It is a useful label, but it describes enforcement rather than the business decisions behind it. A neighboring term also causes confusion, and our guide to data governance vs information governance sorts out that pair.
IT Governance vs Data Governance Examples: One Project, Two Sets of Decisions
The difference is easiest to see on a single project, so return to the Fabric migration from the opening. Every decision in that project belongs to one side or the other, although several come in pairs.
In each row below, the IT decision makes the platform work, while the data decision makes the output trustworthy. Skip either column, and the project still fails, just in a different way.
| Topic | IT governance decides | Data governance decides |
|---|
| Capacity | Which Fabric capacity size to buy and who pays for it | Which datasets are critical enough to load first |
| Metrics | Where the semantic model is hosted and how it is deployed | The approved definition of revenue and active customer |
| Security | Enforcing multifactor authentication for every user | Which roles may see customer personal data |
| Quality | Monitoring that pipelines run on schedule | The completeness threshold a sales table must meet before it is published |
| Change | How pipeline changes are tested and released | Who must approve a change to a certified metric definition |
| Retention | Backup schedules and storage tiers | How long transaction history is kept and when it is deleted |
A failure in the left column looks like an outage or a security incident. A failure in the right column looks like a dashboard nobody believes, which is quieter but often costs more trust.
How IT Governance and Data Governance Work Together
The two systems work best as a relay, where one side writes the rule and the other side builds it into the technology. Most of the friction between them comes from unclear handoffs rather than from real disagreement.
The Policy-to-Enforcement Handoff
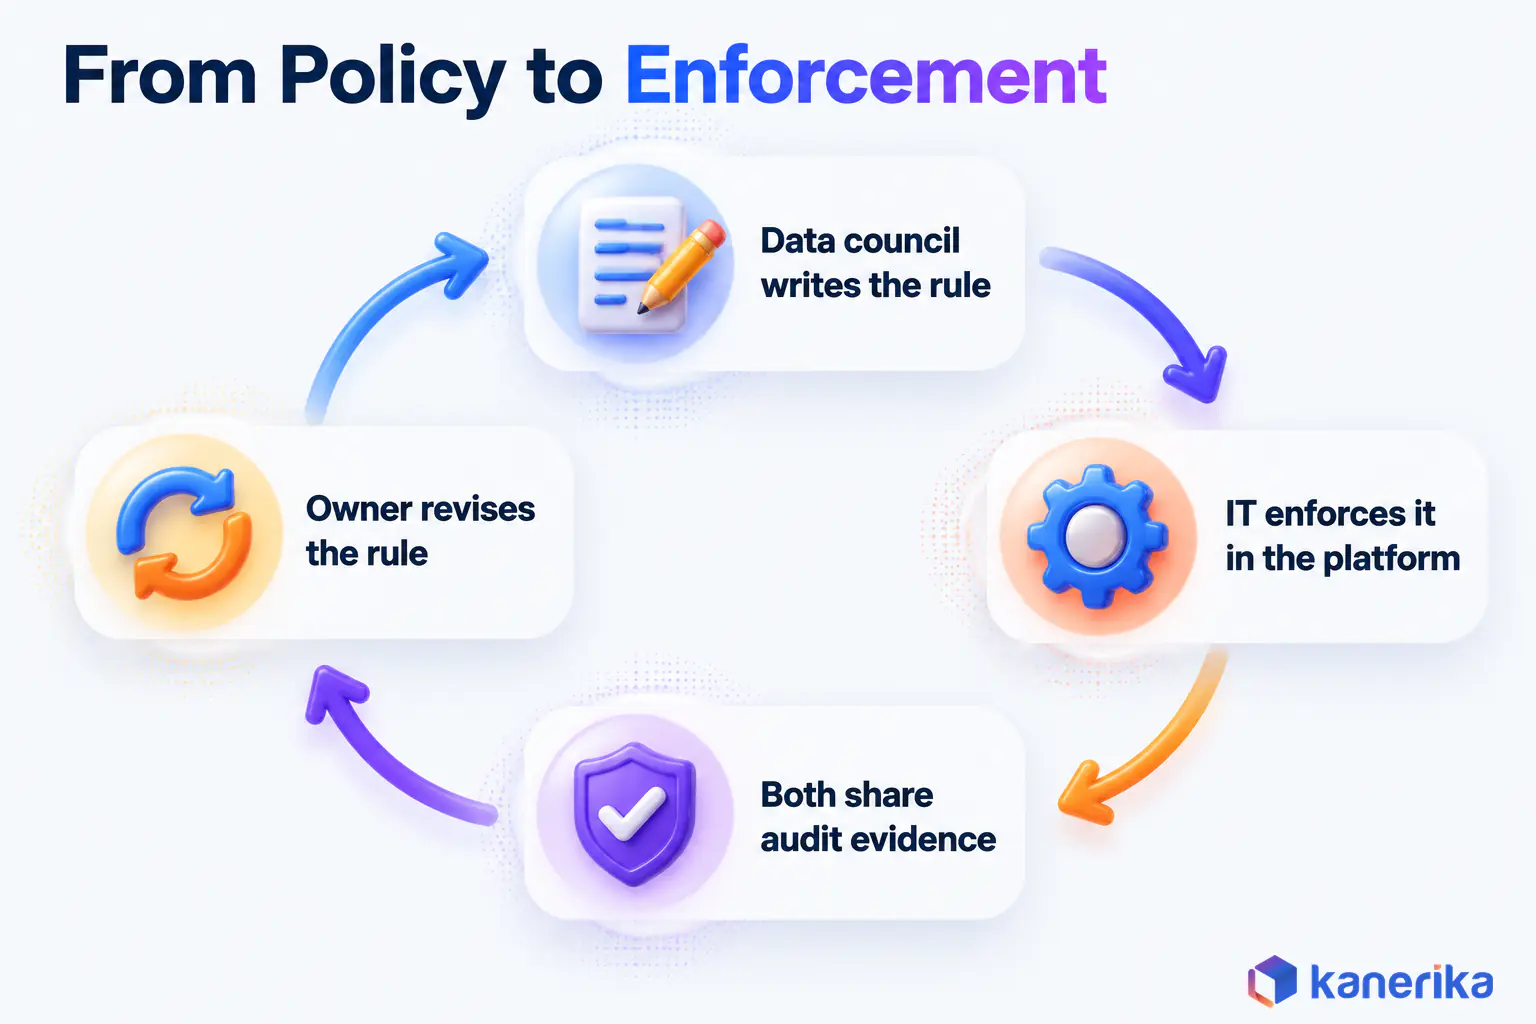
Take a rule that customer national ID numbers are restricted data. First, the data council writes that rule and names the data owner. IT then enforces it in the platform, through classification scans, sensitivity labels, access controls and data loss prevention policies.
Microsoft Purview also shows how close the two sides now sit. Its Data Map and Unified Catalog serve data governance, while Information Protection, data loss prevention and Insider Risk Management serve data security. Its Audit capability then collects the evidence that both sides hand to auditors.
The loop closes when audit results come back to the council. When people keep requesting exceptions to a rule, the rule may be wrong, and the data owner revises it.
A RACI for Shared Decisions
A RACI chart turns the handoff into named accountability. Each decision gets one accountable role, the people who do the work, and the people consulted before it is made. Everyone else on the list is simply kept informed, so the sample below leaves that column out.
| Decision | Accountable | Responsible | Consulted |
|---|
| Platform and capacity investment | CIO | Platform team | CDO, CISO |
| Business metric definitions | CDO | Data owner, data steward | Finance and business leads |
| Data classification scheme | CDO | Data steward | CISO, data owner, platform team |
| Labels and loss prevention rules in tools | CISO | Platform team | CDO, data steward |
| Approving access to a dataset | Data owner | Platform team | CISO, data steward |
| Identity and MFA standards | CISO | Platform team | CIO |
| Quality thresholds for critical data | Data owner | Data steward | CDO, platform team |
| Retention and deletion rules | CDO | Data steward, platform team | CISO, data owner |
Look at where accountability lands. The CIO holds it for investment and the CISO for security controls, while the data side holds it for meaning, quality and access. That pattern is the whole argument of this guide in one grid, so adjust the roles to your own organization but keep the split.
Settling Conflicts Between the Two
Conflicts still happen. For instance, a data owner may want a sensitive dataset opened to a new analytics team. The CISO wants it locked down until a review is done.
The fix is a defined escalation path. Disputes go first to the two people who hold the conflicting decision rights, before anyone else gets involved. If they still cannot agree within a set time, the question goes to the shared executive forum, which decides and records the reason.
Written decisions matter more than the forum’s name. Each ruling becomes a precedent, so the next similar dispute settles faster.
Kanerika Service
Data Governance Services
Kanerika helps you set decision rights, charter a shared council and enforce data policies in Microsoft Purview, so IT and data owners settle shared decisions in one place.
Explore Data Governance Services
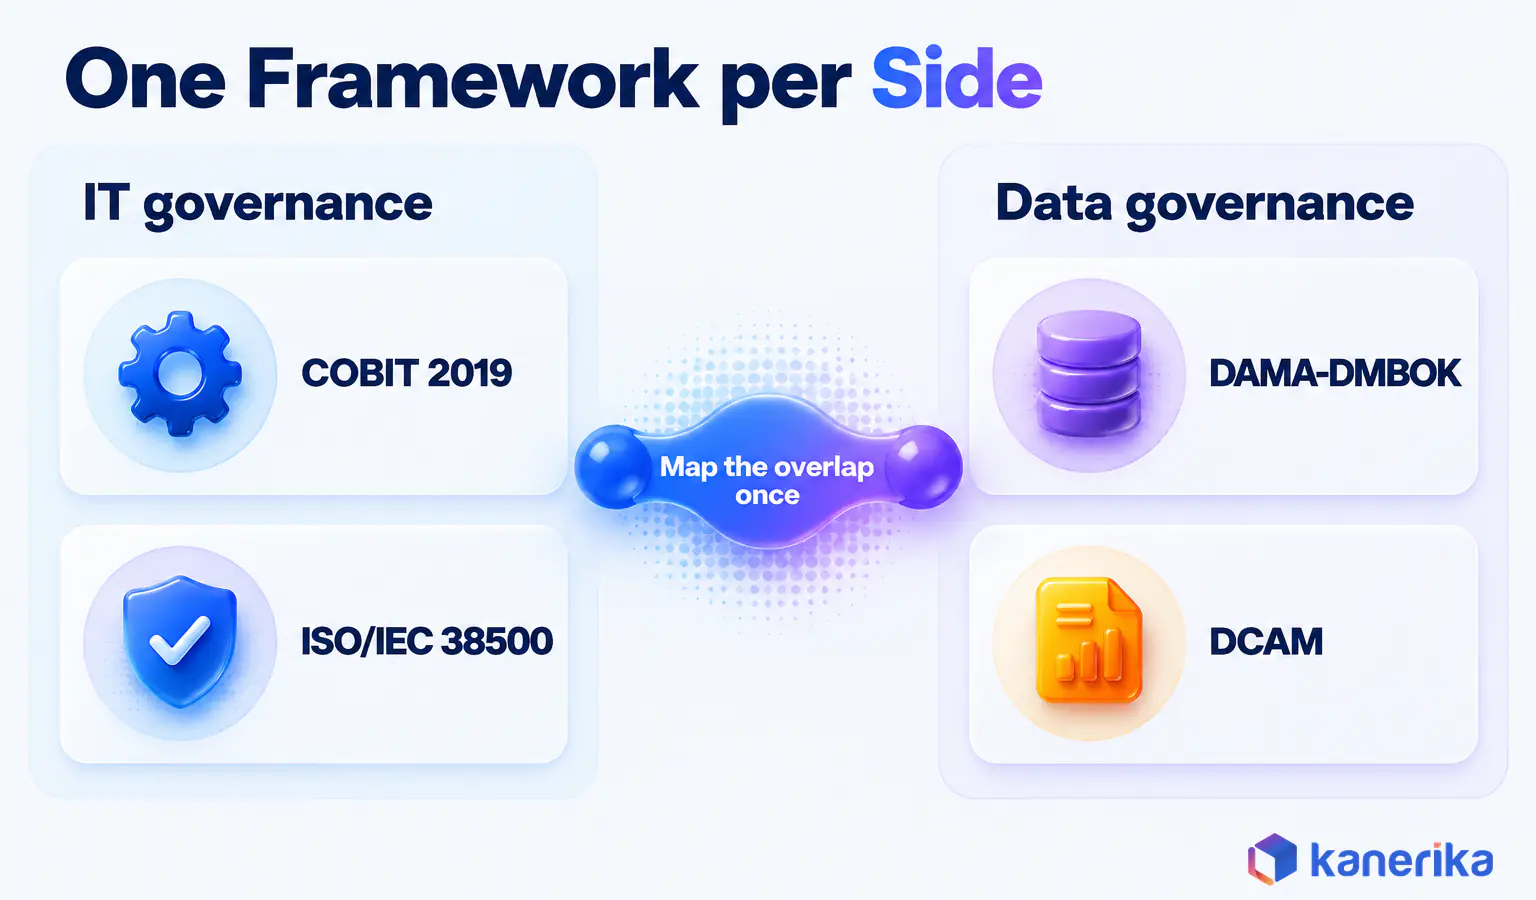
Frameworks: COBIT and ISO/IEC 38500 vs DAMA-DMBOK and DCAM
Each side of the split has its own reference frameworks, and knowing which is which saves a lot of wasted reading. None of them is a law. They are structured descriptions of good practice that a team adapts to its own size and risk.
On the IT side, COBIT from ISACA is the most detailed option. COBIT 2019 organizes its core model into 40 governance and management objectives covering planning, delivery and monitoring of IT. The 2024 edition of ISO/IEC 38500, by comparison, works at a higher level, guiding boards on governing the organization’s use of IT.
On the data side, the DAMA-DMBOK is the standard reference for data management as a discipline. The DMBOK2 Revision is the current edition, while DAMA started work on version 3.0 in 2025. The DCAM from the EDM Association is a capability model for scoring a data program. Its third version also adds cloud, AI and machine learning, and a stronger privacy focus.
| Framework | Side it covers | What it gives you | Typical user |
|---|
| COBIT 2019 | IT governance | 40 governance and management objectives with practices and metrics | CIO office, IT audit, risk teams |
| ISO/IEC 38500 | IT governance | Board-level guidance on governing the use of IT | Boards and executive committees |
| DAMA-DMBOK | Data governance | A body of knowledge for data management, with governance at its center | CDO office, data stewards |
| DCAM | Data governance | A capability model for assessing and scoring a data program | Banks and other regulated firms |
Do You Need Both?
Most mid-size and large companies need one framework from each side, because neither covers the other’s ground in depth. COBIT touches on data, but it will not tell you how to run a stewardship program. DAMA-DMBOK, likewise, will not tell the board how to weigh a cloud contract.
Pick one per side and map the overlaps once. Access control, security and audit evidence, for example, appear in both. Assign each overlapping control to one owner, and reference it from the other framework instead of building it twice.
Which Regulations Land on Which Function
A single regulation usually puts duties on both functions at once, whichever way your org chart splits governance. Knowing which half of each duty belongs to which function prevents the gaps that auditors find later.
The pattern repeats across laws, so it is worth learning once. IT governance owns the systems and controls. Data governance, meanwhile, owns knowing what the data is, where it lives and what it may be used for. The following four examples take a US company’s point of view.
| Rule | What it requires | IT governance owns | Data governance owns |
|---|
| SOX Section 404 | Management states its responsibility for internal control over financial reporting and assesses that control each fiscal year | Access, change and operations controls on financial systems | Definitions and lineage of the figures that feed financial reports |
| HIPAA Security Rule, 45 CFR 164.308(a)(1) | A risk analysis is a required implementation specification | Technical safeguards, access control and audit logging | An inventory of where electronic health data lives and who owns each source |
| GDPR Article 5(2) and Article 30, for US firms handling EU personal data | The controller must be able to demonstrate compliance and keep records of processing activities | Security controls, logging and incident detection on processing systems | Records of processing, purposes, retention rules and approved uses |
| NIST AI RMF 1.0 | A voluntary framework for managing AI risk, with a Generative AI Profile added in July 2024 | Model hosting, access, monitoring and change control | Provenance, quality and permitted use of training and grounding data |
Why AI Needs Both Halves
The AI row is where the split matters most. NIST released AI RMF 1.0 on January 26, 2023, and added a Generative AI Profile, NIST-AI-600-1, on July 26, 2024. AI also works on the data side from the other direction, because much of the cataloging, classification and quality checking that stewards once did by hand now runs on AI platforms for data management. A model can be well hosted and still be trained on data nobody approved for that use, so AI governance needs both halves. Teams comparing AI governance tools should check that a tool covers data lineage and usage policy as well as model monitoring.
Which Should You Fix First?
Fixing both systems at the same time stretches budget and attention, so the practical question is where to start. The answer comes from the symptoms you already see rather than from a maturity model.
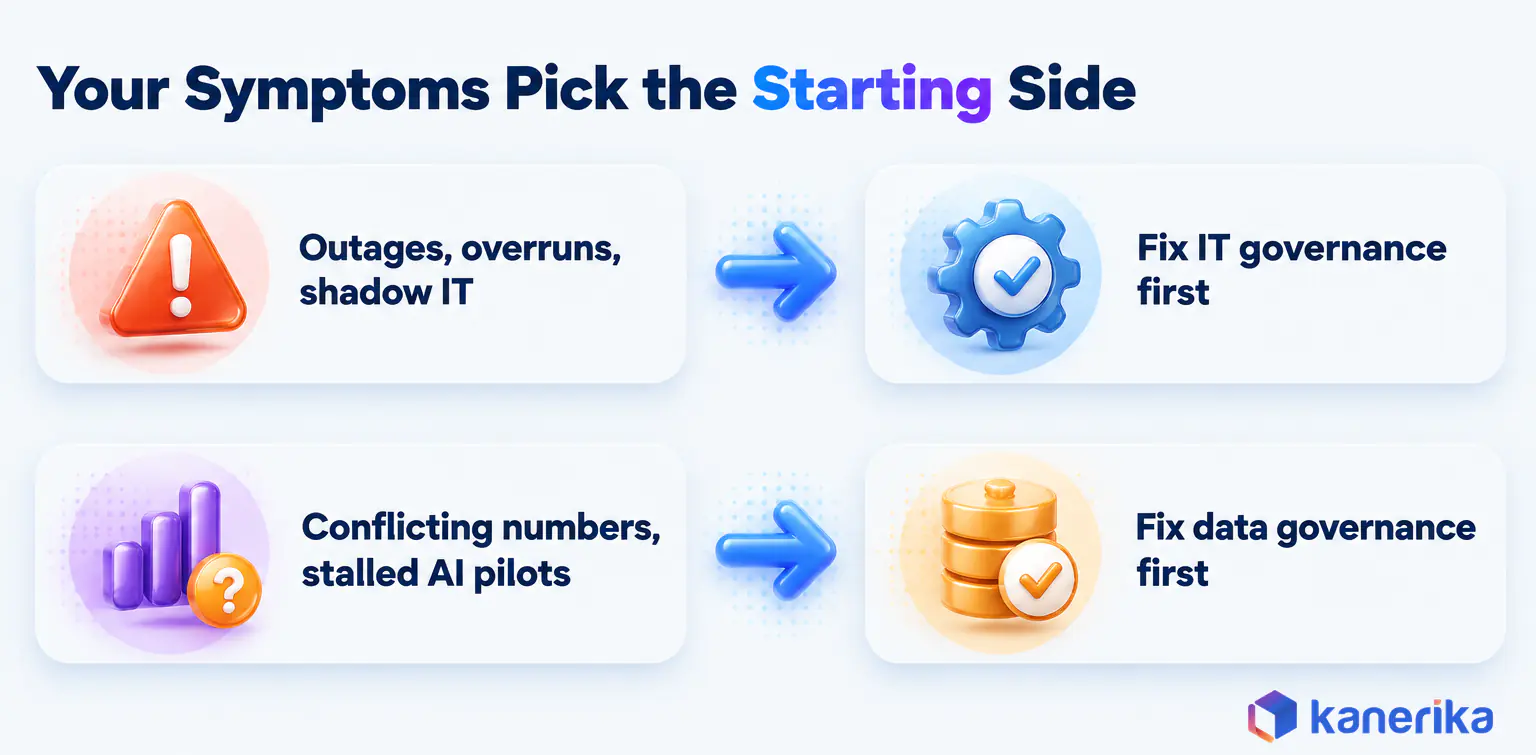
Read the Symptoms
Each symptom below points to one side. When your list is split evenly, start with the side whose failures reach customers or regulators first.
| Symptom you see | Fix first |
|---|
| Frequent outages or slow incident recovery | IT governance |
| Projects over budget or running late | IT governance |
| Teams buying their own tools without review | IT governance |
| Two reports showing different numbers for the same metric | Data governance |
| Audit findings about data access, retention or lineage | Data governance |
| AI pilots stuck because nobody can approve the data | Data governance |
The retailer from the opening, for instance, had a working platform and three versions of the truth. Its first fix was a data owner for the customer domain, not another infrastructure review.
A Phased Alignment Sequence
Once you know where to start, align both sides in five steps. The timing below assumes a mid-size company with an existing IT steering committee, so it fits in roughly 90 days.
- Inventory decisions (weeks 1-2). List the recurring decisions about technology and data, and note who makes each one today.
- Name owners (weeks 3-4). Give each decision one accountable role, then publish the RACI so everyone can see it.
- Charter a shared council (weeks 5-6). Set up one executive forum, co-chaired by the CIO and CDO, with a written escalation path.
- Pick one control plane (weeks 7-10). Use a single tool set for catalog, classification and access evidence, such as Microsoft Purview Data Map and Unified Catalog.
- Measure (weeks 11-13). Baseline the KPIs for both sides, then review them each quarter at the council.
This sequence aligns the two systems, but it does not design your data program from scratch. To build a data governance framework with policies, roles and a rollout plan, follow our step-by-step guide instead.
KPIs to Track for Each
Measure each side on its own terms. IT measures tell you whether technology is reliable and well spent, while data measures tell you whether the data is owned and trusted.
| IT governance KPI | Data governance KPI |
|---|
| Uptime of critical systems | Data quality score for critical data elements |
| Return on IT projects | Share of critical data elements with a named owner |
| Patch latency for security fixes | Completion rate of periodic access reviews |
| Open IT audit findings | Lineage coverage for regulatory and board reports |
Keep the list short. Four measures per side, reviewed every quarter, beat a dashboard of forty that nobody reads.
Watch on YouTube
Empower Your Business with Kanerika’s Data Governance Solutions | Microsoft Purview Integration
See how Kanerika uses Microsoft Purview to discover, classify and govern data across an estate, the single control plane from step 4 of the alignment sequence.
Where Alignment Stalls
Governance often means new rules. Teams may resist, particularly if they view it as additional work or a challenge to their control. These issues often connect with IT compliance challenges and best practices, especially when organizations try to implement new governance structures. Even the strongest governance plans can fail without support from both users and leadership.
Three mistakes also cause most stalls. The first is treating data governance as an IT project instead of a business one. A team buys a catalog, nobody is named as owner, and soon the tool fills with stale entries.
The second is running two councils with no tie-breaker, so every cross-cutting dispute waits for a meeting that never resolves it. The third is waiting for a reason to act. Gartner predicted in 2024 that by 2027, 80% of data and analytics governance initiatives will fail due to a lack of a real or manufactured crisis.
A failed audit, a stalled AI pilot or a board question about conflicting numbers can be that crisis, so use it to get the mandate. Our guide to data governance challenges also covers the other common blockers.
How Kanerika Aligns IT and Data Governance
Kanerika works on the boundary this guide describes, where IT controls and data decisions meet in one platform. As a Microsoft Solutions Partner for Data and AI, we build that meeting point on Microsoft Purview. Data owners set the rules there, while IT enforces them from the same catalog.
Our data governance services run on three accelerators. kanGovern handles discovery, cataloging and governance on Purview and Databricks Unity Catalog. kanGuard extends that work to data security, and kanComply to compliance.
A global bank shows the pattern. The bank runs nearly 9,000 branches and 22,000 ATMs, with data spread across SAP, Dynamics 365, CRM, Oracle and Netezza and no unified data governance. Its IT estate was mature, but nobody could see what sensitive data lived where.
We used the Purview Data Map to discover and classify assets automatically, applied Purview policies to personal, payment card and health data, and automated lineage. The bank case study reports zero data breaches, 100% adherence to compliance regulations and a 72% improvement in classification accuracy. Both disciplines now work from one control plane.
Talk to Kanerika
Map Who Decides What Across Your IT and Data Estate
In a working session, Kanerika reviews your current governance decisions, flags the ones with no clear owner and sketches a shared council and Purview control plane to close the gaps.
Schedule a Demo →
The Bottom Line: Who Decides What
IT governance decides how technology is funded, secured and run, and data governance decides what data means, who owns it and who may use it. Neither belongs inside the other. Put both under one oversight forum, give every shared decision a single accountable owner, and fix whichever side your symptoms point to first. That is how to settle IT governance vs data governance in practice: one forum above, two sets of decision rights below.
Frequently Asked Questions
What is the difference between IT governance and data governance?
IT governance decides how technology is funded, secured and run, and the CIO is accountable for it. Data governance decides what data means, who owns it, how good it must be and who may use it, usually under a chief data officer. They overlap on security, access and compliance, so shared decisions need one named owner.
What is IT governance in simple words, and why does it matter?
IT governance is the set of rules and decision rights that tells a company which technology to buy, how to run it and who answers for the risk. It matters because technology choices are expensive and hard to reverse. Good IT governance keeps spending tied to business goals and stops outages and security gaps from growing unnoticed.
What is the difference between data governance and information governance, and is there another term for it?
Data governance focuses on structured data, its definitions, quality and access. Information governance is broader and covers all information, including documents, email and records, with a strong focus on retention, legal holds and records management. Some teams also use data stewardship for the same ground, though that term usually describes a narrower part of it.
What are the main roles in data governance?
The main roles are the chief data officer, who leads the program, and the data governance council, which approves policies. Data owners are business leaders accountable for a domain. Data stewards maintain definitions and check quality day to day. Data custodians, usually in IT, run the storage, security and backups that keep the data available and protected.
What is governance in ITIL 4?
In ITIL 4, governance is one part of the service value system. It describes how an organization is directed and controlled, and it guides how services are planned, delivered and improved. ITIL 4 does not replace an IT governance framework such as COBIT. It focuses on service management, and governance gives it direction and oversight from above.
What are examples of IT governance and data governance decisions?
IT governance decisions include which cloud platform to standardize on, which projects get funded, how production changes are approved and what multifactor authentication standard applies. Data governance decisions include the approved definition of revenue, which roles may see customer personal data, the quality threshold a report must meet before publication and how long transaction history is kept.
What is the difference between data governance and technical governance?
Technical governance refers to the controls built into systems, such as access roles, encryption, monitoring and deployment rules, and it belongs to the IT side. Data governance sets the business rules those controls enforce, such as who may see customer data and what a metric means. Technical governance answers how a rule is enforced, while data governance decides the rule.
Which should a company implement first, IT governance or data governance?
Start with the side your symptoms point to. Outages, budget overruns and shadow IT point to IT governance first. Conflicting reports, data audit findings and AI pilots stuck on unapproved data point to data governance first. If both appear, start where failures reach customers or regulators soonest, and then align the two under one council.
What is the difference between COBIT and DAMA-DMBOK?
COBIT is an IT governance framework from ISACA that covers how technology is planned, delivered and monitored, with 40 governance and management objectives in COBIT 2019. DAMA-DMBOK is a body of knowledge for data management, with data governance at its center. Most companies use one of each, since neither covers the other’s ground in depth.
What KPIs measure IT governance and data governance success?
IT governance is usually measured by uptime of critical systems, return on IT projects, patch latency for security fixes and open audit findings. Data governance is measured by data quality scores, the share of critical data elements with a named owner, completion of access reviews and lineage coverage for regulatory and board reports, all reviewed every quarter.
How does data governance support AI governance?
AI systems are only as trustworthy as the data they learn from and draw on. Data governance supplies the provenance, quality checks and usage permissions that AI governance needs. NIST released its AI Risk Management Framework in January 2023 to help organizations manage AI risk. IT governance then controls how models are hosted, accessed and monitored.
Is data governance part of IT governance?
It can be, but a hybrid works best. In a nested model, data governance reports to the CIO, and business leaders often treat data as an IT problem. In a peer model, the CDO and CIO hold separate decision rights, which can leave two councils disagreeing. The hybrid puts one shared oversight forum above two separate sets of decision rights.
What falls under data governance?
Data governance covers the decisions about meaning, trust and permitted use of data. That includes business definitions, quality thresholds for critical data, classification of sensitive data, access policy, lineage and retention rules. It also names the people responsible, such as data owners, stewards and custodians, and sets how disputes between business units about data get settled.
Who is responsible for IT governance vs data governance?
The board holds final accountability for IT governance and delegates it to the CIO, who usually chairs an IT steering committee with the CISO owning security. Data governance is led by a chief data officer or chief data and analytics officer, a data governance council, and business data owners who are accountable for domains such as customer or product.
Should data governance report to the CIO or the CDO?
Data governance usually works better under a CDO or another business executive than under the CIO. Reporting into IT tends to turn definitions and quality into technical tickets that business leaders ignore. The CIO still plays an essential part, since IT enforces the rules in systems. A shared executive forum lets both leaders settle cross-cutting decisions together.
Can IT governance and data governance work together, or run without each other?
They can run separately for a while, but each fails in its own way without the other. Strong IT governance alone delivers reliable platforms full of untrusted data. Strong data governance alone writes rules that nobody enforces in systems. They work together as a relay, where the data council writes the rule and IT builds it into the platform.
Which frameworks are most commonly used for IT governance?
COBIT from ISACA and ISO/IEC 38500 are the most widely used IT governance frameworks. COBIT 2019 organizes its core model into 40 governance and management objectives. ISO/IEC 38500, revised in 2024, gives boards guidance on governing the use of IT. Many companies also use ITIL for service management, which supports governance without replacing it.
What are the main focus areas of IT governance?
IT governance focuses on aligning technology with business strategy, getting value from IT investments, managing technology and cyber risk, managing resources such as people, vendors and infrastructure, and measuring performance. Different frameworks group these areas in different ways, so treat any fixed list as a starting point rather than a rule, and adapt it to your company’s own risk profile.
What are the core principles of data governance?
The core principles are clear accountability, with a named owner for each data domain, and shared definitions that everyone uses. Others include quality standards that are measured, transparency about where data comes from, protection of sensitive data, and policies that are applied consistently. Programs also need a way to settle disputes and to update rules as the business changes.




