TL;DR
Fabric data governance covers ownership, access and discovery on its own, but regulated data also needs Microsoft Purview. Fabric decides who owns each workspace, who can open it and which datasets people should trust. Purview adds protection, such as sensitivity labels and data loss prevention. Both need extra Purview licensing on top of Fabric. Set up ownership and access first, then add Purview, then check the results every month. Microsoft suggests growing governance in small stages as Fabric use grows.
Key Takeaways
- Fabric covers estate management, discovery, access control and governance health natively, so a Fabric-only team can start without Purview.
- Sensitivity labels and data loss prevention run through Microsoft Purview, and both need additional Purview licensing.
- Governance sits in five layers, from tenant to item, so each layer needs a named owner before data lands.
- The setup order matters more than the tools, starting with tenant settings and ending with monitoring.
- Copilot and data agents only see what the signed-in user can see, so weak workspace roles become weak AI boundaries.
- Owner coverage, endorsement coverage and label coverage show whether governance works, and the Govern section reports all three.
The Audit That Found Workspaces Nobody Owned
The auditor’s first request sounded simple. She wanted a list of every Fabric workspace that held customer data, and the person accountable for each one.
The platform team needed two weeks to answer, because pilot workspaces from the first rollout were still live. Several had no admin left in the company. One semantic model also fed six finance reports, yet nobody could say who had approved its revenue logic.
Nothing in that story was a breach. It was ordinary sprawl, the kind that builds up when a platform grows faster than its rules. Fabric makes it easy to create workspaces, lakehouses and reports, which is the whole point of the product. That same ease is why governance has to arrive before the data does, rather than after the audit.
This guide answers three practical questions. It shows what Fabric governs on its own, where Microsoft Purview takes over and what that costs in licenses. It then sets out the order to configure everything, so the next audit takes an afternoon.
What Is Fabric Data Governance?
Fabric data governance is the set of rules, roles and tools that decides who owns data in Microsoft Fabric and who can use it. It also covers how you prove that data was handled correctly, from tenant settings down to a single report.
Microsoft groups the work into five outcome areas in its Fabric governance and compliance overview. Each area answers a question that an auditor, an analyst or an admin might ask. The table maps each area to the tools that do most of the work.
| Outcome area | Question it answers | Main tools |
|---|---|---|
| Manage your data estate | What do we have, where does it run and who owns it? | Admin portal, domains, workspaces, capacities |
| Encourage trusted discovery | Which dataset should I use? | OneLake catalog, endorsement, tags, lineage |
| Protect, secure and comply | Who can see sensitive data, and can we prove it? | Workspace roles, OneLake security, Purview labels, DLP and Audit |
| Understand governance health | Where are the gaps, so we can fix them first? | Govern section insights and recommended actions |
| Monitor operations | What is running, and what is it costing? | Monitoring hub, Capacity Metrics app |
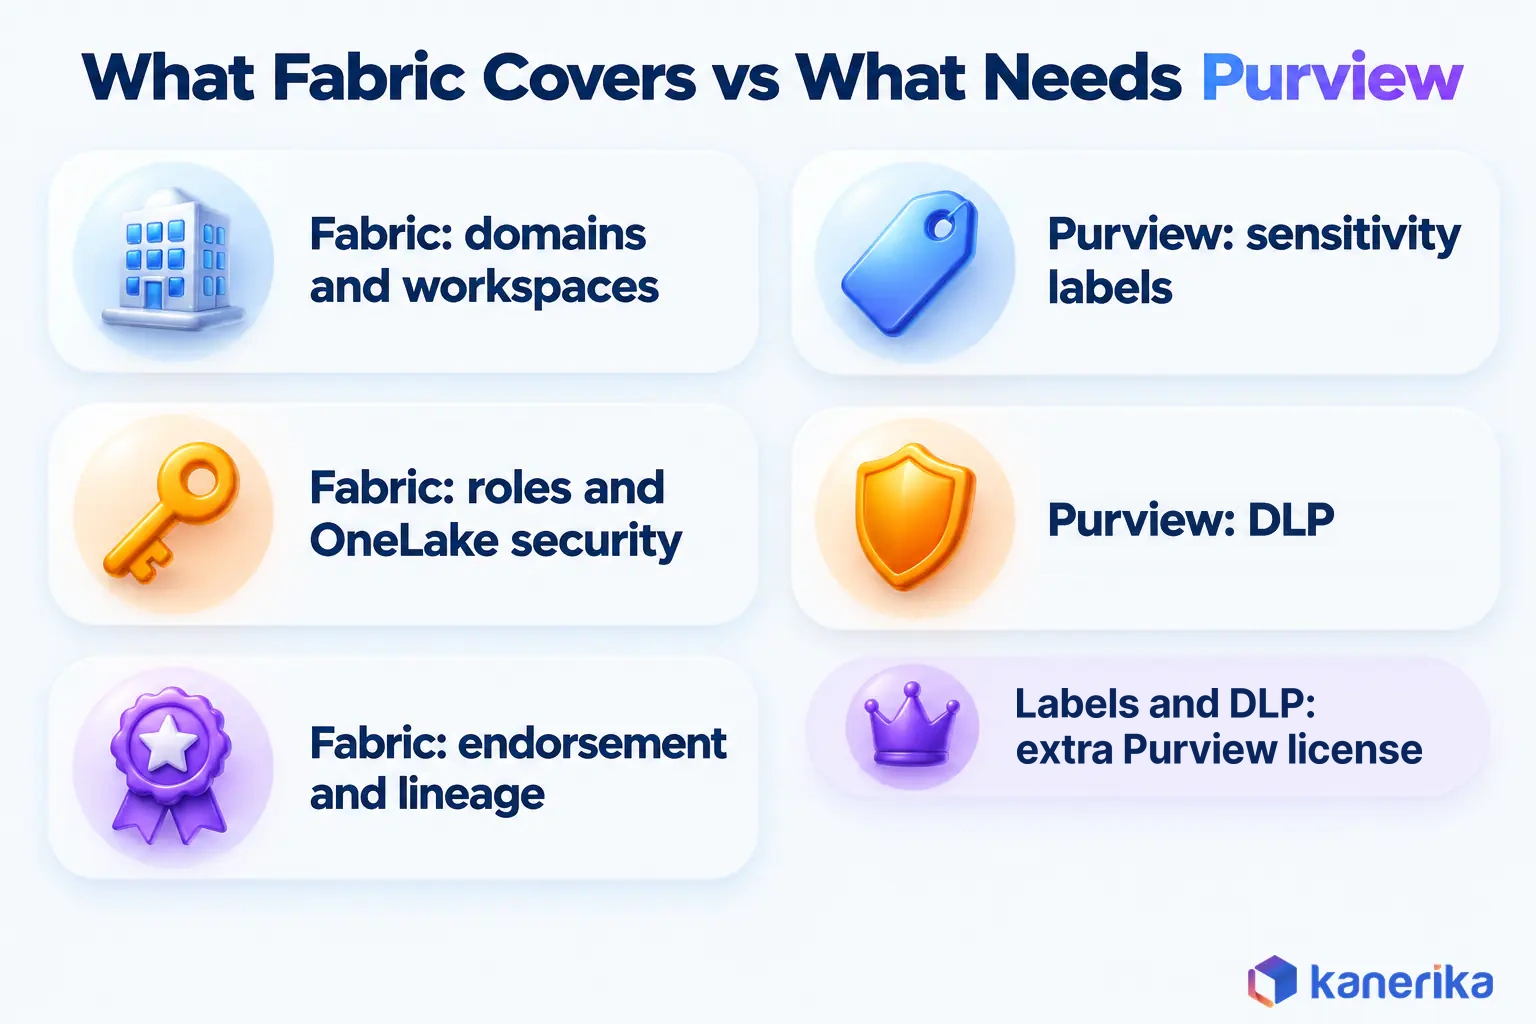
Two things stand out in that list. Most of the tools ship inside Fabric, while only the protection row leans heavily on Purview. Microsoft also states plainly that many capabilities come with the Fabric license, but some need additional Purview licensing.
Fabric holds certifications such as a HIPAA Business Associate Agreement and ISO/IEC 27001, 27017, 27018 and 27701. Of those, ISO 27701 covers privacy management, and this guide to ISO 27701 certification explains what it requires. Those certifications cover Microsoft’s side of the platform, though. How your tenant is configured is still your job, so that is what the rest of this guide covers.
How Governance Is Layered in Fabric: Tenant, Capacity, Domain, Workspace and Item
Fabric governance works like a set of nested boxes. A setting made at the outer box applies to everything inside it, unless someone with the right role overrides it further in.
The outer box is the tenant, where the Fabric admin decides which features exist at all. Inside it sit capacities, which supply compute, and domains, which group workspaces by business area. The two are independent, so one domain can span several capacities. Workspaces then hold items such as lakehouses, warehouses and reports. For example, a finance lakehouse inherits tenant rules, runs on a finance capacity, belongs to the Finance domain and lives in a finance workspace.
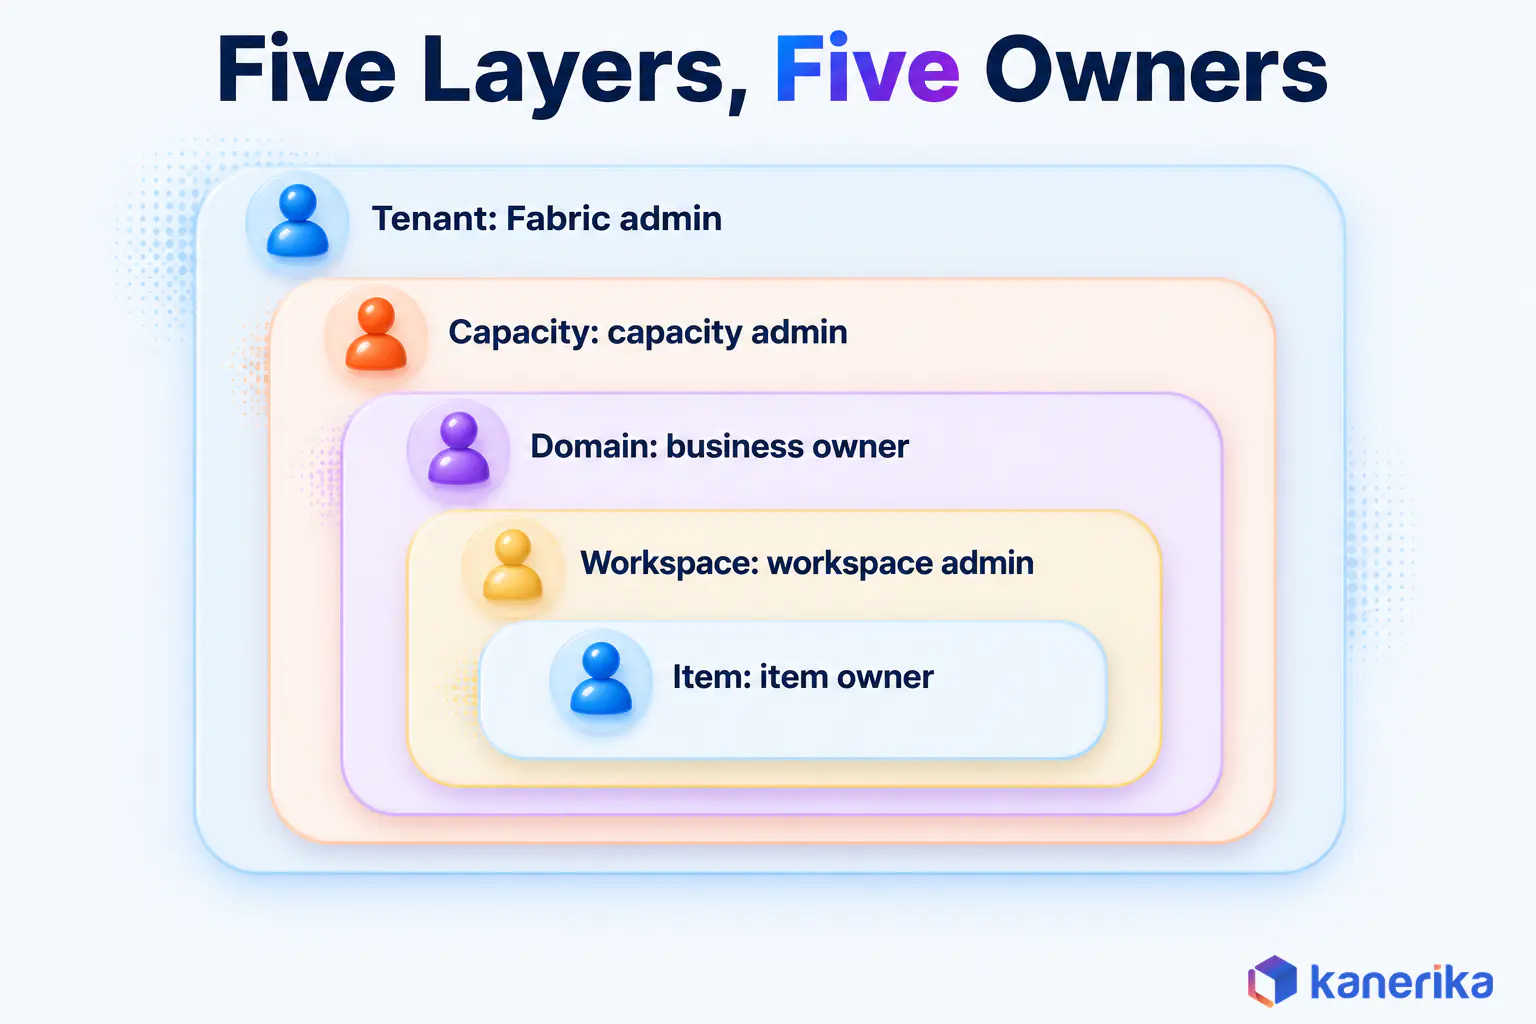
Each layer needs one accountable owner and one main decision. The table shows the usual split in an enterprise, so you can match names to rows before any data lands.
| Layer | Typical owner | Main decision |
|---|---|---|
| Tenant | Fabric admin in the central platform team | Which features are on, and for which security groups |
| Capacity | Capacity admin | Which workloads share compute, and who pays for it |
| Domain | Domain admin, ideally a business owner | Which workspaces belong to the business area |
| Workspace | Workspace admin | Who gets which role, through which group |
| Item | Item owner | Description, endorsement, label and sharing |
Tenant Settings and Delegated Administration
Tenant settings are the master switches for features such as export, external sharing, workspace creation and Copilot. Most of them can also be limited to named security groups instead of the whole organization.
Microsoft’s guidance is for Fabric admins to define tenant-wide settings and then delegate some of them to domain and capacity admins. Delegation lets a Finance domain admin tighten export rules for Finance, while Marketing keeps its own rules. Write down every setting you change and why, because undocumented changes are hard to defend later.
Domains and Subdomains
Domains group workspaces by business area, such as Finance, Sales or Supply Chain, while subdomains refine that grouping. They turn a flat list of workspaces into an estate that matches how the company is actually run.
Three roles manage domains in Microsoft Fabric. The Fabric admin creates domains and then assigns domain admins and contributors. Domain admins, ideally business owners, update descriptions and attach workspaces, but they cannot delete the domain. Domain contributors are workspace admins who may also assign their own workspaces to the domain.
Workspaces and Capacities as Isolation Boundaries
Workspaces are where most day-to-day access decisions happen, so their structure shapes everything else. A common pattern separates development, test and production workspaces for each team, while production stays locked to fewer people.
Capacities add a second boundary, this time for compute and cost. Microsoft suggests using capacities as isolation boundaries for compute and chargeback, so that a heavy data science job cannot slow the CFO’s dashboard. Our guide to Microsoft Fabric workspaces also covers naming and structure patterns in more depth.
Native Fabric Governance vs Microsoft Purview: Which Controls What?
The licensing split decides your budget, so it is worth getting precise. Fabric governs structure, access and discovery on its own, while Microsoft Purview governs classification and protection across Fabric and the wider Microsoft estate.
A practical test helps here. When a control decides who owns or can find something, it is usually native. When it classifies content or watches how people handle sensitive data, it usually runs through Purview. Microsoft confirms that both sensitivity labels in Fabric and Purview DLP require additional Purview licensing.
| Capability | Where it runs | Extra Purview license? |
|---|---|---|
| Tenant settings, domains, workspaces, capacities | Fabric | No |
| Workspace roles and OneLake security | Fabric | No |
| Endorsement, tags and descriptions | Fabric | No |
| Lineage and impact analysis | Fabric | No |
| Govern section insights and recommended actions | Fabric (OneLake catalog) | No |
| Sensitivity labels | Purview Information Protection, applied in Fabric | Yes, and Pro or PPU is also needed to label Power BI items |
| Data loss prevention policies | Purview DLP | Yes |
| Audit search of Fabric activity | Purview Audit | Usually no: Audit (Standard) is on by default with eligible Microsoft 365 plans, while Audit (Premium) costs extra |
| Insider Risk Management and AI interaction controls | Purview | Purview licensing |
So when should the Purview budget start? Buy it at the outset when regulated data, such as patient or financial records, lands in the first release. Otherwise finish the native setup first, and add Purview once owners and roles are clean.
The OneLake Catalog Govern Section
The OneLake catalog is Fabric’s built-in hub for finding and managing data, with three experiences named Explore, Govern and Secure. It also appears inside Teams, Excel and Copilot Studio, while a Catalog Search REST API exposes it to other tools.
The Govern section is the closest thing Fabric has to a governance dashboard. Governance admins get an All data estate view with insights, health signals and recommended actions. Data owners, by contrast, get a My data view scoped to the items they own. The data comes from the Admin Monitoring workspace, which Fabric creates when someone first opens Govern.
The expanded report has three tabs worth bookmarking. One covers the estate inventory, another covers freshness and endorsement coverage, and the third covers label coverage and DLP. For a walkthrough of the catalog itself, see our guide to the Microsoft Fabric OneLake catalog.
Where Native Governance Stops
Native tools are strong inside one Fabric tenant, but they get thinner at the edges. Knowing those edges early saves a painful redesign later.
- Lineage across workspaces. The lineage view shows connections inside a workspace, so Microsoft points you to impact analysis for downstream items elsewhere.
- Labels across tenants. Label protection does not follow data that is shared across tenants or exported to CSV or text files.
- Estates beyond Fabric. When key data also lives in other clouds or platforms, a Fabric-only catalog shows only part of the picture.
For that last case, the Purview Unified Catalog or another enterprise catalog may be worth the cost. Our Purview vs Collibra comparison weighs two common options. The test is simple. If auditors ask about systems Fabric never touches, you need a catalog that reaches them.
Talk to Kanerika
Not Sure Where Native Fabric Governance Ends?
Kanerika’s Fabric and Purview team reviews your tenant settings, domains and roles, then shows which gaps need Purview and which need only configuration.
Talk to a Governance Expert →Access Control in Fabric: Workspace Roles, Item Permissions and OneLake Security
Access control in Fabric works in layers too. Workspace roles open the door, item permissions share single items, and OneLake security then narrows what someone sees inside the data.
The four Fabric workspace roles grant rising levels of control. Assign them to Microsoft Entra security groups rather than individuals, so a leaver loses access once HR removes them from the group. Service principals can hold roles as well, which keeps automation off personal accounts.
| Role | What it allows | Give it to |
|---|---|---|
| Admin | Update or delete the workspace and manage all access | Two or three named owners per workspace |
| Member | Add people with lower permissions, then share and publish | Team leads |
| Contributor | Create and edit items | Engineers and report builders |
| Viewer | View content without changing it | Business consumers |
Item sharing lets someone open one report without joining the workspace. It is convenient, which is why shared links pile up quietly. Review them during every access review.
OneLake security adds role-based access inside items such as lakehouses. It is deny by default, and a role can also carry row-level and column-level security. Workspace roles stay the first boundary, so OneLake security mainly narrows what Viewers see.
Admins, Members and Contributors keep full data access through their write permission. For example, a Viewer in a finance workspace can be limited to one region’s rows. Roles that grant ReadWrite cannot carry row or column rules.
For SQL-level controls and network isolation, read our guide to data warehouse security in Microsoft Fabric. Our Power BI row-level security guide covers row rules inside semantic models.
Protecting Sensitive Data: Sensitivity Labels, DLP, Audit and Insider Risk
Protection is where Fabric hands the job to Microsoft Purview. These controls classify sensitive content, warn people who handle it badly and then record what happened for later review.
Sensitivity labels come first, because the other controls build on them. A label such as Confidential flows downstream to dependent items and carries into new items built from labeled ones. Power BI semantic models can also inherit a label from labeled data sources. Protection follows Power BI content outside Fabric only through supported export paths, such as Excel, PDF, PowerPoint and .pbix downloads. Our explainer on Microsoft Purview Information Protection covers label design.
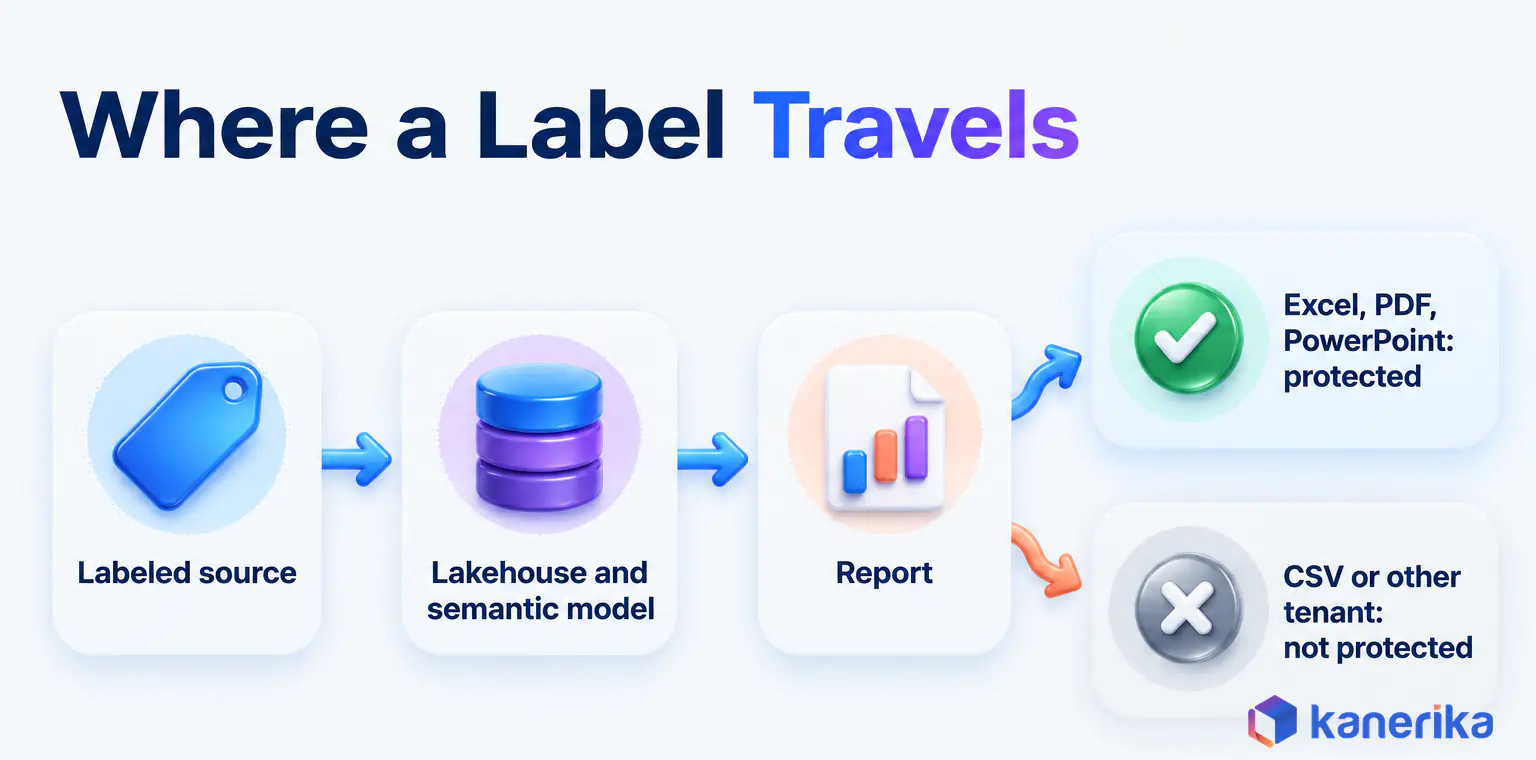
The table sets out each control and the limit to plan around.
| Control | What it does | Limit to know |
|---|---|---|
| Sensitivity labels | Classify items and carry protection downstream | No coverage for cross-tenant sharing or CSV and text export |
| Data loss prevention | Detect sensitive data, then raise policy tips and alerts | Restrict access was still in preview in October 2026, and evaluation runs when data changes |
| Purview Audit | Record lakehouse, Power BI, Spark and Data Factory activity | Searched in Purview rather than in Fabric |
| Insider Risk Management | Flag risky Power BI and lakehouse activity | Needs a risk policy and reviewers before it helps |
DLP, Audit and Insider Risk in Practice
DLP policies for Fabric cover semantic models, lakehouses, warehouses, KQL databases, mirrored databases, SQL databases and Cosmos databases. KQL databases are on that list, so event data you analyze with Real-Time Intelligence in Microsoft Fabric falls under the same policies. Semantic models are checked on publish and refresh, while other items are checked when their data changes. DLP evaluation consumes capacity too, so include it in sizing.
Insider Risk Management ships ready-to-use risk indicators for Fabric, such as Power BI and lakehouse activity. Turn it on after labels and DLP, once you know which data matters most.
Trusted Discovery: Endorsement, Tags, Lineage and Impact Analysis
Discovery is the part of governance that users actually feel. When analysts can find the right dataset in a minute, they stop building private copies, so there is less to secure.
Fabric gives you four discovery tools, and they work best in this order.
- Endorsement. Anyone with write access can promote an item they consider ready, while reviewers named by the Fabric admin certify items that meet the quality bar. A third badge, Master data, identifies the authoritative source for data such as customer lists. Endorsed items also rank higher in some searches.
- Tags. Fabric admins define a tag list, and data owners then apply those tags so consumers can filter by them.
- Lineage. The lineage view traces data from source to report inside a workspace, so owners can see every dependency. Our data lineage guide covers the wider practice.
- Impact analysis. Before changing an item, owners check which downstream items will break, even those in other workspaces.
Certification only works when someone owns the standard. Write down who may certify, what checks an item must pass and how often it is reviewed. A certified badge on an unreviewed model does more harm than no badge at all, because people trust it blindly.
Larger estates can also pull metadata out through four scanner APIs. These are GetModifiedWorkspaces, PostWorkspaceInfo, GetScanStatus and GetScanResult. They return details such as item names, sensitivity and endorsement status for external catalogs.
Governing Copilot and Data Agents on Fabric Data
AI assistants raise a fair question for governance teams. If Copilot can answer questions about company data, who decides what it can see?
The answer starts with the access you already set. Copilot and Fabric data agents work with the permissions of the signed-in user, so they only see data that person can already see. Weak workspace roles therefore become weak AI boundaries, which is one more reason to fix roles first.
Two more controls sit on top. Microsoft’s Copilot setup guide (August 2026) says Copilot runs on paid F2 or larger capacities and is on by default tenant-wide. Scope its tenant setting to a pilot security group before wider use.
On the Purview side, Purview governance for Fabric Copilots and agents adds risk discovery in prompts and responses. It also covers audit of AI interactions, plus retention and eDiscovery for AI-generated content. In October 2026, Microsoft still listed some of these agent controls as preview.
A sensible rollout starts with one pilot group whose workspaces hold only certified, labeled data. Widen access once the pilot shows Copilot answering from the right data. Our guide to Copilot in Microsoft Fabric covers enablement, capacity and cost in detail.
Kanerika Service
Microsoft Purview Implementation Services
Kanerika designs and rolls out Microsoft Purview for Fabric and the wider Microsoft estate, from assessment and architecture design to labels, DLP and audit.
Explore Purview ServicesHow to Set Up Fabric Data Governance in Six Steps
Order matters more than tooling when you set up governance. Each step below depends on the one before it, so each has an owner and a test that tells you it is done.
- Set tenant settings and delegation. The Fabric admin owns this step. It is done when every setting for export, sharing, workspace creation and Copilot is scoped to a named group.
- Design domains and name domain admins. The Fabric admin works with business leads here. It is done when every production workspace sits in a domain with a named business owner.
- Structure workspaces and assign roles to groups. Domain and workspace admins own this step. It is done when production workspaces hold only group assignments rather than individual Admins or Members.
- Endorse and describe what people should trust. Item owners own this step. It is done when the most used semantic models and reports are certified and also carry descriptions.
- Turn on labels, DLP and audit in Purview. The security and compliance team owns this step. It is done when a test item with sample sensitive data raises a policy tip.
- Monitor and review monthly. The governance lead owns this step. It is done when recommended actions are reviewed each month and the scorecard trend is reported.
Steps one to four use native Fabric only, so a team without Purview licenses can finish them first. Step five is where the Purview budget starts. Waiting until then saves rework, because labels on a messy estate only label the mess.
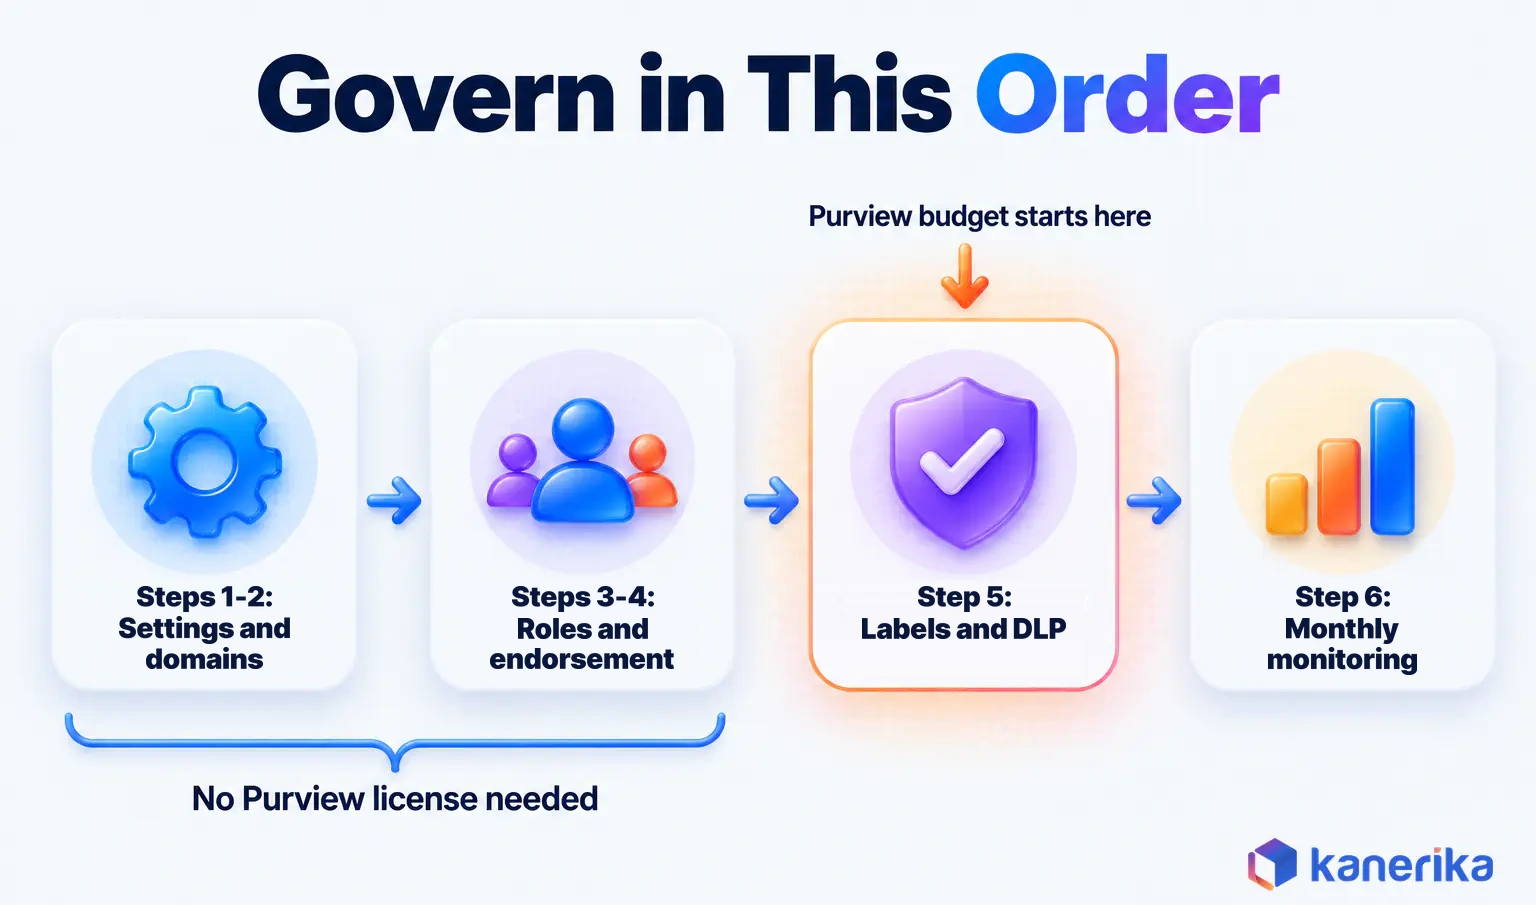
A small first scope works best. Pick one domain, such as Finance, run all six steps there and then copy the pattern to the next domain.
Testing Step Three With the Admin API
Step three has a test you can script, which beats opening workspaces one by one. The Get Groups As Admin call in the Power BI REST API lists every workspace in the tenant, with its users and their roles.
Only a Fabric administrator or a service principal can run it. Below, the script flags active workspaces with no Admin, plus those whose only Admins are individual people.
import os
import requests

# Fabric admin token: delegated Tenant.Read.All, or a service principal
token = os.environ["FABRIC_ADMIN_TOKEN"]
url = "https://api.powerbi.com/v1.0/myorg/admin/groups"
params = {"$top": 5000, "$expand": "users"}  # add $skip past 5,000 workspaces
headers = {"Authorization": f"Bearer {token}"}

resp = requests.get(url, params=params, headers=headers, timeout=60)
resp.raise_for_status()

for ws in resp.json()["value"]:
    if ws.get("type") != "Workspace" or ws.get("state") != "Active":
        continue  # skip personal and deleted workspaces
    admins = [u for u in ws.get("users", [])
              if u.get("groupUserAccessRight") == "Admin"]
    if not admins:
        print("NO ADMIN:", ws["name"], ws["id"])
    elif all(u.get("principalType") == "User" for u in admins):
        print("INDIVIDUAL ADMINS ONLY:", ws["name"], len(admins))
Microsoft’s own sample calls the first group orphaned workspaces, which is exactly what the auditor in the opening story found. Two limits shape the schedule. The call allows 50 requests per hour per tenant and times out after 30 seconds, so a weekly run fits well.
Microsoft also flags that the users field will leave this response in a future release. Its replacement route is Get Group Users As Admin, or PostWorkspaceInfo with getArtifactUsers.
Choosing a Governance Model: Centralized, Federated or Hybrid
A governance model decides who makes which call. The right one depends on how your estate is shaped, rather than on which model sounds most modern.
Centralized governance keeps decisions with one platform team, so it suits a small estate with one data team. Federated governance hands day-to-day decisions to domain owners inside central guardrails, which suits many business units with their own analysts. Hybrid governance centralizes regulated data but federates the rest. If you need the theory behind these models, our data governance framework guide explains it.
| Estate shape | Model | How it looks in Fabric |
|---|---|---|
| One data team, a few business units | Centralized | One team owns tenant settings, domains and certification |
| Many business units with their own analysts | Federated | Domain admins own workspaces and certify within central rules |
| Regulated core plus self-service teams | Hybrid | Central control for labeled finance or patient data, while other teams self-serve |
Timing is a separate choice from structure. Microsoft’s Fabric adoption roadmap, updated in January 2026, describes three rollout methods. The first rolls Fabric out and adds governance later, while the second plans governance in depth before any rollout. Iterative governance with rollouts sits between them, and Microsoft calls it the best choice for most organizations. Our guide to Microsoft Fabric adoption covers the wider rollout plan.
Iterative still means disciplined. Each new domain arrives with its owners, roles and labels already decided, so governance grows at the same pace as use.
Case Study
76% Faster Insights with One Governed Rule Set on Fabric
A global consumer electronics brand replaced region-by-region transformation rules and KPI definitions with one governed rule set on Microsoft Fabric, with 60% faster data processing and 42% lower infrastructure costs.
Read the Case Study →Mapping Fabric Controls to HIPAA, GDPR and SOX Evidence
Auditors want evidence that a control exists and works. So the useful question for each regulation is which Fabric or Purview control produces that evidence.
Take HIPAA as an example. The HIPAA Security Rule at 45 CFR 164.312(b) requires mechanisms that record and examine activity in systems holding electronic health data. In Fabric, Purview Audit records that activity, while labels mark which items hold patient data. Our data governance in healthcare guide covers the wider patient-data picture. Sarbanes-Oxley takes a different angle, since Section 404 asks management to assess internal control over financial reporting.
| Requirement | Fabric or Purview control | Evidence an auditor asks for |
|---|---|---|
| HIPAA audit controls | Purview Audit, plus labels on patient data items | Activity records for items holding patient data |
| HIPAA access to patient data | Group-based workspace roles, OneLake security | Role assignments per workspace and access review sign-offs |
| GDPR records of processing | Domains, OneLake catalog, descriptions, lineage | Inventory of items holding personal data, with owners |
| GDPR security of processing | Labels, DLP, OneLake security | DLP policy settings and alert history |
| SOX internal control over financial reporting | Certified semantic models, separate production workspaces | Named owners for financial models and logs of role changes |
A table like this works best as a living document. Keep it next to the scorecard, and update it whenever a new domain goes live.
How Much Time and Effort Fabric Governance Takes
Fabric governance is mostly people time rather than software time. Settings take minutes to change, but agreeing on owners and label rules takes meetings.
A four-week pilot on one domain is a realistic starting point for most teams. The plan below assumes one domain, a part-time governance lead and a Fabric admin. Treat it as a sample to adapt to your own estate.
| Week | Scope | Deliverable | Exit check |
|---|---|---|---|
| 1 | Tenant settings and inventory | Documented settings and a workspace list with owners | Every setting has a group and a reason |
| 2 | Domain and roles | Pilot domain with group-based roles | No individual Admin assignments in production |
| 3 | Endorsement and labels | Certified core models and a first label policy | Top models certified, then labels visible downstream |
| 4 | DLP and monitoring | One DLP policy and a monthly scorecard | Test policy tip fires, and the scorecard is reviewed |
Costs come from four places, and none of them has a fixed price you can copy from a blog.
- Purview licensing for labels, DLP and the wider Purview suite. Our Microsoft Purview licensing guide breaks down the plans.
- Label and DLP rollout effort, such as user training and tuning false positives.
- Steward time from domain owners who certify, describe and review access. Our data stewardship guide defines the role.
- Capacity consumption, since DLP evaluation and monitoring use capacity. See Microsoft Fabric pricing for how capacity is billed.
Checklist
Data Governance Checklist
Plan ownership, access, classification and monitoring before your pilot starts, with a checklist your platform and business teams can work through together.
Get the Checklist →Common Fabric Governance Mistakes and How to Fix Them
Most Fabric governance problems come from timing rather than missing features. Each mistake below comes with a fix you can test. For the wider list, see our data governance best practices guide.
- Governance after launch. Rules added after a year of use mean cleaning up hundreds of items. Run the six steps on each new domain before data lands instead.
- Over-permissioned pilots. Pilot workspaces often give everyone Admin and never change. A monthly check should confirm production has no individual Admin assignments.
- No domain design. Without domains, every workspace looks equal, so nobody owns a business area. Map each workspace to a domain with a named owner.
- Purview left too late. Labels added after sharing has spread miss the copies already exported. Label sensitive sources before any wide release.
- Workspace sprawl. Open workspace creation produces dozens of near-empty workspaces. Limit creation to a security group, then archive workspaces with no activity.
- Tenant-setting drift. Settings change quietly, and nobody remembers why. Keep a settings log, and review it during each quarterly access review.
Many of these problems also appear outside Fabric. Our article on data governance challenges covers the organizational side in more depth.
How to Measure Whether Fabric Governance Is Working
Governance that nobody measures tends to fade. A short scorecard keeps it visible, and most of the numbers already sit in Fabric.
The Govern section is the main source, because it tracks label coverage, endorsement coverage and recommended actions. The monitoring hub also shows activity for items each user can view, while the Capacity Metrics app shows usage across capacities. Pull the figures monthly and plot the trend, since direction matters more than any single month.
| Metric | How to compute it | Source |
|---|---|---|
| Owner coverage | Production workspaces in a domain with a named admin, divided by all production workspaces | Admin portal, Govern section |
| Endorsement coverage | Certified or promoted items divided by items in active use | Govern report, discovery tab |
| Label coverage | Labeled items divided by all items | Govern report, protection tab |
| Open recommended actions | Count of open actions, then tracked month over month | Govern section |
| Capacity headroom | Peak utilization compared to capacity size | Capacity Metrics app |
For a broader view of maturity levels, Microsoft’s adoption roadmap describes how governance matures over time. Our data governance maturity model guide sets out the levels in plain terms. Use either to set targets, and then let the scorecard show progress.
How Kanerika Implements Fabric Data Governance
Kanerika treats Fabric data governance as an operating model first and a configuration task second. The work runs in four stages, so each one ends with something the client can test.
- Assess. Inventory the tenant, workspaces, owners and current settings, then rank the gaps. The admin API check above makes a good first query, since ownerless workspaces decide what gets fixed first.
- Design. Agree on domains, ownership, role patterns and label rules with business leads before anything changes.
- Configure and test. Apply settings, roles, endorsement and Purview policies. Then prove each one with a test case, such as a sample sensitive file that must raise a DLP policy tip.
- Monitor and extend. Set up the scorecard, then roll the pattern out domain by domain.
Our data governance consulting services combine three offerings. KANGovern handles catalog, lineage and glossary work, while KANGuard covers DLP, classification and labeling. KANComply supports regulatory compliance, and all three are powered in part by Microsoft Purview. On the platform side, we also deliver Microsoft Fabric consulting and Microsoft Purview implementation.
Case Study: An Independent Fabric Review Before an ERP Go-Live
Forest River was moving from Dynamics AX to Dynamics 365 Finance and Operations, with Microsoft Fabric on the critical path. A third-party integrator had built the Fabric solution, and leadership wanted an independent view before go-live. Our webinar on Microsoft Fabric for Dynamics 365 looks at this combination in more detail.
Kanerika ran a six-week, read-only review of the Fabric workspace, a 124-table Dataverse mirror, pipelines, notebooks and security settings. No production or non-production system changed. The team scored the platform across five lenses and 18 dimensions, then logged about 136 findings with owners, effort and sequence.
That evidence supported a conditional go-live decision, with pre-cutover actions scoped at an estimated 30 days and about three person-weeks of internal effort. The Fabric architecture review also defined security and governance target states for growth. Putting an owner on every finding is the same principle that domains and named workspace admins enforce in Fabric.
Case Study: One Governed Rule Set Across Regions
A global consumer electronics brand sold across several international markets, but each region transformed data with its own rules and KPI definitions. Reports disagreed, so leaders spent meetings arguing about whose number was right.
Kanerika moved the high-volume data flows from Informatica to Fabric using its FLIP migration accelerator. Its team also set one governed rule set for data structure and KPIs across every region. The Informatica to Fabric migration delivered 60% faster data processing, 42% lower infrastructure costs and 76% faster time to insights.
The governance lesson is about shared definitions and clear ownership. Those two foundations are exactly what domains and certification formalize in Fabric.
Kanerika Service
Data Governance Consulting Services
Kanerika combines KANGovern, KANGuard and KANComply, powered in part by Microsoft Purview, to catalog, protect and prove compliance across your data estate, Fabric included.
Explore Governance ServicesBottom Line: What Fabric Covers, What Needs Purview and Where to Start
Fabric covers ownership, structure, access and discovery on its own, so a Fabric-only team can govern well with those tools. Purview is needed once you must classify sensitive data, enforce DLP or hand auditors activity evidence.
Start with tenant settings and domains, finish the native steps and then add Purview for protection. Run that pattern on one domain first, and Fabric data governance grows with use while Purview spend stays tied to sensitive data.
Frequently Asked Questions
What is Microsoft Fabric governance?
Microsoft Fabric governance is the set of rules, roles and tools that control who owns, finds and uses data in Fabric. It spans tenant settings, domains, workspaces and individual items. Native features handle structure, access and discovery, while Microsoft Purview adds sensitivity labels, data loss prevention and audit search for regulated or sensitive data across the estate.
How does Microsoft Purview integrate with Microsoft Fabric?
Purview connects to Fabric without extra plumbing. Sensitivity labels from Purview Information Protection apply directly to Fabric items and flow downstream to dependent items. Purview DLP policies check supported items such as lakehouses and semantic models. Purview Audit records Fabric activity, and Insider Risk Management includes ready-made Fabric indicators. Labels and DLP both need additional Purview licensing.
How do you govern Copilot and data agents in Microsoft Fabric?
Start with access, because Copilot and data agents only see data the signed-in user can already see. Copilot is on by default for the whole tenant on paid F2 or larger capacities, so scope its setting to a pilot security group first. Purview then adds prompt risk discovery, audit of AI interactions, and retention and eDiscovery for AI content.
Who should own Fabric governance in an enterprise?
Ownership is shared across layers. A central platform team with the Fabric admin owns tenant settings and domain design. Domain admins, ideally business owners, own their workspaces and certification. Workspace admins manage roles, and item owners keep descriptions and endorsement current. A governance lead tracks the scorecard, and security teams run Purview labels and DLP.
How long does it take to set up Fabric data governance?
A focused pilot on one domain can run in about four weeks, covering tenant settings, roles, endorsement, a first label policy and one DLP policy. A large estate takes longer, because agreeing on owners and label rules needs business time. Microsoft recommends iterative rollouts, adding governance one domain at a time as Fabric use grows.
How does lineage work in Microsoft Fabric?
The lineage view shows how data moves from sources through lakehouses, pipelines and semantic models to reports inside a workspace. For downstream items in other workspaces, open impact analysis, which lists everything a change would affect. Check impact analysis before editing a shared semantic model, so report owners hear about the change before their numbers move.
What are the best practices for Microsoft Fabric governance?
Set up governance before data lands, and do it in a fixed order. Scope tenant settings to groups, design domains with business owners, assign workspace roles to groups and certify core models. Then add Purview labels and DLP for sensitive data. Track owner, endorsement and label coverage every month, and repeat the pattern one domain at a time.
What roles are available in Microsoft Fabric workspaces?
Fabric workspaces have four roles. Admin can update or delete the workspace and manage all access. Member can add people with lower permissions and share content. Contributor can create and edit items. Viewer can only view content. Assign roles to Microsoft Entra security groups rather than individuals, so access changes automatically when people move or leave.
How do DLP policies work in Microsoft Fabric?
Purview DLP policies detect sensitive information in supported Fabric items, including semantic models, lakehouses, warehouses, KQL databases and mirrored databases. Semantic models are checked on publish and refresh, while other items are checked when their data changes. A match can raise a policy tip and an alert. The restrict access action is in preview, and DLP requires Purview licensing.
What is endorsement in Microsoft Fabric?
Endorsement marks Fabric items that people can trust. Anyone with write access can promote an item, and reviewers named by the Fabric admin certify items that pass quality checks. A third badge, Master data, identifies the authoritative source for data such as customer lists. Certification works best when a named group owns the standard and reviews certified items regularly.
Do I need Microsoft Purview to govern Microsoft Fabric?
Not for the basics. Fabric natively covers tenant settings, domains, workspace roles, OneLake security, endorsement, lineage and the Govern section. You need Purview for sensitivity labels, data loss prevention, Insider Risk Management and AI interaction controls. Labels and DLP require additional Purview licensing, and labeling Power BI items also needs a Pro or Premium Per User license.
What is the difference between the OneLake catalog and Microsoft Purview?
The OneLake catalog is the built-in Fabric hub for finding, governing and securing Fabric items, through its Explore, Govern and Secure experiences. Microsoft Purview is a wider governance and compliance suite that covers Fabric plus the rest of the Microsoft estate. Use the OneLake catalog for Fabric discovery and health, and Purview for classification and protection.
What are domains in Microsoft Fabric?
Domains group Fabric workspaces by business area, such as Finance or Sales, and subdomains refine that grouping. A Fabric admin creates them and names domain admins, ideally business owners, who manage descriptions and attach workspaces. Some tenant settings can be delegated to domains, so each business area can apply stricter rules where its own data needs them.
How do you prevent workspace sprawl in Microsoft Fabric?
Limit workspace creation to a named security group through tenant settings, and require every new workspace to sit in a domain with a named owner. Separate development, test and production workspaces. Review activity monthly and archive workspaces nobody uses. The Govern section inventory insights and recommended actions help you spot empty or ownerless workspaces early.
Can OneLake security replace row-level security in Power BI?
Not on its own. OneLake security defines deny-by-default roles on items such as lakehouses, and a role can include row-level and column-level security. ReadWrite roles cannot carry those rules, and workspace roles stay the first access boundary. Treat OneLake security as one layer in your access design, and test it with real user accounts first.