TL;DR
The best AI governance tools for 2026 depend on your stack, so Microsoft shops should start with Purview. Databricks shops should start with Unity Catalog. Policy-led teams should add Credo AI or OneTrust, and insurers should try Monitaur first. Pick a tool that lists your AI, records each approval and keeps proof of how it behaves. Few tools do every job well, so pair what you own with one specialist. Then test two or three tools on your own agents before you sign.
Key Takeaways
- AI governance tools record which AI systems exist, who approved them, how they were tested and what they do in production.
- The market splits into five categories: policy and GRC specialists, model lifecycle platforms, data security for AI, runtime guardrails and platform-native controls.
- Extend what you already own, such as Microsoft Purview or Databricks Unity Catalog, then add a specialist only where a real gap remains.
- AI agents need identity, tool permissions and runtime enforcement, so check agent coverage on every vendor’s own pages.
- EU AI Act high-risk obligations now apply from December 2, 2027 for Annex III systems and August 2, 2028 for systems inside regulated products.
- A proof of concept on your own agents, with pass conditions written in advance, is the only fair way to compare vendors.
The Audit Request That Arrives After Launch
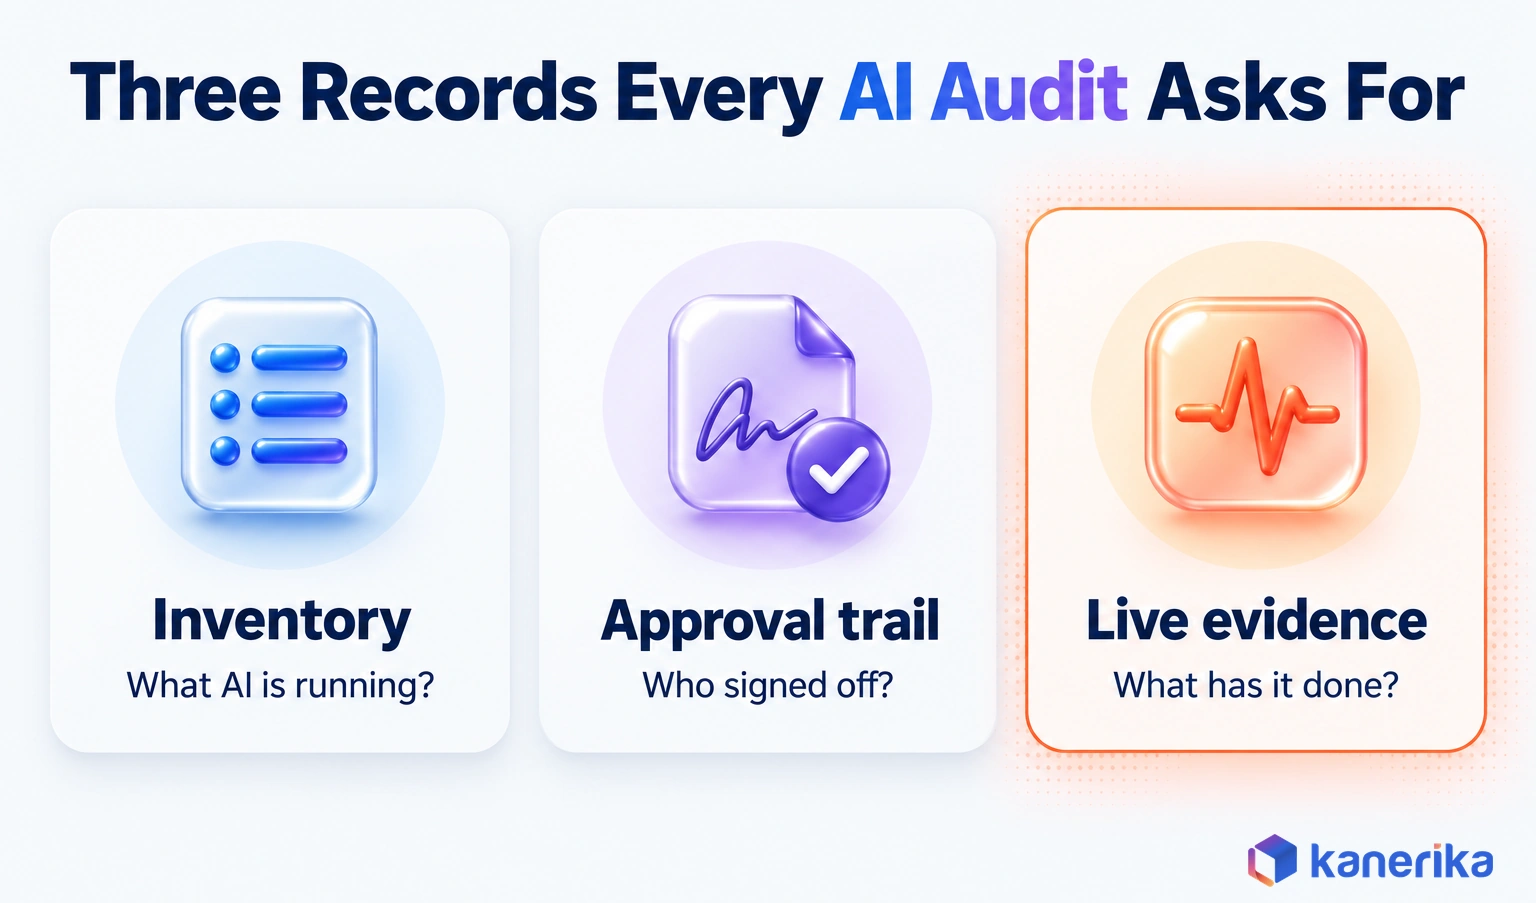
Picture a Monday morning six weeks after your customer-service agent went live. An internal auditor sends three short questions. Which AI systems are running in production? Who approved this agent, and on what evidence? What has it done since launch?
Your engineering team can answer the third question from logs, although it takes some digging. The first two, by contrast, take a week of email, spreadsheets and screenshots from people who have since changed teams.
That lost week is exactly the problem AI governance tools exist to remove.
The Three Records Every AI Governance Tool Must Produce
Every AI governance tool is judged on three records: an inventory, an approval trail and evidence of how each system behaves. The first two describe a system at the moment someone signed it off. The third, live evidence, is where spreadsheets fail.
Each record has an owner and a format. An inventory lists every model, agent and AI-enabled vendor product, along with an accountable person and a risk tier. Approval trails show who reviewed the use case, which tests ran and what conditions came with the sign-off.
Evidence is the hardest part, because it keeps changing after launch. Monitoring results, incidents, prompt changes and retraining runs all belong in it. A spreadsheet can hold the first two records for a while, but it cannot collect live evidence from a running agent.
Here is what one exported record might look like, with all three parts in one place. The field names are illustrative, since each tool uses its own schema.
# One AI system record, exported for an auditor (illustrative schema)
system: customer-service-agent
type: agent
owner: head-of-customer-operations
risk_tier: high              # result of the EU AI Act screening
data_access:
  - crm.customers: read
  - orders.refunds: write    # capped, see approval conditions
approval:
  approved_by: [risk-committee, legal, data-governance]
  approved_on: 2026-09-14
  conditions:
    - human review for refunds above the cap
  tests: [bias-eval-v3, prompt-injection-suite-v2]
evidence:
  monitoring: drift and policy alerts, daily
  incidents_open: 0
  last_review: 2026-10-27
So the test for any tool in this guide is simple. Can it produce those three records for your systems on demand, without a week of manual work? The rest of this article compares 14 platforms against that test.
What Are AI Governance Tools (and What They Are Not)
AI governance tools are software that inventories AI systems, routes them through risk review and approval, and stores proof that each control ran. In other words, they turn an AI policy into a repeatable workflow with an audit trail. A separate guide explains how AI policy management software keeps versions, approvals and exceptions together.
They are not model-building tools, though. An AI governance tool does not train, tune or host your models, and it rarely replaces your MLOps stack. Instead, it sits beside that stack, pulls metadata and test results from it, and then adds policy, approval and evidence on top.
That distinction matters, because many products now use the word governance in their marketing. A monitoring tool with a policy tab is useful, yet it may not run intake or keep a register. If you want the wider program view first, Kanerika’s guide to what AI governance is covers the operating model behind the software.
Six Capabilities Every AI Governance Tool Should Cover
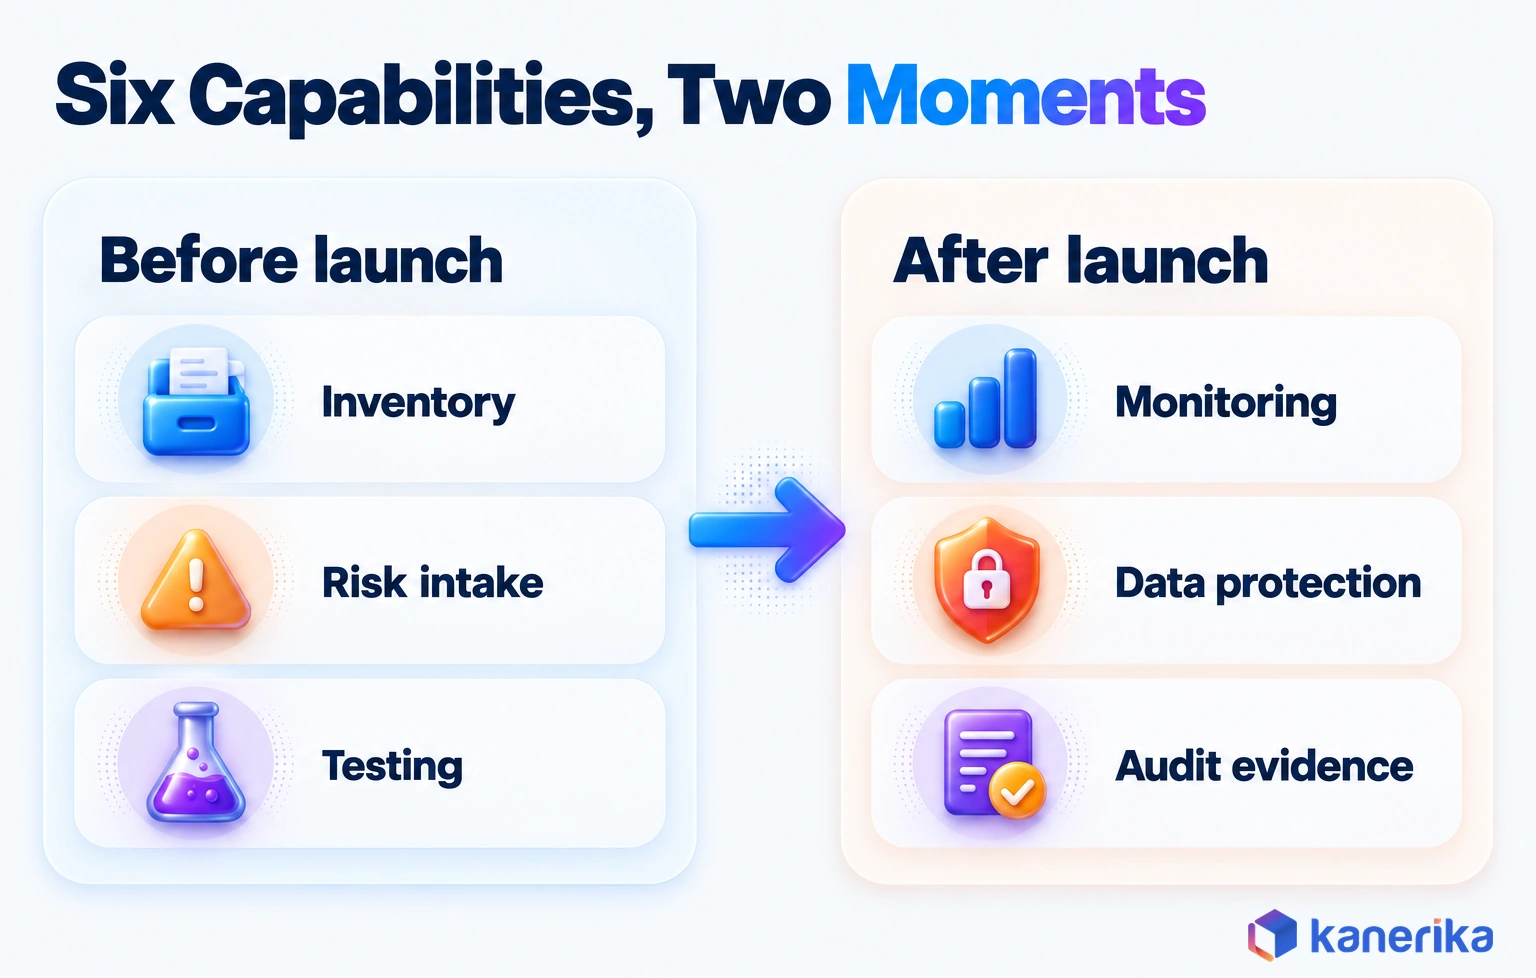
Before comparing vendors, it helps to agree on what “covered” means. These six capabilities map to the questions auditors ask, and each one also produces a specific piece of evidence.
- AI inventory. A register of every model, agent and AI-enabled vendor product, with an owner and a risk tier. For example, a marketing team’s new copy generator appears in the register before it reaches customers.
- Intake and risk workflow. A form and review path that classifies each use case and then routes it to the right approvers. For example, a hiring screening model is flagged as high risk and sent to legal and HR.
- Testing and evaluation. Bias, accuracy, robustness and safety checks run before approval and stored with the record. For example, a credit model’s fairness results attach to its approval ticket.
- Runtime monitoring and guardrails. Drift, quality and policy checks on live traffic, with blocks or alerts when a limit is crossed. For example, an agent cannot call a payments tool until a person signs off.
- Data protection for AI. Controls on what sensitive data reaches prompts, training sets and agent tools. For example, customer account numbers are masked before they reach a chatbot.
- Audit evidence. Exportable reports that tie each system to its approvals, tests and incidents. For example, a quarterly pack for the risk committee is generated in minutes rather than assembled by hand.
A tool does not need to excel at all six to earn a place on your shortlist. Still, it should be honest about which ones it covers and which ones it hands to another product.
AI Governance Tools vs Data Governance Tools vs AI Observability Tools
Three adjacent categories often get mixed up in buying conversations. The quickest way to separate them is to ask what each one governs and what evidence it produces.
| Category | What it governs | Typical evidence |
|---|---|---|
| AI governance tools | AI systems as a whole, such as use cases, models, agents and approvals | Register, risk assessments, approvals and policy checks |
| Data governance tools | Data assets, such as catalog, lineage, quality and access | Lineage graphs, quality scores and access reviews |
| AI observability tools | Model and agent behavior at runtime, such as traces and drift | Traces, eval results and alerts when behavior changes |
Data catalogs feed AI governance, but they do not approve AI use cases, as Kanerika’s roundup of data governance tools explains. AI observability tools supply the runtime signals that a governance platform then turns into evidence. AIOps tools do a different job again, since they watch IT operations rather than AI behavior.
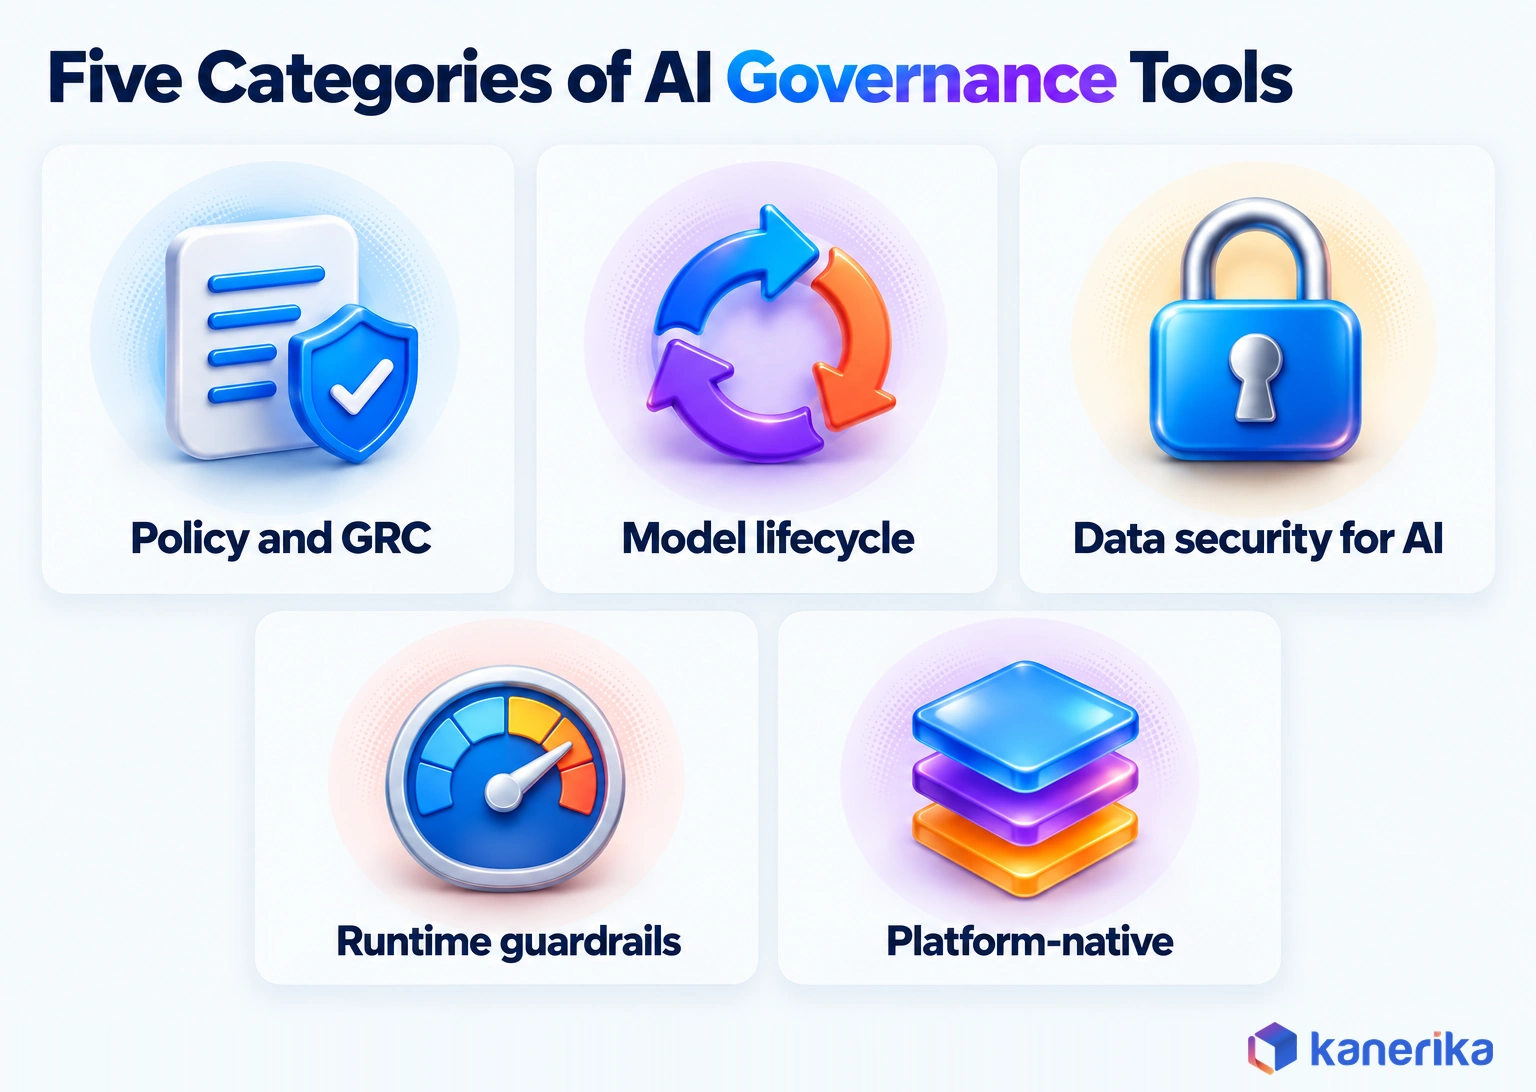
The Five Categories of AI Governance Tools
Vendors in this market start from very different places, and that starting point shapes what they do well. A privacy platform and a model monitoring company can both sell “AI governance,” yet they solve different halves of the problem.
Sorting a long list into five categories makes the comparison fair. It also shows where gaps will appear when you buy only one product.
| Category | What it governs | Example tools | Gap it usually leaves |
|---|---|---|---|
| Policy and GRC specialists | Use-case intake, risk assessment, policy mapping and approvals | Credo AI, OneTrust, Holistic AI | Deep monitoring once models run in production |
| Model lifecycle and risk | Model inventory, validation, lifecycle stages and model risk | IBM watsonx.governance, ModelOp, Monitaur, Dataiku Govern | Sensitive data exposure, such as prompts and agent tools |
| Data security for AI | Sensitive data reaching AI apps, copilots and agents | Microsoft Purview, Securiti | Use-case approvals and model validation |
| Runtime monitoring and agent guardrails | Live model and agent behavior, guardrails and alerts | Fiddler AI, Arthur | Policy workflow before launch |
| Platform-native controls | Access, lineage and runtime policy inside one platform | Unity Catalog and Unity Gateway, Purview, ServiceNow AI Control Tower, Collibra | AI that runs outside that platform |
Many real programs combine two categories. For instance, a Microsoft-heavy bank might pair Purview for data protection with a policy specialist for intake. Kanerika’s explainer on AI TRiSM describes the same split between trust, risk and security controls.
Where Shadow AI Detection Fits
Shadow AI is any AI tool or model used without approval, such as a team pasting contract text into a public chatbot. You cannot govern what is missing from the register, so discovery comes first.
Three categories see this activity from different angles. Data security tools such as Purview DSPM watch what sensitive data flows into AI apps. Policy platforms such as Holistic AI and OneTrust also add discovery to their inventory, while Securiti tracks sensitive data across the systems AI reads from.
No single view catches everything. Network and browser signals find public chatbot use, whereas platform logs find unregistered models inside your own cloud.
How We Selected These 14 Platforms
A tool made this list only if it governs AI systems, not just the data underneath them. In October 2026 we checked each vendor’s public product pages and documentation against six criteria.
- Governs AI systems. Inventory, risk or policy controls for models and use cases, rather than datasets alone.
- Agent coverage. Some way to register, monitor or restrict AI agents, as stated on the vendor’s own pages.
- Regulatory content. Workflows or mappings that help with the EU AI Act, NIST AI RMF or ISO/IEC 42001.
- Evidence export. Reports or records that an auditor could actually use.
- Enterprise deployment. Built for large organizations with many teams and systems.
- Public documentation. Enough published detail to verify claims before any sales call.
When a vendor’s site did not state a capability, we left it out rather than guess. One disclosure: Kanerika is a Microsoft and Databricks partner, and two of the 14 entries are Microsoft Purview and Databricks Unity Catalog.
The 14 Best AI Governance Tools for 2026
Each entry covers who it fits, what it governs, where it is strongest and what to check before you buy. The order follows the categories above, so it is not a ranking.
1. Credo AI
Best for: policy-led governance teams that need an agent registry.
Credo AI is a governance platform built around policy. Its product set includes an AI Agent Registry, agent governance workflows, Policy Packs and a library of risks and controls. Teams use those packs to turn a regulation or internal standard into checks.
Policy-to-control mapping is the reason to shortlist it. A risk team can register a new agent, apply the relevant pack and see which controls are still open. As a result, legal and compliance staff get a working view without reading model code.
Check evidence collection before you buy, because a policy layer is only as current as the results it receives. Ask how Credo AI pulls evidence from your ML platform and observability stack, and what stays manual.
Talk to Kanerika
Narrowing 14 AI Governance Tools to Three?
Kanerika maps your models, agents and data exposure, then shortlists the two or three governance platforms that fit the estate you already run.
Talk to an Expert →2. IBM watsonx.governance
Best for: enterprises that run formal model risk management across many models.
IBM watsonx.governance covers lifecycle governance, risk management and compliance for AI models. It tracks each model from request through validation and deployment, so every stage leaves a record.
IBM says it used watsonx.governance to approve more than 1,000 models for reuse, so the workflow has been run at portfolio scale. That history especially suits banks and insurers with a model risk function already in place.
Ask how it handles AI agents and their tool access, since we did not find agent coverage stated on the product page. Confirm it in a demo with one of your own agents.
3. OneTrust AI Governance
Best for: privacy-led programs that already run OneTrust for data protection.
OneTrust AI Governance handles discovery, inventory, monitoring and policy evaluation across models, data, agents and vendors. It also adds automated intake and risk scoring, so new use cases arrive with a first risk view attached.
If many of your AI risks arrive inside third-party products, its vendor coverage matters most. OneTrust treats AI vendors as part of the same inventory as internal models. Privacy teams that already assess vendors there can extend a familiar workflow.
Depth on model testing is the thing to probe. A privacy-first platform may rely on other tools for bias and performance evaluation, so map which tests it runs itself.
4. Microsoft Purview
Best for: Microsoft 365 and Azure estates where Copilot and agents touch sensitive data.
Microsoft positions Data Security Posture Management (DSPM) as the front door to discover, secure and apply compliance controls for AI usage. By October 2026, Microsoft labeled the older DSPM for AI as classic, and the new DSPM covers AI apps and agents. It shows which AI apps people use, what sensitive data flows into them and which policies apply.
Purview also manages data security and compliance for Microsoft Agent 365. For a Microsoft-heavy enterprise, agent data controls sit beside labels, data loss prevention and retention. That is why Kanerika’s Microsoft Purview services team often starts AI governance work here.
Microsoft Learn spells out the detail. Endpoint data loss prevention can warn or block a user who pastes a credit card number into ChatGPT. Prompts and responses land in the unified audit log, and Compliance Manager adds assessment templates for AI regulations. The same controls reach Copilot in Fabric, which Kanerika’s guide to Microsoft Fabric governance explores.
Scope is the limit to plan around. Purview governs data security and compliance for AI well, but it is not a use-case intake or model validation tool. Pair it with a policy layer if you need approvals and model risk records.
Kanerika Service
Microsoft Purview Services
Kanerika configures Purview DSPM, sensitivity labels and data loss prevention so Copilot and agents only reach the data they are allowed to see.
Explore Purview Services5. Holistic AI
Best for: enterprises that need one inventory across models, agents and applications, including shadow AI.
Holistic AI brings models, agents and applications into one platform. Its approach runs in three layers called Identify, Protect and Enforce. Identify finds AI in use, including shadow AI, while the other two layers apply controls and policy.
Programs often stall because nobody knows what AI is running, and Holistic AI is designed to answer that question first. It especially suits organizations where business units adopted AI faster than the central team could track.
Test how discovery works in your own environment. Ask which sources it scans and how it treats AI features inside approved SaaS tools.
6. ServiceNow AI Control Tower
Best for: enterprises that already run IT, risk and service workflows on ServiceNow.
ServiceNow positions AI Control Tower as a central hub for governing AI. It keeps an inventory of AI systems, models, prompts, datasets and MCP servers. Each record also carries the provider, lifecycle phase and risk classification.
If your risk committee already lives in ServiceNow, this is the natural place to start. Approvals, incidents and change requests already run through it in many companies. Governing AI there means a new agent follows the same ticketed path as any other production change.
Before you sign, ask how it collects test and monitoring evidence from your data science tools, since that data lives outside ServiceNow.
7. ModelOp
Best for: teams that want one system of record for ML, generative AI and agents.
ModelOp calls its product an Enterprise AI Command Center. It acts as a system of record across traditional ML, generative AI and agentic AI. Each asset is tracked through its lifecycle with controls attached.
A bank might run decades-old scoring models next to new agents, and ModelOp aims to govern both in one register. This also means nobody keeps separate inventories for “old” and “new” AI.
Check how much configuration the workflows need before you commit. A system of record only helps once each team’s process is modeled in it, so plan for that setup work.
8. Monitaur
Best for: insurers and other regulated firms that answer to examiners.
Monitaur builds model governance for insurers and other regulated industries. Its design centers on documenting models, decisions and controls in a form that regulators and auditors can review.
Insurers face scrutiny of pricing, underwriting and claims models, so a tool shaped around that work needs less tailoring. Model owners can show reviewers how a model was built and validated. When examiners ask why a model made one decision, pair the record with explainable AI techniques.
If most of your AI is copilots and agents rather than scored decisions, test its workflows on one of those before you sign.
9. Collibra AI Governance
Best for: organizations that want AI governance tied directly to governed data.
Collibra AI Governance includes an AI Command Center, described as a unified control plane for agents, models and use cases. Collibra also uses guardian agents to help enforce policy across those assets.
Because it began as a data catalog, Collibra lets a use case point to its datasets and their quality and access rules. That data lineage view helps when an auditor asks what data trained or grounds a model.
Runtime depth is the thing to confirm. Ask what live monitoring Collibra performs itself and what it imports from observability tools.
Datasheet
Elevate Data Governance, Compliance and Security
A datasheet on how Kanerika sets up governed, classified and access-controlled data, the foundation every AI governance tool depends on.
Get the Datasheet →10. Securiti, Now Part of Veeam
Best for: security and privacy teams focused on sensitive data reaching AI.
Securiti states on its site, as of October 2026, that it is part of Veeam. It focuses on sensitive data across the systems AI reads from and writes to. Its Agent Commander product also extends those controls to AI agents and what they can access.
Its data-first view matters because many AI incidents start with data that should never have reached a prompt. Securiti maps that exposure across clouds and SaaS, a practice known as data security posture management. A security team can decide which AI uses need tighter limits.
Before you sign, ask about the roadmap, licensing and how the product will fit with the rest of the Veeam portfolio after the acquisition.
11. Fiddler AI
Best for: ML and platform teams that want governance grounded in runtime behavior.
Fiddler AI started in model monitoring and has since added agentic observability. It also includes policy enforcement guardrails and an AI GRC module, so monitoring signals can feed governance records.
When an agent drifts or breaks a rule, the event is visible and can block or flag the action. That ties live behavior directly to policy, and teams that already use Fiddler for monitoring can add governance without a second data pipeline.
Before you sign, check whether the GRC module covers intake, approvals and committee reporting at the depth your risk team expects.
12. Arthur
Best for: teams that need to find and control agents running across the business.
Arthur provides agent discovery, runtime guardrails, anomaly alerting, and audit and compliance support. That mix suits organizations where agents spread faster than central teams can register them.
Arthur can find agents, watch their behavior and alert when something unusual happens, while keeping records that support audit work. For the signals worth tracking, see Kanerika’s guide to AI agent observability.
Like other runtime-first tools, however, it leaves a question about pre-launch work. Ask how it handles risk review and approvals, or whether those stay in another system.
13. Dataiku Govern
Best for: data science teams that build and run most of their AI inside Dataiku.
Dataiku Govern keeps a unified inventory of datasets, analytics projects, models and agents, each with an owner. Because it sits inside the platform where work happens, the inventory updates as projects move forward.
Data scientists do not have to copy details into a separate tool, so the register stays current. Approval steps can also sit at the points where projects move to production.
If many models and agents live outside Dataiku, plan how they will reach the same register before rollout.
14. Databricks Unity Catalog and Unity Gateway
Best for: Databricks-centric estates that want runtime controls close to data and models.
Databricks describes Unity Catalog as the unified governance layer for data and AI, and it tracks lineage as those assets are used. Unity Gateway, as the October 8, 2026 documentation names it, extends that control to runtime. It governs interactions between models, agents, MCP servers and tools, with guardrails set through service policies and usage monitoring.
Once an agent’s calls pass through the gateway, policy applies at the point of use and usage is logged. Platform teams get real enforcement at runtime, with every call on record.
The approval record can also live on the model itself. This sketch follows the Databricks guide to models in Unity Catalog, where model access is granted on the FUNCTION securable. The catalog, model and group names are placeholders.
import mlflow
from mlflow import MlflowClient

mlflow.set_registry_uri("databricks-uc")
client = MlflowClient()
name = "prod.risk.credit_model"

# Register the validated run as a governed model in Unity Catalog
mv = mlflow.register_model("runs:/<run_id>/model", name)

# Tie the version to its approval ticket, then mark it as the live version
client.set_model_version_tag(name, mv.version, "approval_ticket", "RISK-1042")
client.set_registered_model_alias(name, "Champion", mv.version)

# Only the serving team may load the approved model
spark.sql("GRANT USE CATALOG ON CATALOG prod TO `model-serving`")
spark.sql("GRANT USE SCHEMA ON SCHEMA prod.risk TO `model-serving`")
spark.sql("GRANT EXECUTE ON FUNCTION prod.risk.credit_model TO `model-serving`")
The tag ties a version to its approval, the alias marks which version is live, and the grant limits who can load it. For the data side of the setup, see how enterprises are using Databricks Unity Catalog.
Before you sign, map everything that sits outside Databricks. Use cases, vendor AI and agents outside the platform still need another home, often a policy specialist.
AI Assessment
How Ready Is Your Organization to Govern AI?
Score your data, processes, skills and governance in a few minutes, and see where your AI program needs controls before you buy a platform.
Start Your AI Assessment →AI Governance Tools Comparison Table
The table below puts all 14 platforms side by side. Use it to narrow a long list to three or four names, and test those names properly.
The agent column reflects only what each vendor states on its public pages as of October 29, 2026. “Check” means we did not find agent coverage stated, so confirm it in a demo.
| Tool | Category | Gap to plan for | Covers agents |
|---|---|---|---|
| Credo AI | Policy and GRC | Evidence collection from ML and observability tools | Yes |
| IBM watsonx.governance | Model lifecycle and risk | Agent coverage not stated | Check |
| OneTrust AI Governance | Policy and GRC | Depth of model testing | Yes |
| Microsoft Purview | Data security for AI | No use-case intake or model validation | Yes |
| Holistic AI | Policy and GRC | Discovery reach in your environment | Yes |
| ServiceNow AI Control Tower | Platform-native | Evidence from data science tools | Partial |
| ModelOp | Model lifecycle and risk | Workflow configuration effort | Yes |
| Monitaur | Model lifecycle and risk | Copilot and agent coverage | Check |
| Collibra AI Governance | Platform-native | Runtime monitoring depth | Yes |
| Securiti (Veeam) | Data security for AI | Roadmap after the acquisition | Yes |
| Fiddler AI | Runtime monitoring | Intake and approval depth | Yes |
| Arthur | Runtime monitoring | Pre-launch review and approvals | Yes |
| Dataiku Govern | Model lifecycle and risk | AI built outside Dataiku | Yes |
| Databricks Unity Catalog and Unity Gateway | Platform-native | AI outside Databricks | Yes |
Read the table by category first. Two tools from the same category rarely belong on one shortlist, whereas tools from different categories often work well together.
What the EU AI Act, NIST AI RMF and ISO/IEC 42001 Ask of Your Tools
Regulation is the main reason AI governance moved from a nice idea to a budget line. Three frameworks shape what auditors ask for, and each one expects evidence that a tool can produce.
Behind all three sit shared principles. The OECD AI Principles, adopted in 2019 and updated in May 2024, name accountability as a core value, as most responsible AI programs do. Kanerika’s overview of AI compliance covers the obligations in detail, so this section stays on what your tools must produce.
EU AI Act Dates After the AI Omnibus
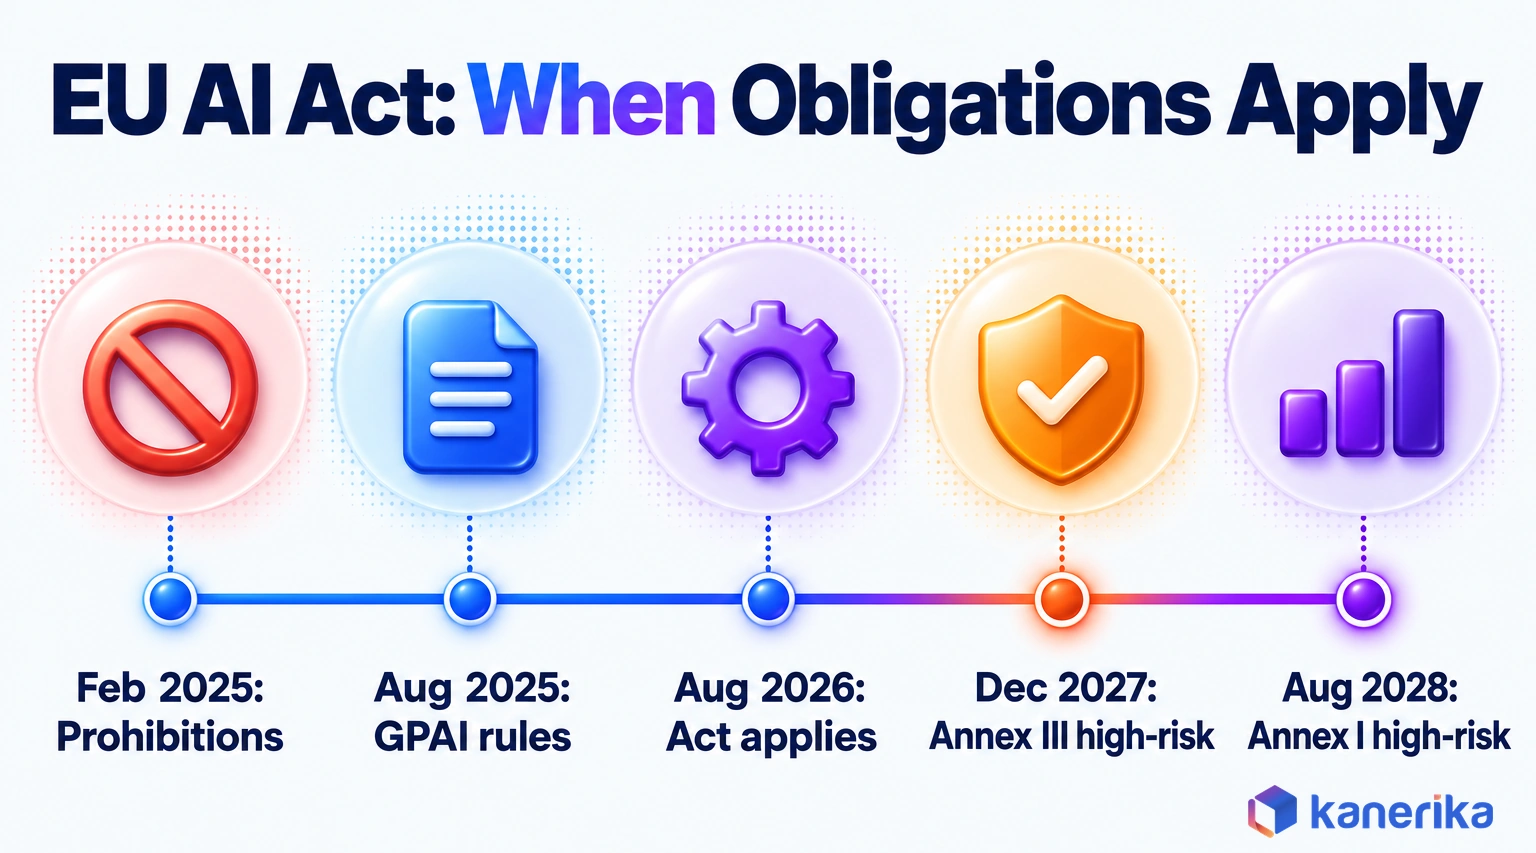
The EU AI Act entered into force on August 1, 2024 and began to apply in stages. Prohibited practices and AI literacy duties started on February 2, 2025. Rules for general-purpose AI models and the governance structure followed on August 2, 2025.
The Act becomes applicable on August 2, 2026, when the AI Office and national authorities start enforcement and transparency rules apply. The AI Omnibus also moved the high-risk dates. It was proposed on November 19, 2025, agreed politically on May 7, 2026 and entered into force on July 27, 2026.
Under the revised timeline, high-risk systems in Annex III areas such as biometrics, critical infrastructure, education, employment and migration face obligations from December 2, 2027. High-risk systems built into regulated products under Annex I follow on August 2, 2028. That gives most enterprises a planning window, but inventory and risk classification take time to build.
NIST AI RMF and ISO/IEC 42001
In the United States, the NIST AI Risk Management Framework is the common reference. NIST released AI RMF 1.0 on January 26, 2023, and added the Generative AI Profile, NIST AI 600-1, on July 26, 2024. Although it is voluntary, many risk teams use its Govern, Map, Measure and Manage functions as their control structure. The NIST AI RMF Playbook lists suggested actions for each function, which makes a handy checklist when you test a vendor’s framework mapping.
ISO/IEC 42001:2023 is the management system standard for AI. Organizations that want a certifiable program use it to show that policies, roles and reviews run on a cycle.
What Each Framework Needs as Evidence
All three frameworks ask for similar proof, even though they phrase it differently. The table maps each request to the tool capability that produces it. How the NIST Playbook’s suggested actions turn into evidence is covered in NIST AI RMF Playbook.
| What the framework asks for | Tool capability that produces the evidence |
|---|---|
| Know which AI systems you run and their risk level | AI inventory and risk classification |
| Assess risk before deployment | Intake workflow and risk assessment templates |
| Test for accuracy, bias and robustness | Evaluation runs stored with the system record |
| Monitor systems after launch | Runtime monitoring, drift alerts and incident logs |
| Keep technical documentation and logs | Evidence export and audit reports |
| Assign roles and review on a cycle | Ownership fields, approval routing and review reminders |
For a clause-by-clause view of how these frameworks map to controls, see Kanerika’s guide to building an AI governance framework. The point for tool buyers is narrower. Every row in that table needs a system of record, and spreadsheets break at the monitoring row.
How AI Governance Tools Work: From Registration to Retirement
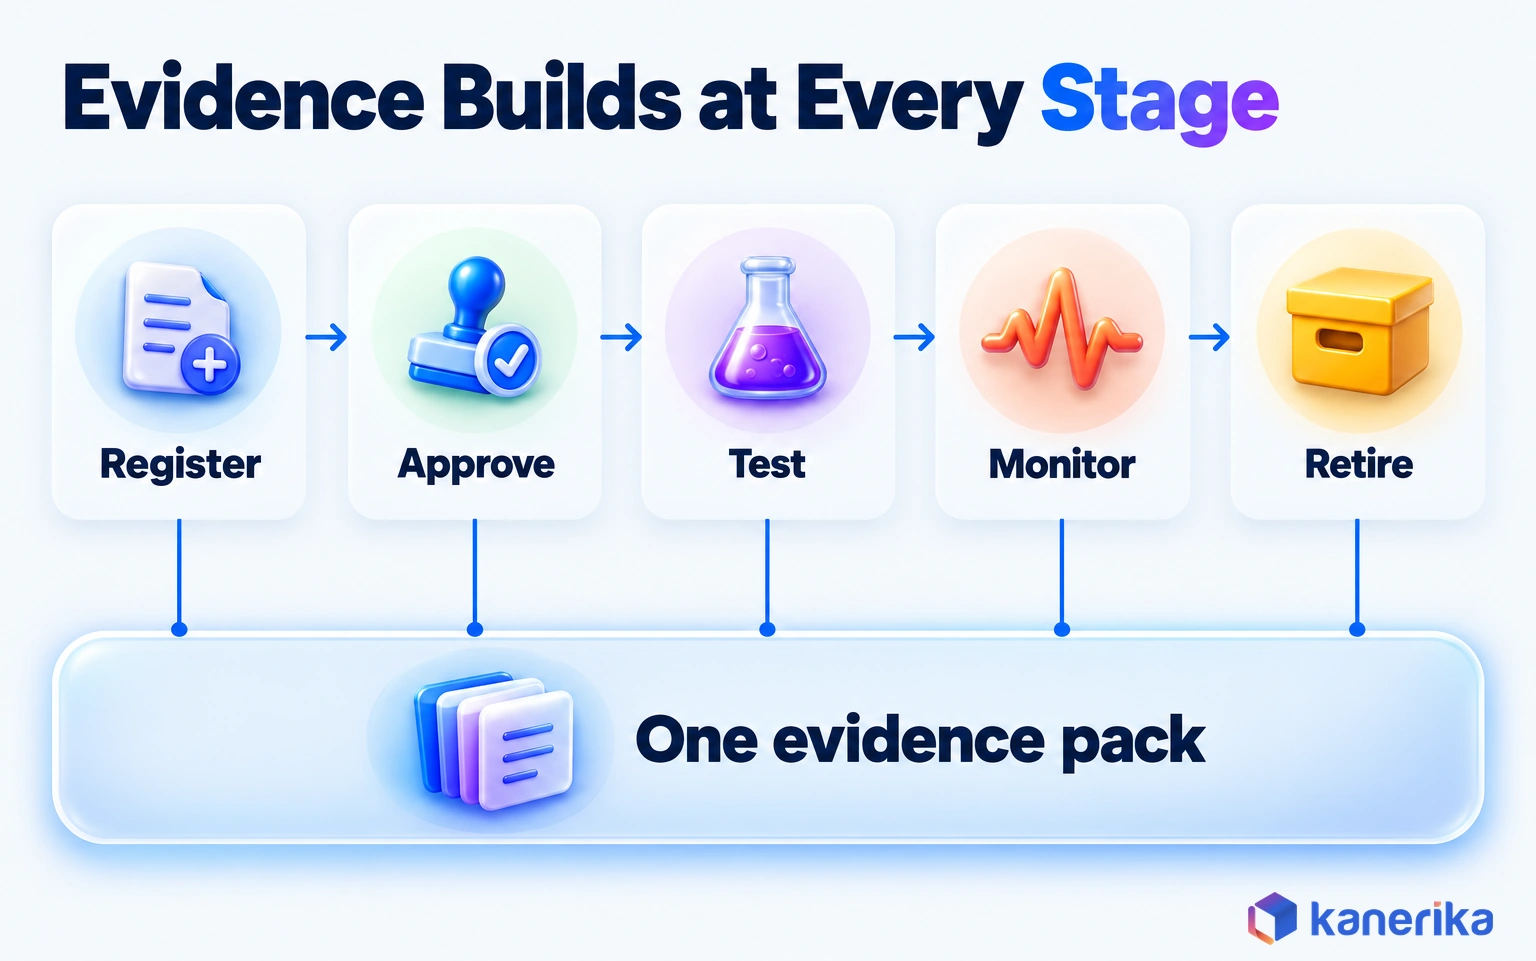
An AI governance tool follows each system through its whole life, from registration to retirement. Its value comes from linking each stage to the next, so evidence builds up without anyone assembling it later.
- Register. A product owner records the use case, the model or vendor, the data it uses and the people accountable.
- Classify risk. The tool scores the use case against policy and regulation, such as the EU AI Act risk tiers.
- Approve. Reviewers from risk, legal and data sign off, often with conditions such as human review for some decisions.
- Test. Bias, accuracy, safety and security tests run before launch, and results attach to the record.
- Deploy with guardrails. Runtime policies limit what the system can do, such as which tools an agent may call.
- Monitor. Drift, quality and policy breaches raise alerts and open incidents.
- Produce evidence. Reports pull approvals, tests and incidents into one pack for auditors or the board.
- Retire. Finally, the system is decommissioned, its access removed and its record closed.
For traditional ML, monitoring centers on drift and bias, which Kanerika covers in its guide to machine learning governance. Agents add a different set of risks, which is why the next part matters.
Why AI Agents Need Different Controls Than Predictive Models
A predictive model returns a score, and then a person or system decides what to do with it. An agent, by contrast, takes actions itself. It calls tools, reads documents, writes records and sometimes triggers other agents.
That changes what governance has to cover. Each agent needs an identity, so its actions can be traced to an owner. Its tool permissions need limits, such as read-only access to a CRM or a cap on refund amounts. Access to MCP servers and external APIs also needs the same review as any new integration.
The OWASP Top 10 for LLM applications, 2025 edition, names two of these risks directly. LLM01 is prompt injection, and LLM06 is excessive agency, where an agent holds more tools or permissions than its task needs. Both belong in your AI security framework as well as your governance register.
Runtime controls do most of this work, which is why gateways and AI guardrails matter more for agents than for models. Kanerika’s guide to agentic AI governance covers how to design those controls before the first agent ships.
Who Owns Governance After the Tool Is Installed
A tool records decisions, but people still make them. Programs stall when the tool goes live and nobody owns the queue of open reviews.
| Role | Owns | Typical action in the tool |
|---|---|---|
| Risk and compliance | Policy, risk tiers and committee reporting | Sets policy packs and approves high-risk use cases |
| Legal and privacy | Regulatory reading, contracts and vendor terms | Reviews intake for legal exposure and AI vendor terms |
| Data governance | Data quality, access and lineage | Confirms training and grounding data is approved before use |
| ML and platform team | Testing, deployment and runtime guardrails | Attaches test results and configures runtime policies |
| Business owner | The use case and its outcomes | Registers the system and answers for its results |
Name one person for each row before the pilot starts. Otherwise, a tool with no owner for its review queue becomes a register that nobody updates.
How to Choose an AI Governance Platform
Choosing an AI governance platform starts with your estate rather than the vendor list. The platforms you already run, the regulators you answer to and the type of AI you build decide which category fits first.
Begin with three questions. Where do most of your models and agents run today? Which team will own the review queue? Which regulation sets your deadline? Those answers usually cut 14 options to three.
Best Fit by Scenario
The table maps common enterprise situations to a starting shortlist. Treat it as a first cut, and test the names against your own systems. If two rows describe you, start with the row tied to your nearest regulatory deadline.
| Your situation | Start with | Add if needed |
|---|---|---|
| Microsoft-heavy estate with Copilot and agents | Microsoft Purview | Credo AI or OneTrust when intake and approvals lead |
| Databricks-centric data and AI platform | Unity Catalog and Unity Gateway | Credo AI or ModelOp when you need a cross-platform register |
| Regulated insurer with pricing and claims models | Monitaur | A runtime tool such as Fiddler AI for live monitoring |
| Privacy-led program with many AI vendors | OneTrust AI Governance | Securiti when sensitive data exposure is the worry |
| IT and risk workflows run on ServiceNow | ServiceNow AI Control Tower | Arthur or Fiddler AI for agent runtime control |
| Data-science-led team building in one platform | Dataiku Govern or IBM watsonx.governance | Holistic AI when shadow AI is spreading |
Notice that every row starts with one tool and adds at most one more. Buying three overlapping platforms at once is a common way to stall a program before it produces any evidence.
Checklist
AI Governance Checklist
Work through inventory, risk tiers, approvals, testing and monitoring step by step, so your shortlist starts from a clear view of what you must govern.
Get the Checklist →Worked Example: A Bank With 40 Models and Six Agents
This example is illustrative, not a client case. Picture a regional bank running 40 production models, mostly credit and fraud scoring, plus six new agents built on Azure. It already licenses Microsoft 365 E5 and runs a model risk team.
The bank’s first question is where the risk sits. Its 40 models already go through model risk review, but the records live in documents. Meanwhile, the six agents read customer data, and two of them can draft account changes.
That points to two needs. Purview DSPM covers the data side of the agents. The bank may be able to turn it on under its existing Microsoft licensing, which it should confirm in the Purview service description. A lifecycle tool such as IBM watsonx.governance or ModelOp would give the model risk team one register for all 40 models.
So the shortlist becomes Purview plus two lifecycle candidates, tested in a short proof of concept. The bank skips a third product until the pilot shows a real gap, such as agent runtime guardrails.
One Platform or Several?
Extending what you own is usually the cheaper first step. Purview, Unity Catalog and ServiceNow already hold identity, data and workflow context, so adding AI controls there avoids a new integration project. Each extra product also adds a connector to maintain and another queue for reviewers to watch.
A specialist earns its place when the gap is real and measurable. Typical gaps include use-case intake across many platforms, model risk records for a regulator, or runtime guardrails for agents. Add one specialist for that gap, then connect it to the platform you extended.
A rough threshold helps with the call. If most of your models and agents run on one platform, extend that platform and hold off on a specialist. Once they spread across three or more platforms, a cross-platform register earns its place sooner, because no native tool sees the whole estate.
The test is simple. If a gap appears in your proof of concept, buy for it. If it only appears in a vendor’s slide deck, wait.
Talk to Kanerika
Planning an AI Governance Pilot?
Kanerika designs a short proof of concept on your own models and agents, with pass conditions written in advance so every vendor faces the same bar.
Plan Your Pilot →Open-Source AI Governance Tools
Open-source projects cover parts of AI governance well, especially testing and runtime guardrails. They suit teams with strong engineering skills and a narrow, technical gap to fill.
| Project | What it covers | License |
|---|---|---|
| Fairlearn | Fairness assessment and bias mitigation for ML models | MIT |
| AI Fairness 360 (AIF360) | Bias metrics and mitigation algorithms | Apache-2.0 |
| NeMo Guardrails | Programmable guardrails for LLM apps and conversations | Apache-2.0 |
| VerifyWise | Governance platform tagged for the EU AI Act, ISO 42001 and NIST AI RMF | VCEL 1.0 (source-available; commercial license after a 60-day evaluation) |
Fairlearn and AIF360 handle the testing stage, while NeMo Guardrails handles part of runtime control. VerifyWise comes closest to a full governance platform, since it targets the main frameworks directly. It is source-available rather than open source, though, so production use inside a company needs a commercial license after a 60-day evaluation.
What open source rarely replaces is the enterprise layer. Inventory across many teams, approval routing, audit-ready reports and support all take work to build and run. For that reason, many enterprises use open-source testing libraries inside a commercial governance platform rather than instead of one.
What AI Governance Tools Cost
Vendors in this market rarely publish list prices, so cost depends on how each one meters use. Understanding the pricing model matters more than any single quote, because it decides what makes your bill grow.
Four pricing models are common. Some vendors charge per use case or per model under governance. Others charge per seat for reviewers and owners, or by consumption, such as requests through a gateway. Platform-native controls, by comparison, are often bundled into a license you already pay for.
| Cost driver | Why it moves the bill | What to ask |
|---|---|---|
| Number of models and use cases | Per-asset pricing rises when new systems go live | Are retired or test models still counted? |
| Number of agents and runtime calls | Consumption pricing rises when agent traffic grows | Is there a cap once traffic spikes? |
| Reviewer and owner seats | Seat pricing climbs when more teams join | Do occasional reviewers also need a paid seat? |
| Integrations and connectors | Each ML platform or data source adds setup work | Which connectors are included, and which are custom? |
| Regulatory content | Policy packs and framework mappings may be add-ons | Are EU AI Act and NIST mappings in the base price? |
Integration effort is the cost buyers most often miss. Custom connectors to your ML platform, ticketing system and identity provider can take longer than the license term suggests. So ask each vendor for a connector list and a reference customer with a similar stack.
Seven Tests to Run in an AI Governance Proof of Concept
A proof of concept is where vendor claims meet your real systems. Write the pass condition for each test before the pilot starts, so every vendor faces the same bar.
- Inventory import. Load your current model and agent list. It passes when every system appears with an owner and risk tier, without manual retyping.
- Shadow AI discovery. Point the tool at one business unit. It passes when it finds AI use that is missing from your register.
- Intake to approval. Run one new use case through the full workflow. It passes when the right reviewers are routed automatically and the approval is recorded with conditions.
- Evaluation evidence. Attach bias and accuracy results from your own pipeline. It passes when results link to the system record without screenshots. Kanerika’s guide to AI in quality assurance also covers how to design those evaluation tests.
- Agent guardrail. Give a test agent a tool it should not use. It passes when the call is blocked or held for approval, and the event is logged.
- Regulatory mapping. Pick one high-risk use case. It passes when the tool shows which EU AI Act or NIST AI RMF controls are met and which are open.
- Audit export. Ask for an evidence pack for one system. It passes when a reviewer outside the project can follow it without a walkthrough.
Score each test pass or fail before you weigh price. A tool that fails the audit export test has failed the job you are buying it for, however strong its demo looked.
Common Mistakes When Buying AI Governance Tools
Buying mistakes in this market follow a pattern. Each one below starts when governance is treated as a one-time software purchase.
Buying before the inventory exists. A team signs a three-year contract, then discovers that nobody can list the company’s AI systems. Build a rough register in a spreadsheet first, so the pilot has real data to load.
Choosing by framework logos. A vendor shows EU AI Act, NIST and ISO badges on its slides. Still, the real question is whether it produces evidence for your systems, and only a pilot answers that.
Governing AI on ungoverned data. A chatbot passes every model test but leaks a salary file, because document permissions were never cleaned up. Fix access and classification as part of your data governance framework before agents read from it.
Ignoring agents in the pilot. A team tests only its credit models and later finds the tool cannot see the agents that business units launched. Include at least one agent in every proof of concept.
Leaving the review queue unowned. The tool goes live, intake forms pile up and teams route around it. Assign an owner and a review service level on day one, before the backlog forms.
How Kanerika Helps Enterprises Govern AI in Production
Kanerika’s AI governance services start from the systems a client already runs, rather than from a new platform. The work follows four steps, and each one produces something a risk team can use.
First comes an assessment of the AI inventory and data exposure. Kanerika lists the models, agents and AI-enabled products in use, then maps which sensitive data each one can reach. As a result, the client gets a register and a risk view before any purchase.
Next, Kanerika extends the controls the client already owns. As a Microsoft and Databricks partner, the team configures Purview DSPM, Unity Catalog and Unity Gateway policies. Agents and models inherit existing data controls.
A specialist tool comes in only when a gap remains, such as cross-platform intake or model risk records. Finally, Kanerika runs the program with the client and keeps the evidence pack current as systems change.
Governance by Design: A Payment Technology Provider
One engagement shows the design principle at work. A payment technology provider needed faster brand compliance approvals for its partners, without loosening its rules.
Kanerika built a conversational AI assistant that answers only from a centralized, approved policy corpus. Because the assistant cannot draw on unapproved sources, every answer traces back to a governed document.
Case Study
60% Faster Brand Approvals with Conversational AI
A payment technology provider raised brand compliance by 35%, cut approval turnaround by 60% and reduced manual effort per brand query by 70% with an assistant grounded in approved policy.
Read the Case Study →The project was not an AI governance platform rollout. Instead, it shows how controls built into an AI system’s design make it both faster and easier to audit. The evidence trail exists from the first answer, so nobody has to assemble it before a review.
Choosing AI Governance Tools: The Bottom Line
Start with your estate. Extend Microsoft Purview if you run Microsoft 365 and Azure, or Unity Catalog and Unity Gateway if you build on Databricks. Choose Credo AI or OneTrust when policy and intake lead, Monitaur when insurance regulators do, and ServiceNow AI Control Tower when workflows already live there. Then prove the shortlist with seven tests on your own models and agents. The best AI governance tools for 2026 hand your auditor an inventory, an approval trail and live evidence on the day they ask.
Frequently Asked Questions
What are AI governance tools?
AI governance tools are software that keeps an inventory of AI systems, routes each one through risk review and approval, tests and monitors it, and stores the evidence that every control ran. They turn a written AI policy into a repeatable workflow with an audit trail, so teams can answer regulators, auditors and customers quickly.
What is the difference between an AI governance tool and an AI governance platform?
An AI governance tool usually covers one job, such as bias testing, runtime guardrails or data protection for AI. An AI governance platform combines several jobs in one system, including inventory, intake, approvals, monitoring and evidence export. Many enterprises run one platform as the system of record and connect specialist tools to it.
Does Microsoft Purview support AI governance?
Microsoft Purview covers the data security and compliance side of AI governance. Its Data Security Posture Management for AI discovers AI usage and the sensitive data flowing into AI apps, and Purview manages data security for Microsoft Agent 365. Teams that need use-case intake and model risk records usually pair Purview with a policy platform.
How long does it take to implement an AI governance platform?
Timing depends on how many AI systems you run, how many integrations the tool needs and whether an inventory already exists. Implementation usually moves through phases. Teams build the inventory, configure intake and approval workflows, connect testing and monitoring sources, pilot with a few systems and then roll out across business units in waves.
How do you measure the ROI of AI governance tools?
Measure the time it takes to answer an audit request, the share of AI systems with an owner and risk tier, and the days from intake to approval. Track incidents caught by monitoring before customers notice them. Compare these figures before and after the pilot to show what the platform saves the risk and engineering teams.
How does Kanerika help enterprises pick AI governance tools?
Kanerika starts with an assessment of your AI inventory and data exposure, then extends the controls you already own, such as Microsoft Purview, Unity Catalog and Unity Gateway. Where a gap remains, the team shortlists specialist tools and runs a proof of concept on your systems. Kanerika then helps operate the program and keep evidence current.
Which AI governance tools support the EU AI Act and NIST AI RMF?
Several platforms help. Credo AI turns regulations into checks through its Policy Packs, OneTrust runs policy evaluation with automated risk scoring, and IBM watsonx.governance covers compliance across the model lifecycle. The source-available VerifyWise project targets the EU AI Act, ISO 42001 and NIST AI RMF directly. Always confirm during a pilot that the tool produces evidence for your own systems.
When do EU AI Act high-risk obligations apply?
After the AI Omnibus entered into force on July 27, 2026, high-risk obligations moved later. Systems in Annex III areas such as biometrics, education, employment and critical infrastructure must comply from December 2, 2027. High-risk systems built into regulated products under Annex I follow on August 2, 2028, while the wider Act applies from August 2, 2026.
What is the difference between AI governance tools and data governance tools?
Data governance tools manage data assets through catalogs, lineage, quality checks and access rules. AI governance tools manage AI systems through use-case intake, risk classification, approvals, testing, runtime monitoring and audit evidence. The two connect closely, since a model trained or grounded on poorly governed data carries that risk into every answer it gives.
How much do AI governance tools cost?
Most vendors quote prices privately, so cost depends on the pricing model and your scope. Common models charge per use case or model, per reviewer seat, or by consumption through a gateway. Platform-native controls are often bundled into licenses you already own. Integration work with your ML platforms and ticketing systems can add significant setup cost.
Do I need more than one AI governance tool?
Many enterprises end up with two tools, one platform-native control and one specialist. A Microsoft estate might extend Purview for data protection and add Credo AI or OneTrust for intake and approvals. Start with what you own, run a proof of concept, and add a second tool only when the pilot shows a measurable gap.
What is shadow AI and which tools detect it?
Shadow AI is any AI tool, model or agent used without approval, such as staff pasting customer data into a public chatbot. Holistic AI and OneTrust include discovery in their inventory workflows. Microsoft Purview DSPM shows which AI apps receive sensitive data, and Securiti tracks sensitive data across the systems AI reads from.
Are there open-source AI governance tools?
Yes. Fairlearn and AI Fairness 360 cover bias testing, NeMo Guardrails adds runtime guardrails for LLM apps, and source-available VerifyWise targets major frameworks but needs a commercial license for company use. These projects suit engineering-led teams. Enterprises still need inventory, approval routing and audit reports across many teams, so many use open-source libraries inside a commercial platform.
What tools are used to govern AI agents?
Agent governance needs an agent register, identity, tool permissions and runtime enforcement. Credo AI includes an AI Agent Registry, Arthur adds agent discovery and guardrails, and Fiddler AI provides agentic observability with policy guardrails. Databricks Unity Gateway governs calls between agents, models, MCP servers and tools, while Purview manages data security for Microsoft Agent 365.