TL;DR
Snowflake security is a shared job, and the controls your team configures matter more than the defaults Snowflake ships. By default, Snowflake encrypts data, blocks known malicious IP addresses and checks for leaked passwords. The controls that would have stopped the 2024 customer account breaches, such as MFA and network policies, are settings your team turns on. Start with SSO and MFA for people, and key pairs, OAuth or workload identity for services. Next, add an account network policy, least-privilege roles and masking on sensitive columns. Enterprise edition adds masking, row access policies and access history, while Business Critical is needed only for customer-held keys or private connectivity.
Key Takeaways
- Snowflake encrypts all data and blocks known malicious IP addresses by default, but MFA, network policies, roles and masking are settings you turn on.
- The 2024 customer account breaches came from stolen passwords on accounts with no MFA and no network allow lists, rather than from a flaw in Snowflake.
- Snowflake’s published schedule retires single-factor passwords in phases, so service users should move to key pairs, OAuth, tokens or workload identity.
- Least-privilege roles and a small, named ACCOUNTADMIN group limit what one stolen login can reach, especially when sensitive schemas use managed access.
- Trust Center flags missing MFA and network policies by default, LOGIN_HISTORY shows who signed in, and Enterprise edition’s ACCESS_HISTORY shows what they read.
- Masking and row access policies need Enterprise edition, while Tri-Secret Secure and private connectivity need Business Critical.
One Saved Password, No Second Check
An analyst at a mid-sized retailer installs a free PDF converter on a personal laptop. But the installer also carries infostealer malware. Within minutes, it copies every password saved in the browser, such as the one for the company’s Snowflake account.
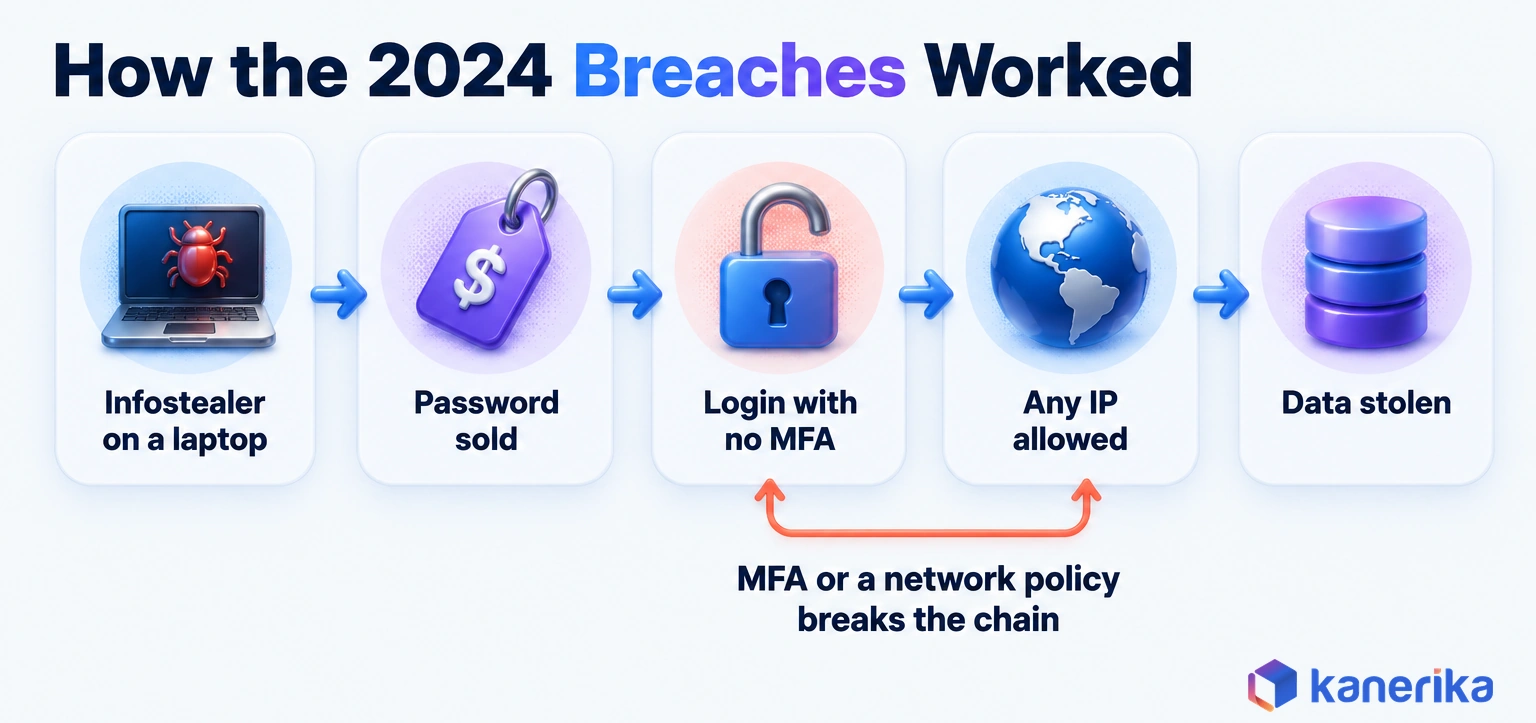
Nothing happens for months. Then the stolen login shows up for sale. A buyer later signs in from a rented server on another continent, runs a few large queries and copies customer tables out. No alarm fires, because the account never asked for a second factor and accepted logins from any IP address.
The scene is a composite, but every step matches what Mandiant documented in the 2024 campaign it tracks as UNC5537. Most of the credentials came from infostealer infections on systems unrelated to Snowflake, some dating back to 2020. According to Mandiant’s investigation, at least 79.7% of the accounts the attacker used had prior credential exposure.
The fallout was wide, since Mandiant and Snowflake notified about 165 potentially exposed organizations. Some of the stolen passwords had also gone unrotated for as long as four years.
Why Snowflake Security Is a Configuration Problem
Despite the headlines, Snowflake itself was not breached in 2024. Mandiant found no evidence that the attacks stemmed from a breach of Snowflake’s enterprise environment. Instead, every incident it responded to traced back to compromised customer credentials.
That finding reframes the whole topic. The platform runs a secure baseline, but the controls that decide whether a stolen password works belong to the customer. Mandiant named three gaps in the affected accounts: no MFA, credentials that were never rotated and no network allow lists.
All three are settings, so none of them needs a new product or a bigger budget.
The useful question is whether your account is configured so that one leaked password is worth nothing, and whether you would notice if someone tried.
What Is Snowflake Security?
Snowflake security is the set of controls deciding who reaches your account, what they see inside and how you spot trouble. Some of those controls are on from day one, before anyone logs in. Most of the ones that matter, though, are yours to configure.
Snowflake’s own guide to securing Snowflake draws that line clearly. For example, the platform encrypts data in transit and at rest, blocks sign-ins from known malicious IP addresses and checks for leaked passwords. Its Security Essentials scanner in Trust Center also runs by default, checking for missing MFA and missing network policies.
Everything else sits on your side, such as how people and services sign in, which networks can connect and which columns get masked. It is a shared-responsibility model, much like the one cloud providers use for servers. The main difference is that a warehouse holds the data attackers want most, so the stakes are higher.
What Snowflake Covers and What You Configure
Here is how that split looks in practice. On day one, a new account already has encryption, malicious IP blocking and a baseline scanner. Still, nobody has set a network policy, moved service users off passwords or written a masking policy. The defaults protect the platform, while the configuration protects the business.
Table 1: What Snowflake provides by default and what you configure
| Area | Snowflake provides by default | You configure |
|---|---|---|
| Encryption | Data encrypted at rest and in transit, with keys rotated automatically | Periodic rekeying (Enterprise), as well as Tri-Secret Secure with your own key (Business Critical) |
| Sign-in | Leaked password protection | SSO, MFA, key pairs, OAuth, access tokens, workload identity and agent identity |
| Network | Malicious IP protection | Network rules and policies, as well as private connectivity |
| Access | Built-in system roles | Role hierarchy, grants and managed access schemas, together with data movement policies |
| Data | Encryption of every table | Masking, row access and tag-based policies |
| Monitoring | Security Essentials scanner in Trust Center | Extra scanner packages, alerts and regular log reviews |
Teams comparing platforms will also find the same shared model elsewhere. Our guides to data warehouse security in Microsoft Fabric and Databricks security show how those platforms divide the work differently than Snowflake does. For the wider picture, see our overview of data security. Our written Databricks vs Snowflake comparison goes deeper, and the video below compares the two on pricing, AI and security side by side.
Architecture also shapes where these settings live. Our guide to Snowflake architecture covers how storage, compute and cloud services fit together. For security, the main point is simpler. Controls live at the account, user and object level, so one policy applies no matter which warehouse runs the query.
How Snowflake Security Works From Login to Data Access
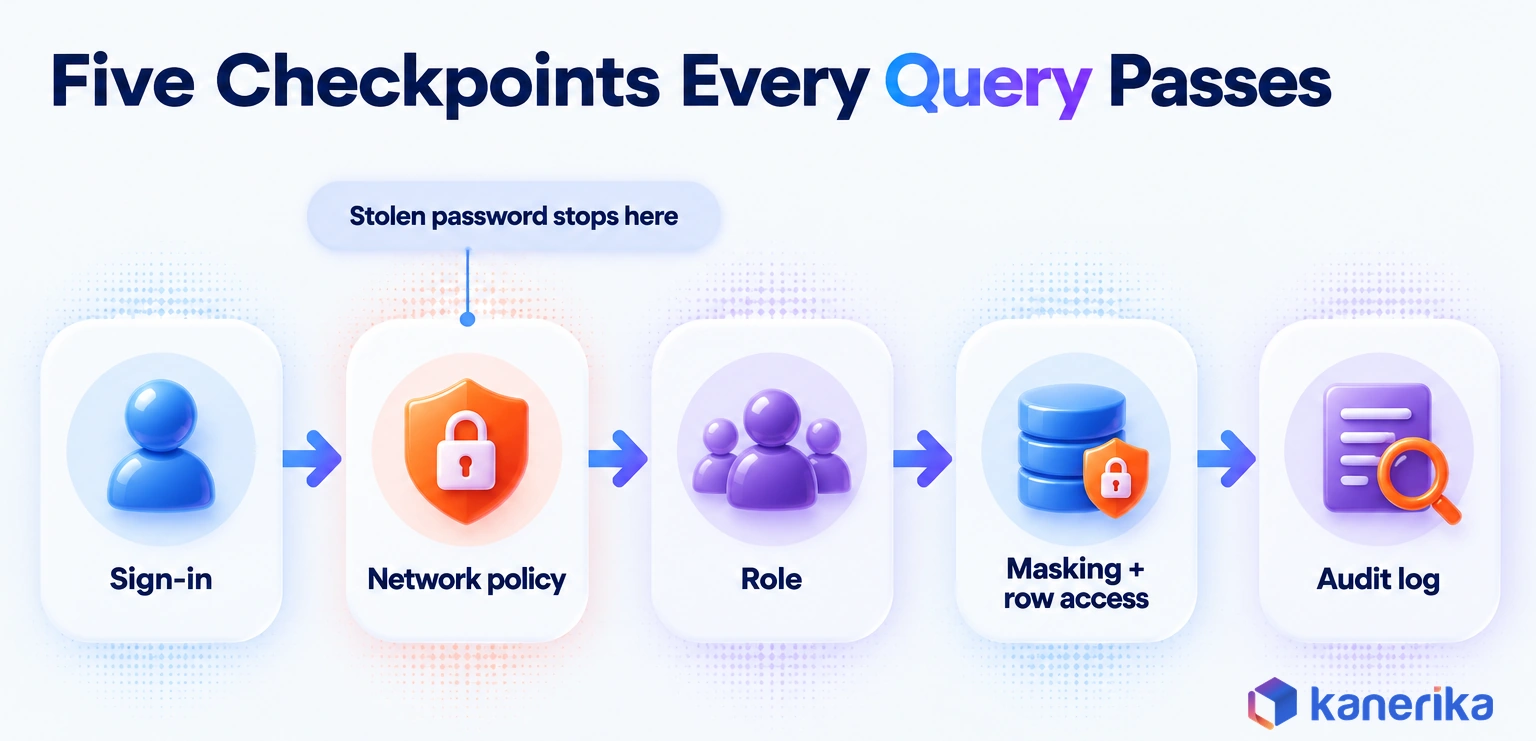
Every query in Snowflake passes the same five checkpoints, and each one can stop a request the previous one let through. For example, picture the analyst from the opening story running a sales report at 9 a.m. from the office. Then picture the attacker running the same query at 3 a.m. from an unknown server.
A well-configured account treats those two requests very differently, even though the password is the same. Here is where each checkpoint does its work.
The Five Checkpoints, One at a Time
Authentication. Snowflake first asks who is signing in and how, before anything else happens. A password alone is the weakest answer, while SSO with MFA, a key pair or an OAuth token is far harder to steal and reuse.
Network policy. After that, Snowflake checks where the request came from. A network policy can allow only office ranges, VPN addresses or a private endpoint. So the 3 a.m. login from a rented server fails here, even with a valid password.
Role and privileges. Once inside, the session acts under one primary role. That role decides which databases, schemas and tables the user can query, so a marketing analyst role never sees payroll tables at all.
Masking and row access. Even on a permitted table, policies can still hide values or rows. For example, a support agent might see only the last four digits of a card number, and only for their own region.
Audit trail. Finally, the login, the query and the objects it touched land in Snowflake’s account usage views. When the first four checkpoints fail, this record is how you find out.
Each layer assumes the others might fail, which is the idea behind defense in depth. It also matches the zero trust model in NIST SP 800-207 (August 2020), which grants no implicit trust based on network location. For background on how the platform stores and serves the data underneath these checks, see how the Snowflake data warehouse works.
Case Study
47% Faster Breach Detection with Incorta Analytics
SeaLink, Australia’s largest integrated transport operator, cut breach identification time by 47% and improved compliance adherence by 32% with Kanerika-built analytics on Incorta.
Read the Case Study →Identity and Authentication: SSO, MFA and the End of Passwords
Sign-in is where most Snowflake security failures start, so it is where hardening should start too. The goal is simple to state, even if it takes work to reach. No account, human or machine, should be able to sign in with a password alone.
Snowflake is also pushing in the same direction. Its strong authentication program retires single-factor passwords in phases, and it treats people differently than software. That split shapes everything below.
Human Users: SSO, MFA and Authentication Policies
For people, the cleanest setup is single sign-on through your identity provider. Users sign in with the same corporate identity they use everywhere else. Joiners and leavers are then handled in one place, and the identity provider’s MFA covers the second factor.
Users who still sign in with a Snowflake password need MFA on top. Snowflake made MFA mandatory for Snowsight users in the first phase of its rollout, from September 2025 to January 2026. Users who sign in through SSO were not affected by that phase, since their identity provider handles authentication.
Authentication policies tie this together, because they set which sign-in methods and clients a user or account may use. A common pattern is one account-level policy that requires MFA for people. Service users then get a separate policy that allows only key pairs or OAuth.
The example below follows Snowflake’s authentication policy documentation. It sets one policy for people and a stricter one that limits service users to key pairs, OAuth or workload identity.
-- Run in the schema that holds your security objects
CREATE AUTHENTICATION POLICY people_mfa_policy
  MFA_ENROLLMENT = 'REQUIRED';

CREATE AUTHENTICATION POLICY service_strong_auth_policy
  AUTHENTICATION_METHODS = ('KEYPAIR', 'OAUTH', 'WORKLOAD_IDENTITY');

-- Password users must enroll in MFA
ALTER ACCOUNT SET AUTHENTICATION POLICY people_mfa_policy
  FOR ALL PERSON USERS;

-- Migrate LEGACY_SERVICE users first: this blocks their passwords
ALTER ACCOUNT SET AUTHENTICATION POLICY service_strong_auth_policy
  FOR ALL SERVICE USERS;
Break-glass access also deserves its own plan. Keep one emergency administrator that does not depend on the identity provider, protect it with MFA and store its credentials offline. Test it twice a year, so a broken login does not surface during an outage.
Service Users: Key Pairs, OAuth, Programmatic Access Tokens and Workload Identity
Service users are the logins that pipelines, BI tools and scripts use. They cannot answer an MFA prompt, which is why stolen service passwords are so dangerous. Snowflake’s answer is a separate user type with no password at all, rather than a stronger password.
A user set to TYPE = SERVICE cannot sign in with a password. The LEGACY_SERVICE type still allows one, but only as a temporary bridge. Phase 2 of Snowflake’s rollout stopped new LEGACY_SERVICE users, and phase 3 converts the remaining ones to TYPE = SERVICE, which blocks their passwords. Every LEGACY_SERVICE user left in your account is therefore a pipeline about to stop signing in.
The right replacement depends on the workload. For example, a nightly ETL job on a fixed server suits a key pair. A BI tool that signs users in on their behalf suits OAuth instead. A script that only accepts a secret string can use a programmatic access token, or PAT.
Tokens come with guardrails, though. By default, a user must be subject to a network policy before generating or using a PAT. Each token also expires after at most 365 days by default. An authentication policy can shorten that limit, as Snowflake’s programmatic access token documentation explains.
Workload Identity Federation and Choosing a Method
Workload identity federation goes one step further than tokens. A workload running in a cloud provider proves who it is with that provider’s own identity, so no long-lived Snowflake secret sits in a config file. That is why Snowflake’s security guide names it the preferred method for service-to-service workloads.
The workload identity federation documentation lists AWS IAM roles, Entra ID managed identities, Google Cloud service accounts and any OIDC issuer as sources. So pick it whenever a workload already runs in a cloud provider, and keep key pairs for servers you run yourself.
Table 2: Service user authentication methods compared
| Method | Best for | Watch out for |
|---|---|---|
| Key pair | Scheduled jobs and connectors on servers you control | Private keys copied into code or shared drives, so rotate them on a schedule |
| OAuth | BI tools and apps acting for named users | Token lifetimes and scopes set too broadly in the security integration |
| Programmatic access token | Tools that accept only a secret string | Needs a network policy by default and expires within 365 days, so set 90 days or less |
| Workload identity federation | Workloads running inside a cloud provider | Trust settings loose enough to match workloads you did not intend |
| Password (LEGACY_SERVICE) | A temporary bridge only, until a stronger method is in place | Single factor, and phase 3 converts these users to SERVICE, which blocks the password |
In practice, moving one pipeline off a password takes only a few statements. The example below changes the user type, attaches the public half of a key pair and then checks the result.
-- Turn a pipeline login into a service user
ALTER USER svc_nightly_etl SET TYPE = SERVICE;

-- Attach the public key (paste the full key, without header lines)
ALTER USER svc_nightly_etl SET RSA_PUBLIC_KEY = 'MIIBIjANBgkqh...';

-- Confirm the user type and key fingerprint
DESCRIBE USER svc_nightly_etl;
Snowflake requires at least a 2048-bit RSA key for this method. Its key-pair authentication guide also explains rotation through a second slot, RSA_PUBLIC_KEY_2, so clients can switch keys without downtime.
Snowflake’s Strong Authentication Timeline
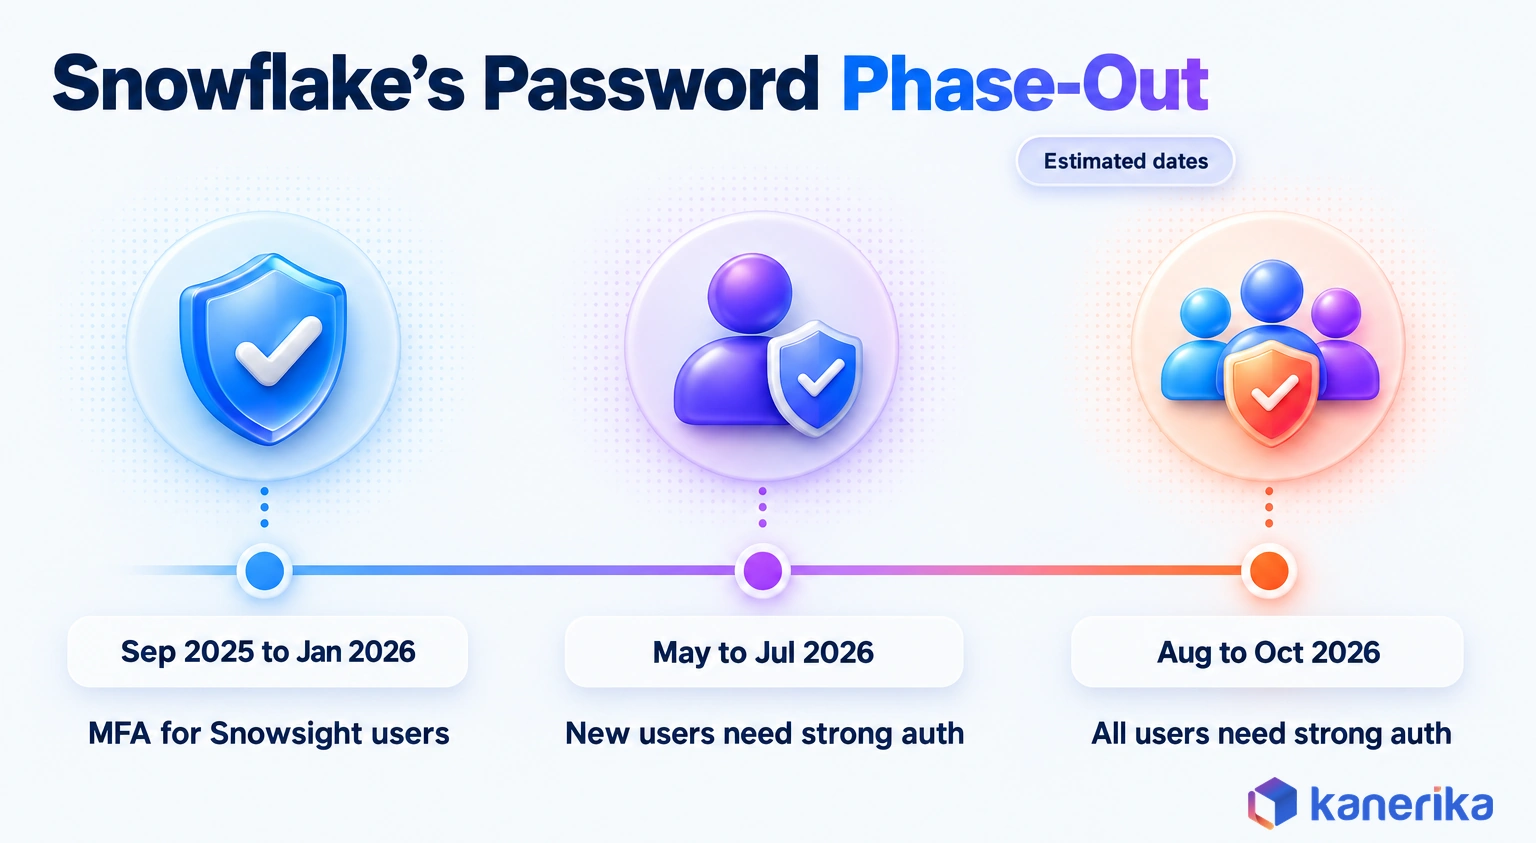
Snowflake published a phased schedule for retiring single-factor passwords. The windows below are Snowflake’s own estimates from its MFA rollout page, so check that page before you plan around a specific week.
Table 3: Snowflake’s published strong authentication schedule
| Phase | Estimated window | What changes |
|---|---|---|
| Phase 1 | September 2025 to January 2026 | MFA became mandatory for all Snowsight users |
| Phase 2 | May to July 2026 | MFA required for new human users who sign in with a password, and no new LEGACY_SERVICE users can be created |
| Phase 3 | August to October 2026 | MFA required for every password user, and password sign-in blocked for all service users |
The last window closes in October 2026, so any password-only login left in your account is now on borrowed time. Treat every remaining one as an open finding.
Least-Privilege Access Control With RBAC
Once a user is signed in, role-based access control decides what they can actually touch. In Snowflake, privileges are granted to roles, and roles are granted to users or to other roles. So in a well-designed account, people get access only through roles they can explain.
The design that holds up best uses two kinds of roles. Access roles hold privileges on objects, such as read access to a finance schema. Functional roles match job functions, such as finance analyst, and inherit one or more access roles.
When someone changes jobs, you swap one functional role instead of hunting down dozens of grants. For example, take a finance analyst who reads ledger tables and writes to a sandbox. The analyst gets the FINANCE_ANALYST role, which inherits FINANCE_READ and SANDBOX_WRITE, and an auditor can read that chain to see why the access exists. Our framework for data access governance covers the access reviews that keep this design honest.
Seven Steps to a Least-Privilege Role Design
The steps below turn that pattern into a working design.
- Map access roles to schemas. Create read, write and owner access roles for each schema or data domain before anything else.
- Build functional roles from job functions. Then grant each functional role only the access roles that job needs.
- Keep ACCOUNTADMIN to a few named people. Two or three administrators with MFA is enough for most accounts, so nobody needs it as a default role.
- Separate security administration. Let SECURITYADMIN and USERADMIN handle grants and users, so routine work never needs ACCOUNTADMIN.
- Use managed access schemas. In a managed access schema, only the schema owner or a role with MANAGE GRANTS can grant access, rather than every object owner. Snowflake’s access control overview describes the full model.
- Set future grants. Future grants give new tables the right access automatically, so nobody hands out broad roles as a shortcut.
- Review grants every quarter. Remove roles nobody has used in 90 days, as well as functional roles with no members.
Roles for BI Tools and Other Service Users
BI service users need the same discipline, especially as dashboards multiply. A reporting tool should connect with its own service user and a narrow read-only role rather than an analyst’s login or a shared admin account.
Teams moving reports from Cognos to Power BI often meet this problem when they repoint dashboards at Snowflake. So that migration is a good moment to create a clean, read-only role for the new tool.
Checklist
Snowflake Checklist
Review your Snowflake account across cost, performance, storage, security and governance, and spot weak access controls before they turn into incidents.
Get the Checklist →Network Security: Policies, Rules and Private Connectivity
Network controls answer a blunt question: where is this request coming from? When the answer is outside your known networks, a good setup refuses the connection, even with valid credentials. Mandiant also found that control missing on the compromised accounts it investigated.
Snowflake builds network control from two objects. A network rule describes a set of addresses or endpoints, such as an office IP range or a private endpoint ID. A network policy then lists which rules to allow and which to block, and one rule can feed several policies.
Private connectivity is the stronger option, though it needs a higher edition. With AWS PrivateLink, Azure Private Link or Google Cloud Private Service Connect, traffic between your cloud network and Snowflake stays off the public internet. A network policy can then block public access entirely and allow only the private endpoint.
Table 4: Network policy vs private connectivity
| Factor | Network policy with IP rules | Private connectivity |
|---|---|---|
| What it controls | Which IP ranges may connect | The network path traffic travels |
| Edition | All editions | Business Critical or higher |
| Traffic path | Public internet, filtered by address | Private cloud network, so traffic avoids the public internet |
| Setup effort | Low, since it is a rule and a policy in SQL | Higher, because it needs cloud endpoints and DNS changes |
| Best for | Office, VPN and fixed server ranges | Regulated workloads as well as cloud-hosted pipelines |
Testing a Network Policy Safely
A minimal policy for an office range looks like the example below. Try it on one user first, because an account-level policy written wrongly can lock everyone out, including you.
-- Run in a schema that holds your security objects
CREATE NETWORK RULE corp_vpn_ips
  MODE = INGRESS
  TYPE = IPV4
  VALUE_LIST = ('203.0.113.0/24');

CREATE NETWORK POLICY corp_only
  ALLOWED_NETWORK_RULE_LIST = ('corp_vpn_ips');

-- Test on one user before applying it to the account
ALTER USER test_analyst SET NETWORK_POLICY = corp_only;
How Policy Precedence Works
Network policies can attach at three levels: the account, a security integration or a single user. When more than one applies, the most specific one wins. So a security integration policy overrides a user-level policy, which in turn overrides the account policy.
Inside a policy, private-connectivity rules take precedence over IPv4 and IPv6 rules. A request that arrives through an allowed private endpoint is therefore judged by the endpoint rule, not by the IP rules beside it. Snowflake’s network policy documentation also covers the full evaluation order.
Precedence can still cause real surprises. A user-level policy written for one contractor can quietly bypass a stricter account policy, so review user-level policies as carefully as the account one.
When Private Connectivity Is Worth Business Critical
Private connectivity requires Business Critical edition or higher, so the decision is partly about budget. It earns its cost when regulators or customers require that data never cross the public internet. It also pays off when most traffic already comes from pipelines inside one cloud provider.
For analysts working from laptops on a VPN, IP-based policies are usually enough when paired with SSO and MFA. A bank streaming card transactions from AWS into Snowflake faces a different calculation, since the private path removes a whole class of exposure. Decide by workload rather than by habit.
Talk to Kanerika
Get a Snowflake Security Review
Talk to Kanerika’s Snowflake team about your sign-in methods, network policies and roles, and leave with a prioritized list of fixes for your account.
Book a Security Review →Encryption and Key Management: Default Encryption vs Tri-Secret Secure
Encryption in Snowflake is on by default, so the real decision is who controls the keys. Every edition encrypts data at rest and in transit, and customers do not switch it on or pay extra for it.
In practice, Snowflake uses strong AES encryption with a hierarchical key model. The root of that hierarchy sits in a hardware security module, which the cloud provider hosts. Keys lower in the tree protect smaller sets of data, so any single key exposes less.
Snowflake also rotates these keys automatically. Enterprise edition then adds periodic rekeying, which re-encrypts older data with new keys, as Snowflake’s key management documentation describes.
Tri-Secret Secure: Holding Your Own Key
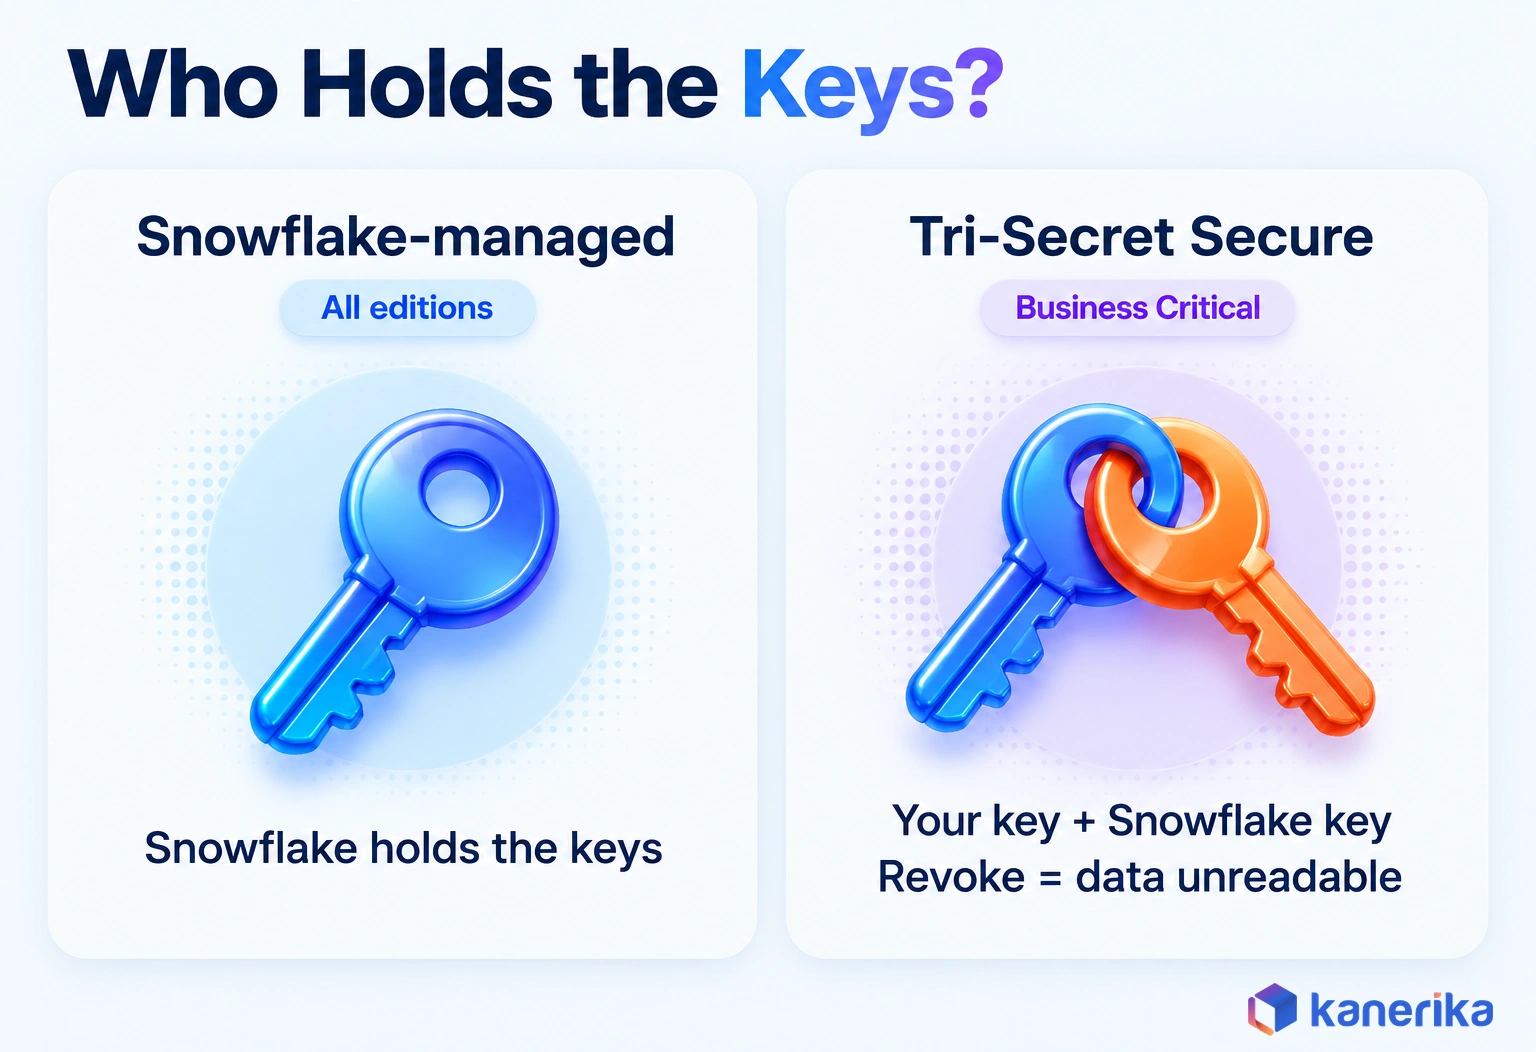
Tri-Secret Secure changes who owns the outcome, rather than how strong the encryption is. It combines a Snowflake-maintained key with a customer-managed key held in your cloud provider’s key service, forming a composite master key. Once you revoke your key, Snowflake can no longer decrypt the data, according to the Tri-Secret Secure documentation. That gives you a hard off switch, and it also gives you a new way to cause an outage.
For example, picture a healthcare company that must prove it can make its data unreadable on demand. Tri-Secret Secure gives it that proof. Yet the same company now owns key rotation, key service access and a runbook for accidental revocation. That matters because one mistaken key policy change can take the warehouse offline.
Table 5: Snowflake-managed encryption vs Tri-Secret Secure
| Factor | Snowflake-managed keys | Tri-Secret Secure |
|---|---|---|
| Edition | All editions, although periodic rekeying needs Enterprise | Business Critical or higher |
| Who holds the keys | Snowflake, rooted in a cloud provider HSM | Snowflake’s key together with your customer-managed key |
| Effect of revoking your key | Not applicable | Snowflake can no longer decrypt the data |
| Operating burden | None for the customer | Key rotation and key service access, as well as recovery runbooks |
| Best for | Most workloads | Regulated data with a customer key-control requirement |
Most accounts never need Tri-Secret Secure, so treat it as an exception. Choose it when a contract, regulator or internal policy demands customer-held keys, and staff the key operations before you switch it on.
Data-Level Protection: Masking, Row Access and Tags
Data-level policies decide what a permitted user sees once they are inside a table. Roles keep the wrong people out of the table, while masking and row access policies shape the answer for the right people.
A masking policy is a rule attached to a column. When someone queries that column, Snowflake checks the rule and returns either the real value or a masked one.
For example, take a customer table with an email column. The rule says the SUPPORT_LEAD role sees full addresses, the SUPPORT_AGENT role sees only the domain and every other role sees a placeholder. So one table serves all three audiences, and nobody maintains extra copies.
A row access policy does the same job for rows, while masking handles columns. A regional sales manager querying the orders table sees only orders from their own region. The policy filters rows at query time using the role or, as Snowflake’s row access policy guide shows, a mapping table.
Scaling Protection With Tags
Tags make this scale, especially in large accounts. You tag a column as PII once, then attach a masking policy to the tag instead of to each column. Every column with that tag inherits the protection, including columns added next quarter. All three policy types require Enterprise edition or higher.
The example below builds the email rule from the support example, then attaches it through a tag. It follows Snowflake’s masking policy reference and its guide to tag-based masking.
-- Run as the policy admin role, in the governance schema
CREATE MASKING POLICY email_mask AS (val STRING) RETURNS STRING ->
  CASE
    WHEN CURRENT_ROLE() IN ('SUPPORT_LEAD') THEN val
    WHEN CURRENT_ROLE() IN ('SUPPORT_AGENT') THEN '*****@' || SPLIT_PART(val, '@', 2)
    ELSE '********'
  END;

-- Attach the policy to a tag, then tag the column
CREATE TAG pii;
ALTER TAG pii SET MASKING POLICY email_mask;
ALTER TABLE crm.public.customers MODIFY COLUMN email SET TAG pii = 'email';
Who owns the policies matters as much as what they say. Keep masking and row access policies in a dedicated governance schema, owned by a policy admin role rather than by table owners. So nobody can quietly remove the protection from their own table.
Classification, data lineage and data ownership sit one level above these controls, so they need their own program. For that layer, see our guide to Snowflake data governance.
Securing Shared Data
Secure data sharing lets another Snowflake account query your data live, without copying it, as our guide to Snowflake data sharing explains. That is convenient, but it also moves part of your exposure into someone else’s account. A share exposes only the objects you grant to it, so the grant list is the real boundary.
A few habits keep sharing safe. Share secure views rather than base tables, so consumers see only the columns and rows you intend. Review the consumer accounts on every share at least quarterly, and remove any whose contracts have ended.
Shares also tend to outlive the projects that created them. For instance, a share set up for a partner pilot can keep serving data long after the pilot ends. Give each share a named business owner and an end date, and treat an ownerless share like an unused admin role.
Monitoring should also cover sharing. A new share, or a new consumer account added to an existing one, deserves the same review as a new ACCOUNTADMIN grant. Also test how your masking and row access policies behave when a consumer account queries the data, before the first share goes live.
On-Demand Webinar
Snowflake + Fabric: Expert Strategies for Interoperability, Data Sharing & Migration
An on-demand session on sharing data between Snowflake and Microsoft Fabric, with the trade-offs to weigh when data crosses platforms.
Watch the Webinar →Monitoring, Trust Center and Incident Response
Monitoring is how you learn that a control failed before an extortion email tells you. The data to catch an intruder early already sits in every Snowflake account. So the real work is deciding what to watch and who receives the alert.
What to Watch in ACCOUNT_USAGE
The SNOWFLAKE.ACCOUNT_USAGE schema keeps a history of logins, queries and data access. Of its many views, three carry most of the security signal. LOGIN_HISTORY records every sign-in attempt and its factors, while QUERY_HISTORY records what ran. ACCESS_HISTORY then records which objects each query read or changed, although it needs Enterprise edition or higher.
Then turn those views into a short alert list that a named person reviews, the same habit that drives data observability for pipelines:
- Successful logins from IP addresses or countries never seen before for that user.
- Password-only sign-ins, especially by service users.
- Bursts of failed logins against one user, a common sign of password spraying.
- Grants of ACCOUNTADMIN or SECURITYADMIN outside a change window.
- New or changed network policies, authentication policies and shares.
- Queries that read far more rows than the user’s normal pattern, or unload data to an external stage.
The query below finds successful password sign-ins with no second factor over the past seven days. It also makes a good first scheduled check.
SELECT user_name, client_ip, reported_client_type, event_timestamp
FROM SNOWFLAKE.ACCOUNT_USAGE.LOGIN_HISTORY
WHERE event_timestamp > DATEADD(day, -7, CURRENT_TIMESTAMP())
  AND is_success = 'YES'
  AND first_authentication_factor = 'PASSWORD'
  AND second_authentication_factor IS NULL
ORDER BY event_timestamp DESC;
Trust Center Scanner Packages
Trust Center is Snowflake’s built-in posture checker. It runs scanner packages against your account and lists findings you can act on. As of October 2026, only one package runs by default, so you enable the others when you need them.
Table 6: Trust Center scanner packages
| Scanner package | Default state | What it adds |
|---|---|---|
| Security Essentials | On by default | Checks for missing MFA and missing network policies |
| CIS Benchmarks | Opt-in | Evaluates the account against the CIS Snowflake Foundations Benchmark |
| Threat Intelligence | Opt-in | Detections of risky sign-in and admin activity, event-driven and daily |
| AI Security | Opt-in | AI misconfigurations and anomalous Cortex Agents, as well as an MCP server inventory |
| Data Security | Opt-in | Event-driven detections of unusual data unloads to stages |
Enabled scanners can add cost, so turn them on deliberately. A sensible start is Security Essentials plus CIS Benchmarks, which scores the account against the CIS Snowflake Foundations Benchmark and gives auditors an outside reference. Snowflake’s Trust Center overview also lists every package and its scanners.
Securing AI Agents and Cortex Workloads
AI features run under the same security model as everything else. A Cortex agent connects and reads data under the same sign-in, network and role rules as any other workload. An agent with a broad role can therefore read everything that role can, and summarize it for whoever asks.
The OWASP Top 10 for LLM and Gen AI Apps (2025 edition) ranks prompt injection first. It also lists excessive agency as LLM06, the risk a broad agent role creates. Our guides to agentic AI security and the wider AI security framework cover the threat model beyond Snowflake.
As of October 2026, Snowflake also adds a few AI-specific controls on top. Agent identity gives each agent an identity of its own, and restricted session scope limits what an agent’s session can do. Cortex AI Guardrails then screen prompts for injection and jailbreak attempts. Give every agent the narrowest role that does its job, exactly as you would a service user.
Agent activity deserves the same monitoring as any service user. Our guide to Snowflake Cortex covers what these features cost and where they break in production. For tracing agent behavior once agents go live, see our guide to AI agent observability.
The First Hour After a Suspected Compromise
When an alert fires, speed matters more than certainty. The steps below assume one human or service login looks compromised.
- Disable the user. Set the user to disabled so no new session can start.
- Rotate every secret it held. Replace its key pair, revoke its access tokens and reset any password.
- Review LOGIN_HISTORY. List every sign-in for that user over the past 30 days, together with IP addresses and client types.
- Review ACCESS_HISTORY and QUERY_HISTORY. Find which tables the session read during the window and whether any query unloaded data. ACCESS_HISTORY needs Enterprise edition, so Standard accounts work from QUERY_HISTORY alone.
- Check shares and stages. Look for new shares, new consumer accounts or new external stages created during the window.
- Notify. Bring in legal, privacy and leadership early, then report to CISA or your regulator where rules require it.
For step 4, the query below lists every base object a suspect user’s queries read over the past 30 days. Allow for some delay, since the ACCESS_HISTORY view can lag by up to three hours.
SELECT ah.query_id,
       ah.query_start_time,
       obj.value:"objectName"::STRING AS object_name
FROM SNOWFLAKE.ACCOUNT_USAGE.ACCESS_HISTORY ah,
     LATERAL FLATTEN(input => ah.base_objects_accessed) obj
WHERE ah.user_name = 'SVC_NIGHTLY_ETL'
  AND ah.query_start_time > DATEADD(day, -30, CURRENT_TIMESTAMP())
ORDER BY ah.query_start_time DESC;
Dedicated posture tools, often sold as DSPM or SSPM products, can add continuous monitoring across Snowflake and other SaaS platforms. They support these steps rather than replace them. Our roundup of data governance tools covers the catalog and policy side of that market.
Lessons From the 2024 Snowflake Customer Account Breaches
The 2024 campaign is the clearest lesson in Snowflake security, because the failures were so ordinary. Mandiant tracked the attacker as UNC5537. The group used stolen customer credentials to sign in, take data and then extort the victims.
Public warnings followed soon after. On June 3, 2024, CISA published an alert titled Snowflake Recommends Customers Take Steps to Prevent Unauthorized Access. It urged customers to hunt for malicious activity and then report findings to CISA.
Mandiant’s write-up adds one detail the opening story only hinted at. In several cases the infostealer infection started on contractor systems that were also used for gaming and pirated software downloads. Your attack surface therefore includes every machine where someone saved a Snowflake password. That is why each fix in the table below sits on the Snowflake side.
Table 7: Each 2024 gap and the control that closes it
| Gap Mandiant found | Control that closes it |
|---|---|
| No MFA on the affected accounts | SSO with MFA for people, as well as key pairs, OAuth or workload identity for services |
| Credentials not rotated, in some cases for four years | Service users without passwords, together with token expiry and key rotation |
| No network allow lists | An account network policy, or private connectivity when workloads are sensitive |
| Credentials stolen from unrelated machines | Credential monitoring, together with alerts on abnormal access attempts |
The real lesson is about concentration. A cloud data platform holds so much value in one place that one weak login can expose all of it. Every control in this guide exists to make sure a single stolen secret is never enough.
Snowflake Compliance: What Snowflake Holds and What You Still Prove
Snowflake’s certifications cover the platform, not your use of it. For example, an auditor will accept Snowflake’s SOC 2 report for the service itself. You still have to show how your own account controls access, protects sensitive data and keeps logs.
Snowflake’s compliance documentation lists a long set of attestations. These include SOC 1, SOC 2, ISO 27001, 27017 and 27018, PCI DSS and HITRUST CSF. Public sector attestations such as FedRAMP Moderate and High, DoD IL5, CJIS, IRAP, ITAR and TX-RAMP are also on the list.
Table 8: What Snowflake’s certifications cover and what you still own
| Certification | What it covers | Your obligation |
|---|---|---|
| SOC 1 and SOC 2 | Snowflake’s controls over its own service | Show your access reviews and change control, as well as monitoring |
| ISO 27001, 27017 and 27018 | Snowflake’s security management and cloud privacy practices | Map your account controls to your own security program |
| PCI DSS | Snowflake as a service provider for card data | Restrict and mask cardholder data in your account |
| HITRUST CSF | Healthcare security controls on the platform | Use Business Critical and sign a BAA before storing PHI |
| FedRAMP Moderate and High | US government cloud authorizations | Deploy in an authorized environment, then meet agency controls |
| DoD IL5 | Defense workloads at Impact Level 5 | Use AWS GovCloud US-West, since the authorization covers that region |
Most of the obligation column comes from an enterprise data governance program rather than from Snowflake settings alone. Access reviews, data owners and retention rules are business decisions first.
Two sectors need extra care, particularly around editions and regions. Healthcare teams can store protected health information under HIPAA only on Business Critical edition or higher, with a signed business associate agreement. Defense teams should also note that Snowflake’s DoD IL5 provisional authorization covers AWS GovCloud US-West only.
Which Security Controls Need Which Snowflake Edition
Snowflake sells security in tiers, so the edition you buy sets a ceiling on the controls you can use. The basics work everywhere, but policy-based data protection and customer-held keys do not.
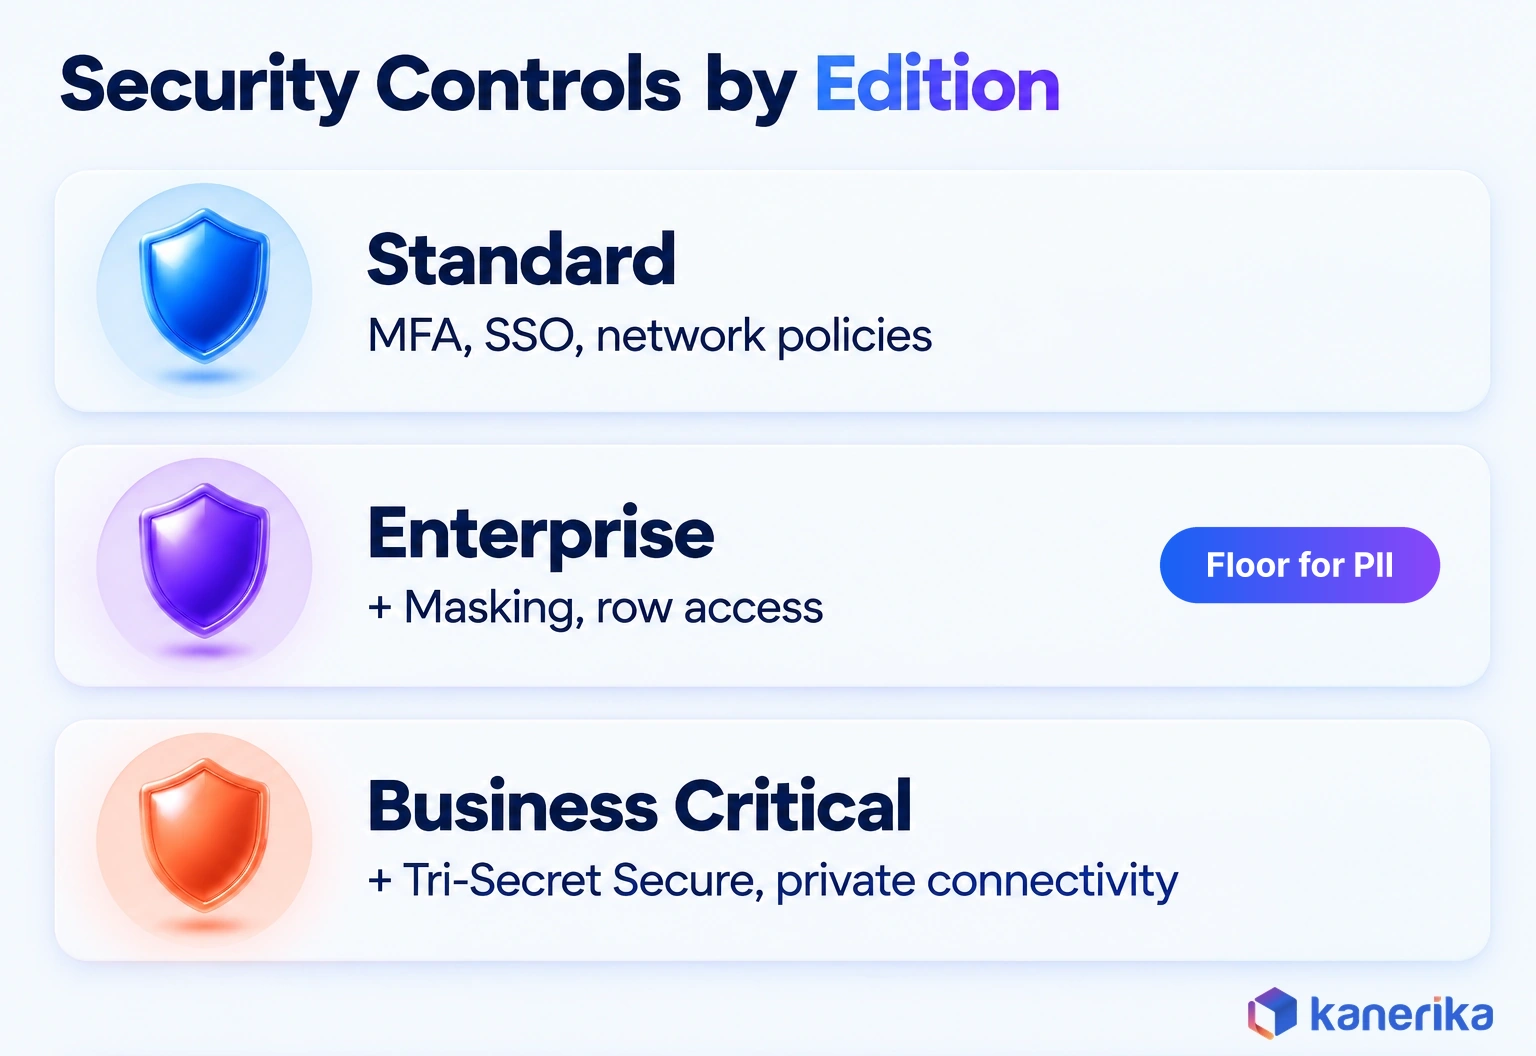
Snowflake’s edition comparison draws three clear lines. Standard covers encryption, MFA, SSO, network policies and role-based access. Enterprise then adds masking, row access policies, periodic rekeying and Time Travel of up to 90 days. Business Critical also adds Tri-Secret Secure, private connectivity and support for PHI under a BAA.
Table 9: Security controls by Snowflake edition
| Edition | Security controls it adds | When to choose it |
|---|---|---|
| Standard | Encryption, SSO, MFA, key pairs, network policies and role-based access | When no data needs masking or row-level filtering |
| Enterprise | Masking and row access policies, ACCESS_HISTORY auditing, periodic rekeying and Time Travel up to 90 days | Once you hold PII or other data some users should not see |
| Business Critical | Tri-Secret Secure, private connectivity and PHI support under a signed BAA | When a regulator or contract demands customer-held keys or private networking |
For most companies holding customer data, Enterprise is the realistic floor, because masking and row access are where data-level protection lives. Business Critical makes sense when a regulator, a contract or a specific data class demands it. Credit prices also rise with each edition, so the gap is real, as our guide to Snowflake cost optimization shows. Buying it for features nobody configures only raises the bill.
A 30/60/90-Day Snowflake Security Hardening Plan
Snowflake security best practices are easier to apply as a sequence than as a loose list. The plan below orders the work so each phase builds on the last, and each step names an owner and a done-when check.
The first 30 days close the gaps attackers used in 2024, such as missing MFA. Days 31 to 60 shrink what any one login can reach, while days 61 to 90 protect the data itself and set up monitoring. Treat the timing as a template, since a small account may finish sooner and a large one may need two passes.
For a new account still loading data, fold the first 30 days into your data migration checklist. That way the controls are live before production data arrives.
Days 1 to 30: Close the Sign-In Gaps
- Baseline the account (security lead). Enable CIS Benchmarks in Trust Center next to Security Essentials, and count it done when every finding has an owner.
- Enforce MFA for people (identity team). Move users to SSO and set an authentication policy, then count it done when LOGIN_HISTORY shows no password-only human sign-ins for seven days.
- Set an account network policy (platform team). Allow office, VPN and pipeline ranges, and count it done when a test login from outside those ranges fails.
- Inventory service users (data engineering). List every LEGACY_SERVICE user and its owner, and count it done when each one has a migration date.
Days 31 to 60: Shrink What Each Login Can Reach
- Migrate service users (data engineering). Move each one to TYPE = SERVICE with a key pair, OAuth or workload identity, and stop when no LEGACY_SERVICE users remain.
- Redesign roles (platform team). Split access and functional roles and cut ACCOUNTADMIN to named holders, finishing when no user has ACCOUNTADMIN as a default role.
- Convert sensitive schemas to managed access (platform team). The step is done when object owners can no longer grant access on their own.
- Set up the break-glass account (security lead). It counts as done once it has been tested and its credentials are stored offline.
Days 61 to 90: Protect the Data and Watch It
- Tag and mask sensitive columns (data governance). Tag PII and attach masking policies to the tags, finishing when an unprivileged test query returns masked values.
- Add row access policies where needed (data governance). The step is done when regional or tenant users see only their own rows.
- Schedule alert queries (security operations). Run the login and grant checks daily, and count it done when an alert reaches a named person within one day.
- Review shares and rehearse the runbook (security lead). Finish when every share has a business owner and the team has practiced the first-hour steps once.
The plan also works best inside a wider data governance framework. That framework supplies the data owners and classification rules that masking and row access depend on.
Checklist
Data Governance Checklist
Set up the data owners, classification rules and policies that masking, row access and access reviews depend on, step by step.
Get the Checklist →Common Snowflake Security Mistakes and How to Fix Them
The mistakes below are ordinary, which is exactly why they survive audits. Each one is either a default left alone or a shortcut that outlived its purpose.
Consider a team that created one shared login for a dashboard tool during a proof of concept. Two years later, that login has a password, a powerful role and a dozen tools using it. Nobody wants to touch it, because nobody knows what would break.
That is how most of these problems age. The fixes are rarely hard, but each one needs an owner and a date. Most also appear in our list of data security best practices, since none of them is unique to Snowflake.
Table 10: Common Snowflake security mistakes and their fixes
| Mistake | Why it hurts | Fix |
|---|---|---|
| Password-only service users | They cannot use MFA, so a stolen password works from anywhere | TYPE = SERVICE with key pairs, OAuth or workload identity |
| No account network policy | Any valid credential works from any IP address | An account policy first, then tighter user-level policies |
| ACCOUNTADMIN as a default role | Every session runs with full power | A few named admins with MFA, while daily work uses lower roles |
| Ad hoc grants to many roles | Nobody can explain who has access or why | Access and functional roles, reviewed every quarter |
| Shared logins for BI tools | One leaked secret exposes every dashboard’s data | One service user per tool with a read-only role |
| Access tokens with maximum lifetimes | Long-lived secrets linger in scripts and laptops | Shorter expiry set through an authentication policy |
| Sharing base tables | Consumers see columns you never meant to share | Secure views, as well as a quarterly consumer review |
| Logs that nobody reads | Intrusions surface weeks later, or from outsiders | Scheduled LOGIN_HISTORY and grant alerts with named owners |
How Kanerika Secures Snowflake Environments
Kanerika is a Snowflake Select Tier Partner, a status announced in June 2026. Our Snowflake consulting team runs hardening engagements in the same order as this guide, so the steps above map directly to the work.
An engagement starts with a baseline before any change is made. We run Trust Center with the CIS Benchmarks package, together with a review of LOGIN_HISTORY and existing grants. That shows exactly where passwords, broad roles and open network paths sit.
The build work follows once the baseline is agreed. We move service users off passwords onto key pairs, OAuth or workload identity, and redesign roles into access and functional layers. Network policies come next, then tag-based masking on sensitive columns. Finally, the hand-off includes scheduled alert queries, a first-hour incident runbook and a quarterly review routine for your team.
Security monitoring and compliance reporting are work we have delivered before. For SeaLink, Australia’s largest integrated transport operator, Kanerika built analytics on Incorta that cut breach identification time by 47%. Compliance adherence also improved by 32%, and decision-making time fell by 44%. That project ran on Incorta rather than Snowflake, yet the same habit of measurable detection carries into every Snowflake engagement.
Kanerika Service
Snowflake Services From Kanerika
Kanerika, a Snowflake Select Tier Partner, hardens Snowflake accounts from sign-in and roles to network policies, masking and monitoring.
Explore Snowflake ServicesWrapping Up
Snowflake gives every account a strong floor, with encryption, malicious IP blocking and a default security scanner. But the controls that would have stopped the 2024 attacks sit above that floor, and they are yours to set. Start with MFA, password-free service users and a network policy, then shrink roles, mask sensitive columns and watch the logs. Snowflake security in 2026 comes down to configuring access, encryption and network controls so that one stolen password is never enough.
Frequently Asked Questions
What is Snowflake security?
Snowflake security is the set of controls that protect a Snowflake account and its data. Snowflake handles encryption, malicious IP blocking and leaked password checks by default. Customers configure the rest. That includes sign-in methods, network policies, roles, masking and row access policies, and monitoring through account usage views and Trust Center scanners.
Is Snowflake secure by default?
Partly. Snowflake encrypts all data at rest and in transit, blocks known malicious IP addresses and runs the Security Essentials scanner by default. It does not decide who may sign in, from where, or what each user can see. Those controls are your responsibility under a shared model, and the 2024 breaches happened where customers left them unset.
How do you prevent data exfiltration from Snowflake?
Layer several controls. Require MFA or key-based sign-in, and limit connections with network policies or private connectivity. Give each role only the data it needs, and mask sensitive columns. Share secure views instead of base tables. Then alert on unusual query volumes, unloads to external stages and new shares, so any attempt is spotted quickly.
Does Snowflake support HIPAA, PCI DSS, and FedRAMP?
Yes. Snowflake’s compliance documentation lists PCI DSS, HITRUST CSF, FedRAMP Moderate and High, and DoD IL5, among others. Storing protected health information under HIPAA requires Business Critical edition or higher and a signed business associate agreement. These attestations cover the platform only. You still need to prove your own access, masking and logging controls to auditors.
What is Trust Center in Snowflake?
Trust Center is Snowflake’s built-in security posture tool. It runs scanner packages against your account and lists findings to fix. Security Essentials runs by default and checks for missing MFA and missing network policies. The CIS Benchmarks, Threat Intelligence, AI Security and Data Security packages are optional. Enabled scanners can add cost, so turn them on deliberately.
Which Snowflake edition do you need for advanced security features?
It depends on the control. Standard covers encryption, SSO, MFA, network policies and roles. Enterprise adds masking, row access policies, periodic rekeying and longer Time Travel, which makes it the practical floor for sensitive data. Business Critical adds Tri-Secret Secure, private connectivity and PHI support, so choose it when regulation or contracts demand those controls.
What caused the 2024 Snowflake breaches?
Stolen customer credentials caused them. Mandiant tracked the attacker as UNC5537 and found that most passwords came from infostealer malware on unrelated machines. The affected accounts had no MFA, credentials that had not been rotated and no network allow lists. Mandiant found no evidence of a breach of Snowflake’s own enterprise environment. About 165 organizations were notified.
Does Snowflake require MFA in 2026?
Yes, in stages. Snowflake’s published schedule made MFA mandatory for Snowsight users between September 2025 and January 2026. Strong authentication then applied to new human users from May to July 2026, and to all users, including service users, from August to October 2026. These windows are Snowflake estimates, so confirm details on its MFA rollout page.
How do service accounts authenticate to Snowflake without passwords?
Set the account to the SERVICE user type, which cannot use a password. Then choose a method that fits the workload. Key pairs suit scheduled jobs, OAuth suits BI tools, and programmatic access tokens suit tools that need a secret string. Workload identity federation is the preferred option for workloads that run inside a cloud provider.
How does Snowflake handle encryption?
Snowflake encrypts all data at rest and in transit in every edition. It uses strong AES encryption with a hierarchical key model rooted in a cloud provider hardware security module, and it rotates keys automatically. Enterprise adds periodic rekeying. Business Critical adds Tri-Secret Secure, where your own key joins Snowflake’s key, and revoking it blocks decryption.
What is the difference between a Snowflake authentication policy and a network policy?
An authentication policy controls how a user signs in. It sets the allowed methods and clients, such as requiring MFA or allowing only key pairs. A network policy controls where a connection may come from, using allowed and blocked network rules. Most accounts need both, because a valid sign-in from an unknown network should still fail.
How does role-based access control work in Snowflake?
Snowflake grants privileges on objects to roles, then grants those roles to users or to other roles. A good design uses access roles that hold object privileges and functional roles that match job duties. Keep ACCOUNTADMIN to a few named people with MFA. Use managed access schemas and future grants so access stays consistent as new tables arrive.
How do masking policies and row access policies work in Snowflake?
A masking policy is a rule on a column. At query time it returns the real value or a masked one, based on the user’s role. A row access policy filters which rows a role can see, such as a single sales region. Both can attach through tags to cover many columns, and both need Enterprise edition or higher.
How do you audit user activity in Snowflake?
Query the views in the SNOWFLAKE.ACCOUNT_USAGE schema. LOGIN_HISTORY shows every sign-in attempt and its authentication factors. QUERY_HISTORY shows what ran, and ACCESS_HISTORY (Enterprise edition) shows which objects each query read or changed. Schedule checks for password-only logins, unusual IP addresses and new admin grants, and route each alert to a named owner who reviews it.