TL;DR
Compliance automation monitors controls, collects evidence, maps one control to many frameworks and routes fixes to named owners. It pays off first on repetitive, evidence-heavy controls, so start there and keep judgment calls with people. Buy a GRC platform when certifications such as SOC 2 and ISO/IEC 27001 drive the work. Extend Microsoft Purview or Databricks Unity Catalog when the risk sits in your data estate, and build custom checks only for gaps no product covers. Budget for integration work and control redesign as well as licenses. Keep a person reviewing automated evidence, because a passing test on the wrong control gives false assurance.
Key Takeaways
- Compliance automation takes over four repetitive jobs, so teams stop monitoring controls, collecting evidence, mapping requirements and routing fixes by hand.
- Automate high-volume, evidence-heavy controls first, such as access reviews, configuration checks, training records and offboarding.
- Control mapping lets one tested control serve SOC 2, ISO/IEC 27001 and HIPAA at the same time.
- Data platforms carry much of the exposure, so access, retention, lineage and sensitivity labels belong in scope.
- Licenses are only one cost, since integration, control redesign, change management and run cost also belong in the budget.
- Guard against false assurance with evidence sampling and stale-evidence alerts, and agree on formats with auditors before the pilot.
Why Compliance Evidence Is the Real Bottleneck
The Audit Request That Arrived Before the Evidence
Picture a mid-size bank three weeks before its annual audit. The auditor sends a short request. Show twelve months of quarterly access reviews for every system that holds customer data.
The evidence exists, in a sense, but it sits in six systems. Some reviews live in a ticketing tool, others in spreadsheets, and two in email threads that only one manager can find.
The compliance team spends the next three weeks taking screenshots, chasing sign-offs and rebuilding a trail. Nobody did anything wrong. The process simply produced evidence once a year instead of every day.
That gap between doing a control and proving it is what compliance automation closes. This guide covers what it does, what to automate first, whether to build or buy, what it costs and where it fails.
What Is Compliance Automation?
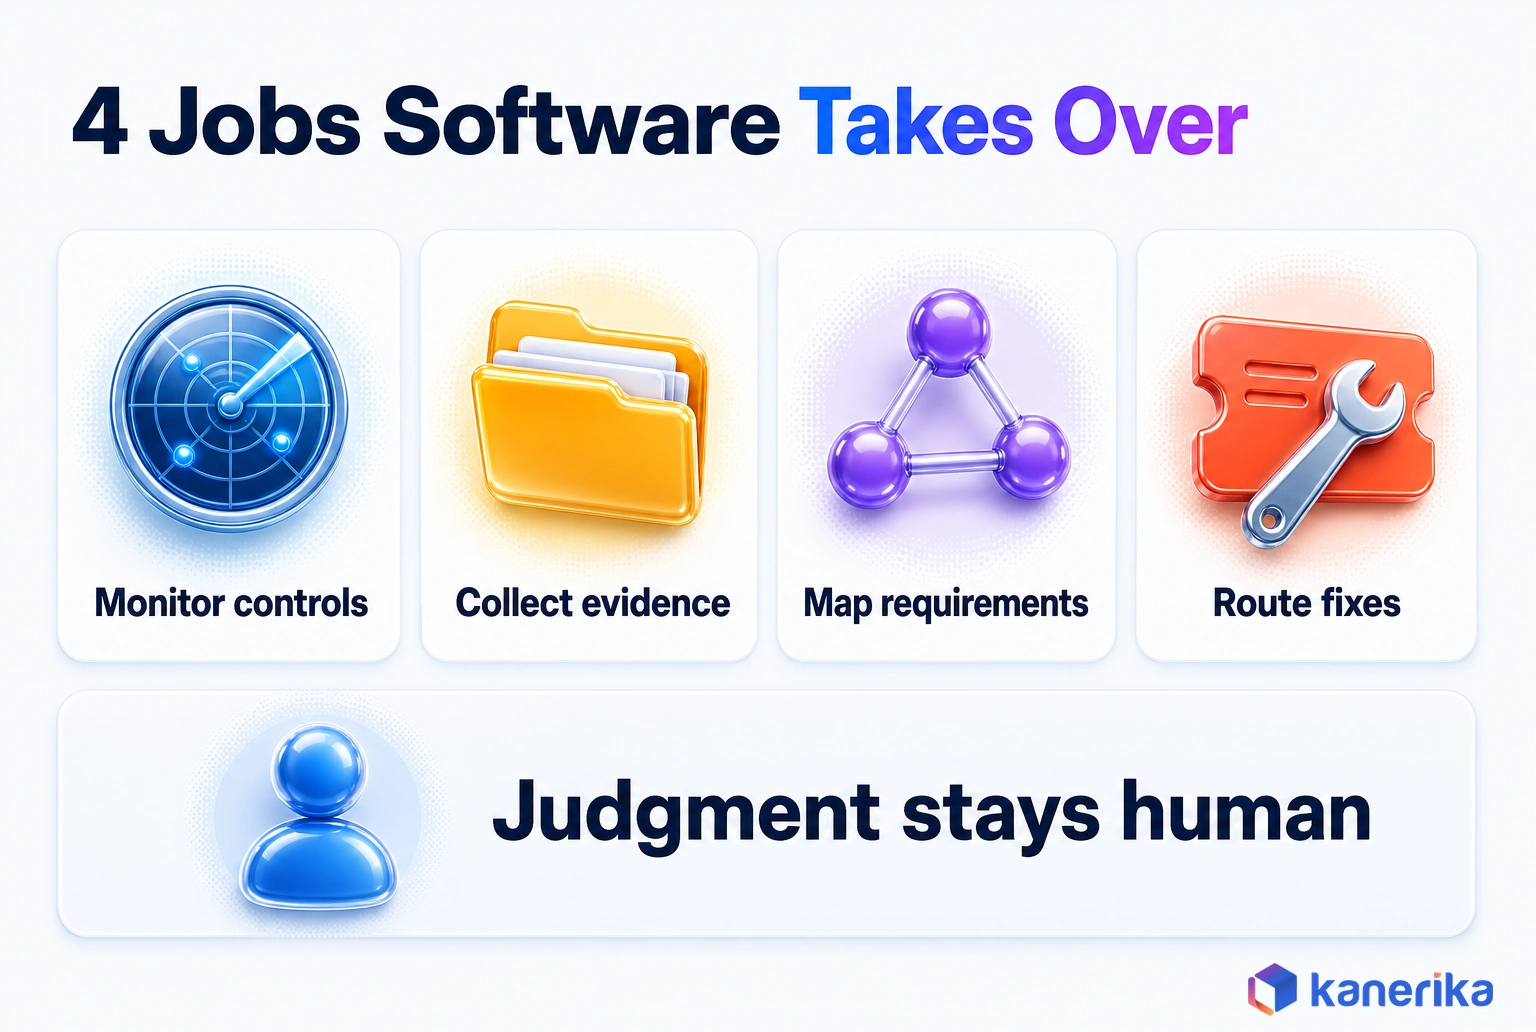
Compliance automation is the use of software to do the repetitive work of staying compliant, while people keep the judgment calls. It does four jobs in practice, and each one replaces a task that used to happen by hand once a quarter.
- Monitor controls. Scheduled checks test whether a control still works, such as whether multi-factor authentication is on for every admin account.
- Collect evidence. Connectors pull logs, configurations and sign-offs into one record, so each item carries a timestamp and a source.
- Map requirements. One internal control is linked to every framework clause it satisfies, so it is tested once and reported many times.
- Route remediation. When a check fails, a ticket goes to a named owner with a due date, and closing it creates fresh evidence.
Go back to the access review in the bank example. Done by hand, a manager exports a user list, marks it up and then emails it back to compliance.
With automation, the platform pulls the list from the identity system and sends it to the manager in a workflow. After the manager signs, it stores the result next to the original export. The control has not changed, yet the proof now builds itself.
Compliance automation is commonly used for data privacy compliance, such as GDPR or CCPA, as well as healthcare regulations like HIPAA, financial requirements such as SOX or AML, and internal audit controls.
The method stays the same across those areas. What changes from one regulation to the next is the rule set that the checks run against, as well as the owners who sign off.
Datasheet
Elevate Data Governance, Compliance and Security of Your Organization
See how Kanerika’s governance stack classifies, protects and monitors data across your estate, so compliance evidence comes from the platform instead of spreadsheets.
View the Datasheet →Compliance Automation vs GRC vs Continuous Control Monitoring
Three terms get mixed up on vendor pages, and the difference matters when you write a requirements list. GRC is the broad management system for governance, risk and compliance. By comparison, continuous control monitoring is a narrow technique that tests technical controls on a schedule.
NIST set out the idea behind continuous monitoring in SP 800-137, its guide to information security continuous monitoring. Automated compliance sits between the two, since it uses monitoring results as one input and then feeds its findings into the GRC record.
| Term | Scope | Main output | Typical users |
|---|---|---|---|
| GRC platform | Policies, risk register, audits and vendor risk | Risk records, compliance records and board reporting | Risk, compliance and audit teams |
| Compliance automation | Control testing, evidence, framework mapping and remediation | Audit-ready evidence and live control status | Compliance, IT and security owners |
| Continuous control monitoring | Automated tests on specific technical controls | Pass or fail results, with alerts when a test fails | Security operations and IT |
Many firms run all three side by side. The GRC platform holds the record, while monitoring tools watch the infrastructure. The automation layer then connects both to the evidence an auditor will ask for.
Why Manual Compliance Breaks at Enterprise Scale
Manual compliance works for a small firm with one framework and a handful of systems. It breaks when systems, rules and auditors multiply faster than the team does. The failure is quiet at first. It shows up as late evidence, missed reviews and repeat findings long before anyone calls it a breakdown.
Regulators leave little doubt about the cost when controls fail. On October 10, 2024, FinCEN assessed a record $1.3 billion penalty against TD Bank for violations of the Bank Secrecy Act.
In the UK, the FCA fined Barclays £42 million on July 16, 2025, for poor handling of financial crime risks. The regulator noted that one simple check of the Financial Services Register would have shown a client was not permitted to hold client money. A lookup like that is easy to automate, because it is the same check every time.
Case Study
60% Less Manual Compliance Work with AI
For a regulatory compliance solutions provider serving financial institutions, Kanerika built an AI compliance platform that automates requirement mapping, controls monitoring and audit traceability, delivering 40% faster regulatory response and 5X better audit traceability.
Read the Case Study →Beyond enforcement, four forces push manual programs past their limits.
- Framework overlap. A firm under SOC 2, ISO/IEC 27001 and HIPAA tests many of the same controls three times unless they are mapped once. Privacy-focused programs may add ISO 27701 certification to that map.
- SaaS sprawl. Every new application adds accounts, logs and settings that someone then has to review, which is why SaaS security belongs in compliance scope.
- Evidence decay. A screenshot proves a setting on one day. By the time the next audit arrives, it proves very little.
- Regulatory change. Rules such as DORA and the EU AI Act add obligations faster than a spreadsheet tracker can absorb them.
Risk teams feel the same squeeze, which is why many pair this work with AI in risk management to spot exposures earlier. The common thread is volume. Once the checks outnumber the people, automating them stops being optional.
Benefits of Compliance Automation
The benefits of compliance automation come down to proof, speed and consistency. Saved audit-prep hours are the most visible gain, yet rarely the most important.
Proof improves first, because a daily test leaves a dated record instead of a screenshot from one afternoon. Speed follows, since a failed check reaches its owner the same day rather than at the next quarterly review. Adding a framework then costs mapping time instead of a new round of testing.
Consistency is the quiet gain, since every auditor reads from the same record and conflicting answers stop turning into findings. Data governance automation works the same way, with the platform applying policies instead of people.
How Compliance Automation Works: From Requirement to Audit Evidence
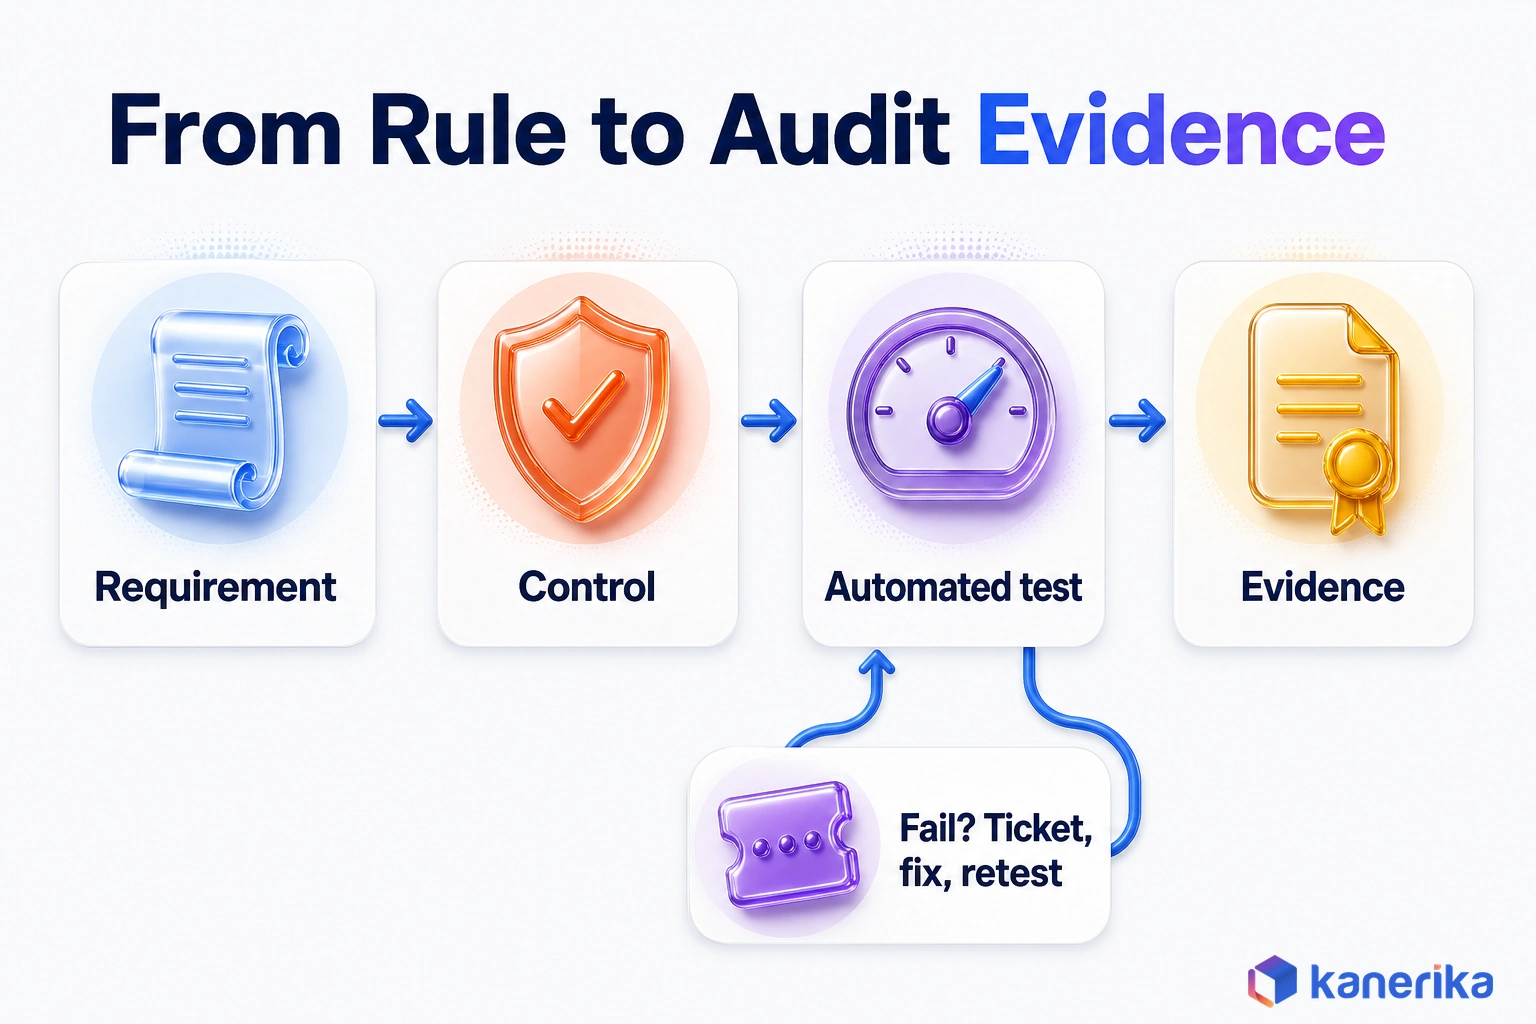
Under the hood, most platforms follow the same chain. A requirement becomes a control, and the control becomes a test. The test then produces evidence an auditor can trace back to its source.
Each link in that chain can be automated to a different degree. For that reason, it helps to see the six stages separately, along with where the work moves from people to software.
- Requirement intake. Frameworks, regulations and policies are loaded as requirements, and rule changes arrive as updates that flag the controls they touch.
- Control mapping. Each requirement links to an internal control with an owner, so one control can satisfy several frameworks.
- System connectors. APIs connect the platform to identity, cloud, HR, ticketing and data systems, since that is where evidence lives.
- Automated tests and evidence. Scheduled tests check each control and then store the result with a timestamp, source and version.
- Remediation tickets. When a test fails, a ticket goes to the control owner, and the fix is retested before the ticket closes.
- Audit-ready reporting. Dashboards show control status, evidence and exceptions per framework, while auditors get read-only access.
Requirement intake is the stage teams neglect most easily. A framework gets loaded once and is never revisited, so a rule change only surfaces at the next audit. A healthy setup instead treats regulatory change as a standing feed that updates the control map.
Worked Example: One Offboarding Control
To see the chain at work, take one control. Say the rule is that former employees lose access within one business day, and the control is an offboarding check.
Each morning, a connector compares the HR termination list with active accounts. Any match then opens a ticket for the system owner. The daily result, clean or not, also becomes the evidence the auditor reviews.
Run that control through the six stages above and the chain becomes concrete. Intake turns the one-business-day rule into a requirement. Mapping then links it to SOC 2, ISO/IEC 27001 and HIPAA, since all three expect leavers to lose access.
The connectors read the HR system and the identity provider, and the test is the daily match. Each hit becomes a ticket that the owner fixes before the account is retested. At audit time, the report shows what the auditor samples: the date, the two lists compared, any exceptions and their ticket IDs.
What You Can Automate and What Stays Human
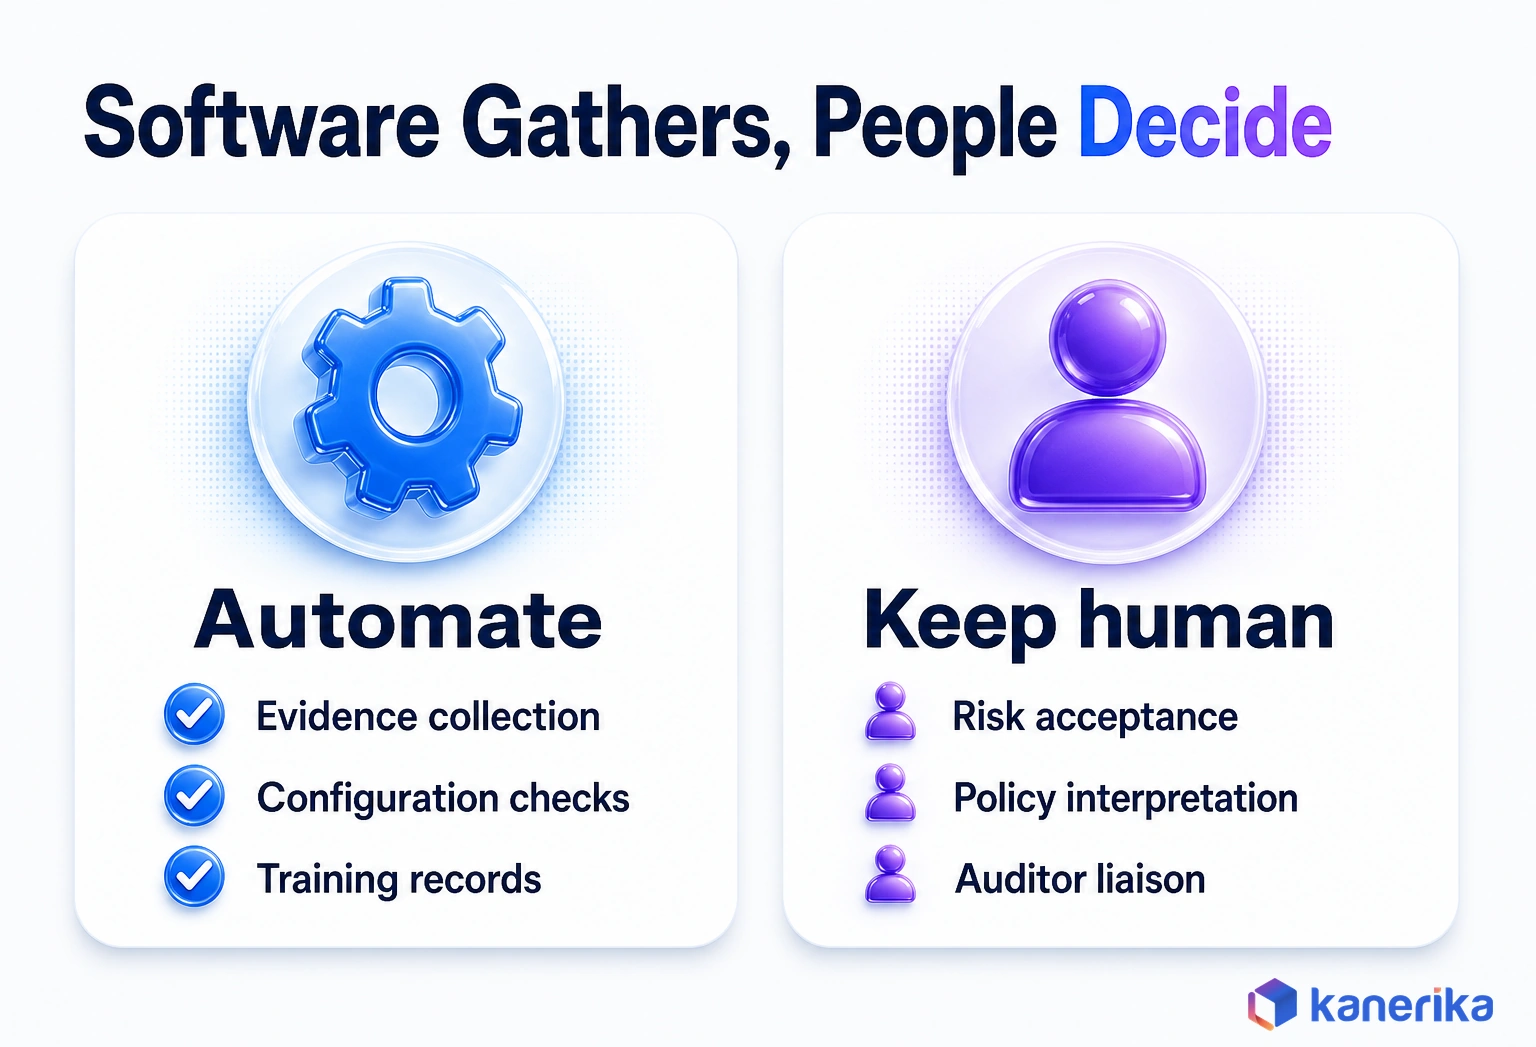
Software is good at work that is frequent, rule-based and easy to verify. It is poor at decisions that weigh risk against business value. Drawing that line early stops teams from automating the wrong things and from trusting the output too much.
Think of it as a division of labor. The platform gathers, tests and flags, while people decide what a finding means. They also judge whether a risk is acceptable and how to explain an exception to an auditor.
| Activity | Automate? | Human role |
|---|---|---|
| Evidence collection, such as logs, configurations and exports | Yes, once connectors are live | Spot-check samples once a quarter |
| Access reviews | Mostly, since list pulls, routing and reminders are routine | Manager confirms each person still needs access |
| Configuration checks, such as encryption, MFA and logging | Yes, fully | Set the baseline, then approve exceptions |
| Policy acknowledgment and training records | Yes, fully | Decide who must take which training |
| Vendor risk questionnaires | Partly, for sending, tracking and scoring | Judge the answers when a vendor is critical |
| Risk acceptance | No | Accountable executive signs off |
| Policy interpretation | No, although AI can draft | Compliance lead decides what a rule means for the firm |
| Auditor liaison | No | Compliance lead explains context and exceptions |
The pattern is simple. Work driven by volume and repetition goes to the machine, while work that depends on context, accountability or negotiation stays with people. For most teams that means full automation for evidence and partial automation for reviews.
Frameworks and Regulations Compliance Automation Supports
Framework templates are a standard feature, although the depth of coverage varies. Some frameworks are mostly technical controls that tests can check. Others lean on documents, governance and judgment, so software can track them but not decide them.
| Framework | Who it applies to | What automation covers |
|---|---|---|
| SOC 2 | Service organizations that handle customer data, under an AICPA attestation | Access, change management, logging and vendor evidence |
| ISO/IEC 27001 | Organizations certifying an information security management system | Control evidence, risk register links and internal audit tracking |
| HIPAA | US health plans, providers, clearinghouses and their business associates | Access logs, encryption checks and training records |
| PCI DSS | Organizations that store, process or transmit payment card data | Configuration scans, access control and log retention |
| SOX | US-listed public companies, for financial reporting controls | IT general controls, segregation of duties and change approvals |
| GDPR and CCPA | Organizations that handle personal data of EU residents or California consumers | Data inventories, privacy requests, retention and consent records |
| NIST CSF 2.0 | Any organization that chooses to adopt it | Mapping controls to six functions, including the Govern function added in February 2024 |
| DORA | EU banks, insurers, investment firms and other financial entities | ICT risk controls, incident records and third-party registers |
| EU AI Act | Providers and deployers of AI systems in the EU | AI system inventory, risk classification and documentation tracking |
Dates to Know for CSF 2.0, DORA and the EU AI Act
Three rows carry dates worth knowing. NIST released CSF 2.0 on February 26, 2024, and added Govern as a sixth function. DORA has applied since January 17, 2025, to banks, insurers and investment firms in the EU.
The EU AI Act entered into force on August 1, 2024, and has applied since August 2, 2026, with exceptions. After the AI Omnibus, rules for the high-risk systems in Annex III start on December 2, 2027. What the Act asks of each AI system is covered in our guide to AI compliance.
One Control, Many Frameworks: Why Control Mapping Matters
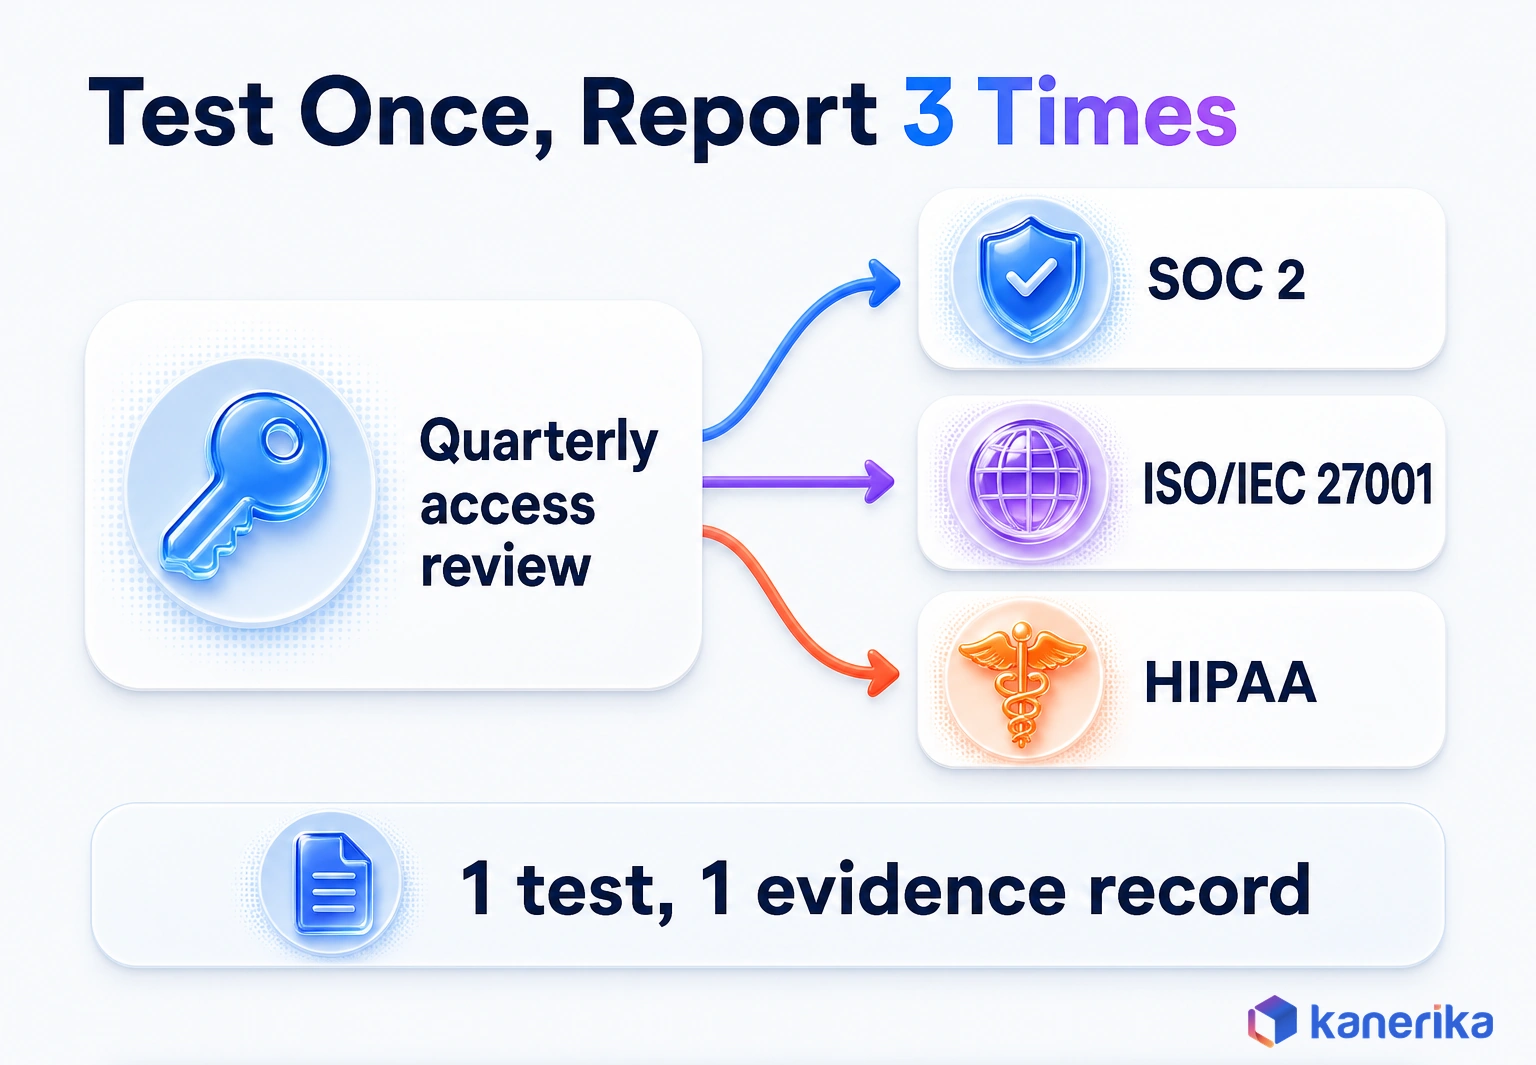
Control mapping is the reason one platform can serve several frameworks at once. Instead of testing a control for each framework, you test it once and then point every framework to the same evidence.
Take a quarterly access review as an example. SOC 2, ISO/IEC 27001 and HIPAA all expect access to sensitive systems to be reviewed and approved. Without mapping, three teams may run three reviews on three schedules.
With mapping, one review produces one evidence record, and each framework report pulls from it. As a result, the saving grows with every framework you add.
Mapping also cuts the risk of conflicting answers, where one audit sees a clean review while another sees a gap. When the auditor for one framework asks a question, the answer is the same one every other auditor gets.
Compliance Automation for Enterprise Data Platforms and AI
In a bank or insurer, the records regulators ask about live in the data platform: customer tables, financial marts and model training sets. Many compliance tools, though, focus on IT systems such as identity, endpoints and cloud accounts.
Six control areas matter most in a data estate. Each can be tested by software, and each also produces evidence an auditor will recognize. Our guide to data governance in banking gives the sector view.
| Control area | What gets automated | Evidence produced |
|---|---|---|
| Access governance | Permission checks and periodic reviews on tables and workspaces | Access logs and signed reviews |
| Retention | Policies that delete or archive records when they reach their limit | Deletion logs per policy |
| Lineage | Capture of how data moves from source to report | Lineage graphs for regulated figures |
| Sensitivity labels | Scanning and labeling of data such as personal and financial records | Label coverage reports |
| Privacy requests | Finding and handling every copy of a person’s data | Request logs with completion dates |
| Model governance | Tracking which data trained which model before approval | Model records and approval history |
Where Purview and Unity Catalog Fit
Platform-native tools already do much of this work. Microsoft Purview Compliance Manager, for example, has pre-built and custom assessments, workflows and step-by-step improvement actions. Which assessments you get depends on your license, so check that before planning.
Its testing settings matter most for evidence. Each improvement action is tested either manually or automatically, and per Microsoft Learn, automatic testing is on by default for eligible actions. Statuses refresh every 24 hours, and each action’s testing history exports to Excel as a dated trail.
Purview’s data loss prevention policies add an automated control that stops sensitive data from leaving approved locations. Every blocked or allowed event is logged, and those logs become evidence too.
On Databricks, Unity Catalog keeps audit logs and lineage for governed data. Per the Databricks system tables docs, system.access.audit holds audit events, and system.access.table_lineage records each read or write on a Unity Catalog table or path. That lineage is evidence in its own right. When an auditor asks where a reported number came from, data lineage answers with a traced graph rather than a manual hunt.
AI adds a second layer. Models that score customers or flag transactions for fraud detection need the same controls as the data behind them. They also need records of testing and approval. Our guide to machine learning governance covers that model side in depth.
Types of Compliance Automation Tools
Tools in this market fall into five categories, and many firms combine two or three. The right mix depends on where your obligations sit. A SaaS company chasing SOC 2, for instance, needs something different from a bank with a large data warehouse.
| Category | Best fit | Limits |
|---|---|---|
| GRC automation platforms | Certifications such as SOC 2 and ISO/IEC 27001, especially at cloud-native firms | Shallow coverage of data platforms and custom systems |
| Platform-native governance (Purview, Unity Catalog, Fabric) | Data estates already on Microsoft or Databricks | Strongest on its own platform, so it needs a GRC layer for full framework reporting |
| Continuous control monitoring and cloud posture tools | Technical controls across cloud accounts | Little help with policies, vendors or people controls |
| Privacy operations tools | Consent, data mapping and privacy requests under GDPR and CCPA | Narrow scope once you step outside privacy |
| RegTech and AML tools | Transaction monitoring, sanctions screening and regulatory reporting in finance | Sector-specific rather than a general control platform |
Platform-native governance is easy to overlook because it is not sold as compliance software. Even so, Microsoft Fabric governance features and Purview already label, track and restrict data in many enterprises. Our roundup of data governance tools compares the main options. Where the goal is masking or removing personal data rather than labeling it, the data anonymization tools roundup sorts options into open-source, enterprise and cloud-native groups.
Kanerika Service
Microsoft Purview Implementation Services
Kanerika sets up Purview Compliance Manager assessments, sensitivity labels and data loss prevention so platform-native controls produce audit-ready evidence.
Explore Purview ServicesProcess automation fills the gaps between tools. Bots and AI steps can gather evidence from systems that lack APIs, and our guide to AI and RPA shows how those pieces fit. Use them sparingly, though, since a screen-reading bot is a weak link in an evidence chain.
Build vs Buy vs Extend an Existing Platform
Once you know the categories, the real choice is how to get there. You can buy a dedicated platform, extend tools you already own or build custom checks. Each path fits a different starting point, so many programs end up mixing them.
| Scenario | Best path | Why |
|---|---|---|
| Startup or SaaS firm needs SOC 2 or ISO/IEC 27001 fast | Buy a GRC automation platform | Templates and connectors cover common controls out of the box |
| Enterprise with Microsoft 365, Fabric or Databricks at its core | Extend Purview or Unity Catalog, then add GRC reporting | Evidence already lives in the platform you pay for |
| Bank or insurer with many legal entities | Buy a GRC platform and also extend data platform controls | Needs multi-entity reporting and deep data controls |
| Controls on in-house or legacy systems | Build targeted checks, then feed results to the GRC record | No product connector exists |
| One framework, few systems | Stay manual with a tracker until scope grows | Tool cost may exceed the effort saved |
Building everything from scratch rarely pays, because custom code turns into a product. You then have to maintain it, document it and defend it to auditors.
Keep custom work for the gaps, and route its output into the same evidence store as everything else. That way the auditor sees one trail, whichever path produced each piece.
What to Check Before You Choose a Platform
Vendor demos tend to look alike, so test every option against the same list. Ask for proof on your own systems rather than a sample tenant.
- Framework coverage. Does it ship the frameworks you need, at the version your auditor uses?
- Integration depth. Do connectors pull real evidence from identity, cloud and data platforms, rather than only confirming that a setting exists?
- Evidence traceability. Is every artifact stored with source, timestamp and version, so an auditor can trace it?
- Auditor access. Can auditors get read-only access to evidence without manual exports?
- Custom controls. Can you add your own controls and tests without paying for vendor services?
- Multi-entity support. Can it report by subsidiary, region or business unit when you need it?
- Regulatory updates. How fast does the vendor update content when a rule changes, and who maps the change?
- Export and lock-in. Can you export controls, mappings and evidence in a usable format if you leave?
Score each option on a simple three-point scale per item. In general, the gaps that matter most are integration depth and evidence traceability, since those decide whether the auditor trusts the output.
What Compliance Automation Costs
Price quotes focus on licenses, but licenses are only one part of the bill. Larger costs often sit in integration and in fixing controls that were never designed to be tested.
Treat the budget as five parts. The split varies from firm to firm, which is why no fixed price range holds across programs. What does hold is that skipping any one part shows up later as delay.
| Cost component | What drives it | How to keep it down |
|---|---|---|
| Licenses | Number of frameworks, entities, users and connectors | Start with the frameworks you are audited on today |
| Integration build | Systems without ready connectors, such as legacy apps | Reuse platform-native controls when they exist |
| Control redesign | Controls written for people that a test cannot check | Rewrite each control with a measurable pass condition |
| Change management | Owner training, new workflows and auditor walkthroughs | Pilot with one team and one framework first |
| Run cost | Connector upkeep, rule changes, evidence reviews and platform admin | Name a platform owner before go-live |
Control redesign is the part teams tend to underestimate. A control that says access is reviewed periodically, for instance, cannot be tested by software.
By contrast, a control that says every admin account is reviewed each quarter and approved by the system owner can be tested. Rewriting a few dozen controls this way takes weeks of compliance time, so it should sit in the plan from the start.
Talk to Kanerika
Scoping a Compliance Automation Program?
Talk to Kanerika about which controls to automate first, what to reuse from your data platform and how to budget integration and control redesign.
Schedule a Demo →Implementation Roadmap: Six Stages With Owners and Exit Criteria
A staged rollout keeps risk low and also proves value early. Each stage below has an owner and an exit criterion, so everyone knows when to move on. Without exit criteria, pilots tend to stall in a permanent half-done state.
| Stage | What happens | Owner | Exit criterion |
|---|---|---|---|
| 1. Assess | Inventory frameworks, controls, systems and current evidence effort | Compliance lead | Baseline hours per audit and a ranked control list |
| 2. Design controls and data architecture | Rewrite controls as testable statements, then map them and choose the evidence store | Compliance lead with an IT architect | Approved control library and mapping |
| 3. Integrate priority controls | Connect the systems behind the top-ranked controls | IT and platform engineers | Evidence flows for priority controls without manual steps |
| 4. Pilot and test effectiveness | Run automated and manual testing side by side for one cycle | Control owners with internal audit | Results match, and internal audit accepts the evidence |
| 5. Expand frameworks and business units | Add frameworks and entities, then the remaining controls | Program manager | Coverage target met for each framework |
| 6. Maintain | Update for rule changes, review exceptions and tune tests | Platform owner | Quarterly review done with no stale evidence |
Stage 4 is the one to protect. Running both methods in parallel for a full cycle shows whether the automated test really measures the control.
It also gives internal audit a chance to object before the external auditor does. Cutting this stage to save a quarter is a fast route to a dashboard nobody trusts.
Checklist
Data Governance Checklist
Use Kanerika’s checklist to confirm ownership, access, retention and lineage are in place before you automate the controls that depend on them.
Get the Checklist →What to Automate First
Start where three things meet. The control is high-risk, it repeats often and it produces a lot of evidence. Those controls save the most hours, and they also carry the most weight in an audit.
- Access reviews. These are frequent, required by nearly every framework and painful to evidence by hand.
- Configuration checks. Encryption, MFA and logging settings can be tested daily without human effort.
- Training and policy records. Completion data is already digital, so it is easy to pull.
- Offboarding. Comparing HR terminations with active accounts closes a gap that auditors look for every year.
Leave policy interpretation, risk acceptance and vendor judgment for later, or for good. Those still need people.
Risks and Common Mistakes
Automation removes old risks, yet it can also add new ones. The biggest is false confidence, where a green dashboard hides a control that no longer works. Each mistake below has a simple guard.
- False assurance. A test may check that a setting exists rather than that it works. Sample evidence by hand once a quarter.
- Stale evidence. A broken connector keeps showing the last good result. Alert on evidence age, not just on failures, much as data observability tools watch pipeline freshness.
- Auditor acceptance. Auditors may reject evidence they cannot trace. Agree on evidence formats with them before the pilot.
- Errors in AI-assisted checks. AI can misread a policy or a contract clause. Keep a reviewer on any AI output that changes a control result.
- Set and forget. Rules change and systems move. Review the control map whenever a framework or system changes.
- Automating a broken process. A flawed review done faster is still flawed. Fix the control before you automate it.
The AI point deserves extra care. Language models are good at reading long policies and drafting control mappings, so they save real hours on both. Our guide to AI contract and policy compliance shows where that helps.
They can also be confidently wrong. Treat their output as a draft until a named person signs off, and then log that sign-off as part of the evidence.
AI Assessment
Is Your Organization Ready for AI-Assisted Compliance?
Take Kanerika’s AI maturity assessment to score your data, governance and processes before AI starts drafting control mappings or reading policies.
Start Your AI Assessment →How to Measure Compliance Automation Success
Measure the outcomes an audit committee cares about rather than tool activity. Five measures cover most programs. Take a baseline during the assess stage, because otherwise there will be nothing to compare against.
| Measure | What it shows | How to track it |
|---|---|---|
| Evidence collection hours per audit | Effort saved | Time logs before and after, per framework |
| Control test coverage | Share of controls tested automatically | Automated controls divided by total controls |
| Time to remediate | Speed of fixing failed controls | Time from ticket open until close |
| Repeat audit findings | Whether fixes hold | Findings that recur across audit cycles |
| Regulatory response time | Speed of acting on new rules | Days from rule publication until controls are mapped |
Expect coverage to rise first and findings to fall later. Fewer repeat findings is the clearest sign the program works, since it means fixes are sticking from one audit to the next.
How Kanerika Helps Enterprises Automate Compliance
Kanerika starts from the data and controls you already have rather than a new tool. We map controls once across your frameworks, then test them where the evidence lives and expand in stages from a pilot.
Our data governance services combine KANGovern, KANGuard and KANComply with Microsoft Purview, Databricks Unity Catalog and Concentric AI. Together they cover access, classification, retention and lineage across the data estate.
For Microsoft estates, our Microsoft Purview practice sets up Compliance Manager assessments, information protection and data loss prevention. For AI systems, our AI governance services extend the same controls to models in production.
One engagement shows the approach at work. A provider of AI-powered regulatory compliance solutions serves financial institutions across several jurisdictions. Its regulatory workflows were fragmented, and manual controls mapping left gaps in audit readiness.
Kanerika built a centralized AI compliance platform that automates requirement mapping, controls monitoring and audit traceability, with dashboards for coverage. According to the compliance oversight case study, the client saw 40% faster regulatory response and 60% less manual compliance work. Audit traceability also improved fivefold.
We hold ISO/IEC 27001, ISO/IEC 27701 and SOC 2. The controls we help clients automate are ones we run every day.
Kanerika Service
Data Governance and Compliance Services
Kanerika combines KANGovern, KANGuard and KANComply with Microsoft Purview and Databricks Unity Catalog to automate access, classification, retention and lineage controls across your data estate.
Explore Data Governance ServicesThe Bottom Line: What to Know Before You Implement Compliance Automation
Compliance automation works when it is aimed at the right controls. Start with high-volume, evidence-heavy checks, keep judgment with people and map each control once across frameworks.
Then choose the path by your starting point. Buy a GRC platform for certification-driven work, extend Purview or Unity Catalog when the risk sits in your data and build only for the gaps. Budget for integration and control redesign before you scale, and run a full pilot cycle.
Before you buy anything, write down the five controls you will automate first, where their evidence lives today and how an auditor will trace it. That list is the real readiness test for compliance automation.
Frequently Asked Questions
What is compliance automation?
Compliance automation is the use of software to handle the repetitive work of staying compliant. It monitors controls, collects evidence, maps requirements across frameworks and sends failed checks to named owners. People still make the judgment calls on risk and policy. Evidence then builds every day, so an audit becomes a review of records that already exist.
How do you automate compliance processes?
Start by listing your frameworks and the controls behind them. Rewrite each control so a test can check it. Connect the platform to the systems that hold evidence, such as identity, cloud and HR tools. Schedule the tests, route failures to owners as tickets and store each result with a timestamp. Pilot one framework before expanding.
How does compliance automation reduce risk and penalties?
It finds failed controls early, often within a day, and routes each one to an owner with a deadline. That shortens the window in which a gap can cause harm. Regulators fine firms for control failures, as FinCEN did with its record $1.3 billion penalty against TD Bank. Continuous testing helps catch those failures sooner.
Which industries benefit most from compliance automation?
Banking, insurance and capital markets benefit heavily because AML, SOX and DORA demand frequent testing. Healthcare gains through HIPAA access and training controls. Software and SaaS firms rely on it for SOC 2 and ISO/IEC 27001. Any company handling personal data at scale gains from automated privacy requests and retention controls.
Is compliance automation suitable for small businesses?
It can be, once the business faces a formal audit or customer security reviews. A startup selling to enterprises often needs SOC 2, and a GRC automation platform covers that quickly. A small firm with one framework and few systems may do fine with a tracker for now. Revisit the choice as systems and frameworks grow.
What is the difference between compliance automation and GRC?
GRC is the broad discipline and system of record for governance, risk and compliance. It holds policies, risk registers, audits and vendor risk. Compliance automation is the engine that tests controls, gathers evidence and routes fixes. Its results feed the GRC record. Many GRC platforms now include automation features, so the two often ship together.
What is continuous control monitoring?
Continuous control monitoring runs automated tests on controls at set intervals, often daily. It checks settings such as encryption, logging and account access, then alerts owners when a test fails. NIST describes the wider practice in Special Publication 800-137 on continuous monitoring. It turns point-in-time audits into an ongoing view of control health.
Can one platform cover SOC 2 and ISO 27001 at the same time?
Yes. Most GRC automation platforms support both frameworks and map shared controls between them. A single access review or change approval can serve as evidence for both. You still need separate audits and reports for each. Mapping saves the duplicated testing and evidence work, which is usually where most of the effort goes.
How much does compliance automation cost?
Cost depends on frameworks, legal entities, users and the number of systems you connect. Licenses are only one part. Budget for integration build, control redesign, change management and ongoing run costs as well. Reusing controls already inside Microsoft Purview or Databricks Unity Catalog can lower integration costs for firms that run those platforms.
Does compliance automation replace compliance officers or auditors?
No. It replaces manual evidence gathering, reminders and routine tests. Compliance officers still interpret rules, accept or reject risks and explain exceptions. External auditors still give the independent opinion a certification or attestation requires. The role shifts toward judgment and oversight as the platform takes over repetitive collection and testing work.
What are the risks of compliance automation?
The main risk is false assurance, where a passing test checks the wrong thing. Broken connectors can show stale results as current. Auditors may reject evidence they cannot trace. AI-assisted checks can misread policies. Teams can also automate a flawed process and make it faster. Sampling, evidence-age alerts and human sign-off reduce each risk.
Will auditors accept automatically collected evidence?
Auditors generally accept automated evidence when they can trace it. Each item should show its source system, collection time and the control it supports. Agree on formats with your auditor before the pilot. Give read-only access where possible. Keep manual sampling in place during the first cycle so the auditor can compare both methods.
How hard is compliance automation to implement, and how long does it take?
Effort depends on how many systems you connect and how testable your controls are. One framework on cloud-native systems can move quickly. A firm with many legal entities and legacy apps takes longer. Integration and control redesign usually set the pace. Plan for one full audit cycle of parallel testing before you rely on the output.
What are the core elements of an effective compliance program?
The HHS Office of Inspector General lists seven elements in its general compliance guidance. They are written policies, compliance leadership and oversight, training, open lines of communication, enforced standards, risk assessment with auditing and monitoring, and corrective action when problems surface. Automation supports several of them, mainly training records, monitoring, auditing and tracking corrective action.
What are the stages of building a compliance program?
Most programs move through six stages. Assess your obligations and current controls first. Then design testable controls and map them across frameworks. Integrate the systems that hold evidence for priority controls. Pilot automated testing next to manual testing for one cycle. Expand to more frameworks and business units, then maintain the program as rules change.
What are the main types of compliance?
Regulatory compliance covers laws such as HIPAA, SOX, GDPR and DORA. Industry compliance covers standards like PCI DSS for payment cards. Security compliance covers frameworks such as SOC 2, ISO/IEC 27001 and NIST CSF 2.0. Internal compliance covers a firm’s own policies and codes of conduct. Many firms manage all four types at once.
What types of automation are used in compliance?
Five types show up most often. Continuous control monitoring tests technical settings on a schedule. Evidence collection connectors pull logs and records from business systems. Workflow automation routes reviews, approvals and remediation tickets. Robotic process automation gathers data from systems without APIs. AI assists with reading policies, drafting control mappings and flagging unusual transactions.
What are examples of compliance automation?
Common examples include quarterly access reviews sent to managers through a workflow. Daily checks confirm that encryption and multi-factor authentication stay switched on. Offboarding checks compare HR termination lists with active accounts. Retention policies delete records on schedule and log each deletion. Privacy request tools find every copy of a person’s data and record when each request closes.
What are the benefits of compliance automation?
Teams spend far less time collecting evidence by hand. Controls are tested continuously, so failures surface in days rather than at the next audit. One tested control can serve several frameworks through mapping. Auditors get traceable records with sources and timestamps. Compliance staff gain time for risk judgment, policy work and talking with regulators.
Can AI do compliance work?
AI can handle parts of compliance work well. It reads long regulations, drafts control mappings, summarizes policy changes and flags unusual transactions for review. It can also be confidently wrong. Treat AI output as a draft until a named person approves it. Log that approval so the review itself becomes part of the audit evidence.