TL;DR
Choose between data governance frameworks by your main pressure: DGI for program design, with DAMA-DMBOK for shared terms, on a first program, DCAM for banks, CDMC for sensitive cloud data and COBIT for IT audit. A data governance framework is the set of policies, roles, decision rights, standards and controls that decides who owns data and what good data means. You can combine frameworks, as long as one primary framework owns the structure and each add-on fills a named gap. A hybrid operating model suits a business with several domains, because standards stay central while domain owners make the daily calls. Build it in 90 days on one domain: assess and name owners, then write and enforce the rules, then measure and plan the next domain. Tools such as Microsoft Purview and Databricks Unity Catalog enforce the framework, but they do not replace named owners and agreed definitions.
Key Takeaways
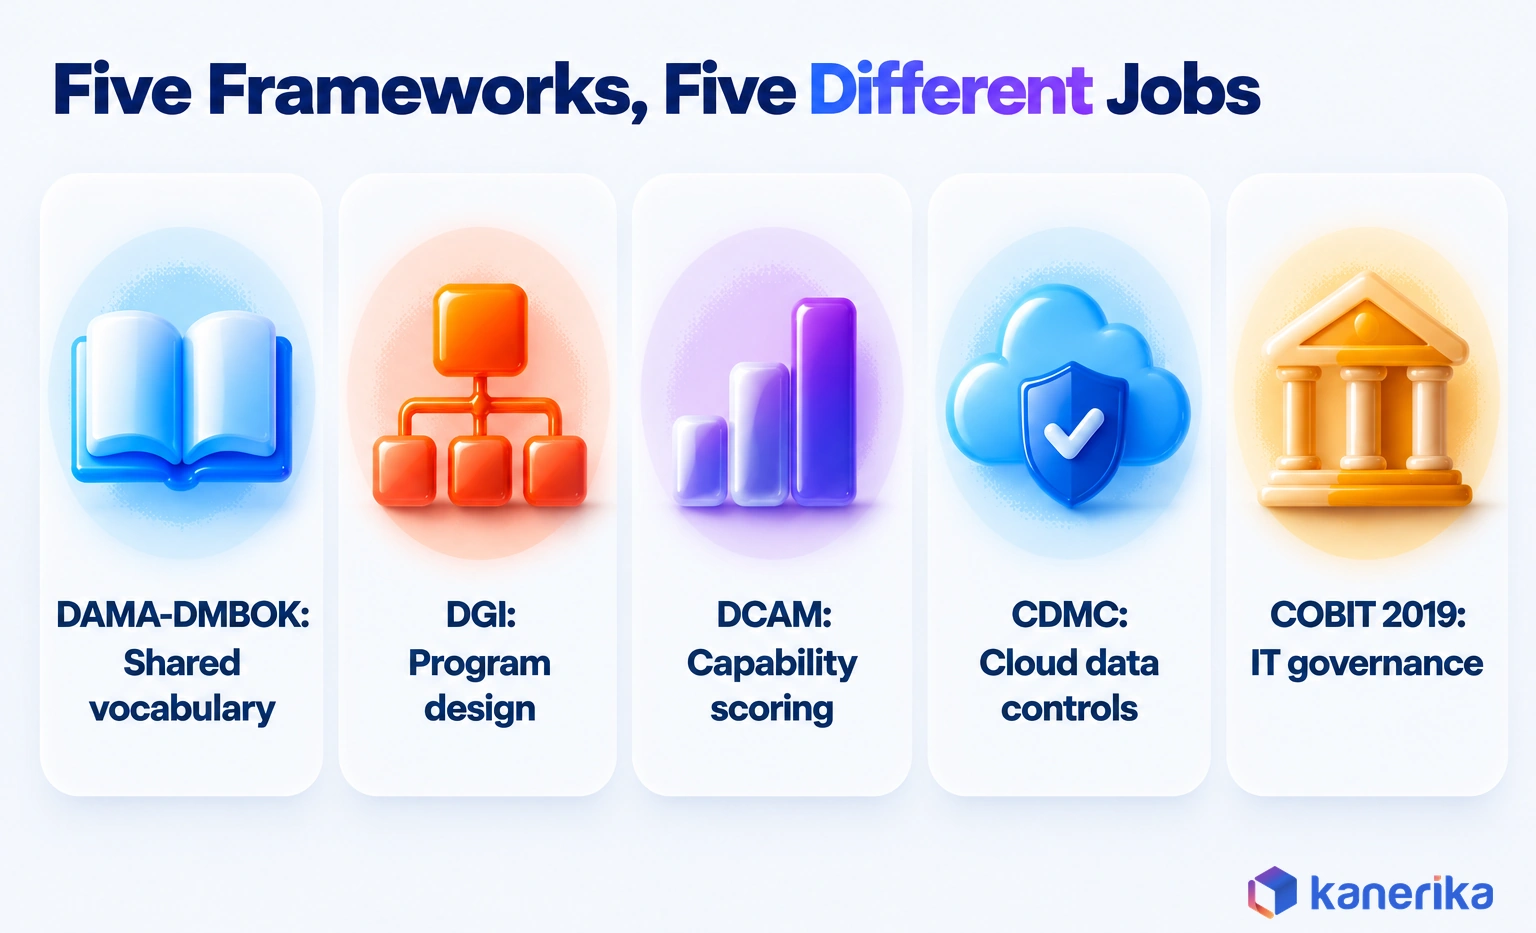
- Data governance frameworks differ by job: DAMA-DMBOK defines vocabulary, DGI designs the program, DCAM scores capability, CDMC sets cloud controls and COBIT governs IT.
- Choose by your main pressure, such as a regulator or a cloud migration, and add a second framework only for a named gap.
- Every framework needs eight working parts, from policies and decision rights to metadata, access control and metrics.
- Start with one domain and a 90-day plan, so every critical data element in it gets a named owner first.
- Track a few KPIs, such as rule pass rate and time to resolve issues, and expand only when the first domain hits its targets.
- Use a hybrid operating model when several domains share KPIs, so each decision has exactly one accountable owner.
Two Dashboards, Two Revenue Numbers, and an Audit Next Month
Picture a Monday leadership meeting at a mid-size distributor. The finance dashboard shows one figure for quarterly revenue. Meanwhile the sales dashboard, built on the same warehouse, shows a number several percent higher, and the auditors arrive next month.
Nobody in the room has done anything wrong. Finance counts revenue when an invoice is paid, net of returns, while sales counts it when an order is booked. Both definitions are reasonable, but neither is written down where the other team can find it.
So the meeting turns into a hunt for answers to questions nobody owns. Who decides which definition is official? Who approves a change to it, and how would anyone know when a report quietly drifted back?
A data governance framework exists to settle those questions before the meeting, not during it. This guide compares the main data governance frameworks and shows how to choose one for your situation. After that, it walks through a 90-day build, with a template, a sample RACI and the KPIs that prove it works.
What Is a Data Governance Framework?
A data governance framework is the set of policies, roles, decision rights, standards and controls an organization uses to manage data. It also defines who owns each data domain, which quality and access rules apply and how success is measured.
The framework sits inside the wider discipline of data governance, which covers the goals, the culture and the long-term program. It also differs from data management, the daily work that the framework governs, as our guide to data governance vs data management explains. Think of the framework as the blueprint, because it turns a broad goal such as “trusted data” into named owners, written rules and checks that run inside your platforms.
The timing matters because governance programs are easy to launch and hard to keep alive. In February 2024, Gartner predicted that 80% of data and analytics governance initiatives would fail by 2027. Its stated reason was the lack of a real or manufactured crisis. So a framework works best when it is tied to a problem people already feel, such as the revenue dispute above.
Framework vs Program vs Operating Model vs Tool
Teams often use these four terms as if they meant the same thing. That is how a team buys a catalog and calls it a framework. Since each one answers a different question, skipping one leaves a gap the others cannot fill.
| Term | What it is | Example |
|---|---|---|
| Framework | The reference structure of components, roles, rules and measures | DAMA-DMBOK, DCAM or your own adapted version |
| Program | The funded effort that puts the framework into practice | A 90-day rollout for the finance domain |
| Operating model | How decision rights split between a central team and the domains | A central council with domain data owners |
| Tool | Software that enforces and records the rules | Microsoft Purview Unified Catalog or Databricks Unity Catalog |
Read the table from the bottom up to see how the four depend on each other. A tool can enforce only the rules the framework defines. Only the owners named by the operating model can approve those rules. When people say “data governance model”, they usually mean this operating model.
Core Components of a Data Governance Framework
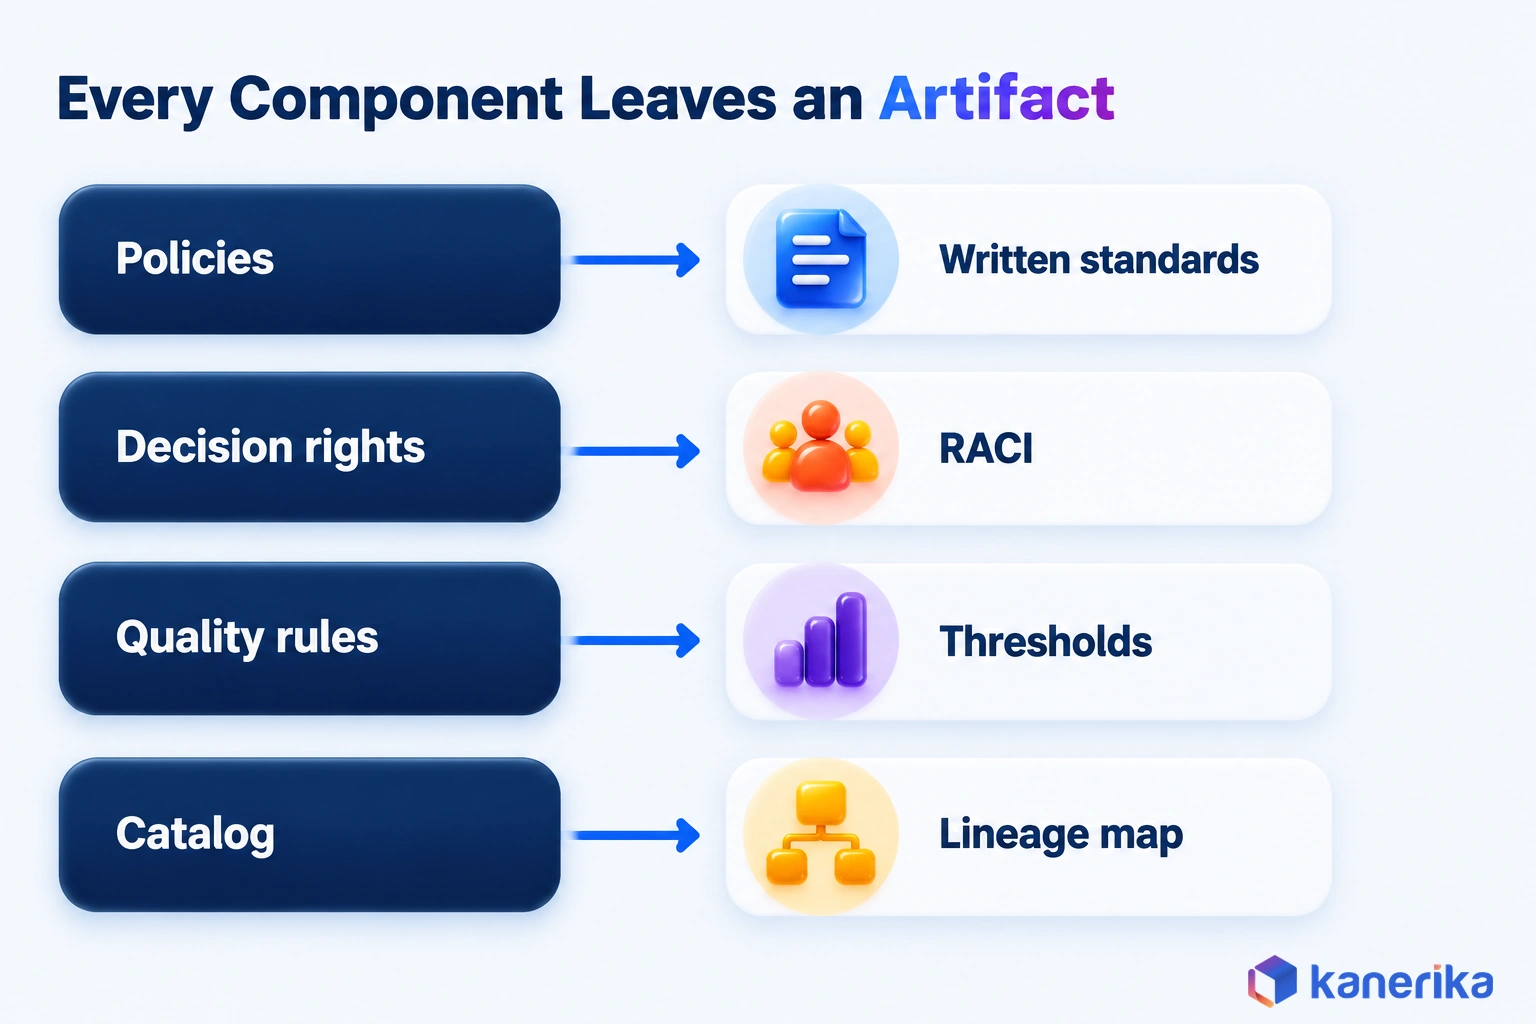
Every framework, whatever its name, breaks down into the same working parts. For each part, ask which decision it settles and what artifact it leaves behind for the next person.
Go back to the revenue dispute. First, a policy says each board KPI has one certified definition, and decision rights say the finance team owns it. A data-quality rule checks that returns are netted out, while lineage shows which reports read the certified table. Without those artifacts, the same argument starts again as soon as the next meeting begins.
| Component | Decision it settles | Artifact it produces |
|---|---|---|
| Policies and standards | Which rules apply to data and what “good” means | Policy documents, naming and definition standards |
| Decision rights and roles | Who approves, who does the work, who is consulted | RACI, role charter, named owners |
| Data quality rules | Which checks data must pass, and at what threshold | Rule catalog with thresholds and owners |
| Metadata, catalog and lineage | What data exists, what it means and where it flows | Business glossary, catalog entries, lineage maps |
| Classification and access control | Who can see which data, and under which label | Sensitivity labels, access policies, review logs |
| Lifecycle and retention | How long data is kept and when it is deleted | Retention schedule, archive and deletion rules |
| Issue management and escalation | How data problems are logged, routed and closed | Issue log, escalation path, response times |
| Metrics | Whether the framework is working, and where it is not | KPI scorecard reviewed by the council |
Metadata: The Component Teams Skip
Metadata is the part teams skip most often, because it feels like paperwork. Then the auditor from the opening asks where the quarterly revenue figure came from, and someone has to trace it by hand.
A catalog with data lineage answers that question directly. It shows the board report reading the certified revenue table, which reads the invoice and returns data. The auditor sees every step and its owner.
Some guides group these parts into broader data governance pillars such as people, process and technology. Others start from data governance principles like accountability and transparency. The grouping matters less than coverage, since a part with no owner and no artifact is where the next data incident will start.
Data Governance Frameworks Compared: DAMA-DMBOK, DGI, DCAM, CDMC, and COBIT
Published data governance frameworks save you from inventing the structure yourself. They differ less in quality than in purpose, so the right question is what each one was built to do.
A bank preparing for a supervisor’s review needs a way to score its capabilities against a standard. A retailer launching its first program needs shared vocabulary and a simple design. Those are different jobs, so no single framework does both equally well.
| Framework | Owner body | Best at | Best fit | Regulatory weight | Effort to adopt |
|---|---|---|---|---|---|
| DAMA-DMBOK | DAMA International | Shared vocabulary for data management | First programs, training and cross-team alignment | Indirect, since it is a reference rather than a control standard | Medium |
| DGI Data Governance Framework | The Data Governance Institute | Designing the governance program | Mid-size firms setting up a council and charter | Low | Low |
| DCAM | EDM Association | Scoring data management capability | Banks, insurers and other regulated firms | High in financial services | High |
| CDMC | EDM Association | Controls for sensitive data in the cloud | Cloud migrations carrying PII or MNPI | High where cloud controls are audited | Medium to high |
| COBIT 2019 | ISACA | Governance of enterprise IT | IT-led organizations under audit pressure | High in IT audit | High |
The regulatory weight and effort columns are planning judgments from our project work, not ratings the framework owners publish. Use them to compare, then read the short profiles below before you commit.
DAMA-DMBOK: The Body of Knowledge
DAMA-DMBOK is DAMA International’s reference guide to data management terms and practices. Treat it as a textbook rather than a checklist. In practice, it gives your council, stewards and engineers one shared vocabulary, and it places governance at the center of the wider data management discipline.
The second edition is still the current one. DAMA launched a DMBOK 2.0 revision in 2024 and started an evergreening project for DMBOK 3.0 in 2025, so expect the content to keep moving. Use it to name things consistently, then pair it with a model that tells you what to build first.
DGI Data Governance Framework: Designing the Program
The DGI Data Governance Framework from the Data Governance Institute is built for program design. Its 10 components answer four plain questions. WHY covers mission and value, plus the beneficiaries who gain from the program. WHAT covers data products, controls, accountabilities, decision rights, and policy and rules.
WHO is the participants, and HOW covers processes, tools and communication together with the work program. That order suits a mid-size firm’s first council, because members agree on the purpose before they debate rules. It is also lighter than DCAM and easier to explain to business leaders who have never read a governance standard.
DCAM: Capability Assessment and Scoring
DCAM, the Data Management Capability Assessment Model, comes from the EDM Association, formerly the EDM Council. It is an assessment model, so you score your organization’s capabilities against defined criteria and track that score over time. Boards and regulators like that, because they want evidence of progress rather than a policy binder.
DCAM is particularly strong in financial services. Version 3 adds capabilities for cloud-native architectures, AI and ML integration, and modern data pipelines. So it stays relevant for firms moving analytics to the cloud.
CDMC: Controls for Cloud Data
Cloud Data Management Capabilities (CDMC), also from the EDM Association, focuses on one problem: protecting sensitive data once it lives in the cloud. Its core is a set of 14 controls and automations for data such as personal information (PII) and material non-public information (MNPI).
CDMC works best as a layer on top of a broader framework. It tells you which protections a cloud estate must automate for sensitive data. What it leaves to the base framework is how to run a council or who should approve a KPI definition.
Datasheet
Elevate Data Governance, Compliance and Security of Your Organization
See how Kanerika sets up cataloging, classification and compliance controls on Microsoft Purview, the protections CDMC-style frameworks expect for sensitive data.
View the Datasheet →COBIT 2019: Where IT Governance Fits
COBIT 2019 from ISACA governs enterprise IT as a whole, with 40 governance and management objectives in its core model. Data is one part of that scope, so COBIT fits when IT audit sets the agenda and data controls must map to IT controls. ISACA has announced COBIT 7 as its successor for late 2026, so check which version your auditors reference. For how the two disciplines split and overlap, see our guide to IT governance vs data governance.
How to Choose the Right Data Governance Framework
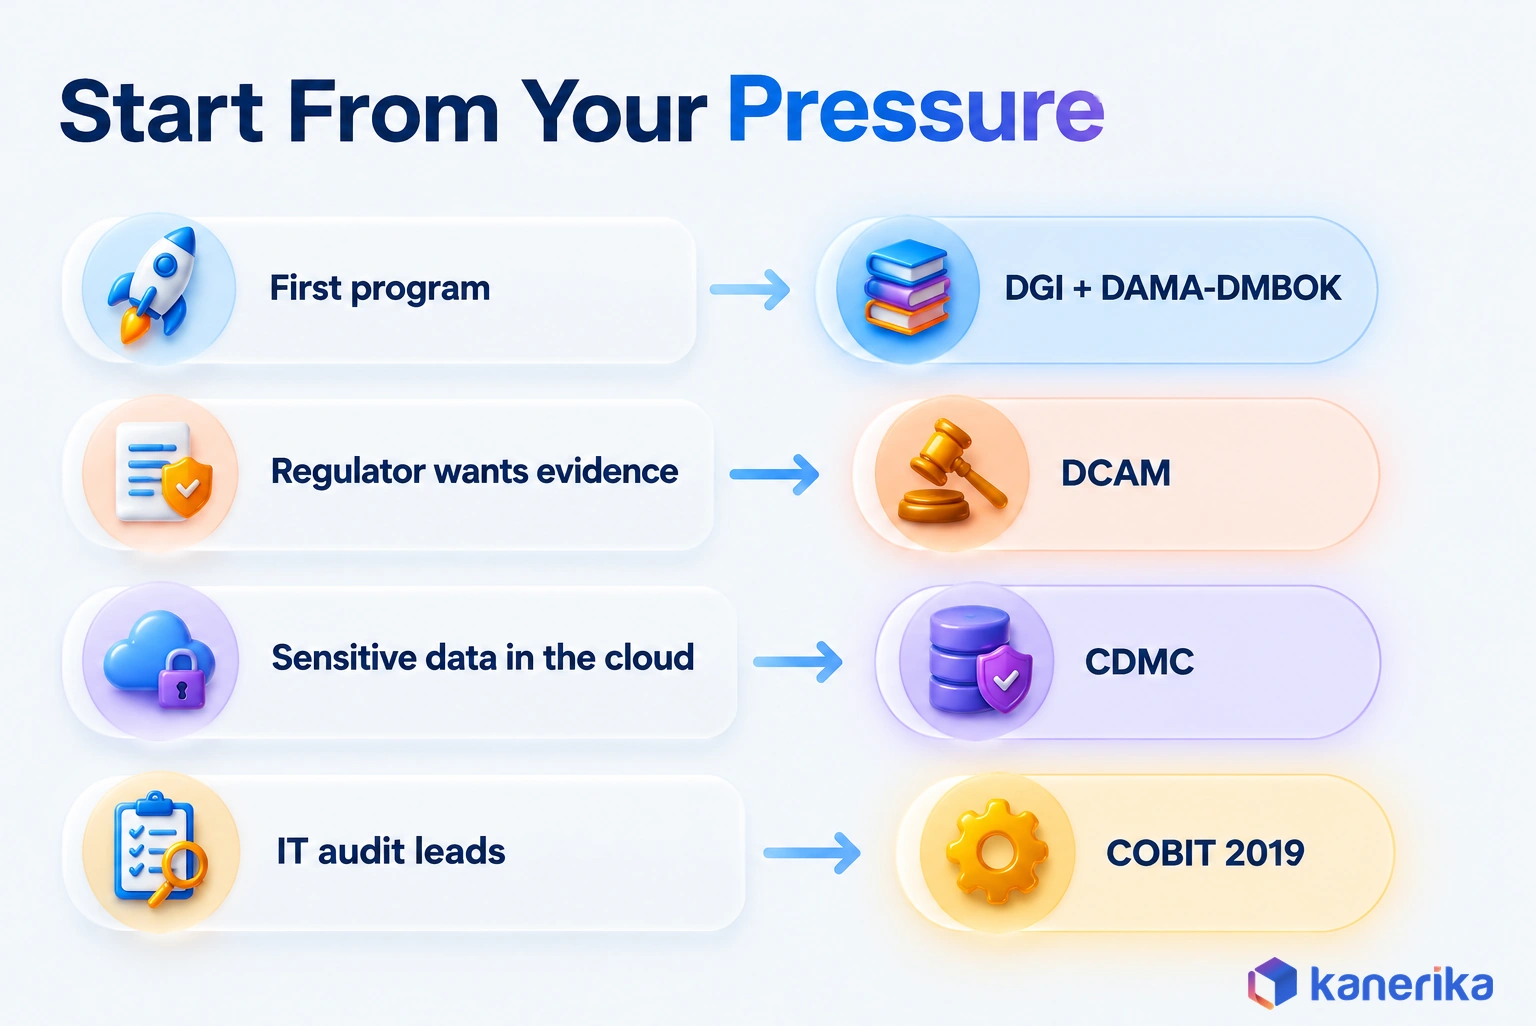
The right framework depends less on its features than on the pressure that started your program. Once you name that pressure, such as a regulator, an auditor, a migration or a broken report, the shortlist gets short quickly.
A regional bank and a software company can both say they need governance and mean different things. The bank needs scored evidence for supervisors. By contrast, the software company needs owners and definitions before an investor’s due diligence starts.
| Situation | Primary framework | Add-on |
|---|---|---|
| First program at a mid-size firm | DGI for program design | DAMA-DMBOK for shared terms |
| Regulated bank or insurer | DCAM for capability scoring | CDMC for cloud estates |
| Cloud migration with sensitive data | CDMC for cloud controls | DAMA-DMBOK for definitions |
| IT-led firm under audit pressure | COBIT 2019 | DAMA-DMBOK for data-specific practice |
| Healthcare or public sector | DGI for program design (DAMA-DMBOK terms) | CDMC when regulated data moves to the cloud |
Industry guides go deeper on the regulated rows, such as data governance in banking and data governance in healthcare. Before you settle on a row, answer six questions with the people who will run the program.
- Which event will make leaders care: an audit, a regulator, a migration or a failed report?
- Do you need a score to show progress, or a design to start?
- Is data moving to the cloud, and does it include personal or market-sensitive data?
- Who will own the framework: the business, IT or a joint council?
- How many domains will you govern in year one?
- Which platforms will enforce the rules, and do they have catalog features?
Answer the first two honestly and one primary framework emerges. A “score” answer to question 2 points to DCAM, while a “design” answer points to DGI. Other answers then shape the add-on, so a yes to question 3 adds CDMC.
Should You Combine Frameworks?
Yes, and combining is often the practical answer, because each framework covers a different job. For example, a common pairing uses DAMA-DMBOK for vocabulary and DCAM for scoring. Firms with large cloud estates add CDMC controls on top, and COBIT joins where IT audit drives the agenda.
The rule is to pick one primary framework that owns the structure. Every add-on should then fill a named gap that you can state in one sentence. Otherwise, the add-on is adding paperwork rather than coverage.
Worked Example: A Mid-Size Lender Choosing a Framework
The following is an illustrative example rather than a client story. A lender is moving its loan data to a cloud lakehouse, and its regulator has asked for evidence of data controls.
- Name the trigger. The regulator’s request sets a deadline, so leadership is already paying attention.
- Pick the primary framework. Because the lender needs scored evidence, DCAM becomes the structure.
- Add the gap-filler. Loan data includes personal information headed to the cloud, so CDMC controls apply to that estate.
- Borrow the vocabulary. The team adopts DAMA-DMBOK terms for its glossary, so stewards and engineers mean the same thing.
- Scope the first domain. Loan origination data goes first, because the regulator’s questions start there.
- Set a baseline. A first DCAM self-assessment gives the board a score to track every quarter.
Notice what the lender did not do, though. It did not buy a tool first, and it did not try to govern every domain at once.
Kanerika Service
Data Governance Services
Kanerika helps you pick the right framework for your pressure, name owners and enforce the rules on Microsoft Purview and Databricks Unity Catalog.
Explore Data GovernanceCentralized, Federated, or Hybrid: Choosing the Operating Model
A framework says which decisions exist, while the operating model says who makes them. Get this wrong and even a well-chosen framework stalls, because every decision either queues behind one committee or nobody enforces anything.
In a centralized model, one governance office writes and enforces every rule, especially in smaller firms. In a federated model, domains such as finance or supply chain own their data and their rules, which is the idea behind a data mesh. Finally, a hybrid model keeps standards central and pushes everyday decisions out to domain owners.
| Model | How decisions flow | Fits when | Risk |
|---|---|---|---|
| Centralized | One office sets and enforces all rules | When the firm is small or one domain dominates | Bottlenecks, since the business sees governance as IT’s job |
| Federated | Each domain sets and enforces its own rules | When mature domains have their own data teams | Definitions drift when domains disagree |
| Hybrid | A central council sets standards; domains decide within them | When several domains share KPIs | Slow calls unless escalation rules are clear |
For a business whose domains share KPIs, hybrid is usually the safer start. It gives each domain an owner while keeping one definition of revenue. As a rule of thumb, stay centralized while one domain produces most of your critical data elements.
Move to hybrid once two or more domains publish KPIs that other teams consume. Go federated only when every domain has its own data team and steward. The people who make it work day to day are owners and stewards, and data stewardship is where most of that effort sits.
A Sample RACI for Five Data Governance Decisions
A RACI turns the operating model into named accountability, so nobody has to guess who signs off. R is responsible for the work, A is accountable and signs off, C is consulted and I is informed. Here is a starting version for five decisions that every framework faces sooner or later.
| Decision | Data owner | Data steward | Custodian / platform team | Governance council | Data consumers |
|---|---|---|---|---|---|
| Approve a KPI definition | A | R | I | C | C |
| Set a data-quality threshold | A | R | C | I | C |
| Grant access to sensitive data | A | C | R | I | I |
| Change a retention period | A | C | R | C | I |
| Resolve a cross-domain conflict | C | R | I | A | I |
Adapt the letters, not the principle. Each decision needs exactly one A, and that A should sit in the business unless the conflict crosses domains, when the council takes it.
The access and retention rows overlap with your data security and data privacy programs. Invite those owners as C on both rows, so a grant or a deletion never surprises them.
How to Implement a Data Governance Framework in 90 Days
Ninety days is long enough to prove the framework on one domain and short enough to keep sponsors interested. The trick is to resist governing everything at once and instead pick the domain where a visible problem already exists.
For the distributor in the opening scene, that domain is finance, and the first deliverable is one certified revenue definition. Everything in the plan below serves that outcome.
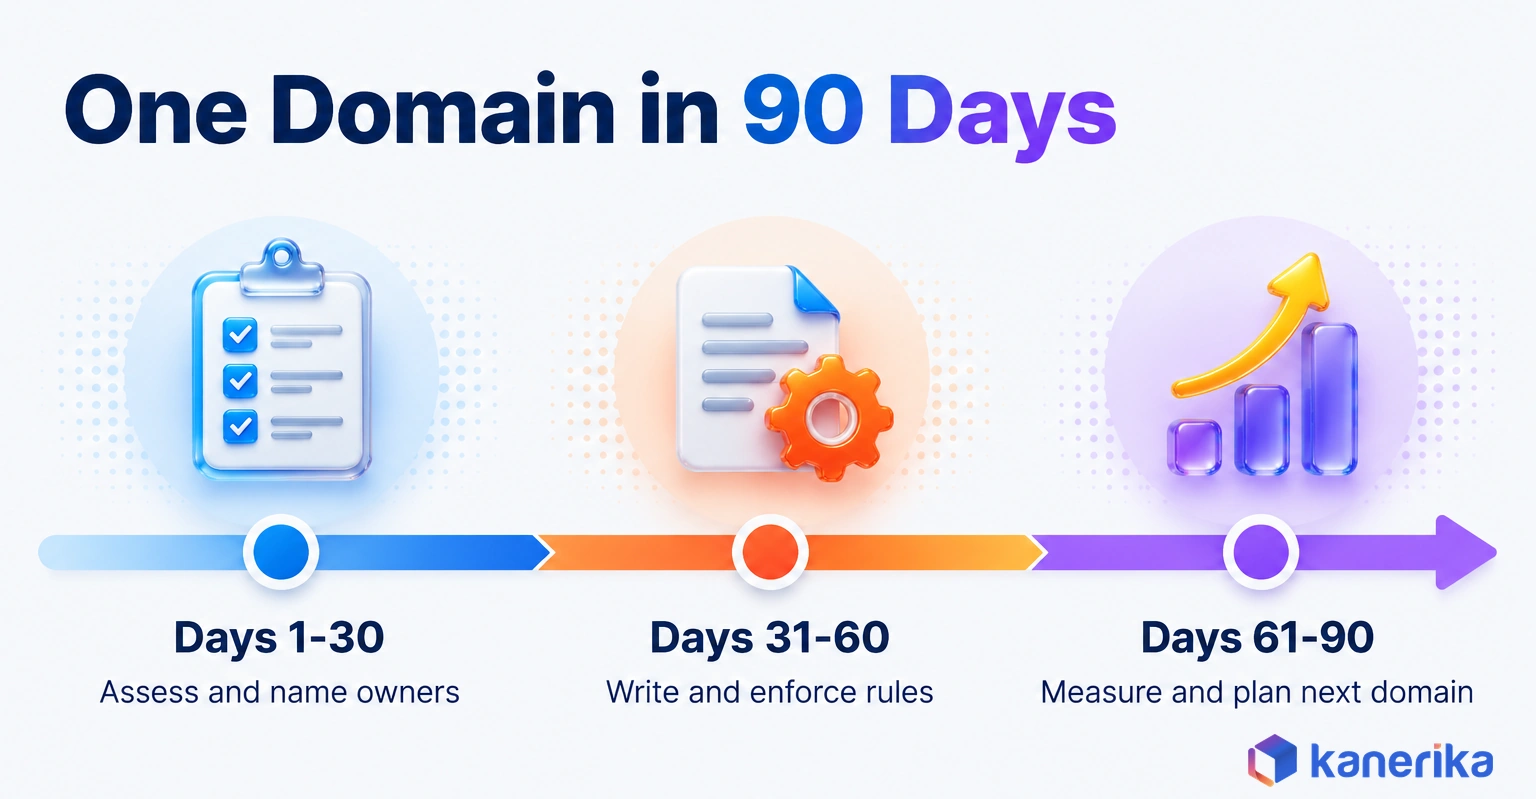
- Days 1-30: Assess and assign. List the domain’s critical data elements, interview the people who use them and run a quick maturity check. Name a data owner and a steward for each element, then agree on the business problem you will fix first.
- Days 31-60: Write and enforce. Draft the policies and glossary entries for the domain, then set data-quality rules with thresholds. Configure classification and access controls in your platform so the rules run, rather than sit in a document.
- Days 61-90: Measure and expand. Track the KPIs, fix the failures the rules surface and hold the first council review. Close with a written plan for the next domain, based on what the first one taught you.
Cost depends on four drivers more than on the framework you pick: scope, the number of domains, existing tooling and steward time. Tooling costs less if you already run a platform with catalog features, while steward time is the cost most plans underestimate.
Tools That Put the Framework Into Practice
Tools are the enforcement layer of a framework, and they work best once owners and rules exist. At that point, two platforms cover much of the enforcement work for Microsoft and Databricks estates.
Microsoft Purview Unified Catalog provides a platform for data governance, with an inventory of data assets, their metadata and their lineage. Business users can then see glossary terms, owners and quality results in one place. Our overview of Microsoft Purview covers the wider product, and teams on Fabric can read about Microsoft Fabric governance.
Databricks Unity Catalog is a unified governance layer for data and AI. It enforces access control, tracks lineage and logs activity for auditing, which maps straight onto the access and metadata components. Our Unity Catalog guide also shows how it is set up.
Here is what the RACI and the template look like as Unity Catalog SQL for the certified revenue table. The owner group is the A from the RACI, the grants follow the access row, and the tag and mask carry the classification rule.
-- Data owner from the RACI (the A) owns the certified table
ALTER TABLE gold.finance.revenue_daily OWNER TO `finance-data-owners`;

-- Consumers read the certified table
GRANT USE CATALOG ON CATALOG gold TO `finance-analysts`;
GRANT USE SCHEMA ON SCHEMA gold.finance TO `finance-analysts`;
GRANT SELECT ON TABLE gold.finance.revenue_daily TO `finance-analysts`;

-- Policy status, visible in the catalog
ALTER TABLE gold.finance.revenue_daily
  SET TAGS ('certified' = 'true', 'policy' = 'certified-kpi-definitions');

-- Classification: tag and mask a personal-data column
ALTER TABLE gold.finance.customers
  ALTER COLUMN email SET TAGS ('pii' = 'email');

CREATE FUNCTION gold.finance.mask_email(email STRING)
  RETURN CASE WHEN is_account_group_member('finance-pii-readers')
    THEN email ELSE '***' END;

ALTER TABLE gold.finance.customers
  ALTER COLUMN email SET MASK gold.finance.mask_email;
Readers need USE CATALOG and USE SCHEMA on the parent objects before SELECT works, which is why those grants come first. The mask runs at query time, so the approved group sees the email and everyone else sees asterisks. Databricks documents each statement in its privileges, tags and row filter and column mask guides.
Many estates run both platforms, and connecting them has pitfalls, such as lineage that breaks where data crosses between catalogs. For a wider shortlist, compare data governance tools and data catalog tools against the components your framework needs.
A Data Governance Framework Template You Can Adapt
A template is useful only if it forces specific answers. The stub below covers one policy, one decision-rights entry and one data-quality rule for the revenue example, so every field asks for a name, a number or a date.
Copy the structure, not the values. The thresholds shown are examples, so replace them with your own once you know what your reports and regulators require.
POLICY: Certified KPI Definitions (finance domain)
Purpose:        One approved definition for every board-level KPI
Scope:          Net revenue, gross margin, days sales outstanding
Owner:          VP Finance (data owner)
Steward:        Finance data steward
Rule:           Board reports read KPIs only from certified tables
Threshold:      100% of board reports on certified tables (example)
Exception path: Steward logs it; owner decides within 5 business days
Review cycle:   Quarterly, at the governance council

DECISION RIGHT: Change the net revenue definition
Proposes:   Finance data steward
Approves:   VP Finance
Consulted:  Sales operations, FP&A, governance council
Informed:   All report owners, through a catalog change notice

DATA QUALITY RULE: DQ-FIN-007 Returns netted from revenue
Check:      net_revenue = gross_invoiced - returns_amt - credits_amt
Applies to: gold.finance.revenue_daily
Threshold:  >= 99.5% of rows pass per load (example)
On fail:    Block publish, alert steward, open an issue
Notice how the rule points back to the policy and its owner, rather than standing alone. A rule such as DQ-FIN-007 checks whether values are right, which differs from proving data changed only through approved steps. Our guide to data integrity vs data quality explains where each control belongs.
Talk to Kanerika
Turn This Template Into Your First Policy Set
Talk to Kanerika about adapting the policy, decision-rights and data-quality templates to your first domain, with thresholds that fit your reports and regulators.
Schedule a Demo →How to Measure Whether Your Framework Works
A framework that cannot show progress tends to lose its sponsor by the second budget cycle. So pick a few measures that track owners, quality and response time, then report them to the council every month.
Each metric below has a formula, so two people calculating it get the same answer. The example targets are illustrative starting points rather than industry benchmarks.
| Metric | Formula | Example target (illustrative) |
|---|---|---|
| Critical data elements with a named owner | Owned elements / elements in scope | 100% by day 90 |
| Data-quality rule pass rate | Rows passing all rules / rows checked | 98% or higher |
| Time to resolve a data issue | Average days from issue logged to issue closed | Under 10 business days |
| Assets cataloged with lineage | Assets with lineage / assets in scope | 80% in the first domain |
| Access-review completion | Reviews completed on time / reviews due | 100% each quarter |
| Open policy exceptions | Open exceptions older than 90 days | Zero |
The pass-rate row is the easiest one to automate. On Databricks, one query over the certified table gives the daily number for rule DQ-FIN-007 from the template.
-- Daily pass rate for DQ-FIN-007 over the last 30 days
SELECT load_date,
       COUNT_IF(net_revenue = gross_invoiced - returns_amt - credits_amt)
         / COUNT(*) AS pass_rate
FROM gold.finance.revenue_daily
WHERE load_date >= date_sub(current_date(), 30)
GROUP BY load_date
ORDER BY load_date;
Microsoft Purview Unified Catalog covers the same measure with no-code or low-code rules. Those data quality rules apply at the column level and roll up into scores for data assets, data products and governance domains. For the wider set of quality dimensions, see our data quality framework guide.
Data observability tools can feed the pass-rate and freshness numbers automatically. That keeps the scorecard honest, because nobody has to compile it by hand.
When to Expand to the Next Domain
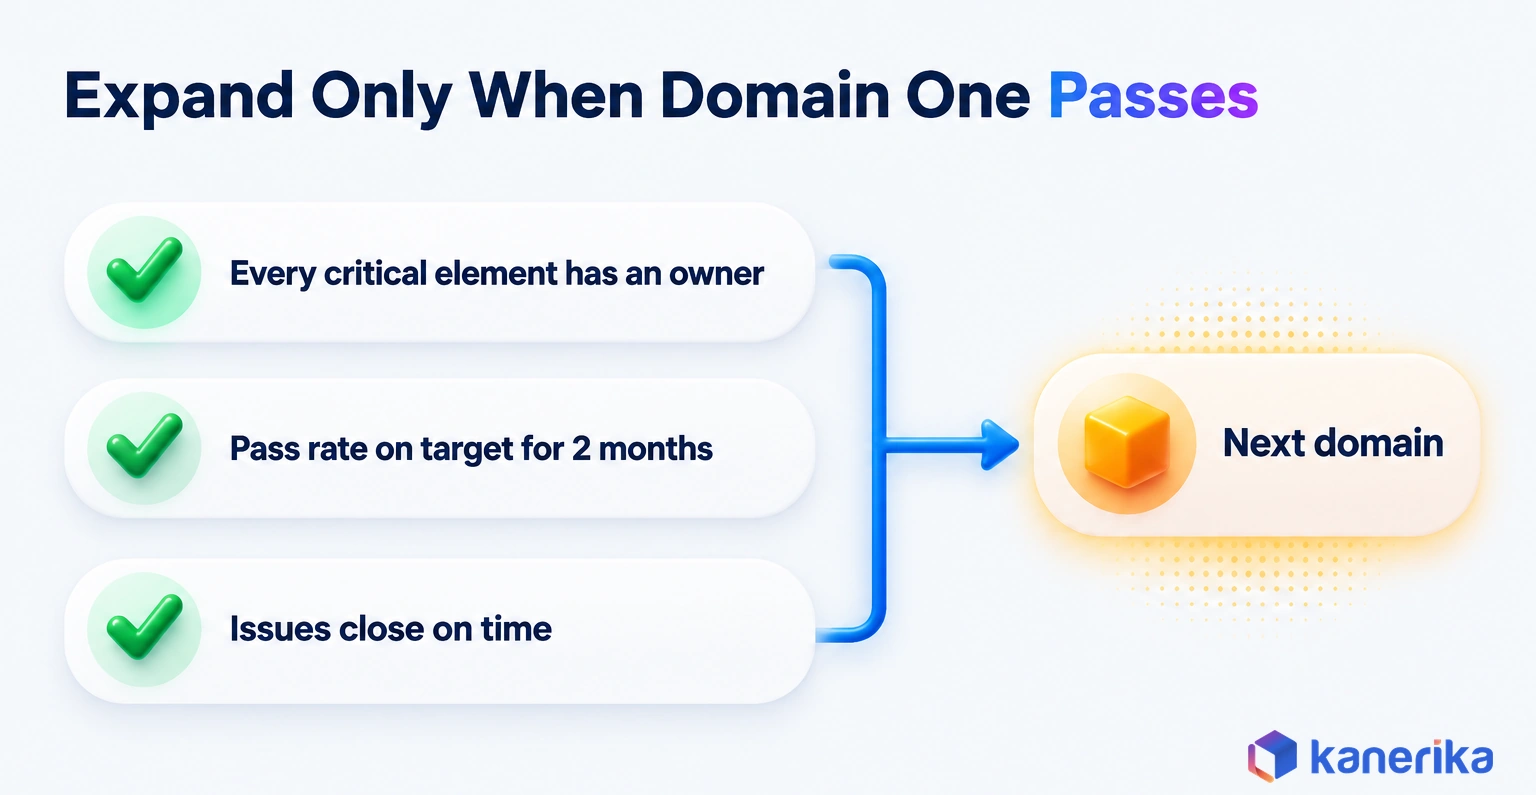
Expanding too early spreads stewards thin and repeats the original mess at a larger scale. Move to the next domain only when three things are true.
- Every critical data element in the first domain has a named owner who attends reviews.
- The rule pass rate has held at its target for at least two consecutive months.
- Issues close within the agreed time, without the core team chasing them.
For a longer view, a data governance maturity model shows what the next level looks like and which capabilities to add as you grow.
Why Data Governance Frameworks Stall
Frameworks stall on a handful of organizational mistakes, and each one shows up early if you know where to look. Catch them in the first domain and the fix stays cheap.
- Buying the tool first. A catalog without owners soon becomes a well-indexed list of data that nobody trusts.
- No named owners. “The data team” is not an owner, so a rule without an accountable person is only a suggestion.
- Governance as a side project. Stewards with no protected time drop governance work the moment a deadline arrives.
- No business trigger. The crisis Gartner warns about at the top of this guide is the cure: tie the program to a problem leaders already feel.
Each mistake has a cheap early fix: owners before tools, time in job plans and a trigger in the charter. For a longer list, see these common data governance challenges and the data governance best practices that counter them.
Extending the Framework to AI and Cloud Data
AI and cloud projects stretch the framework you already run, so extend it rather than start a second one. Models amplify whatever data they learn from, while cloud estates multiply the places where sensitive data can land.
In February 2025, Gartner predicted that through 2026, organizations will abandon 60% of AI projects not supported by AI-ready data. It also reported that 63% of organizations either do not have, or are unsure whether they have, the right data management practices for AI.
Checklist
AI Governance Checklist
Check training-data lineage, classification and model oversight before data reaches an AI project, using Kanerika’s AI Governance Checklist.
Get the Checklist →Three extensions to the framework you already run close most of that gap.
- Training-data lineage. Record which datasets fed each model version, so you can explain or retrain when a source changes.
- Classification before model use. Label personal and confidential data before it reaches a training set or a retrieval index.
- Cloud controls. Apply CDMC-style controls to sensitive data in cloud platforms, using automation rather than manual checks.
Model-level rules, such as risk tiers and human oversight, belong in a separate layer. Our AI governance framework guide covers that layer, and our overview of AI governance shows how it connects to data governance. Teams comparing platforms for that layer can start with these AI governance tools. Keep both layers on the same council agenda, so a model owner cannot approve a dataset its data owner has not cleared.
How Kanerika Builds Data Governance Frameworks
Kanerika starts a governance engagement with the business problem, the same way this guide does. We then build the framework around the platforms a client already runs, rather than starting from a new tool. Our data governance services package that work into three offerings, each mapped to framework components.
- KANGovern covers the catalog, lineage and business glossary on Microsoft Purview and Databricks Unity Catalog, which is the metadata component.
- KANGuard handles data loss prevention, classification and labeling across Microsoft 365, which is the classification and access component.
- KANComply maps controls to over 360 international regulations, standards and frameworks, which supports the policy and metrics components.
The offerings run on Microsoft Purview, Unity Catalog and Concentric AI. Kanerika is a Microsoft Solutions Partner for Data and AI with the Analytics on Azure specialization, and a Microsoft Fabric Featured Partner.
One engagement shows the framework at work. A global packaging leader had more than 10,000 distinct measures spread across 400+ reports and 600 production dataflows. Definitions conflicted from report to report, so governance gaps made the numbers hard to trust.
Kanerika unified the sources in OneLake and built an automated metadata repository for the 10,000+ metrics, with naming conventions to match. Role-based access control and audit trails also ran through Microsoft Purview. Then Power BI templates and a Community of Practice kept new reports on the standard.
Each piece maps to a framework component. For example, the definitions became policy and standards, the metadata repository became the catalog, and access control came with audit trails. The results were a 60% increase in data accessibility, a 45% improvement in decision-making and a 30% reduction in ETL processing time.
Case Study
60% More Data Accessibility with Microsoft Fabric
A global packaging leader standardized 10,000+ measures with an automated metadata repository, naming conventions, and RBAC and audit trails in Microsoft Purview.
Read the Case Study →Data Governance Frameworks: Which One to Start With
Choosing among data governance frameworks comes down to the pressure you face. Start a first program with DGI for program design, with DAMA-DMBOK for shared terms. Pick DCAM when regulators want scored evidence, CDMC when sensitive data moves to the cloud and COBIT when IT audit leads.
Building one is the same job, whichever you pick. Name owners for one domain, write the rules into your platforms and then measure the results for 90 days. If you want help scoping that first domain, the Kanerika team can work through it with you.
Choose the framework that answers your loudest problem, then build it one domain at a time.
Frequently Asked Questions
What is a data governance framework?
A data governance framework is the set of policies, roles, decision rights, standards and controls an organization uses to manage data. It defines who owns each data domain and which quality and access rules apply. It also sets how those rules are enforced in platforms and how success is measured. Tools enforce it, but people and rules define it.
What are the most common data governance frameworks?
Five published frameworks appear in most comparisons. DAMA-DMBOK supplies shared vocabulary for data management. The DGI framework helps you design the program itself. DCAM scores data management capability and is strong in financial services. CDMC sets controls for sensitive data in the cloud. COBIT 2019 governs enterprise IT and suits organizations where IT audit leads.
What types of data governance frameworks exist?
Frameworks fall into a few broad types. Reference frameworks such as DAMA-DMBOK define vocabulary and practice. Program frameworks such as DGI guide how to set up governance. Assessment models such as DCAM score capability over time. Control frameworks such as CDMC specify required controls. IT governance frameworks such as COBIT treat data as one part of enterprise IT.
What are the dimensions of data quality in a governance framework?
Commonly cited dimensions include accuracy, completeness, consistency, timeliness, validity and uniqueness. Accuracy asks whether values match reality. Completeness checks that required fields are filled. Consistency means a value agrees across systems. Timeliness asks whether data is fresh enough for its use. Validity and uniqueness check formats and duplicates. Each dimension needs a rule and a threshold.
How long does it take to implement a data governance framework?
A first domain can be governed in about 90 days if the scope stays narrow. That covers assessing the domain, naming owners, writing policies and rules, and measuring the results. A full enterprise rollout takes longer, because each new domain repeats the cycle. The pace depends on scope, tooling and how much time stewards can give.
Is a data governance framework the same as a data governance model?
Not exactly. The framework is the full structure of policies, roles, standards, controls and metrics. The model usually means the operating model, which is one part of that structure. It describes how decisions flow, whether centrally, by domain or through a hybrid setup. You choose a framework first, then pick an operating model to run it.
Is centralized or federated data governance better?
Neither is better in every case. Centralized governance suits a small firm or one dominant domain, but it can turn into a bottleneck. Federated governance suits mature domains with their own data teams, but definitions can drift apart. A hybrid model fits firms with several domains, because standards stay central while domain owners decide locally.
Do AI systems need a separate data governance framework?
Usually not. AI projects extend the data governance framework you already have rather than replace it. Add lineage for training data, classify sensitive data before models use it, and apply cloud controls wherever that data moves. Model-level rules, such as risk tiers and human oversight, belong in a separate AI governance layer built on top of it.
What are the main components of a data governance framework?
A working framework has eight components. The first four are policies and standards, decision rights and roles, data quality rules, and metadata with catalog and lineage. The other four are classification and access control, lifecycle and retention, issue management, and metrics. Each one should settle a specific decision and leave an artifact, such as a RACI or rule catalog.
How do you create a data governance framework?
Start with one business problem and one data domain. In the first 30 days, assess the domain and name an owner and steward for each critical data element. In days 31 to 60, write policies, glossary terms and quality rules, then enforce them in your platform. In days 61 to 90, measure the results and plan the next domain.
What are the core principles of data governance?
Common principles include accountability, transparency, standardization, data quality and compliance. Accountability means every important dataset has a named owner. Transparency means people can see definitions, lineage and rules. Standardization keeps one definition per business term. Quality and compliance mean data is checked against agreed thresholds and legal duties. A framework turns these principles into enforceable rules.
What are examples of data governance in practice?
A finance team certifying one definition of net revenue is data governance in practice. So is a steward approving a quality threshold for customer addresses. Other examples include labeling personal data before it reaches an analytics workspace, reviewing who can access payroll tables each quarter, and setting how long transaction records are kept before they are deleted.
What tools support a data governance framework?
Catalog and governance platforms enforce the framework once the rules exist. Microsoft Purview Unified Catalog keeps an inventory of data assets with their metadata and lineage. Databricks Unity Catalog enforces access control, tracks lineage and logs activity for auditing. Data quality and observability tools add automated checks. None of these tools replaces named owners or agreed definitions.
What are the main roles in data governance?
The main roles are data owners, data stewards, data custodians and a governance council. Owners are business leaders accountable for a domain’s data. Stewards define terms, set quality rules and resolve issues day to day. Custodians, often the platform team, run the technical controls. The council sets shared standards and settles conflicts that cross domains.
What are the main goals of a data governance framework?
The main goals are trusted data, clear accountability and lower risk. A framework gives every critical data element an owner and one agreed definition. It sets quality thresholds so reports can be relied on. It controls who sees sensitive data and keeps the records auditors ask for. It also makes data easier to find and reuse safely.
What are the three core elements of good data governance?
The three core elements are people, process and technology. People means named owners, stewards and a council with real decision rights. Process means written policies, quality rules, issue handling and regular reviews. Technology means the catalog, lineage, classification and access tools that enforce the rules. A weakness in any one element undermines the other two.