TL;DR
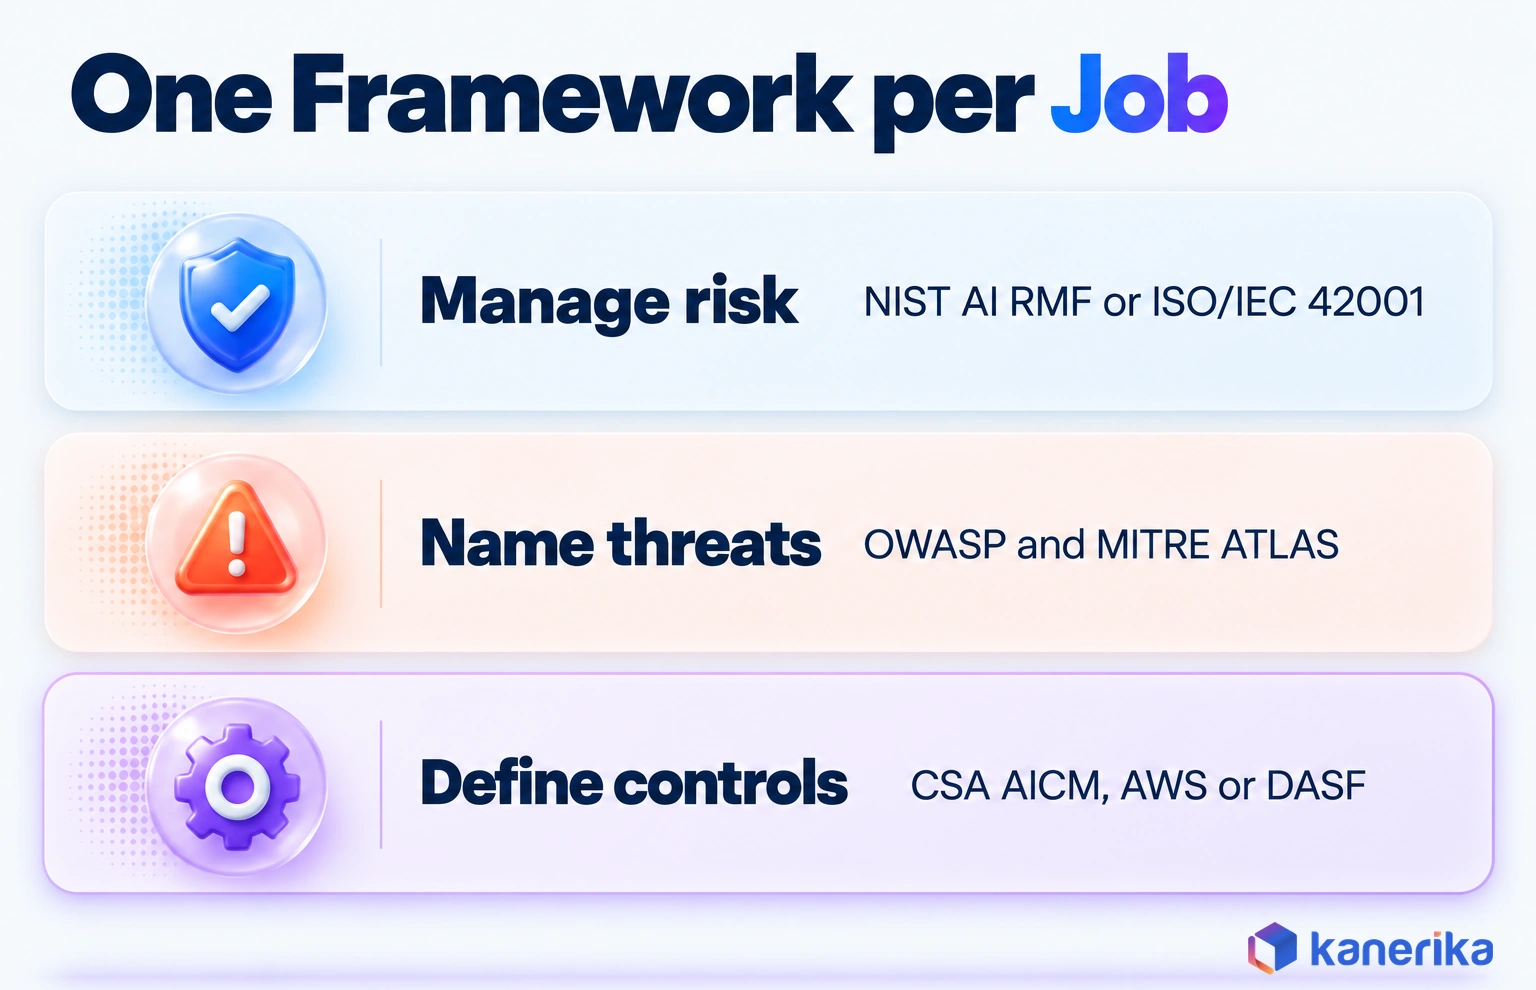
The AI security framework most enterprises need starts with NIST AI RMF, or ISO/IEC 42001 when a certificate matters. Neither one lists attacks, so add the OWASP Top 10 and MITRE ATLAS to test how models and agents can be abused.
Then choose one control list, such as the CSA AI Controls Matrix, to decide what gets built. Banks and hospitals usually start with a management standard, while software teams shipping AI features start with OWASP. Teams that run AI agents should also add agent-specific threat lists. Every control then needs an owner, a test and proof an auditor can check.
Key Takeaways
- An AI security framework maps the threats to your AI systems onto controls, so each one gets an owner, a test and evidence.
- No single framework covers everything, so layer one management standard, one threat catalog and one control catalog.
- NIST AI RMF suits US-led programs, while ISO/IEC 42001 fits when customers or regulators want a certificate.
- OWASP Top 10 lists and MITRE ATLAS turn abstract AI risk into attacks your team can test before release.
- AI agents need their own identities and scoped permissions, as well as human approval for high-impact actions.
- Start with an AI inventory and access enforced at retrieval, since 97% of organizations with AI breaches lacked AI access controls (IBM, 2025).
On-Demand Webinar
The Real Cost of LLM Security Risks and How to Reduce Them
Kanerika’s recorded session on LLM security risks, from manipulated prompts to leaked data, with live demos of LLM-powered agents built to resist manipulation.
Watch the Webinar →When an AI Assistant Becomes a Data Exposure Path
Picture a finance analyst who asks the company’s new AI assistant to summarize a quarterly pricing deck. The answer comes back fast, and at first it looks accurate. It also quotes salary bands from an HR folder that the analyst could never open.
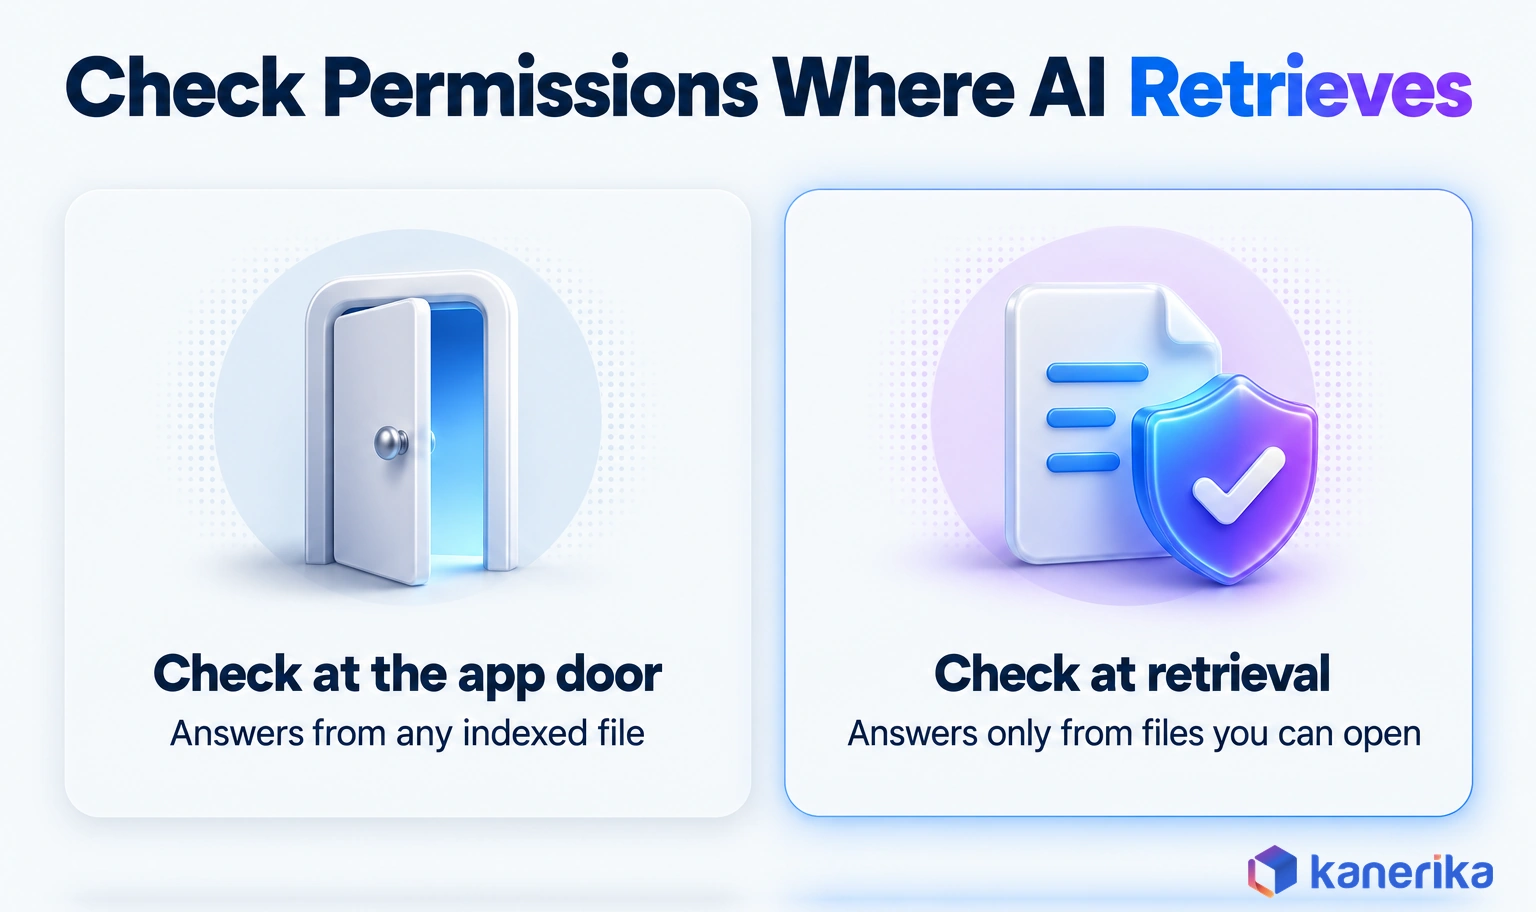
Nobody hacked anything, though. The assistant’s search index was built with a service account that could read every folder, so it answered from files its user could never see. In other words, the permission check happened at the app’s front door instead of where the AI retrieved the data.
Real incidents also follow this pattern. Between August 8 and 18, 2025, a threat actor tracked as UNC6395 stole Salesforce data using compromised OAuth tokens, according to Google Threat Intelligence. The tokens belonged to the Salesloft Drift third-party app, so the theft rode on trust the app already had.
That same month, Cybernews researchers showed that a single prompt could make Lenovo’s chatbot, Lena, leak session cookies. A roughly 400-character prompt made Lena reply in HTML that ran in support agents’ browsers. Unvalidated model output thus became a way to steal their sessions, which is why output validation appears in the crosswalk later.
A security framework built for AI exists to catch these gaps before they ship. This guide explains what one is and then compares the main options. It also shows how to combine them into controls your teams own and test.
What Is an AI Security Framework?
An AI security framework is a structured way to find the threats that target your AI systems and answer each one with a control. Every control then gets an owner, a test that proves it works and evidence an auditor can check.
These threats differ from classic IT risks because they run through language and data. For example, a model can be steered through its inputs, leak data through its outputs or overreach when it calls tools. A framework names those threats, and it also decides who fixes each one and how you prove it stayed fixed.
The word “framework” also covers several kinds of documents. Some are management standards, while others are threat lists or control catalogs. Enterprises need at least one of each, so the comparison later in this guide matters more than any single pick.
AI Security vs AI Governance vs Traditional Cybersecurity
These three disciplines overlap, but each answers a different question. AI governance decides whether and how the business should use AI, including its responsible AI principles. AI security protects AI systems from attack and misuse, while traditional cybersecurity protects the networks, endpoints and cloud accounts underneath them.
| Discipline | Main question | Example control |
|---|---|---|
| AI governance | Should we use this AI system, and under what rules? | An approval board for high-risk use cases |
| AI security | Can this AI system be attacked or made to leak data? | Prompt injection tests before every release |
| Traditional cybersecurity | Is the infrastructure under the AI protected? | Network segmentation as well as endpoint protection |
A gap in any one of them leaves the others exposed. Even a well-governed model on a patched server can leak data when nobody tests its prompts.
Kanerika Service
AI Services Built With Security From Day One
Kanerika designs, builds and secures enterprise AI, from retrieval apps and copilots to agents, with access controls and testing built into delivery.
Explore AI ServicesWhich AI Systems Need Coverage
Scope is where many programs quietly fail, because AI now arrives through many doors. A framework should cover every system that uses a model to read, generate or act on company data. That includes far more than the models your data science team trains.
- Models you train or fine-tune, together with their training data.
- Retrieval-augmented generation (RAG) apps, especially those that answer from internal documents.
- Copilots inside productivity suites, which also raise their own Copilot security concerns.
- AI agents, particularly those that call tools, APIs or other agents.
- AI features inside SaaS products, which often switch on during a routine vendor update.
The last item is the easiest to miss. When a CRM or HR platform adds an AI feature, that feature can reach the platform’s data on day one. It belongs in the inventory as well.
Why AI Security Frameworks Matter More in 2026
AI has moved from pilots into daily work, so attackers have followed it there. As enterprise AI adoption spreads across departments, the number of exposed systems grows faster than security teams can review them.
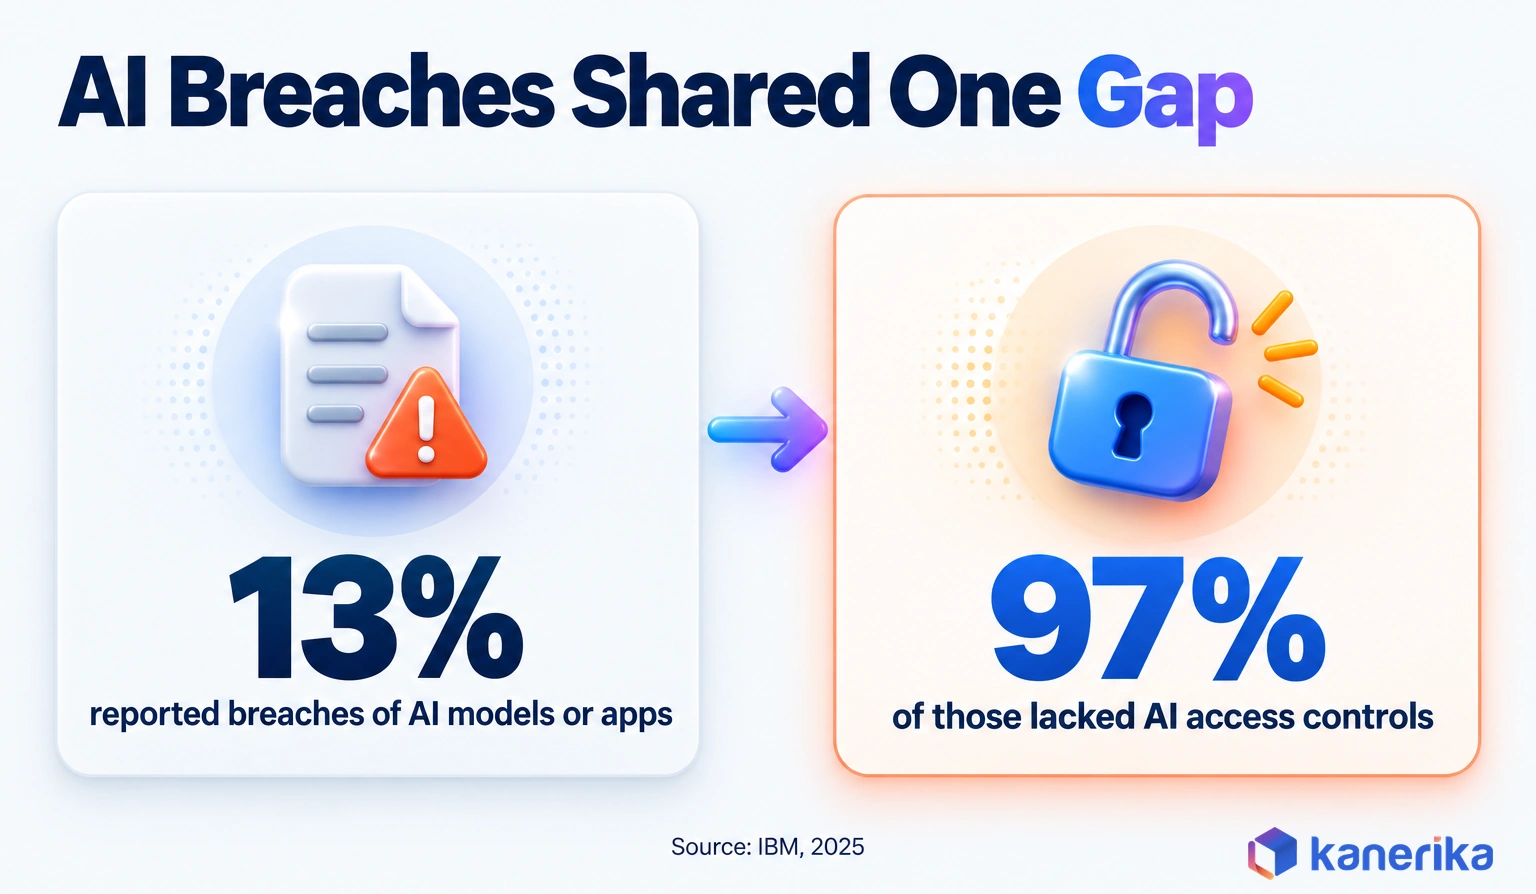
IBM’s 2025 breach research puts numbers on that gap. In IBM’s July 2025 report, 13% of organizations reported breaches of AI models or applications. Of those, 97% still lacked proper AI access controls.
The same study found that one in five organizations had a breach due to shadow AI. Organizations with high levels of shadow AI also saw $670,000 higher average breach costs. Even so, only 37% of organizations had policies to manage AI or detect shadow AI.
Three shifts widen the gap further in 2026:
- Agents widen the blast radius. An agent with write access can move money, change records or send email. So one manipulated prompt can become a real action.
- AI arrives through vendors. Copilots and SaaS features bring models into the business before any security review takes place.
- Regulation keeps taking shape. The EU AI Act entered into force on August 1, 2024, according to the European Commission. Prohibitions then applied from February 2, 2025, followed by general-purpose AI obligations from August 2, 2025.
The AI Omnibus, Regulation (EU) 2026/1744, entered into force on July 27, 2026. It moved stand-alone (Annex III) high-risk obligations to December 2, 2027 and product-embedded (Annex I) ones to August 2, 2028. The deadlines moved, but the duties did not disappear. Our guide to AI compliance covers that regulatory side, while the security framework turns those duties into working controls.
The Main AI Security Frameworks Compared
Each major framework was written to do one job well, but none of them does every job. So the useful question is not which framework is best. Instead, ask which layer each one covers: managing risk, naming threats or defining controls.
The table below compares the seven you are most likely to meet. Read the last column first, because it shows where each framework stops and another must take over.
| Framework | Publisher | Type | Best for | Where it stops |
|---|---|---|---|---|
| NIST AI RMF and Generative AI Profile | NIST | Voluntary risk management framework | Running the program in US-led firms | No control catalog or certificate |
| ISO/IEC 42001:2023 | ISO and IEC | AI management system standard | Certification and audit evidence | Does not describe attack techniques |
| OWASP Top 10 for LLM and Agentic Applications | OWASP | Ranked threat lists | Testing apps and agents before release | Lists risks rather than a full program |
| MITRE ATLAS | MITRE | Adversary tactics and techniques | Threat modeling as well as red teams | No governance or control set |
| Google SAIF | Conceptual framework with six elements | Extending an existing security program | Needs a detailed control set before use | |
| CSA AI Controls Matrix and MAESTRO | Cloud Security Alliance | Control catalog and agent threat model | Defining and reviewing controls | Needs a management layer around it |
| AWS AI Security Framework and Databricks DASF | Platform vendors | Platform control maps | Teams building on that platform | AWS is AWS-specific; DASF is vendor-published but platform-neutral |
The sections below explain each one, starting with the two management standards.
AI Assessment
Not Sure Where Your AI Program Stands?
Take Kanerika’s AI Maturity Assessment to see where your data, governance and controls stand before you choose an anchor framework.
Start Your AI Assessment →NIST AI RMF and the Generative AI Profile
The NIST AI Risk Management Framework is a natural foundation for US enterprises, because it comes from the federal standards body. NIST released version 1.0 on January 26, 2023, for voluntary use, so no US law requires it on its own.
The AI RMF 1.0 document organizes the work into four functions: Govern, Map, Measure and Manage. Govern sets roles and policy, while the other three find, test and treat each risk. NIST then added the Generative AI Profile, NIST-AI-600-1, on July 26, 2024.
NIST published a concept note for a critical infrastructure profile on April 7, 2026. Its AI RMF page also states that “the AI RMF 1.0 is being revised as part of the White House AI Action Plan.” Whatever the revision changes, the RMF tells you how to run a program rather than which controls to build. It therefore pairs naturally with a control catalog. The Playbook’s suggested actions are explained in NIST AI RMF Playbook, without turning them into a checklist.
ISO/IEC 42001
ISO/IEC 42001:2023, published in December 2023, is the international standard for an AI management system. It plays a role similar to ISO/IEC 27001, which does the same for information security. It defines how an organization sets policy, assesses AI risk, applies controls and improves over time.
Its main advantage is assurance, because organizations can be audited and certified against it by accredited bodies. That gives customers and regulators evidence instead of a promise. For a SaaS vendor selling AI into regulated industries, the certificate can also shorten security reviews. What the Stage 1 and Stage 2 audits involve, and what they cost, is covered in ISO 42001 certification.
OWASP Top 10 for LLM and Agentic Applications
The OWASP lists are where abstract AI risk finally becomes something an engineer can test. The OWASP Top 10 for LLM Applications 2025 edition ranks the most critical risks in apps built on large language models. Several entries map directly to the incidents above:
- LLM01:2025 Prompt Injection, where hostile instructions in user input or retrieved content change what the model does.
- LLM02:2025 Sensitive Information Disclosure, where a model reveals data it should not.
- LLM10:2025 Unbounded Consumption, where runaway usage drives up cost or blocks service.
OWASP then published the Top 10 for Agentic Applications for 2026 on December 9, 2025, as a peer-reviewed list of risks for autonomous AI. Our overview of generative AI risks also covers the business side of the same threats.
Prompt injection deserves special attention because it needs no stolen password. A crafted sentence in an email or shared document is enough when the model treats it as an instruction.
MITRE ATLAS
MITRE ATLAS is a public knowledge base of adversary tactics, techniques and procedures that target AI systems. It does for AI what MITRE ATT&CK does for enterprise IT, since it describes how real attackers work.
Security teams generally use it in two ways. First, threat modelers walk an AI system through the ATLAS tactics to see where an attacker could get in. Red teams then use the same techniques to plan realistic tests, so their findings map to a shared vocabulary.
Google SAIF
Google’s Secure AI Framework (SAIF) is a conceptual framework built on six core elements, such as expanding strong security foundations to the AI ecosystem. The other five extend detection and response, automate defenses and harmonize platform controls. They also adapt controls through faster feedback and place AI risk in its business context.
SAIF’s message is that AI security should grow out of the program you already run, rather than start from scratch. It works well as a frame for leadership, although teams still need a detailed control set to put it into practice.
CSA AI Controls Matrix and MAESTRO
When teams need a control list, the Cloud Security Alliance publishes a detailed one that is free to use. Its AI Controls Matrix (AICM) holds 243 control objectives across 18 security domains. It also maps to ISO 42001, ISO 27001, NIST AI RMF 1.0 and BSI AIC4, so it bridges the management standards and daily engineering.
CSA also published MAESTRO on February 6, 2025, as a threat-modeling framework for agentic AI. It splits an agent system into seven layers, so teams can trace a threat from the model up to the wider agent ecosystem.
Platform Frameworks: AWS and Databricks DASF
Cloud and data platforms also publish their own frameworks, which translate the general guidance into controls for their services. For example, AWS’s own framework, published May 15, 2026 and updated May 26, sorts controls into three phases. Phase 1 covers zero to prototype, Phase 2 covers prototype to production, and Phase 3 covers continuous improvement and scale.
The Databricks AI Security Framework (DASF) comes from a vendor, yet it is written to be platform-neutral. Its own page says teams can follow its four steps no matter which platform they use. Those steps build an AI risk profile and then map each risk to concrete controls. AWS’s framework, by contrast, stops at the AWS boundary, so both work best as one layer inside a wider program.
How to Combine Frameworks Without Duplicating Work
The simplest way to combine frameworks is to give each one a single job. Pick one management standard to run the program and one or two threat catalogs to name the attacks. Then add one control catalog to define what gets built.
For a US enterprise, that might mean NIST AI RMF for management and the CSA AI Controls Matrix for controls. OWASP and MITRE ATLAS would then cover threats. A company selling into Europe might instead swap in ISO/IEC 42001, because it can be certified.
The control catalog stays the same either way, since the AICM already maps to both.
The mistake to avoid is running each framework as its own project. Three teams writing three risk registers produce three versions of the truth, so none of them gets fixed. Instead, one shared control list, tagged with the framework references it satisfies, keeps the work in one place.
One Risk Through Four Frameworks: Prompt Injection
A crosswalk shows how this works in practice for a single risk. The table follows prompt injection through each framework and then ends with one control, one owner and one evidence artifact that satisfy all of them.
| Crosswalk field | Prompt injection entry |
|---|---|
| Risk | Hostile instructions hidden in user input or retrieved documents |
| NIST AI RMF | Map the exposure, Measure it with tests, then Manage it with controls |
| OWASP | LLM01:2025 Prompt Injection |
| MITRE ATLAS | Listed as the LLM Prompt Injection technique |
| ISO/IEC 42001 | AI risk assessment and AI risk treatment |
| Control | Input filtering, permission checks at retrieval and output validation |
| Owner | AI platform engineering lead |
| Evidence | Red-team report, signed off before each release |
One control, written once, now answers four frameworks. When an auditor asks about ISO 42001 risk treatment, the same report also serves a customer who asks about OWASP LLM01.
Core Components of an Enterprise AI Security Framework
Whatever frameworks you choose, the controls tend to fall into the same seven areas. Think of the frameworks as the building code, while these areas are the rooms where the work actually happens.
Datasheet
Elevate Data Governance, Compliance and Security of Your Organization
A Kanerika datasheet on data governance, compliance and data security, the controls that decide what an AI system can retrieve and reveal.
View the Datasheet →| Control area | What it covers | Typical owner | Evidence |
|---|---|---|---|
| AI inventory | Models, apps, copilots and agents, as well as SaaS AI features | AI governance lead | Inventory with owners and risk tiers |
| Data protection | Labels and access, enforced when the AI retrieves data | Data governance team | Access tests on each AI index |
| Identity and access | User and agent identities, scoped tool permissions | Identity team | Permission reviews per agent |
| Model and supply chain | Model sources, versions, third-party models and plugins | ML platform team | Registry records and approved sources |
| Input and output guardrails | Prompt filtering, output checks and content rules | AI engineering | Guardrail test results |
| Monitoring and response | Prompt, output and tool-call logs, AI incident playbook | Security operations | Alerts and incident runbooks |
| Testing and red teaming | Prompt injection, jailbreak and data leakage tests | Security testing team | Red-team report before each release |
Where to Focus First: Data and Supply Chain
Data protection deserves the most attention, because many AI incidents are really data security incidents. Labels and access rules from your data governance framework must apply where the AI retrieves data, not only when a person opens a file. When data cannot move at all, federated learning keeps training data where it lives while models still learn from it.
Model and supply chain controls then start with a model registry. It records where each model came from, who approved it and which version runs in production. Third-party models, plugins and datasets also deserve the same scrutiny you give open-source code.
Before buying new AI-specific tools, extend the ones you already own, including your data governance tools. For instance, identity platforms can issue agent identities, and data security posture management tools can find sensitive data in AI indexes. Your SIEM can also ingest prompt and tool-call logs, so AI-specific products only need to fill the remaining gaps.
How to Implement an AI Security Framework Step by Step
Implementation works best as a short loop that you repeat, rather than a one-off project. Each step below names an owner and the evidence that proves the step is done, so progress stays visible.
- Inventory systems and name owners. List every model, RAG app, copilot, agent and SaaS AI feature, then give each one a business owner. An AI security assessment is a fast way to build this baseline. Evidence: a living AI inventory.
- Tier each system by risk. Rate systems by the data they touch and the actions they can take. The risk team owns the tiers, so the evidence is a tier on every inventory row.
- Threat model the high tiers. Security architects walk each high-tier system through OWASP and MITRE ATLAS, or through MAESTRO when it is an agent. Evidence: one threat model per system.
- Map threats to controls. Control owners choose controls from the catalog and also record which framework references each one satisfies. Evidence: the crosswalk.
- Verify before release. AI engineering builds prompt injection, data leakage and permission tests into its MLOps pipelines, so no model or prompt change ships untested. Evidence: test results per release.
- Monitor and reassess. Security operations logs prompts, outputs and tool calls, much as data observability tracks pipelines, then reruns the threat model whenever a system changes. Evidence: dashboards, incident records and review dates.
How Risk Tiers Set the Pace
Risk tiering decides how deep every later step goes. For example, a customer-facing agent with write access sits in a higher tier than an internal drafting tool. It gets a full threat model, red-team testing and human approval before it acts.
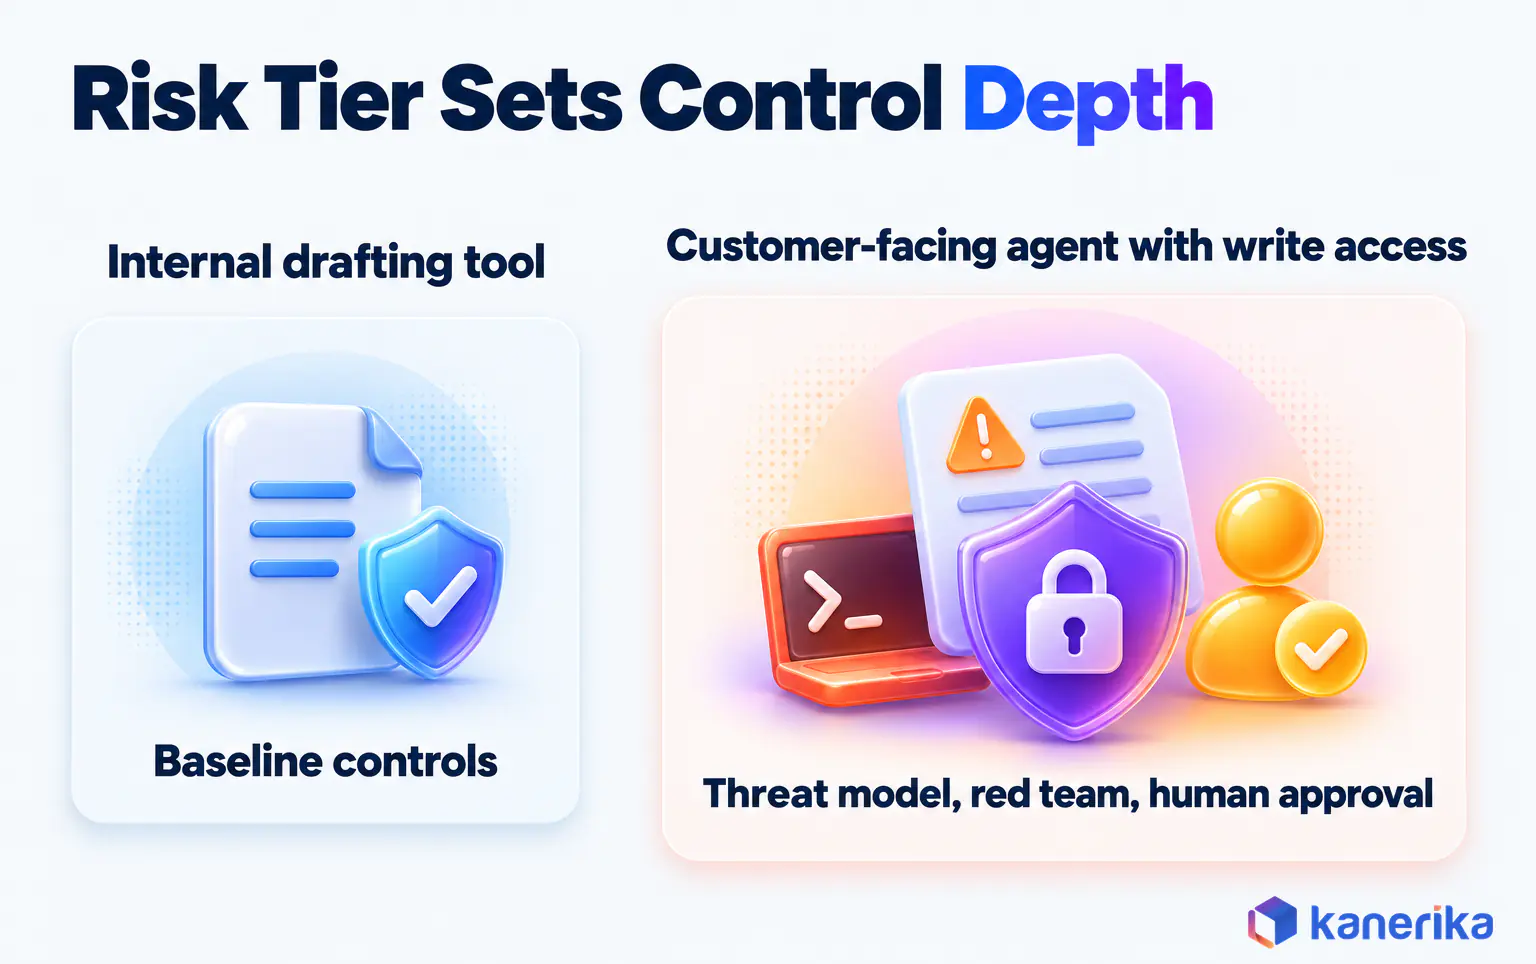
The tier also decides how fast a system moves through the AWS framework’s three phases. A high-tier agent should not leave Phase 1 until it has a scoped identity and human approval for risky actions. A low-tier drafting tool, by contrast, can move to production with baseline controls and pick up the rest as it scales.
Keep the loop short and repeatable. Low-tier systems can then follow a fixed review schedule, whereas high-tier systems should be retested whenever they gain a new data source, tool or model version.
Securing AI Agents: What the Framework Must Add
Agents change the risk because they take actions as well as give answers. An autonomous agent that can read a mailbox, query a database and send payments turns a prompt injection into a financial loss.
A framework built for chatbots therefore needs four additions for agents:
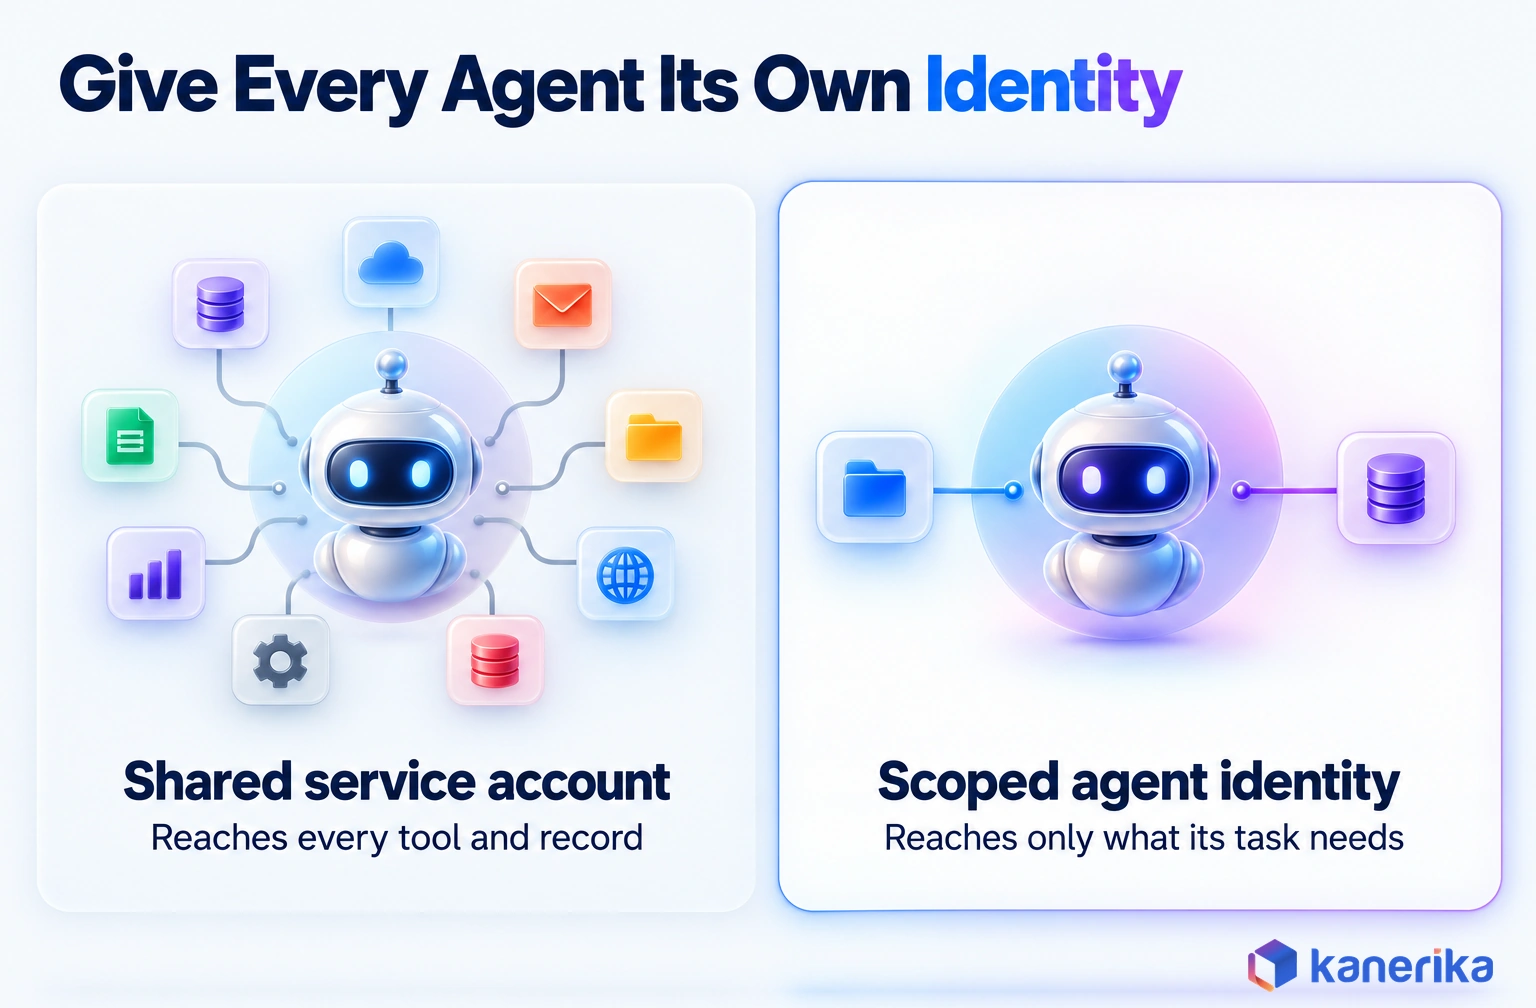
- A distinct identity per agent. Each agent gets its own credentials, so its actions can be scoped, logged and revoked.
- Scoped tool permissions. An agent should reach only the tools and records its task needs, rather than a shared admin account.
- Human approval for high-impact actions. Payments, deletions and external messages wait until a person confirms them.
- Agent-specific threat models. The OWASP agentic list and CSA MAESTRO cover risks that only appear once AI can act on its own.
Salesloft Drift shows why identity matters so much. Those stolen OAuth tokens belonged to a connected app, so the theft rode on access the app already had. Scoped, revocable credentials limit what a stolen token can reach.
Multi-agent setups raise the stakes again. When several agents hand work to each other through AI agent orchestration, every hand-off needs the same identity and permission checks.
That covers the framework-level view, while our guide to agentic AI security goes deeper into agent design and runtime controls.
Which AI Security Framework Fits Your Enterprise?
The right mix depends on your sector, your regulators and what your AI actually does. In the table, the anchor framework runs the program, while the add-ons cover its gaps. The first control is where to spend the first month.
| Scenario | Anchor framework | Add-ons | First control |
|---|---|---|---|
| US bank | NIST AI RMF | OWASP LLM list, MITRE ATLAS, CSA AICM | Inventory and tier every model, especially vendor AI |
| Healthcare provider | ISO/IEC 42001 or NIST AI RMF | OWASP LLM list, CSA AICM | Enforce patient-data access when the AI retrieves |
| SaaS company shipping LLM features | OWASP Top 10 for LLM | MITRE ATLAS, then ISO/IEC 42001 once customers ask | Prompt injection tests before each release |
| Agent-heavy operations | NIST AI RMF | OWASP agentic list, CSA MAESTRO | A distinct identity and scoped permissions per agent |
| EU market exposure | ISO/IEC 42001 | NIST AI RMF, OWASP LLM list | Classify each system by EU AI Act risk tier |
Two patterns stand out. Regulated industries anchor on a management standard because auditors ask for one. Product teams, on the other hand, start with OWASP since it produces tests they can run in a sprint.
Either way, the anchor alone is never the whole answer. Every scenario above also pairs it with a threat catalog and at least one control, because a framework without controls is only a policy.
Checklist
AI Governance Checklist
Work through AI inventory, ownership, risk tiers, access and monitoring step by step, so every release gate checks the controls that matter.
Get the Checklist →Common Mistakes That Weaken Enterprise AI Security
Frameworks rarely fail on paper. Instead, they fail in the gaps between teams, and these six gaps are worth checking first:
- Logging prompts without tool calls. Teams keep chat logs but not the actions agents took, so an incident cannot be traced from the prompt to what changed.
- Skipping the inventory. Teams jump to tools before they know which AI systems exist, so unlisted systems never get controls.
- Treating one framework as complete. NIST AI RMF without a control catalog leaves half the work undone, and so does OWASP without a management layer.
- No identity for agents. Agents that run under shared service accounts cannot be scoped or traced when something goes wrong.
- No red teaming. Controls that were never attacked are still assumptions, which is why AI red teaming matters. So test prompts, retrieval and tool use before each major release.
- Ignoring shadow AI. Employees reach for public AI tools when approved ones are missing, so offer sanctioned options and monitor for the rest.
Each of these mistakes is cheaper to fix in design than after an incident. A short checklist review at every release gate catches most of them before they reach production.
How Kanerika Secures Enterprise AI
Kanerika treats AI security as part of the data and AI platform, rather than an add-on at the end. Our AI services follow a five-stage method that turns the frameworks above into owned, tested controls.
- Assess. Review the AI and data security posture, especially the AI inventory and how data reaches each system.
- Design. Build the framework and control map, together with the crosswalk that ties each control to its framework references.
- Implement. Put data, identity and AI controls in place, such as access enforced at retrieval, agent identities and guardrails.
- Test. Run red-team prompts and permission checks before release.
- Operate. Monitor, respond and reassess as systems and threats change.
One example is a leading investment bank that needed fast answers from unstructured RFI documents as well as its databases. Kanerika deployed KlarityIQ for documents and Karl for database queries behind one chat interface. It also applied secure role-based access control at the retrieval layer.
That design is the opening scenario in reverse, because every answer is filtered by what the user is allowed to see. The bank reported 43% faster information retrieval and 35% higher workforce efficiency. It also reached 100% role-based compliance at the point of retrieval.
Case Study
43% Faster Document Retrieval for an Investment Bank
Kanerika put KlarityIQ and Karl behind one chat interface with role-based access enforced at retrieval, reaching 100% role-based compliance at the point of retrieval.
Read the Case Study →Read More: AI Governance Consulting Services for Enterprises
What Should Enterprises Do First?
Start small and concrete, since three moves in the first quarter give any program a base to build on.
First, build the AI inventory, including copilots and SaaS features, and name an owner for each system. Next, choose your anchor framework, NIST AI RMF or ISO/IEC 42001, and adopt OWASP and MITRE ATLAS as the shared threat vocabulary. Finally, enforce access at retrieval and give every agent its own identity.
The third move matters most, because access at retrieval and agent identity close the gaps behind the Salesloft Drift and assistant-leak cases in this guide.
So what does an enterprise need from an AI security framework in 2026? It needs a layered set of standards turned into controls with owners, tests and evidence, starting with the systems that touch its most sensitive data.
Frequently Asked Questions
What is an AI security framework?
An AI security framework is a structured way to identify the threats that target AI systems and answer each one with a control. It covers models, retrieval apps, copilots, agents and AI features inside SaaS tools. Each control gets an owner, a test that proves it works and evidence an auditor can check, so security becomes measurable.
What is the best AI security framework for enterprises?
No single framework covers everything, so the best choice is a layered set. Use NIST AI RMF or ISO/IEC 42001 to manage risk, OWASP and MITRE ATLAS to name threats, and a control catalog such as the CSA AI Controls Matrix. Pick ISO/IEC 42001 as the anchor when customers or regulators expect a certificate.
How do AI security frameworks address AI agents?
Agent-focused guidance adds controls for systems that act, not just answer. The OWASP Top 10 for Agentic Applications for 2026 lists the main risks, and CSA MAESTRO models agent threats across seven layers. In practice, give each agent its own identity, scope its tool permissions tightly and require human approval for payments, deletions and external messages.
How does MITRE ATLAS help secure AI systems?
MITRE ATLAS is a public knowledge base of adversary tactics, techniques and procedures that target AI systems. Threat modelers use it to walk an AI system through the ways an attacker could get in. Red teams use the same techniques to plan realistic tests, so their findings map to a vocabulary that security and engineering teams share.
Which AI security frameworks can you be certified against?
ISO/IEC 42001 is the main AI standard that organizations can be audited and certified against by accredited bodies. NIST AI RMF, OWASP lists, MITRE ATLAS and Google SAIF are guidance with no certificate. The CSA AI Controls Matrix maps to ISO 42001 and ISO 27001, which helps teams reuse their control evidence during a certification audit.
What is an example of an AI security threat?
Prompt injection is the most common example, listed as LLM01:2025 in the OWASP Top 10 for LLM Applications. An attacker hides instructions in user input, an email or a shared document, and the model follows them. In 2025, Cybernews researchers showed a single prompt could make Lenovo’s chatbot Lena leak session cookies through cross-site scripting flaws.
Which AI security framework suits healthcare and banking?
Both sectors usually anchor on a management standard, because auditors expect one. Banks often start with NIST AI RMF, while healthcare providers choose ISO/IEC 42001 or NIST AI RMF. Both then add the OWASP LLM list and the CSA AI Controls Matrix. The first control is usually access enforced where the AI retrieves sensitive records.
What are AI security tools?
AI security tools protect models, prompts and agents. They include prompt filters and guardrails, model scanners, AI red-teaming tools, posture management for AI services and monitoring for prompts and tool calls. Before buying them, extend what you already own, because identity platforms, data security posture management tools and your SIEM can cover a large share of the work.
How does the EU AI Act affect an AI security framework?
The EU AI Act sorts AI systems into four risk tiers: unacceptable, high, limited and minimal. It entered into force on August 1, 2024, with prohibitions from February 2, 2025. Published legal analyses say a 2026 amendment package moved most high-risk obligations to late 2027 and 2028, so classify each system by tier now.
What are the main AI security frameworks and standards?
The main options are NIST AI RMF with its Generative AI Profile, ISO/IEC 42001, the OWASP Top 10 lists for LLM and agentic applications, MITRE ATLAS, Google SAIF and the CSA AI Controls Matrix with MAESTRO. Platform frameworks from AWS and Databricks add service-level controls. Each covers a different layer, so enterprises usually combine three or four.
What are the core components of an AI security framework?
Most frameworks share seven control areas. They are an AI inventory, data protection, identity and access including agent identities, model and supply chain controls, input and output guardrails, monitoring and incident response, and testing with red teaming. Each area needs a named owner and evidence, such as access tests, registry records or red-team reports.
What is the NIST AI Risk Management Framework?
The NIST AI Risk Management Framework is a voluntary framework from the US National Institute of Standards and Technology. Version 1.0 was released on January 26, 2023. It organizes AI risk work into four functions: Govern, Map, Measure and Manage. NIST added a Generative AI Profile, NIST-AI-600-1, on July 26, 2024 for generative models.
Is the NIST AI RMF mandatory?
No. NIST states that the AI RMF is intended for voluntary use, so no US law requires it on its own. Many enterprises still adopt it because it gives a shared structure for AI risk work. Contracts, sector regulators or customer security reviews may reference it, which can make it a practical expectation even without a mandate.
What is the difference between ISO/IEC 42001 and NIST AI RMF?
ISO/IEC 42001 is an international management system standard for AI, published in December 2023, and organizations can be audited and certified against it by accredited bodies. NIST AI RMF is a voluntary US framework with no certificate. Both structure how you govern AI risk, and many enterprises use NIST for guidance and ISO 42001 for assurance.
What is the difference between AI security and AI governance?
AI governance decides whether and how the business should use AI, including policy, accountability and approval of use cases. AI security protects AI systems from attack, misuse and data leakage once they exist. The two meet in shared controls, such as access rules and risk tiers, but a well-governed model can still be attacked if nobody tests it.
Why can't traditional cybersecurity frameworks fully secure AI?
Traditional frameworks protect networks, endpoints and cloud accounts, but AI adds attack paths that run through language and data. A model can be manipulated by prompt injection, leak information through its answers or misuse tools as an agent. These threats need AI-specific tests, retrieval-level access controls and agent identities that classic control sets do not describe.
How should enterprises choose the right AI security framework?
Start with your regulators and customers, then look at what your AI actually does. US-led programs usually anchor on NIST AI RMF, while firms that need a certificate choose ISO/IEC 42001. Add OWASP and MITRE ATLAS for threats, then a control catalog. Agent-heavy teams should also add the OWASP agentic list and CSA MAESTRO.