TL;DR
Data governance examples are the rules, roles and checks a company uses to keep its data correct and safe. A data ownership policy is one example. Labels that mark personal data are also an example. So are quarterly reviews of who can see sensitive data, and checks that stop bad records from loading. Each program also names data owners, data stewards and a small council that approves the rules. Most teams start with one business area and show results within about 90 days.
Key Takeaways
- The most useful data governance examples are artifacts you can copy, such as policy wording, a control list, a RACI chart and a 90-day plan.
- Six policies cover most programs, namely ownership, classification, access, retention, data quality and acceptable AI use.
- Controls turn a policy into evidence, so every control needs an owner, a frequency and an audit trail.
- A federated operating model suits most large enterprises, with a central council setting standards and domain stewards applying them.
- Regulators have penalized Citibank, Morgan Stanley and Marriott over weak data governance, device disposal and data security.
- Kanerika’s Microsoft Purview programs cut data discovery time by 57% for a healthcare provider and reached 100% compliance adherence for a global bank.
The Week-Long Search for One Number
Picture a letter from a regulator that asks just one question. Where did the risk figure in last quarter’s filing come from?
The analytics team knows which dashboard shows it, but little else. However, nobody can say which source tables fed it, who approved the logic, or whether a filter changed in March.
As a result, five people spend a week rebuilding the trail by hand. The figure turns out to be correct, yet the company had no ready evidence to prove it.
That missing evidence is exactly what data governance supplies, because it records decisions as they happen. For that reason, the examples below are the working parts of real programs, written in the same plain, defensible language you’d expect from a website provides essay writing service that has to hold up to a reader’s scrutiny. They cover policy wording, controls, roles and frameworks, as well as a 90-day plan and the metrics leaders actually read.
What Data Governance Looks Like in Practice
Data governance is the set of decision rights, rules and controls behind your data. In other words, it decides who owns data, who may use it, and how good it must be.
The data governance pillar guide covers the theory, while this article sticks to examples you can adapt.
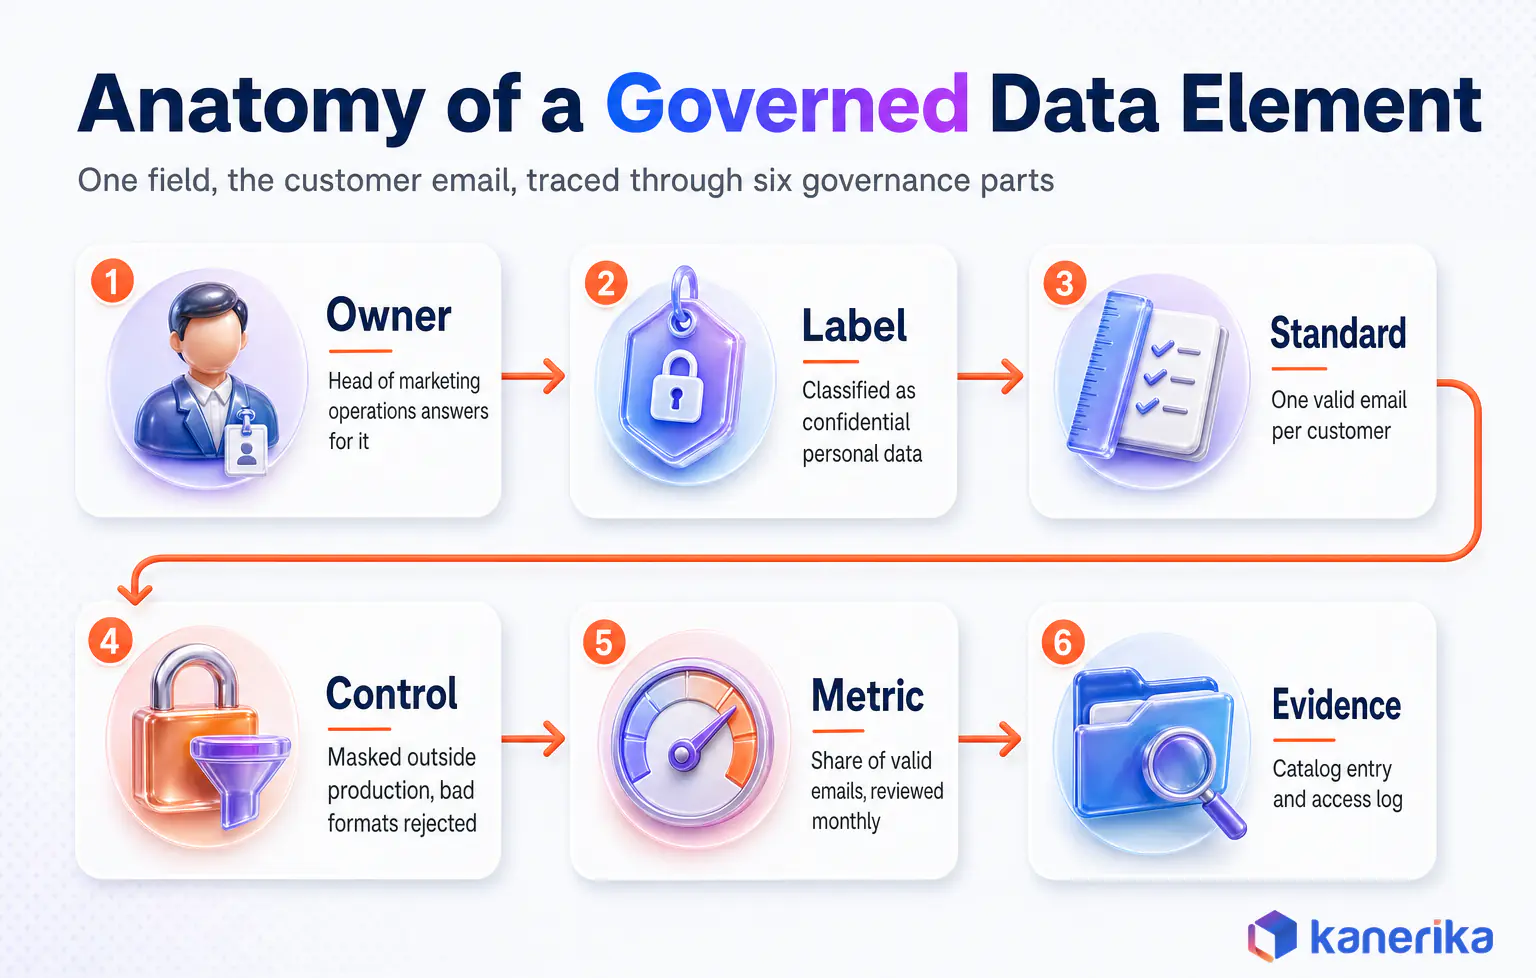
Take one field, such as the customer email address, and follow it through a governed program. First, it has an owner, usually the head of marketing operations, who answers for how it is used. It also carries a label, Confidential personal data, which triggers masking in test environments.
Then a standard says each customer holds one valid email in a set format. Next, a quality rule rejects records that break it, and a steward reviews the rejects each week. Finally, the catalog shows all of this in one entry, and the access log proves who read the field and when.
Together, owner, label, standard, control, metric and evidence make one governed data element. When you scale that pattern to your 20 most important data elements, you have the core of a program.
Data Governance vs Data Management
Governance decides the rules and who is accountable for them, whereas data management does the daily work. That work follows those rules, such as building pipelines, storing data and running backups. The comparison of data governance vs data management goes deeper on where one ends and the other begins, as well as how they overlap.
Why These Examples Matter Now
AI has raised the stakes, especially for data quality and access. Gartner found that 63% of organizations lack, or are unsure they have, the right data management practices for AI. It also expects companies to abandon 60% of AI projects unsupported by AI-ready data through 2026.
Still, people matter as much as tools. Meanwhile, Gartner surveyed 223 data and analytics leaders in March 2026.
In that survey, cultural resistance outranked funding as the main reason governance initiatives fail, by 60% to 40%. For this reason, concrete and shared examples are one of the fastest ways to get business teams on board.
Case Study
Zero Breaches and 100% Compliance for a Global Bank
Kanerika used Microsoft Purview to automate classification of PII, PCI and PHI, and also to track lineage across SAP, Dynamics 365 and core banking systems.
Read the Case Study →12 Data Governance Examples at a Glance
Most governance programs are built from the same dozen parts, whatever the industry. For example, the two tables below list each one with the person who usually owns it and the evidence that shows it is working.
Rule and Control Examples
Table 1: Six rule and control examples, who owns them and the evidence they leave
| Example | What it looks like in practice | Typical owner | Evidence it works |
|---|---|---|---|
| Data ownership policy | Every critical dataset lists a named business owner, so issues have a clear route | Chief data officer | Share of critical datasets with an owner, measured monthly |
| Classification labels | Tables and files tagged by sensitivity, such as Confidential or Restricted | Data owners, security | Share of sensitive columns labeled |
| Access reviews | Owners recertify who can read restricted data before each quarter closes | Data owners | Review completion rate as well as revoked grants |
| Masking of personal data | Names, emails and account numbers masked when used outside production | Platform team | Masking policy coverage |
| Data quality rules | Loads fail or quarantine when a rule such as “email must be valid” breaks | Data stewards | Quality score per critical data element, such as customer ID |
| Lineage capture | Each report column traces back to its source tables, even across tools | Platform team | Share of certified reports with lineage, especially board reports |
People, Process and Measurement Examples
Table 2: Six people, process and measurement examples, who owns them and the evidence they leave
| Example | What it looks like in practice | Typical owner | Evidence it works |
|---|---|---|---|
| Business glossary | One agreed definition for terms such as “active customer” or “net revenue” | Data stewards | Terms approved, terms in use |
| Retention schedule | Records deleted or archived once their retention period ends | Compliance, records management | Deletion jobs run on time |
| Data catalog | A searchable inventory of datasets, as well as their owners and labels | Governance office | Monthly active catalog users |
| Governance council | A monthly forum that approves policies and also settles disputes | Chief data officer | Decisions logged, issues closed |
| KPI scorecard | A dashboard of governance metrics that leadership reviews every month | Governance office | Trend of scores over quarters |
| Acceptable AI data use policy | Rules for which data may feed AI tools such as copilots, agents and models | AI governance lead | AI apps that use approved sources only, rather than any file |
Where to Start
Nobody needs all twelve on day one. Instead, start with ownership, classification, access reviews and quality rules for one domain, then add the rest as the program grows.
Data Governance Policy Examples With Sample Wording
A policy states what must be true, who it applies to and how compliance is checked afterward. The six policies below cover most enterprise programs, and each sample is also short enough to fit on one page.
1. Data Ownership Policy
This policy makes a named person accountable for each critical dataset, rather than a department. Without it, every other rule has nobody to enforce it, so this policy comes first.
Every dataset listed as critical in the enterprise catalog has one named data owner at director level or above. The owner approves access, accepts the quality standard, and also reviews the dataset at least once a year.
2. Data Classification Policy
Classification tells people and systems how carefully to handle data, so it drives most other controls. Four levels are enough for most companies, because more levels usually mean more mistakes.
All data is classified as Public, Internal, Confidential or Restricted. Personal, payment and health data is always Confidential at minimum. New sources are classified before they are published to analysts.
3. Data Access Policy
Access rules follow least privilege, so people get only the minimum data needed for their role. The data access governance framework explains role-based and attribute-based models in more detail than this example.
Access to Confidential and Restricted data is granted by role, approved by the data owner, and reviewed every quarter. Also, shared or generic accounts may not access Restricted data.
4. Data Retention and Deletion Policy
Keeping data forever raises storage costs and breach exposure, so retention needs rules too. A retention policy therefore sets how long each record type is kept and how it is destroyed.
Each record type has a retention period in the retention schedule. When the period ends, records are deleted or anonymized within 30 days, and deletion is logged. Devices that stored Confidential data are wiped and certified before disposal.
5. Data Quality Policy
Quality policies stop arguments about whose number is right, because everyone uses the same test. They name the data elements that matter and then set a measurable standard for each.
Critical data elements have documented quality rules, such as completeness, validity and timeliness. Scores are published monthly, and any rule below its threshold for two months is escalated to the data owner.
6. Acceptable AI Data Use Policy
Copilots and agents read whatever they can reach, so AI needs its own data rules. This policy therefore ties AI use back to the classification and access rules above.
AI applications may only use data sources approved in the catalog for AI use. Restricted data may not be sent to external models either. Finally, every production AI application has an owner and a record of the data it uses.
Wording also shifts by industry. A bank adds references to risk data aggregation, a hospital adds HIPAA’s minimum necessary standard, and a manufacturer adds supplier and product master data. In practice, short policies with a named owner and a review date get followed far more often than long manuals nobody opens.
Data Governance Standards Examples
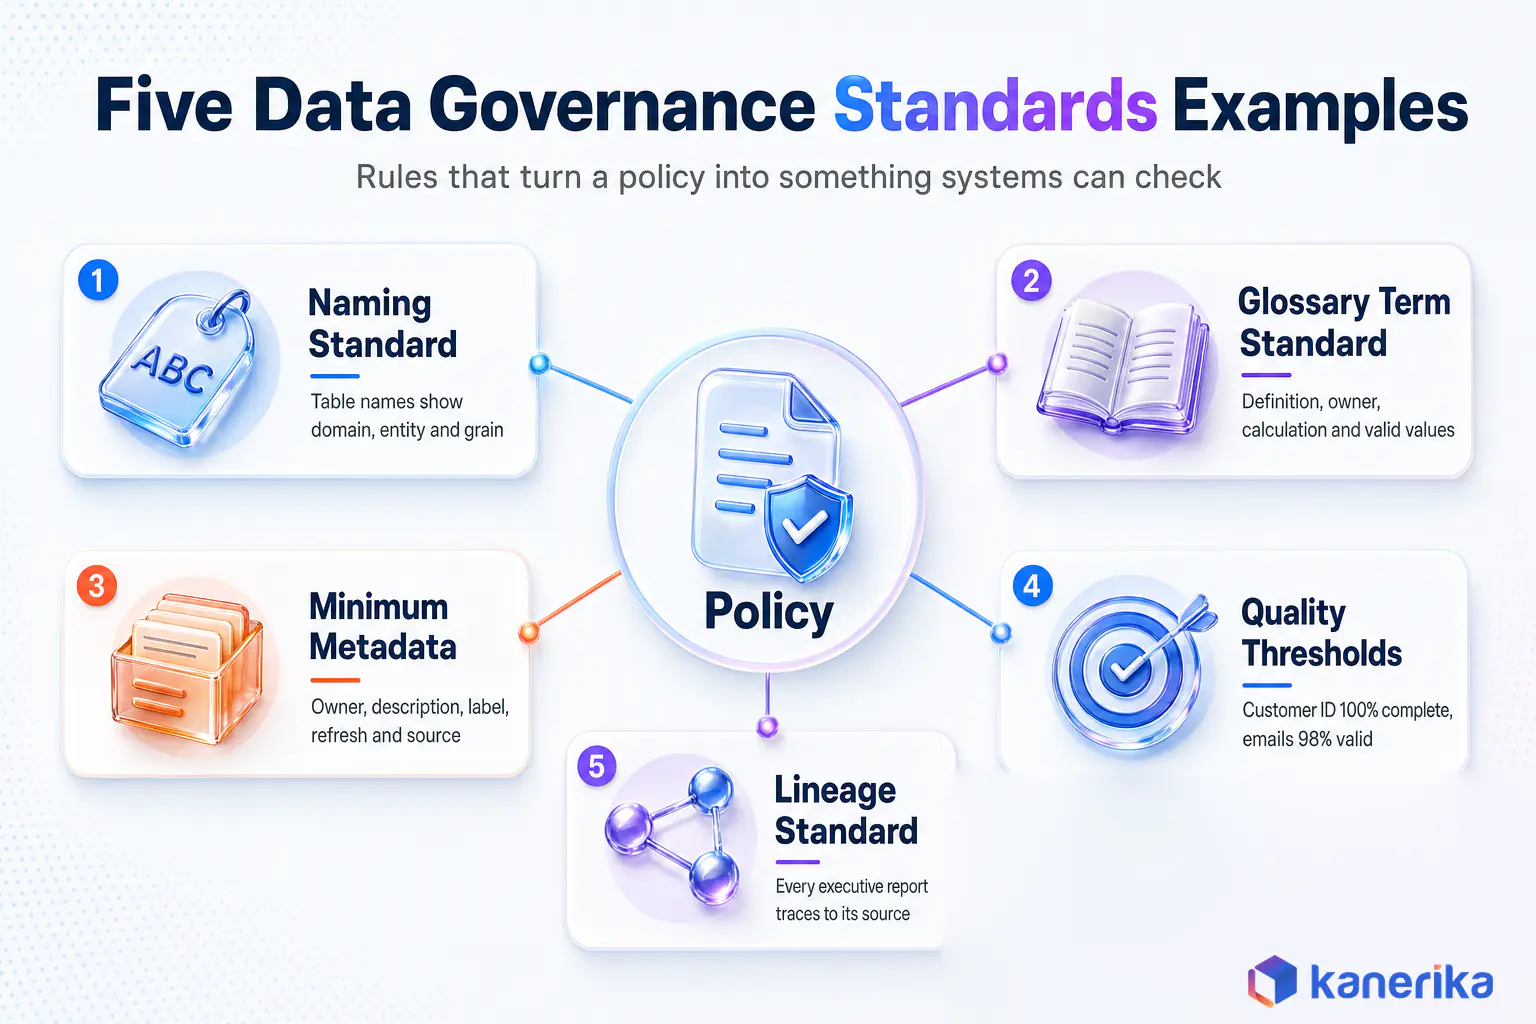
Standards turn a policy into something a system can check, such as a tag, a field or a threshold. For instance, when a policy says personal data must be protected, a standard says exactly which columns count and how fast they must be tagged.
- Naming standard. Tables follow domain_entity_grain, such as sales_order_daily, so people can guess what a table holds.
- Glossary term standard. Each business term has a definition and an owner, as well as a calculation, valid values and an example.
- Minimum metadata standard. No dataset is published until it has an owner, a description, a classification, a refresh schedule and a source system.
- Quality threshold standard. Critical elements such as customer ID must be 100% complete, and email addresses at least 98% valid.
- Lineage standard. Any report shown to executives or regulators must trace every figure back to a source system, especially financial figures.
Policy, Standard, Control and Procedure Compared
The difference between a policy, a standard, a control and a procedure confuses many teams, because the words overlap in everyday use. Table 3 therefore shows all four for the same requirement.
Table 3: Policy, standard, control and procedure compared with one example
| Artifact | What it answers | Example | Who approves it |
|---|---|---|---|
| Policy | What must be true | Customer personal data is labeled Confidential, so only approved roles can see it | Governance council |
| Standard | How exactly we meet the policy | Columns such as email, phone or national ID carry the “PII” tag within 10 days of creation | Data governance office |
| Control | How we prove it happens | A weekly scan flags untagged PII columns and then opens a ticket for the steward | Platform and security teams |
| Procedure | Who does what, step by step | Steward reviews the ticket, tags the column, and finally records the fix in the catalog | Domain data owner |
Data Governance Controls Examples
Controls are how a company proves its policies work, because each one leaves a record. Preventive controls stop a problem before it happens, and detective controls find it afterward and raise an alert.
Table 4: Data governance controls examples with the evidence each one produces
| Control | Type | Example | Evidence for auditors |
|---|---|---|---|
| Role-based access with least privilege | Preventive | Analysts get read access to curated tables rather than raw PII zones | Grant lists exported monthly |
| Quarterly access review | Detective | Owners confirm or revoke each user before the review closes | Signed review log, revocations |
| Dynamic masking | Preventive | Card numbers show only the last four digits unless the user holds a named role | Masking policy and test results |
| Sensitivity labels and DLP | Preventive | Files labeled Restricted are blocked when someone emails them outside the company | DLP policy matches and blocks |
| Quality gate at load | Preventive | A pipeline rejects rows with missing customer IDs and then alerts the steward | Rule results per run |
| Lineage capture | Detective | Column-level lineage for every certified finance report, especially regulatory ones | Lineage graph per report |
| Retention and deletion job | Preventive | Marketing leads older than 24 months are deleted automatically | Job logs with record counts |
| Secure disposal of devices and media | Preventive | Decommissioned drives are wiped and certified before resale | Disposal certificates as well as vendor audits |
Evidence and Disposal Controls
Every control in the table also produces evidence an auditor can check. Otherwise, a control with no record of when it ran and what it found gives an auditor nothing to check.
Disposal is the control teams forget most often, especially for old hardware.
The SEC fined Morgan Stanley Smith Barney $35 million in 2022 after devices holding customer data were not properly wiped. That was a gap in exactly the disposal controls listed above, so it is a useful warning. For Microsoft estates, Microsoft Purview data loss prevention and Purview sensitivity labels handle many of the preventive controls in the table.
Datasheet
Elevate Data Governance, Compliance and Security
How Kanerika’s governance services on Microsoft Purview handle classification and access protection, as well as regulatory compliance for enterprise data.
View the Datasheet →Data Governance Roles and RACI Example
Unclear ownership is one of the most common reasons governance programs stall, because problems have nowhere to go. A short list of roles and a RACI chart fix that, since they make every decision somebody’s job.
- Chief data officer or governance lead. Sponsors the program, sets priorities and then reports progress to leadership.
- Governance council. Business and technology leaders who approve policies and also resolve disputes, usually monthly.
- Data owner. A business leader accountable for a domain such as customer, product or finance data.
- Data steward. The day-to-day expert who maintains definitions, quality rules and issue queues, especially for critical data. The guide to data stewardship also covers the role in depth.
- Platform team. Engineers who implement access, masking, lineage and quality checks so the rules run in the data platform.
- Security and compliance. Map regulations to controls and then test that the controls work.
RACI Chart Example
The chart below assigns each core activity to one accountable role, so nobody has to guess who decides.
Table 5: RACI example for core data governance activities (R = responsible, A = accountable, C = consulted, I = informed)
| Activity | CDO | Council | Data owner | Data steward | Platform team | Security and compliance |
|---|---|---|---|---|---|---|
| Approve a new policy | A | R | C | C | I | C |
| Define a glossary term | I | A | C | R | I | I |
| Approve access to restricted data | I | I | A | C | R | C |
| Fix a data quality issue | I | I | A | R | C | I |
| Classify a new dataset | I | I | A | R | C | C |
| Run the quarterly access review | I | I | A | C | R | C |
| Report governance KPIs | A | C | C | R | C | I |
A RACI chart only works when real names replace the role titles. Review it at each council meeting, because owners change jobs faster than charts get updated.
Case Study
90% Compliance Adherence for a Healthcare Network
A central Microsoft Purview catalog, a classification framework and steward roles cut data discovery time by 57%, so clinicians and analysts found trusted data faster.
Read the Case Study →Data Governance Operating Model Examples
The operating model decides where governance decisions are made and who makes them. The right choice depends on company size as well as how independent the business units and engineering teams are.
Table 6: Data governance operating model examples compared
| Model | How decisions are made | Best fit | Watch out for |
|---|---|---|---|
| Centralized | One governance team writes and also enforces every rule | Mid-size firms, especially single-platform estates | The central team becomes a queue that slows every request |
| Federated (hub and spoke) | A central council sets standards, domain stewards apply them | Large enterprises with several business units | Domains drift from shared definitions unless someone reviews them regularly |
| Decentralized | Each business unit governs its own data | Holding companies with separate, unrelated businesses | No shared view of risk, so cross-unit data stays siloed |
| Data mesh | Domains own data products under global, automated guardrails | Engineering-mature firms with strong platform teams | Fails unless self-serve tooling and policy as code are in place |
Most large enterprises eventually land on the federated model. It keeps one set of standards while finance, sales and operations stewards work at their own pace. Teams moving toward a data mesh add automated guardrails so domains can publish data products without waiting on a central queue.
Data Governance Framework Examples
A framework gives a program its structure and vocabulary, so teams stop arguing over terms. Few companies adopt one wholesale. Instead, most combine a general framework with an industry or AI-specific one.
- DAMA-DMBOK places governance at the center of eleven data management knowledge areas and is the most widely used reference.
- The DGI Data Governance Framework focuses on decision rights, accountability and the governance office, organized into ten components.
- BCBS 239 sets principles for how banks aggregate and report risk data, which makes lineage and data quality supervisory issues.
- The NIST AI Risk Management Framework adds a Govern function for AI systems, covering data provenance, roles and risk tolerance.
Table 7: Data governance framework examples and what to take from each
| Framework | Published by | Best for | What teams usually adopt from it |
|---|---|---|---|
| DAMA-DMBOK | DAMA International | Enterprise-wide data management programs | Knowledge areas and role definitions, as well as shared vocabulary |
| DGI Data Governance Framework | The Data Governance Institute | Setting up decision rights and also a governance office | Its ten components, such as rules, decision rights and processes |
| BCBS 239 | Basel Committee on Banking Supervision | Banks that aggregate risk data for regulators | Principles for accuracy, completeness and timeliness of risk data |
| NIST AI RMF | US National Institute of Standards and Technology | Governing data and models used by AI systems | The Govern, Map, Measure and Manage functions |
Combining Frameworks
A practical pattern is to use DAMA-DMBOK for scope, DGI for decision rights, and an industry framework for the regulator’s view. The data governance framework guide walks through building your own, and the data governance maturity model shows how to measure progress against it.
Data Governance Process Example: Onboarding a New Dataset
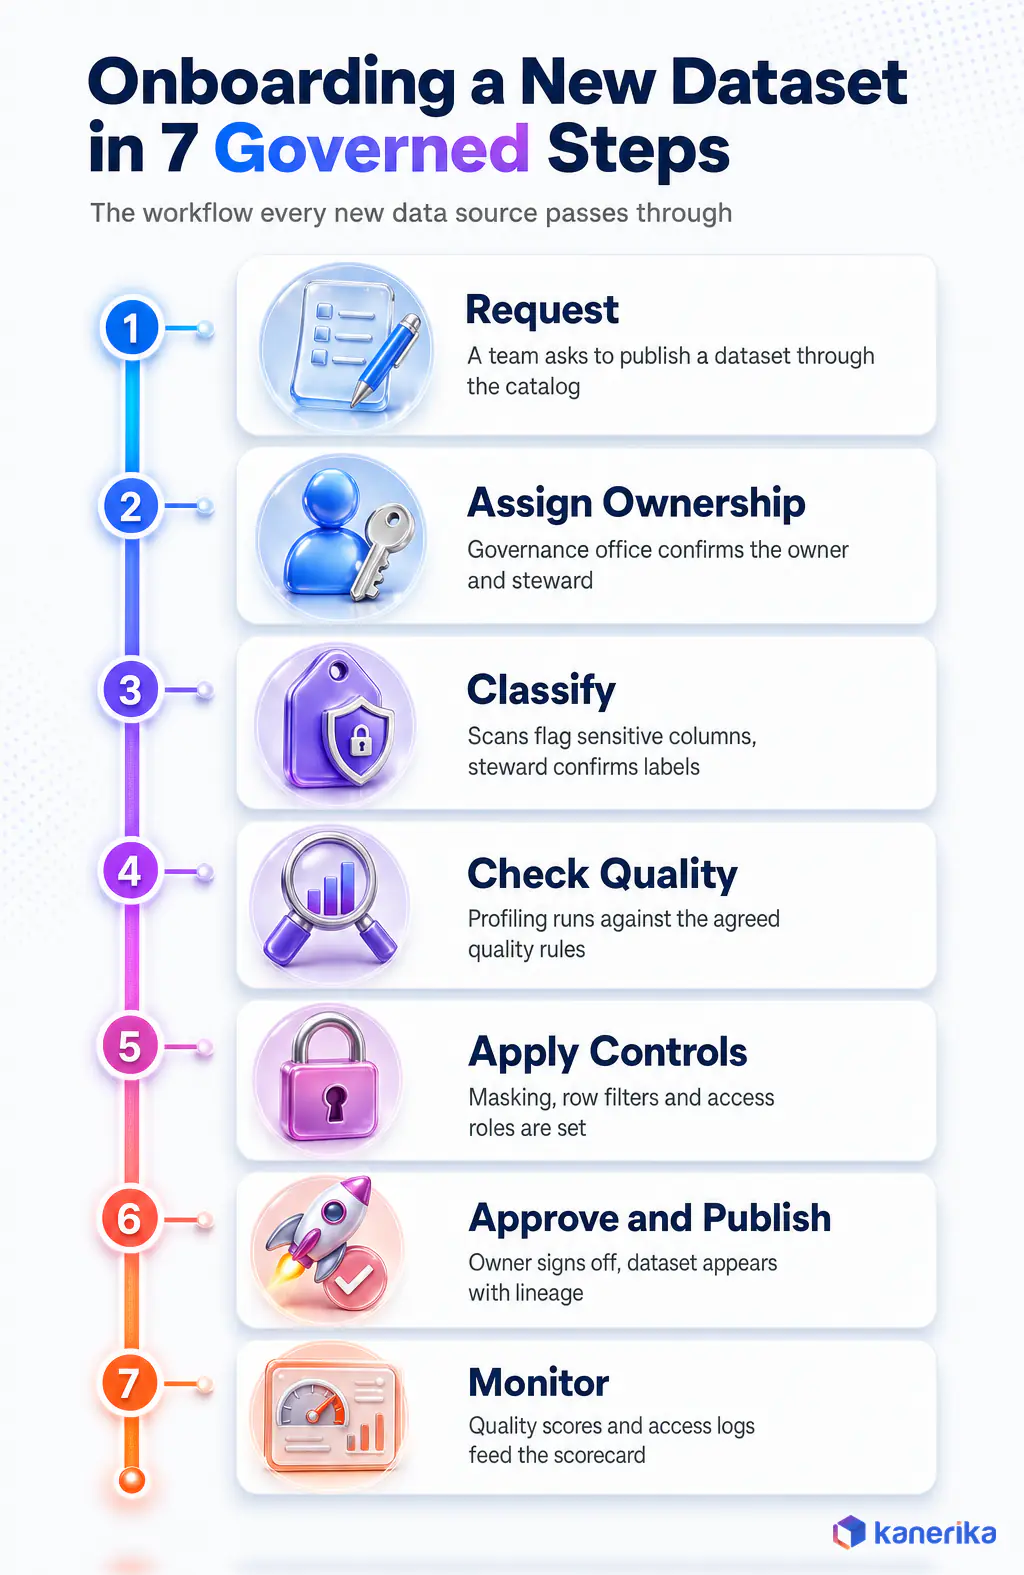
Processes are where governance meets daily work, so they decide whether people follow it. Dataset onboarding is a good first process to formalize, because every new source passes through it.
- Request. A team asks to publish a new dataset, such as a CRM export, through a form in the catalog.
- Assign ownership. The governance office confirms the data owner and steward before any work starts.
- Classify. Automated scans flag personal or sensitive columns, and then the steward confirms the labels.
- Check quality. Profiling runs against the agreed rules, while failures go back to the source team.
- Apply controls. Masking, row-level filters and access roles are then set according to the classification.
- Approve and publish. Once the owner signs off, the dataset appears in the catalog with its lineage.
- Monitor. After that, quality scores and access logs feed the monthly KPI scorecard.
Other processes follow the same shape, such as a trigger, an owner, an approval and a record. Typical ones are access requests, data issue triage, glossary changes and the yearly certification of critical reports.
Data Governance Architecture Example Across Purview, Unity Catalog and Snowflake Horizon
A governance architecture connects the data sources, the platforms that store and process data, the catalog and policy layer, and the people who consume data. Most enterprises run more than one platform, so the real question is which tool governs what.
A common pattern uses Microsoft Purview as the enterprise-wide map and labeling layer. Platform-native tools such as Databricks Unity Catalog and Snowflake Horizon then enforce fine-grained access inside each platform.
Table 8: How common governance controls map to Microsoft Purview, Databricks Unity Catalog and Snowflake Horizon
| Governance need | Microsoft Purview | Databricks Unity Catalog | Snowflake Horizon |
|---|---|---|---|
| Inventory and search | Data Map scans across sources such as Azure, Fabric, on-premises and other clouds | Catalog of tables, volumes, models and functions in one metastore | Catalog and search across Snowflake objects |
| Classification | Built-in and custom classifiers, sensitivity labels | Tags, plus data classification in the catalog | Automatic sensitive data classification and object tags |
| Access control | Access policies and label-based protection | Grants, row filters and column masks | Role-based access, masking and row access policies |
| Lineage | Lineage across supported sources and Fabric items | Automatic table and column lineage for workloads on Databricks | Lineage and access history for Snowflake objects |
| Scope | Broadest reach across the Microsoft estate and many third-party sources | Deepest inside Databricks workspaces, though narrower outside them | Deepest inside Snowflake accounts, though narrower outside them |
Breadth Versus Depth
The trade-off is breadth against depth. Purview sees the most sources, while Unity Catalog and Horizon enforce the most detailed rules inside their own engines. The side-by-side review of Unity Catalog, Microsoft Purview and Collibra and the guide to the Snowflake Horizon catalog compare the tools in more detail.
On-Demand Webinar
Secure, Govern, Thrive With Microsoft Purview
Kanerika’s on-demand session on building a Purview-based governance and security strategy, especially across Microsoft estates.
Watch the Webinar →Data Governance Plan Example: The First 90 Days
A governance plan works best when it is small and time-boxed, because early results fund the next phase. For example, the plan below covers one domain in 13 weeks and ends with evidence leaders can see.
Table 9: Data governance plan example for the first 90 days
| Weeks | Activities | Deliverables | Success measure |
|---|---|---|---|
| 1 to 3 | Pick one domain, name the sponsor and owner, then list 15 to 25 critical data elements | Charter, domain scope, stakeholder map | Sponsor signed off, owners named |
| 4 to 6 | Write the six core policies, agree glossary terms, and then profile data quality | Policies v1, glossary v1, quality baseline | Baseline scores recorded |
| 7 to 9 | Scan and classify sources, apply labels and masking, then turn on quality rules | Catalog entries, labels, rules in production | Share of critical elements classified |
| 10 to 13 | Run the first access review, publish the KPI scorecard, and finally plan domain two | Scorecard, review log, next-domain plan | Improvement against baseline shown to leadership |
Choosing the First Domain
Pick the first domain by the size of its business pain, since that is what leaders notice. Customer data is common because it touches revenue, privacy law and reporting at once, so early wins are visible.
Also, resist the urge to buy a tool first. A plan with named owners and five good quality rules delivers more in 90 days than a catalog nobody maintains.
Checklist
Data Governance Checklist
A step-by-step checklist for launching a governance program, from ownership and policies through to controls and metrics.
Get the Checklist →Data Governance Metrics and KPI Examples
Metrics keep a program funded, especially after the first year. Leadership rarely reads policy documents, although it will read a one-page scorecard that shows coverage and quality moving in the right direction.
Table 10: Data governance metrics and KPI examples
| KPI | How to measure it | Example target |
|---|---|---|
| Ownership coverage | Critical datasets with a named owner divided by all critical datasets | 100% for the first domain |
| Classification coverage | Sensitive columns labeled divided by sensitive columns found by scans | Above 95% within two quarters |
| Data quality score | Share of records passing the rules for each critical data element | A target set per element, reviewed monthly |
| Issue resolution time | Median days from a logged data issue until its fix | Falling quarter over quarter |
| Access review completion | Reviews finished on time divided by reviews due | 100% each quarter |
| Catalog adoption | Monthly active users searching the catalog, especially business users | Rising after each domain launch |
| Report certification | Executive reports with an owner as well as lineage and quality checks | All board-level reports |
Turning Metrics Into a Business Case
A governance business case links each metric to money or risk, so budgets have a basis. Typical cost lines are hours spent reconciling reports, delayed regulatory filings, duplicate tools and data, and breach exposure.
Breach exposure is also easy to size. IBM’s 2025 research puts the global average cost of a data breach at $4.44 million. Therefore, even a modest cut in exposure is worth tracking.
Use your own baseline from the first 90 days rather than borrowed return-on-investment figures.
Enforcement Examples That Show What Weak Governance Costs
Public enforcement actions are the clearest examples of governance gaps, because regulators describe the failure in writing. Each case below also comes from the regulator’s own announcement.
Table 11: Enforcement examples that show what weak data governance costs
| Year and regulator | What happened | Governance lesson |
|---|---|---|
| 2020, OCC | $400 million civil money penalty against Citibank for long-standing deficiencies including data governance and internal controls | Regulators treat risk data governance as a supervisory requirement |
| 2024, OCC and Federal Reserve | A further $75 million OCC penalty for slow remediation and no process to monitor how data quality issues affected regulatory reporting | Quality controls must connect to the reports regulators actually read |
| 2022, SEC | $35 million penalty for Morgan Stanley Smith Barney after devices holding data on about 15 million customers were not properly disposed of | Retention and disposal are governance controls, including for hardware |
| 2024, FTC and 49 states | FTC order against Marriott and Starwood after breaches affecting more than 344 million customers, plus a separate $52 million payment to the states | Security controls and data deletion rights need owners and evidence |
Data Governance Examples by Industry
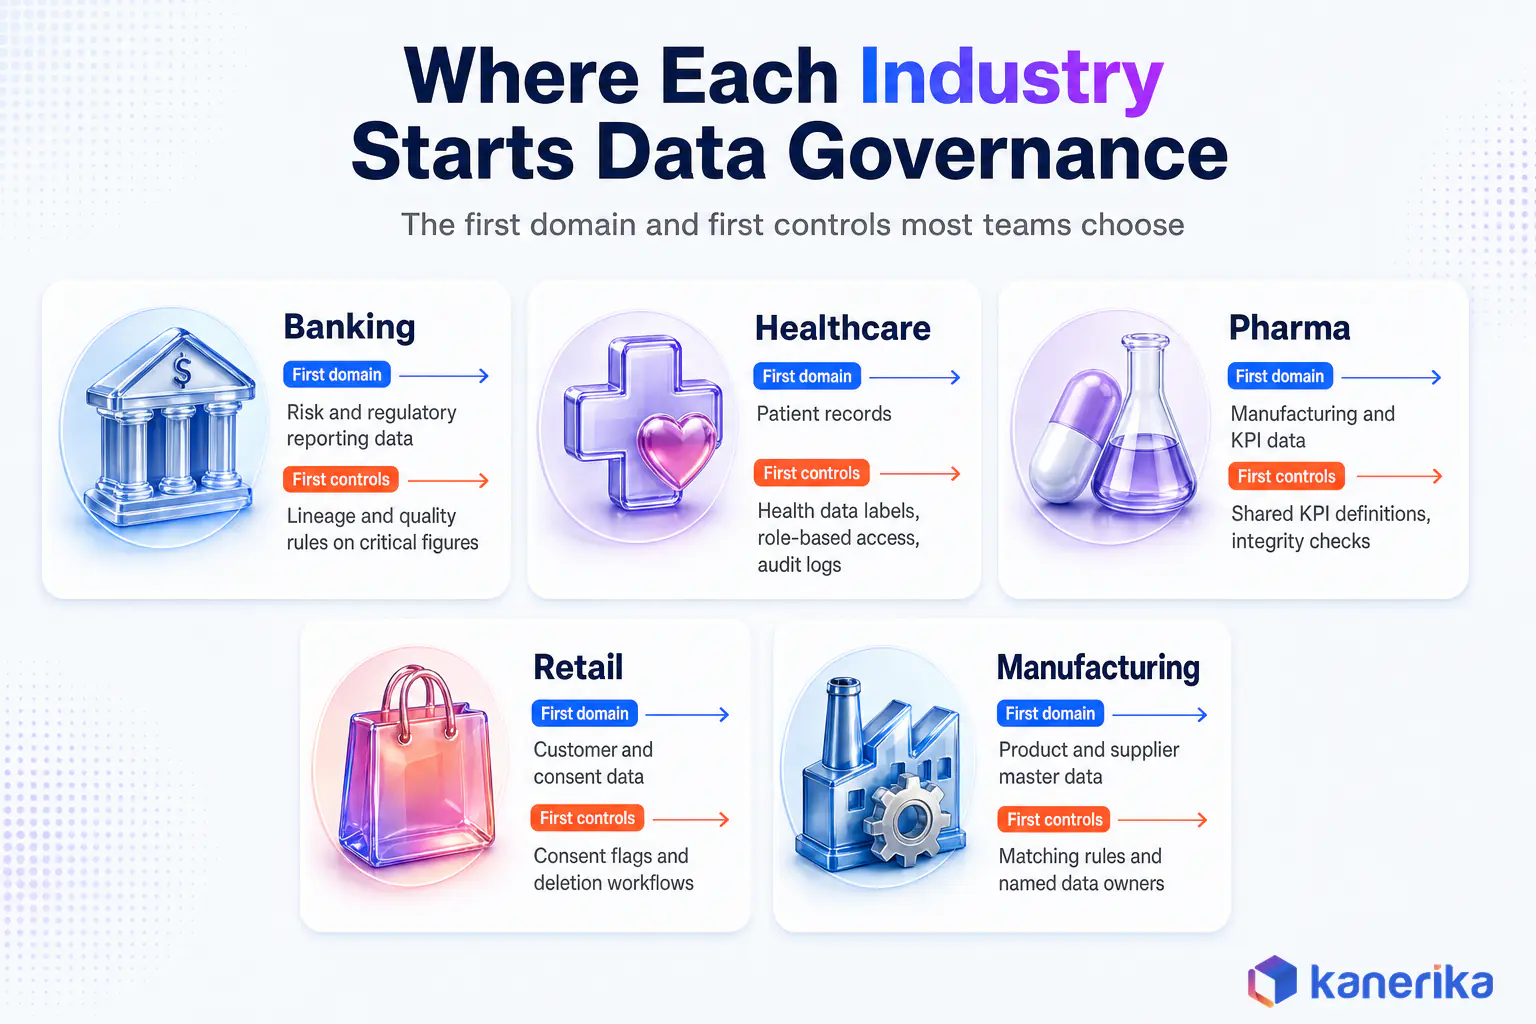
The building blocks stay the same across industries, although the pressure points differ. Each example below shows the typical first domain, the controls that matter most, and the regulation driving them.
Banking and Financial Services
Banks usually start with risk and regulatory reporting data, because that is what supervisors check. The core controls are lineage from each regulatory report back to source systems and quality rules on every critical figure. BCBS 239 and the OCC actions above make both supervisory issues.
The guide to data governance in banking covers the full picture.
Healthcare
Hospitals govern patient data across electronic health records, imaging and billing, often with thin staffing. Classification of protected health information, role-based access for clinicians and audit logs of every record view are the first controls. The guide to data governance in healthcare explains how these map to HIPAA.
Pharma and Life Sciences
Drug makers govern manufacturing, quality and commercial data under strict data integrity expectations, especially in regulated production. A shared definition of each KPI matters as much as security, because the same metric often returns different numbers in different reports.
Retail and Consumer Goods
Retailers usually start with customer and consent data spread across e-commerce, loyalty and marketing tools. Consent flags, deletion workflows and one golden customer record support privacy rights under laws such as the California Consumer Privacy Act. The overview of GDPR and CCPA compliance covers both laws.
Manufacturing and Supply Chain
Manufacturers generally govern product, supplier and equipment master data first. One supplier recorded three ways across ERP systems breaks spend analysis and planning, so matching rules and a named owner for supplier data come early. The guide to supply chain master data management shows the approach.
AI and GenAI Data Governance Examples
AI applications inherit every weakness in the data they read, so governance gaps show up fast. IBM’s 2025 breach research looked at organizations that had an AI-related security incident. It found that 97% of them lacked proper AI access controls, and 63% had no AI governance policies.
- Approved sources for retrieval. A retrieval-augmented assistant may only index documents when the catalog tags them as approved for AI.
- Labels that follow the data. Sensitivity labels travel with files, so a copilot answer drawn from a Restricted file stays restricted.
- Permission-aware answers. Assistants answer with the user’s own permissions, never with a service account that can see everything.
- Training data records. Every model also has a record of its training data, its owner and its intended use.
- Prompt and output checks. Filters stop personal or confidential data from leaving in prompts or answers, even when users paste it in.
Similarly, regulation points the same way. Article 10 of the EU AI Act requires data governance practices for the training, validation and test data of high-risk AI systems. The guides to AI governance frameworks and AI access control cover the model side.
Where Data Governance Programs Stall
Programs rarely fail on technology alone. They stall when governance feels like extra paperwork to the people expected to follow it.
- Policies without owners. A policy nobody is accountable for never gets enforced, however well written.
- Tools before process. A catalog bought before owners and rules exist soon fills up with stale entries.
- Governing everything at once. Programs that start with every domain produce documents rather than visible results.
- No link to business outcomes. If leaders cannot see faster reporting or lower risk, the budget moves elsewhere.
Gartner’s advice from its September 2026 research is to tie governance to business outcomes and build it into daily workflows. The article on data governance challenges covers fixes for each stall point, and data governance best practices lists the habits that keep programs moving.
How Kanerika Runs Data Governance Programs
Kanerika delivers governance as part of its data governance services, mostly on Microsoft Purview, Microsoft Fabric and Databricks estates. Its governance services, kanGovern for strategy and enforcement, kanComply for regulatory compliance, and kanGuard for access protection, are delivered on Microsoft Purview.
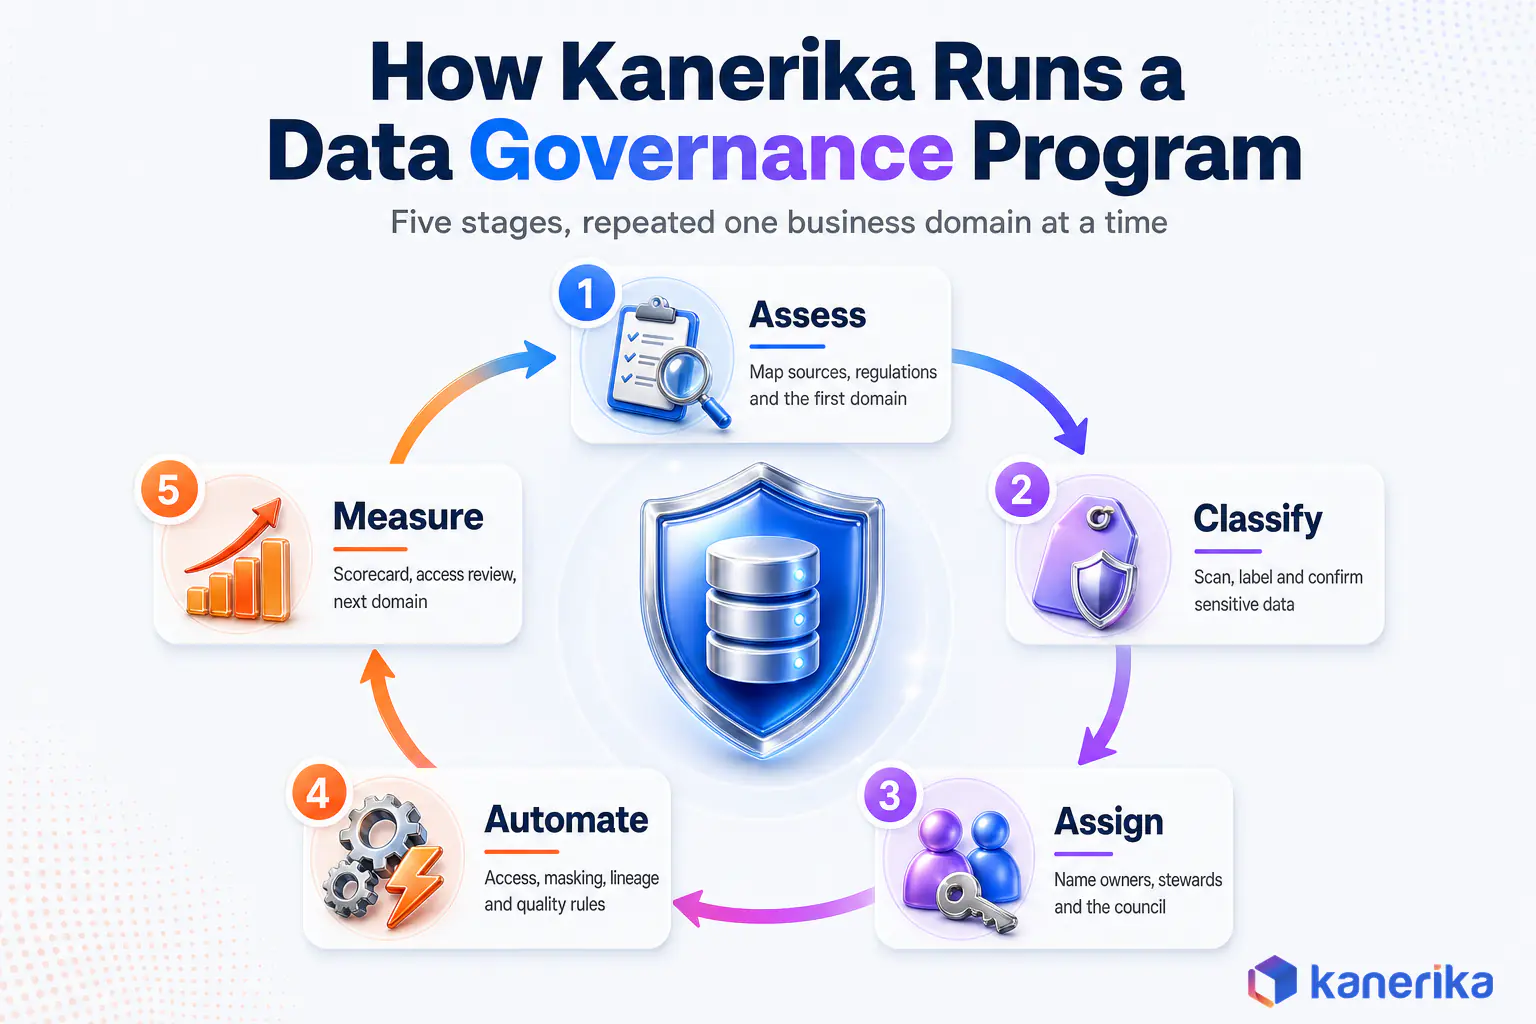
The Delivery Approach
- Assess. Inventory sources, map regulations and then pick the first domain by business pain.
- Classify. Scan the estate, apply classifications and sensitivity labels, and confirm them with stewards.
- Assign. Name owners and stewards, set up the council and also agree the core policies.
- Automate. Turn policies into access rules, masking, lineage and quality checks in the platforms.
- Measure. Publish a scorecard, run the first access review and plan the next domain.
Client Example: A Global Bank on Microsoft Purview
A global bank with nearly 9,000 branches and 22,000 ATMs kept its data in many places. They included SAP, Dynamics 365, core banking systems on Oracle and Netezza, and file shares. Sensitive data was classified by hand, which was slow and error-prone, especially under strict privacy rules.
Kanerika used Purview’s Data Map to discover and classify data automatically. Purview policies governed PII, PCI and PHI, and lineage was automated through the lakehouse layers. According to the bank case study, data classification accuracy improved by 72%, with zero data breaches and 100% adherence to compliance regulations.
Client Example: A North American Healthcare Organization
A large healthcare network had data spread across Azure Blob Storage, SQL databases and SaaS applications, with no consistent classification framework. Kanerika built a central Purview catalog, a classification framework with steward roles and usage policies, and Power BI dashboards for governance reporting.
The healthcare case study reports a 57% reduction in data discovery time, a 90% increase in compliance adherence and a 70% improvement in data accessibility.
Client Example: One Governed KPI Layer for a Pharma Company
A global pharmaceutical company kept KPI definitions inside individual Power BI dashboards, so the same metric returned different numbers. Kanerika built a governed business ontology on Microsoft Fabric that standardized more than 85 KPIs. Per the governed ontology case study, it cut manual investigation and reconciliation time by 70%.
Choosing the Governance Toolset
Kanerika works across Microsoft, Databricks and Snowflake, so tool choice starts from where the data already lives. When Microsoft 365, Azure and Fabric hold most of it, Purview usually becomes the enterprise catalog and labeling layer.
Databricks-centric and Snowflake-centric estates lean on Unity Catalog or Horizon for fine-grained access, with Purview scanning them for the enterprise-wide view. The rule of thumb is simple. Enforce controls where the data is processed, and report on them in one place.
What Kanerika’s Teams Watch For
Three patterns come up again and again in these programs. First, classification scans find far more sensitive data than teams expect, so steward review time needs planning. Second, lineage is only as good as the pipelines feeding it, and hand-built scripts often break it.
Finally, governance sticks when it saves people time. That is why fast catalog search and certified reports win business users over.
Kanerika is a Microsoft Solutions Partner for Data and AI. Its September 2026 announcement lists ISO 27001 and ISO 27701 certifications, SOC 2 Type II compliance and a CMMI Level 3 appraisal.
Kanerika Service
Data Governance Services From Kanerika
Governance strategy, Microsoft Purview implementation and stewardship programs, so your policies become working controls.
Explore Data Governance ServicesWrapping Up
Good data governance examples are specific enough to copy, which is why they work. Start with a one-page ownership policy, four classification levels and a quarterly access review. Add quality rules on 20 critical elements and a RACI chart, and most companies are further along than any framework diagram would take them.
Then pick one domain, measure a baseline, and show leadership the change after 90 days. The enforcement cases above show the cost of skipping the basics, and the client results show what a focused program can deliver.
Frequently Asked Questions
What is a real-life example of data governance?
A hospital that assigns an owner to every patient data table is a real-life example. The owner approves who can see records, and a steward checks quality weekly. Sensitive fields carry labels, so reports mask them automatically. Every access request leaves an audit trail. That combination of owner, rule, control and evidence is data governance in practice.
What are the 5 pillars of data governance?
Most guides name five pillars. They are data quality, data stewardship, data security and privacy, metadata and lineage, and compliance. Quality keeps values accurate and complete. Stewardship gives each dataset an accountable person. Security and privacy limit who sees what. Metadata and lineage explain where data came from. Compliance proves the rules were followed.
What is the main role of data governance?
The main role of data governance is to make data trustworthy and safe to use. It decides who owns each dataset, which rules apply, and how those rules are checked. Good governance lets analysts find approved data quickly. It also gives auditors evidence that sensitive data was handled correctly and on time.
What are the 5 C's of data management?
The 5 C’s are clean, consistent, current, complete and compliant. Clean data has no duplicates or obvious errors. Consistent data uses the same definitions across systems. Current data is refreshed often enough for its use. Complete data has the required fields filled. Compliant data meets privacy and industry rules that apply to it.
What are the two types of data governance?
The two broad types are centralized and decentralized governance. A central team sets and enforces every rule in the centralized type. Business domains make their own decisions in the decentralized type. Most large enterprises now run a federated hybrid. A central council sets shared standards, while domain teams own and steward their own data products.
What is data governance in ETL?
Data governance in ETL means applying ownership, quality and security rules inside data pipelines. Pipelines validate records before loading and quarantine failures for a steward to review. They capture lineage so each report column traces to a source. They also mask sensitive fields in lower environments, which keeps test and development data safe to use.
What are the 3 P's of data governance?
The 3 P’s are people, policies and processes. People are the owners, stewards and council members who make decisions. Policies are the written rules for access, quality, retention and privacy. Processes are the repeatable workflows that apply those rules, such as access requests and issue triage. Tools help automate all three, and the program needs every one of them.
What is an example of IT governance?
A change advisory board that approves every production system change is an example of IT governance. Teams submit a request, assess risk and schedule a rollback plan before release. IT governance covers systems, projects and spending. Data governance sits inside it and focuses on the data itself, including ownership, quality, access and retention.
What is a real-life example of data integrity?
A bank reconciling daily transaction totals between its core system and its data warehouse is a real-life example. Any mismatch raises an alert and blocks the report until a steward resolves it. Checksums, referential constraints and audit logs support the same goal. The data stays accurate and unaltered from source to report.
What are the 5 pillars of data quality?
The five pillars of data quality are accuracy, completeness, consistency, timeliness and validity. Accuracy means values match reality. Completeness means required fields are populated. Consistency means systems agree on the same record. Timeliness means data arrives when it is needed. Validity means values follow the agreed formats, ranges and reference lists.
What are the three principles of data governance?
Three widely used principles are accountability, transparency and integrity. Accountability means each dataset has a named owner who answers for it. Transparency means rules, definitions and lineage are visible to the people using the data. Integrity means data stays accurate and protected across its lifecycle. Most frameworks build their policies on these three ideas.
Who is responsible for data governance?
Responsibility is shared across several roles. A chief data officer or governance lead sponsors the program. A governance council approves policies and settles disputes. Data owners in the business are accountable for specific domains. Data stewards handle definitions and quality issues day to day. Platform and security teams implement the technical controls.
What are the five areas of data governance?
The five areas usually covered are data quality, data architecture, data security, regulatory compliance and data lifecycle management. Quality sets accuracy standards. Architecture defines how data flows between systems. Security controls access and encryption. Compliance maps rules like GDPR and HIPAA to controls. Lifecycle management decides how long data is kept and when it is deleted.
What is an example of a data governance best practice?
Starting with one high-value domain is a widely recommended best practice. A team might govern customer data first by assigning owners, writing five quality rules and labeling sensitive fields. It then measures results after 90 days before expanding the program. This keeps effort focused and gives leaders early evidence of better reporting and lower risk.
What is the most common data governance framework?
DAMA-DMBOK is the most widely referenced data governance framework. It is published by DAMA International and describes eleven knowledge areas, with governance at the center. The Data Governance Institute framework is also popular for its focus on decision rights. Many enterprises combine one of these with a platform catalog such as Microsoft Purview.
What are the four main roles in data governance?
The four main roles are data owner, data steward, data custodian and data governance council. Owners are business leaders accountable for a domain. Stewards manage definitions, quality rules and issues. Custodians are technical teams who store, secure and back up the data. The council sets policy, resolves conflicts and tracks progress across domains.
Why do we need data governance?
Organizations need data governance because data spread across many platforms quickly loses clear ownership and quality. Without it, teams argue over which number is right, audits take weeks, and sensitive fields leak into places they should not be. Governance fixes ownership, rules and access. That makes reports reconcile and AI projects safe to scale.
What is data governance in simple terms?
In simple terms, data governance is the set of rules and responsibilities for an organization’s data. It says who owns each dataset, who may use it, and how good it must be. It also sets how long data is kept. Tools like catalogs and access policies then enforce those rules automatically.
What are examples of data governance policies?
Common examples include a data ownership policy, a classification policy and an access control policy. Others cover retention and deletion, data quality, and acceptable AI use. Each one states the rule, who it applies to, and how compliance is checked. Short, specific policies get followed more often than long manuals.
What are examples of data governance controls?
Examples include quarterly access reviews, automatic masking of personal data, and quality rules that block bad loads. Lineage capture for critical reports and scheduled deletion of expired records are common too. Some controls prevent problems before they happen. Others detect problems afterward and raise an alert. Every control should produce evidence an auditor can check.
How do you create a data governance plan?
Start by picking one domain with a clear business problem. Inventory its critical data elements and assign owners and stewards. Write a few short policies, then implement the controls that enforce them in your catalog and platforms. Set three to five metrics, review them monthly, and expand to the next domain after about 90 days.
What are examples of data governance processes?
Typical processes include dataset onboarding, access requests, data quality issue triage, business glossary updates, and periodic certification of critical reports. Each process names who starts it, who approves it, and what evidence it leaves. Automating these workflows in a catalog such as Microsoft Purview or Unity Catalog keeps them fast enough that people follow them.
How does data governance support AI projects?
Governance tells an AI project which data it may use and how trustworthy that data is. It limits models and copilots to approved, labeled sources. It records lineage from training data to outputs. It also keeps sensitive data out of prompts and answers. That gives teams the evidence needed to scale AI safely.
What are the first steps to implement data governance?
Get an executive sponsor and name a small governance council. Choose one business domain with a visible pain point. Identify its critical data elements and assign owners. Then write a handful of policies and turn on basic controls such as classification and access reviews. Measure a baseline so progress is easy to prove.
What are the top data governance tools?
Widely used data governance tools include Microsoft Purview, Databricks Unity Catalog, Snowflake Horizon, Collibra, Alation, Informatica Cloud Data Governance and Catalog, and Atlan. Platform-native tools govern data inside their own platform. Standalone catalogs span many platforms. The right choice depends on where your data lives and how many platforms you run.
What are the four pillars of data governance?
A common four-pillar model covers data stewardship, data quality, master data management and use-case alignment. Stewardship gives data clear owners. Quality keeps it accurate and complete. Master data management creates one trusted record for customers, products and suppliers. Use-case alignment ties every governance effort to a business outcome that leaders care about.